The ITSPmagazine Podcast
ITSPmagazine Podcast, hosted by Sean Martin and Marco Ciappelli, explores the intersection of technology, cybersecurity, and society. The show features conversations on topics like music, storytelling, branding, and conference coverage, examining how these elements influence the human experience. Originally a written publication, ITSPmagazine has evolved into a multimedia platform offering podcasts, articles, videos, and event coverage.
Episodes
Nobody Says Good Morning to a Shovel. Should You Say It to Your AI? | A Random and Unscripted Conversation with Sean Martin and Marco Ciappelli
⬥EPISODE NOTES⬥A TechCrunch report on Anthropic's usage policy gives Marco Ciappelli a question to put on the table: do you say good morning to your AI, and does it matter if you do not? The policy bans model abuse and election interference, and it adds a new prohibition against prolonged verbal abuse of the model. For Sean Martin and Marco Ciappelli, the news pulls toward a bigger question: what
Deadly Bytes: A Book About a Serial Killer, His AI, and a Reflection on Giving Away Our Judgment | A Conversation With Author Douglas J. Wood
Deadly Bytes: A Book About a Serial Killer, His AI, and a Reflection on Giving Away Our JudgmentConfession first: I recorded more conversations than one analog brain can publish on time. This one is from a few months ago. It only got more relevant while it waited.My wife and I can't watch a thriller in peace. Ten minutes in, I start calling it. He's the one. She won't make it. Never trust the nice
The ESET PROTECT Launch Brings 24/7 Monitoring, AI Security, and a Cyber Warranty to Small and Midsize Businesses | A Brand Story Conversation with Ryan Grant, Country Manager & GM, North America at ESET | Hosted by Sean Martin
Ryan Grant, Country Manager & GM, North America at ESET, joins Sean Martin to discuss the launch of ESET PROTECT, announced September 30, 2026. The platform brings 24/7 monitoring, AI security, and a cyber warranty to small and midsize businesses. Ryan Grant says the design came from feedback from ESET clients and partners, along with a survey of 2,000 SMB customers earlier this year. About 70
Taking Technology for What It Is, and Let's Stop Humanizing AI
Taking Technology for What It Is, and Let's Stop Humanizing AIA new transmission from An Analog Brain In A Digital Age, by Marco CiappelliPrefer to watch? I recorded this one walking uphill through a Tokyo alley. YouTube: https://youtu.be/5nhBNMJ7LFI TikTok: https://vm.tiktok.com/ZN8hExSpT/ Instagram: https://www.instagram.com/reel/DeF7fz2gdpE/It was night, the alley was narrow, and the street was
Giving a Damn: Joe Raiola on 46 Years of John Lennon, MAD Magazine, and Music That Heals | A Music Evolves Conversation with Joe Raiola, President and Artistic Director of Theatre Within
Show NotesJoe Raiola is President and Artistic Director of Theatre Within, the nonprofit behind the Annual John Lennon Tribute, which he has produced since shortly after Lennon's death in December 1980. What began as an informal community gathering of poets, storytellers, and musicians grieving a neighbor has grown into one of New York City's most significant annual benefit concerts, and the only
Do New Technologies Have to Kill the Old Ones? | Recorded at Tokyo Tower, Tokyo, Japan
A new transmission from An Analog Brain In A Digital Age, by Marco CiappelliPrefer to watch? I recorded this one standing under Tokyo Tower:On YouTube: https://youtu.be/glGHghhhXWcOn Tik Tok: https://vm.tiktok.com/ZN8MM8Hd9/On Instagram: https://www.instagram.com/reel/DdlAe7tAOQK/?stkn=NTc4MTIwNjQ2YQ==I spent twenty minutes looking for the right angle.A small camera, a mini tripod, a patch of side
Who Decides You Are a Real Musician | A Music Evolves Conversation with Josh Gilliland, Founder of JG BeatsLab
Show NotesThe argument over AI in music presents itself as a fight about authenticity. Josh Gilliland reads it as a fight about who holds the gate. The Founder of JG BeatsLab teaches musicians how to fold generative tools into real workflows, and he watches the platforms assemble a definition of legitimacy that has little to do with how a song actually gets made.That definition, as Gilliland descr
When Everyone Can Build Their Own Tools, What Holds Security Together? | A Redefining CyberSecurity Podcast Conversation with John Linford, Security Portfolio Director of The Open Group
⬥EPISODE NOTES⬥Something structural is shifting in how security work gets done. When anyone on a team can stand up a working tool in an afternoon, the constraint stops being capability and starts being coherence. John Linford, Security Portfolio Director at The Open Group, spends his time on exactly that problem, running the Security Forum, the Open Trusted Technology Forum, and the Assured Depend
Marketing Volume Held Steady. Scrutiny Went Up. | Lens Four by Sean Martin | Read by TAPE9
⬥EPISODE NOTES⬥
For a full year, agentic AI was the pitch. This year the conversation shifted to whether it holds up once it is actually running in production, against real work. Vendors came armed with customer-sourced numbers rather than concept demos — hours returned per analyst per week, percentages of alerts dispositioned without human review, agreement rates measured against human analyst ju
Executives Can Now Invite Their Lawyer, Banker, and Dog Walker Into a Verified Circle of Trust | A Brand Spotlight Recorded On Location at Black Hat USA 2026 with Matt Covington and Tracey Moon of BlackCloak | Hosted by Sean Martin
Matt Covington, Senior Vice President of Product at BlackCloak, says the feature exists because CISOs kept asking the same question. Can you help us manage this influx of deepfake media, whether it arrives by email, video, or voicemail. The requests that follow are familiar. Change the billing information on a vendor. Wire me $5,000 to bail me out of jail.
Rather than sitting in line with every co
Executives Can Check a Country's Risk and a Caller's Identity From the Same BlackCloak App | A Brand Spotlight Recorded On Location at Black Hat USA 2026 with Matt Covington, Senior Vice President of Product at BlackCloak | Hosted by Sean Martin
Matt Covington, Senior Vice President of Product at BlackCloak, walks through two features recently added to the member application. The first grew out of a question the concierge team fielded often. Members planning family travel to China or Eastern Europe wanted to know what to expect, how to protect their devices, and how to stay safe.
That work now sits inside the app as a travel advisory page
A Secure and Compliant Business Is the Destination. Steel Patriot Partners Maps Five Routes to It. | A Brand Spotlight Recorded On Location at Black Hat USA 2026 with Michael Parisi, Chief Growth Officer at Steel Patriot Partners | Hosted by Sean Martin
What a company is trying to reach is rarely a certificate. Michael Parisi, Chief Growth Officer at Steel Patriot Partners, treats the destination as the opening question rather than the closing one, and the firm orders its own priorities to match. Business owners first, engineers second, compliance and security people third.
What does a secure and compliant business actually look like? It looks li
Six Hours, Five Strangers, and a Song the Machine Could Not Write | A Music Evolves Conversation with Gregoire Gensollen, Producer and Chief Operating Officer of Tucker Tooley Entertainment
Show Notes
The premise sounds like a stunt. Five strangers, one room, six hours, one original song. Meanwhile the show's host sits at a keyboard with a text prompt and half an hour. Grégoire Gensollen, Producer and Chief Operating Officer at Tucker Tooley Entertainment, built that episode of Band of Strangers knowing he could not predict the outcome, which is precisely why he made it.
Gensollen co
Executives Get Reached Through the People Around Them, and BlackCloak Protects That Whole Circle | A Black Hat USA 2026 Recap with Dr. Chris Pierson, Founder and CEO at BlackCloak | Hosted by Sean Martin and Marco Ciappelli
An attacker who wants to reach an executive often goes through the people around them. Family members, assistants, advisors, and caregivers all carry access and standing, and none of them sit inside the corporate directory. Dr. Chris Pierson, Founder and CEO of BlackCloak, describes digital executive protection as work that comes down to an individual and the circle around that individual.
What do

Attackers Relay Codes and Approvals. TokenCore Requires a Live Fingerprint Within Three Feet | A Brand Briefing at Black Hat USA 2026 with Kevin Surace, Chief Executive Officer at TokenCore | Hosted by Sean Martin
Kevin Surace, Chief Executive Officer at TokenCore, opens with the attack path he says is doing the most damage right now. A phishing email carries a PDF and no links, so it clears the filters. The domain is one character off from the real one, the site is pixel perfect because AI built both the page and the message, and the employee approves an auth prompt they were already expecting.
The code wa
Two Inc. Awards in One Year Tell BlackCloak's Cloakers and Clients the Same Thing | A Brand Highlight Recorded On Location at Black Hat USA 2026 with Chris Pierson, Founder and CEO at BlackCloak | Hosted by Sean Martin
BlackCloak collected two Inc. recognitions in 2026. The company was named to Inc.'s Best Workplaces list in June, and in August it landed on the Inc. 5000 for a second consecutive year, at a higher position than the first. Founder and CEO Chris Pierson points both at the same two groups, the people who build BlackCloak and the clients and members who rely on it.
What does a second Inc. 5000 rankin
An imperfect drink with a perfect story. My reflections from Black Hat USA 2026 | An Analog Brain In A Digital Age — An Audio Newsletter by Marco Ciappelli
An imperfect drink with a perfect story.
My reflections from Black Hat USA 2026
An Analog Brain In A Digital Age — A Newsletter by Marco Ciappelli
No time to read? Let TAPE3 read it to you. 🎙️🤖
On day two we decided to go record our recap at the Black Hat bar.
We got there too late to get a drink. The expo floor was closing, and the bartender must have had better things to do. Or another bar to te

Business Owners First, Engineers Second, Compliance People Third | A Brand Spotlight Conversation with Jason Ford and Michael Parisi of Steel Patriot Partners | Hosted by Marco Ciappelli
Steel Patriot Partners lists its priorities in an order much of the cybersecurity industry reverses. Business owners first, engineers second, security and compliance people third. Michael Parisi, Chief Growth Officer, says the sequence is deliberate and shapes how the firm opens a client conversation.
The order tracks the path the founders took. Jason Ford, Co-Founder and CEO, started in the late
Sovereign AI Becomes an Operational Requirement, and Crogl Built for It From the Start | A Recap at Black Hat USA 2026 with Monzy Merza, Co-Founder and CEO at Crogl | Hosted by Marco Ciappelli
Espresso in hand at Black Hat USA 2026, Monzy Merza, Co-Founder and CEO of Crogl, gave Marco Ciappelli the read from a week that started Monday. The free download the company announced the week before had drawn a strong community reaction, and a hackathon was running alongside the conversation with people downloading Crogl, hacking on it, and competing in challenges. Merza credits the openness of
The AI SOC Moves Into Production, and Practitioners Want Hands on the Keyboard | A Recap at Black Hat USA 2026 with Bill Peterson, Senior Director of Product Marketing at Sumo Logic | Hosted by Marco Ciappelli
What actually changed for the AI SOC this year? Bill Peterson, Senior Director of Product Marketing at Sumo Logic, says it reached the point of getting into production, where a year or so ago the same conversation was about what was coming. Marco Ciappelli puts the count of companies carrying AI SOC in the name at 43, and Bill Peterson says that number strikes him as low. The market is maturing, a
Proof Is the Currency on the Black Hat Floor | A Recap at Black Hat USA 2026 with Lisa Liu, Corporate Marketing and Communications Manager at Stellar Cyber | Hosted by Marco Ciappelli
Lisa Liu, Corporate Marketing and Communications Manager at Stellar Cyber, connects with ITSPmagazine on the floor at Black Hat USA 2026 in Las Vegas. What are buyers asking for now that the RSAC Conference noise has settled? Data. Liu says people have had time to run their own research, look at what vendors offer, and come back using specific keywords and asking for something behind the marketing
The Capability Is Already in Your Stack. The Question Is Who You Ask. | A Recap at Black Hat USA 2026 with Michael Parisi, Chief Growth Officer at Steel Patriot Partners | Hosted by Marco Ciappelli
Michael Parisi, Chief Growth Officer at Steel Patriot Partners, connects with ITSPmagazine on location at Black Hat USA 2026 for a recap of the week. He describes Steel Patriot Partners in the order it sets its priorities. Business owners first, engineers second, compliance and security people third. A consulting and advisory company, he says, but really an engineering firm.
What changed at this e
Detection at AI Speed, Prioritization by Workflow, and Autonomous Elimination | A Recap at Black Hat USA 2026 with May Mitchell, Chief Marketing Officer at Qualys | Hosted by Marco Ciappelli
Qualys returns to Black Hat USA 2026 with an AI Risk Operations Center built around three principles customers have been asking for over the last three years. May Mitchell, Chief Marketing Officer at Qualys, walks through them in order. Detect vulnerabilities at AI speed. Prioritize what surfaces, because not every finding calls for action in the same hour and the sequence follows the workflows a
Buyers Are Asking What the AI Actually Does | A Recap at Black Hat USA 2026 with Daniel Bardenstein, CEO and Co-Founder at Manifest Cyber | Hosted by Marco Ciappelli
Daniel Bardenstein, CEO and Co-Founder of Manifest Cyber, uses RSAC Conference as a fixed point and compares it to what he is hearing in Las Vegas. The marketing has held its shape. At RSAC Conference, companies with little claim to the label were describing themselves as agentic. Here, he cites a survey referenced in a talk that morning counting 47 AI SOC companies among the vendors on site.
What
Vulnerability, Visibility, and Velocity Shape the Security Roadmap Now | A Recap at Black Hat USA 2026 with Sean Murphy, Field CISO for North America at F5 | Hosted by Marco Ciappelli
Sean Murphy, Field CISO for North America at F5, spent the week behind the scenes at Black Hat USA 2026, in the corridors and at dinner with the CISOs and cybersecurity minded people who fill the halls. Marco Ciappelli caught him at the close of it and asked what the industry learned this year. The answer arrived as three words. Vulnerabilities, and the flattening of the curve between vulnerabilit
SOC Teams Are Building Their Own Agents, and the Data Sets the Ceiling | A Recap at Black Hat USA 2026 with Brian Dye, Chief Executive Officer at Corelight | Hosted by Marco Ciappelli
Brian Dye, Chief Executive Officer at Corelight, spends Black Hat USA 2026 asking every organization he talks to the same question. What are you doing with AI in the SOC? A year ago, he says, teams thought it was a good idea but were wary of it, and people knew LLMs could produce things without being sure what to do with them. Now he is talking with organizations building their own agents for inci
Coding Is a Fraction of the Work. Harness Secures Everything After It. | A Brand Briefing at Black Hat USA 2026 with Rahul Sood, General Manager, Application Security at Harness | Hosted by Sean Martin
Rahul Sood has run the application security business at Harness for almost a year. He describes application security as one of the core pillars of the company, part of a vision of building a DevSecOps platform. A year ago Harness publicly announced that security accounted for a quarter of its revenue. Sood says the figure is now considerably higher.
The company did not start there. Founder Jyoti B
Compliance Moves at the Speed of DevOps When Paperwork Writes Itself | A Brand Briefing at Black Hat USA 2026 with Travis Howerton, Co-Founder and CEO at RegScale | Hosted by Sean Martin
Why does compliance paperwork fall behind the systems it describes? Because the systems change faster than the documents. Travis Howerton points to cloud native technologies that spin up and down on demand, which makes describing infrastructure in paperwork something that goes out of date instantly. Add new regulation for third party risk, supply chain, zero trust, and privacy, and an approach tha
Post-Quantum Readiness Starts With the Infrastructure You Buy Today | A Brand Briefing at Black Hat USA 2026 with Larry Lunetta, Vice President, Portfolio Technical Marketing at HPE | Hosted by Sean Martin
Post-quantum cryptography was in conversation after conversation at Black Hat USA 2026, yet Larry Lunetta of HPE walked part of the show floor and counted a single reference to quantum. Where the topic shows up, and where it does not, says something about who is expected to solve it.
Why does a problem described in 1994 matter now? Larry Lunetta points to Peter Shor, who asked what would happen to
Agents Get Zero Trust, and the Network Becomes the Sensor | A Brand Briefing at Black Hat USA 2026 with David Hughes, SVP and GM of SASE and Security for Networking at HPE | Hosted by Sean Martin
Most people know HPE for servers, compute, and storage. David Hughes leads a pillar that gets less attention. He runs the SSE and security business inside HPE Networking, which he says accounts for about a third of the company now that HPE has merged with Juniper, and which organizes into four pillars: campus and branch, data center switching, routing infrastructure, and security.
Recorded on loca
AI Agents Act at Machine Speed. Menlo Security Governs What They Actually Do. | A Brand Briefing at Black Hat USA 2026 with Eric Avigdor, Vice President of Product of Menlo Security | Hosted by Sean Martin
Recorded on location at Black Hat USA 2026, Eric Avigdor of Menlo Security describes an adoption pattern he hears in customer conversation after customer conversation. AI makes teams measurably more productive. The guardrails that keep company data inside the business arrive later, if they arrive at all.
Eric Avigdor leads product for AI security and data security at Menlo Security, and he splits
Adversary Behavior Outlasts the Ransomware Brand | A Brand Briefing at Black Hat USA 2026 with Michael DeBolt, President and Chief Intelligence Officer of Intel 471 | Hosted by Sean Martin
Proactive and actionable get used a lot in security, and Michael DeBolt, President and Chief Intelligence Officer at Intel 471, is direct about it. Inside Intel 471, proactive means moving past indicators of compromise, which he describes as temporary, and focusing on adversary behavior instead. Indicators still get blocked. Intent, capability, and motivation are what tell a defender whether they
10,000 Alerts a Day, 75% Cleared With Evidence Analysts Can Check | A Brand Briefing at Black Hat USA 2026 with Seth Summersett, Co-Founder and CEO of Embed Security | Hosted by Sean Martin
Recorded on site at Black Hat USA 2026 in Las Vegas, Seth Summersett joins Sean Martin to talk through the volume problem that shapes a modern security operations team. Seth Summersett spent about a decade at the NSA and roughly a decade at Mandiant, finishing there as head of innovation and custom engineering, then a couple of years at Meta supporting business unit level CISOs. He co-founded Embe
Network Evidence, AI Triage, and Leaving People Better Than They Arrived | A Full Sponsor Brand Briefing at Black Hat USA 2026 with James Pope, Sr Dir of Security Product Research and Technical Marketing Engineering at Corelight | Hosted by Sean and Marco
James Pope is on site in Las Vegas more than a week before the doors open. As SOC lead for the Black Hat NOC and Senior Director of Security Product Research and Technical Marketing Engineering at Corelight, his show starts with switches and access points rather than alerts. The team brings in the ISP, the firewall, the switches, and the access points, deploys them across the conference, and then
The Last Mile of Security Operations Runs on a Local Model | A Full Sponsor Brand Briefing at Black Hat USA 2026 with Karthik Kannan, Founder and CEO at Anvilogic | Hosted by Sean Martin
Recorded on location at Black Hat USA 2026 in Las Vegas at the end of day two, Karthik Kannan, Founder and CEO at Anvilogic, walks through a seven year build that reached its original shape this year. The plan from the start was a full security operations platform covering data, the detection engineering process, triage and investigation, and case management. In the shorthand of the category, SIEM
Agents in Production Need a Named Accountable Owner | A Full Sponsor Brand Briefing at Black Hat USA 2026 with Sean Murphy, Field CISO for North America at F5 | Hosted by Sean Martin
Sean Murphy spent most of the past decade running F5 technology as a customer inside highly regulated environments. He is now about four weeks into the role of Field CISO for North America, and he describes the first month as drinking from a fire hose. Depending on how the math is done, he places F5 among the seven largest cybersecurity companies once BIG-IP is counted as security tooling, with th
Autonomous Remediation Is Already Running at Enterprise Scale | A Full Sponsor Brand Briefing at Black Hat USA 2026 with Sumedh Thakar, President and CEO at Qualys | Hosted by Sean Martin
Sumedh Thakar joined Qualys as an early software engineer on the scanner, back when a 90-day scan cycle came with another 90 days to fix whatever it found. Twenty-three years later he leads the company, and the number he uses now is 90 seconds. At Black Hat USA 2026 he walks through what that compression asks of security teams.
So what has actually changed? The questions have not. Where are my ass
Stellar Cyber Puts Numbers Behind Agentic Auto Triage and Hands Analysts 19 Minutes Back Every Hour | A Full Sponsorship Brand Briefing at Black Hat USA 2026 with Lisa Liu, Corp Marketing and Comms Manager at Stellar Cyber | Hosted by Sean Martin
Lisa Liu, Corporate Marketing and Communications Manager at Stellar Cyber, says the AI noise has been running since RSAC Conference, and that what separates vendors now is whether they can back their claims with data their customers gave them. She came to Black Hat USA 2026 with figures on Agentic Auto Triage.
The numbers she cites: up to 19 minutes saved per hour per analyst, up to 1.5 full-time
Protecting the Executive Means Protecting Everyone They Trust | A Full Sponsor Brand Briefing at Black Hat USA 2026 with Dr. Chris Pierson, Founder and CEO at BlackCloak | Hosted by Marco Ciappelli
On the show floor at Black Hat USA 2026, Marco Ciappelli connected with Dr. Chris Pierson, Founder and CEO at BlackCloak, about a change in where the company draws the line around who gets protected. BlackCloak launched Impersonation Protection several months ago for the C-suite and their families. Clients came back asking for more reach.
Why does deepfake risk extend past the executive? Because t

Thirty Gigs a Month Is the Practice | A Music Evolves Conversation with Frankie Raye, Singer-Songwriter
Show Notes
There is a version of the music career that gets written about, and there is the version that gets played. Frankie Raye lives in the second one. She performs six or seven nights a week across the greater Tampa Bay area, mixes covers with originals depending on what the room wants, and treats the gig itself as the practice session. She points at old video of herself and measures the dist
The Budget Is Already Spent. The ROI Is in the Configuration. | A Full Sponsor Brand Briefing at Black Hat USA 2026 with Michael Parisi, Chief Growth Officer of Steel Patriot Partners | Hosted by Sean Martin
Automation and AI have flooded the sales and marketing side of the market, and Michael Parisi, Chief Growth Officer at Steel Patriot Partners, says the security leaders on the receiving end were already past capacity. The pitch tends to lead with the product rather than the problem. So many CISOs have stopped taking direct sales calls and started asking a different question: what VAR do you work w
Sovereign AI That Runs Where Your Data Lives | A Full Sponsor Brand Briefing at Black Hat USA 2026 with Monzy Merza, Co-Founder and CEO of Crogl | Hosted by Sean Martin
Crogl arrived at Black Hat USA 2026 with two announcements behind it. The week before the show, the company made a free download of its AI SOC agent generally available. On the morning of this conversation, it went public with a major global partner tied to the U.S. Department of Defense. Monzy Merza, Co-Founder and CEO of Crogl, ties both back to a position the company took three years ago, which
AI Has Its Own Supply Chain | A Full Sponsor Brand Briefing at Black Hat USA 2026 with Daniel Bardenstein, CEO and Co-Founder of Manifest Cyber | Hosted by Sean Martin
At Black Hat USA 2026 in Las Vegas, Daniel Bardenstein, CEO and co-founder of Manifest Cyber, starts with a gap his team measured in a survey of security leaders and practitioners. Leadership described one version of what is happening with AI inside the enterprise. The people doing the hands-on work described another. Adoption keeps moving, and security teams are working to catch up.
So what is th
Customer Zero at Exabyte Scale | A Full Sponsor Brand Briefing at Black Hat USA 2026 with Jeremy Powell, CISO of Sumo Logic | Hosted by Sean Martin
Most vendors at Black Hat USA 2026 have something to say about agentic AI. Jeremy Powell, CISO at Sumo Logic, spends this conversation on the harder proof, which is what happens when a company runs its own product in production at scale. Sumo Logic has been doing that for roughly ten to eleven months. Powell calls it customer zero, and it shapes how he answers almost every question here.
The Sumo
Vulnerability Backlogs Can Finally Reach Zero | A Brand Spotlight Conversation with Ondrej Vlcek, Co-Founder and CEO of AISLE | Hosted by Sean Martin
Security leaders count open vulnerabilities in the hundreds of thousands, and in some organizations the number runs past a million. Ondrej Vlcek, Co-Founder and CEO of AISLE, describes teams with no practical route through that backlog while attackers use automation to shrink the time between a disclosure and a working exploit. The question worth asking is what a program looks like when remediatio
Agentic Security Changes Everything | An On Location Conversation at Infosecurity Europe 2026 with John Sotiropoulos and Rock Lambros
Sean Martin catches John Sotiropoulos and Rock Lambros at the end of the OWASP GenAI Security Summit, held alongside Infosecurity Europe 2026 at ExCeL London. Both are deep in the standards work: John Sotiropoulos co-leads the OWASP Agentic Security Initiative and sits on the board of the OWASP GenAI Security Project, and Rock Lambros serves as Director of AI Standards and Governance at Zenity and
The Business Decision Hiding Inside FedRAMP's Consolidated Rules for 2026 | A Brand Story Conversation with Jason Ford and Michael Parisi of Steel Patriot Partners | Hosted by Sean Martin
FedRAMP has changed before. What makes the Consolidated Rules for 2026 different is that the dates are on the calendar and the fence sitters have run out of runway. Jason Ford, Co-Founder and CEO of Steel Patriot Partners, has been inside the program since Rev 3 in 2013. Michael Parisi, Chief Growth Officer, comes at it from the business side. Together they map what changes and, more usefully, wha
FedRAMP First: Modernizing the Defense Supply Chain Without Cutting Corners | A Brand Feature Conversation with Michael Parisi of Steel Patriot Partners and Jason LaPointe of Exostar
For companies in the defense industrial base, a compliance deadline is not paperwork. It is the difference between winning contracts and watching them stall. In this Brand Feature, Jason LaPointe, Chief Technology Officer at Exostar, and Michael Parisi, Chief Growth Officer at Steel Patriot Partners, walk through what it takes to get FedRAMP ready without cutting corners.
Exostar was born out of a
Tech Trailblazers: Recognition That Reaches the Whole Team | An Interview with Rose Ross | An Analog Brain In A Digital Age With Marco Ciappelli
PODCAST EPISODE | An Analog Brain In A Digital Age With Marco Ciappelli
Fifteen years ago, Rose Ross brought a client an idea for an awards program built specifically for enterprise tech startups. The client passed. She built it herself — and the Tech Trailblazers have been running ever since, independent, judged by practitioners, and open for entries until 3 September.
📺 Watch | 🎙️ Listen | marco
Your Team Is Already Using AI. They Just Won't Tell You. | Priyanka Dave, PhD | PODCAST EPISODE | An Analog Brain In A Digital Age With Marco Ciappelli
PODCAST EPISODE | An Analog Brain In A Digital Age With Marco Ciappelli
Every organization has a policy on AI. Most of them are unwritten, unspoken, and enforced by silence. Priyanka Dave — behavioral scientist, dual PhD, and the person responsible for teaching an entire university system how to work with these tools — explains what actually happens inside a company that refuses to say the word ou
The Flood Made Everything Free. So Now We Pay for Proof. | Lens Four by Sean Martin | Read by TAPE9
⬥EPISODE NOTES⬥
Tidal is about to stop paying royalties on any track it judges to be fully machine-made. Frame that as a music story and you miss the shift underneath it. By Deezer's own detection, roughly 75,000 AI-generated tracks now arrive every day, about 44% of everything uploaded, yet that same AI music is only 1 to 3 percent of what people actually play, and around 85% of those streams are
We Made Everything Faster. We Never Defined Better. | Lens Four by Sean Martin | Read by TAPE9
⬥EPISODE NOTES⬥
Almost every booth at Infosecurity Europe 2026 had settled on the same four words. Outcomes. Resilience. Sovereignty. Human in the loop. The messaging had grown up, more tempered than RSAC, more honest in its European register. The tell was quieter — almost none of it could connect those words to a definition of success a buyer could actually verify.
Strip away the polish and the s
A Forrester Analyst on the Security Roles Coming Next — and What AI Makes Obsolete in Cybersecurity | A Conversation with Madelein van der Hout | On Location With Sean Martin And Marco Ciappelli — Infosecurity Europe 2026
ON LOCATION | Sean Martin & Marco Ciappelli — Infosecurity Europe 2026
Two conferences, two moods: at RSA the drumbeat was resilience; at InfoSec, it's sovereignty. Sean and I close the week with Forrester analyst Madelein van der Hout — beaming in from the Netherlands — on why Europe makes a framework out of everything, what AI deployment is doing to the boardroom, and the security jobs that don'
The Identity Gap Behind Nearly Every Breach | A Brand Spotlight Conversation with Kevin Surace, CEO of TokenCore
For most of the internet's life, proving identity has meant proving something you know or something you hold: a password, a code, a text message. Kevin Surace, CEO of TokenCore, argues that era is closing fast. As one of the people who helped invent the AI assistant at General Magic, he has a clear view of why the same technology now makes faces and voices simple to fake.
Why isn't MFA enough? Bec
When You Can't Trust the Face on the Call | A Brand Highlight Conversation with Kevin Surace, CEO of TokenCore
In this Brand Highlight, Kevin Surace, CEO of TokenCore, catches up on a market that has accelerated faster than even his team expected. Biometric-assured identity has gone from the fringes to the core, and the clearest example is the video call: on Zoom or Teams, there is often no reliable way to know whether the person on screen is real, human, or an AI avatar. Surace points to cases where emplo
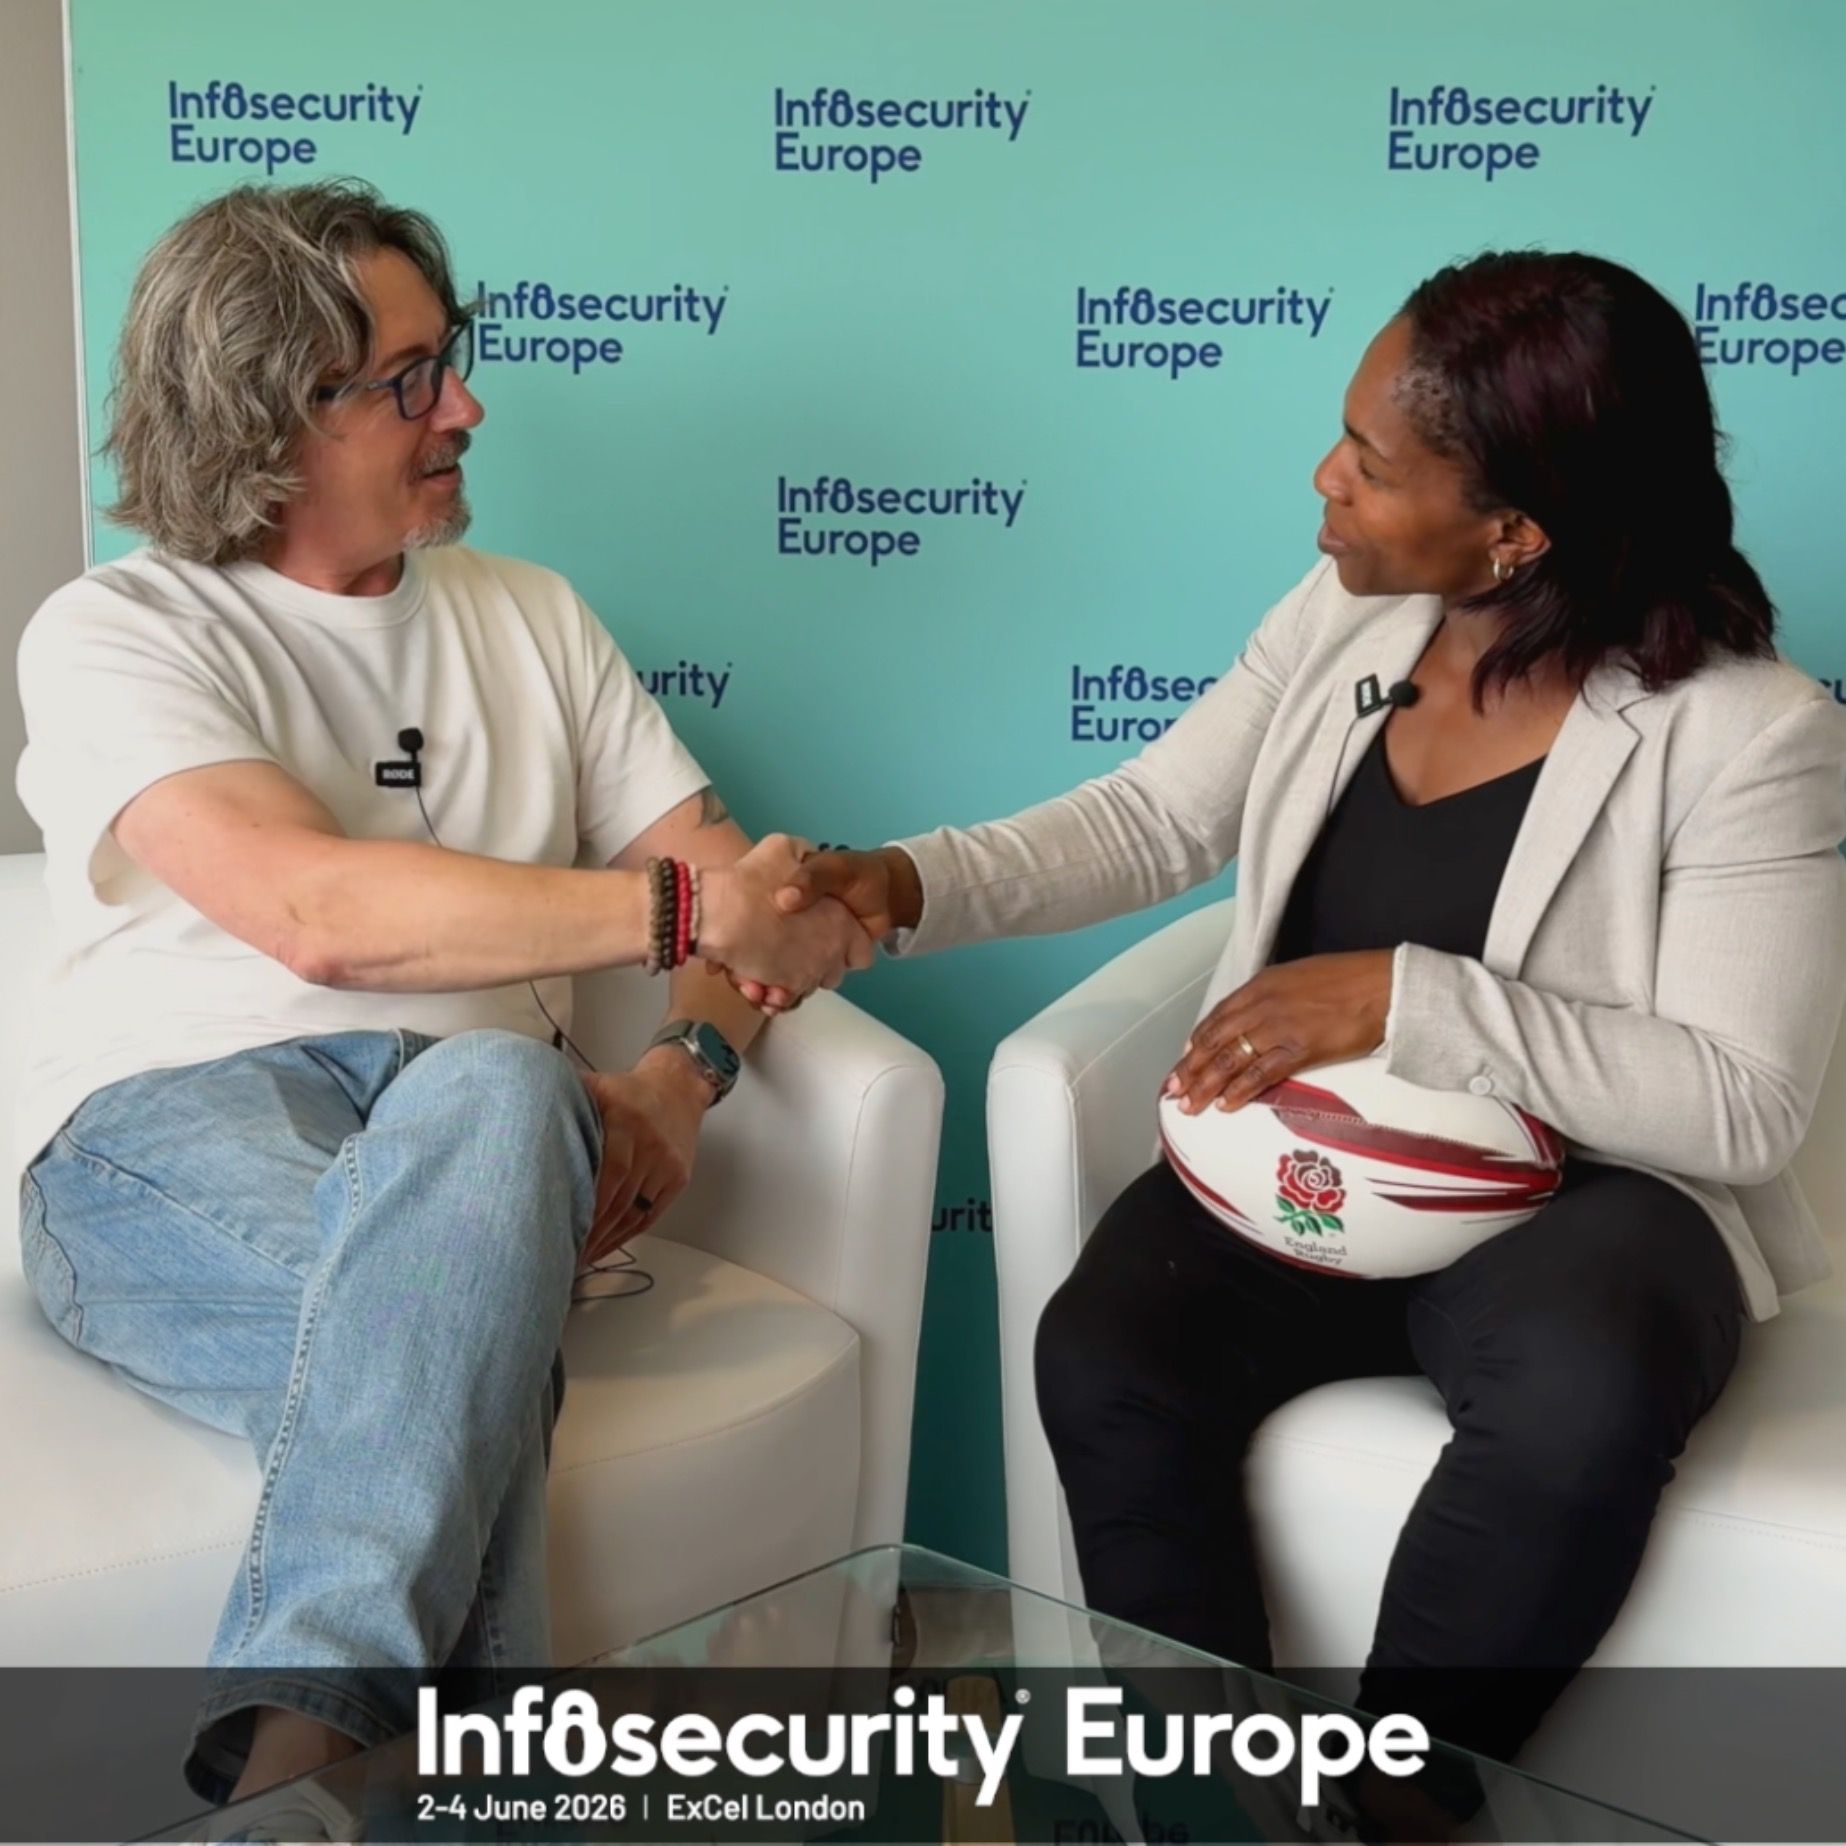
Who Gets to Tell Your Story? Maggie Alphonsi on Strength, Resilience & Owning the Narrative | An Analog Brain In A Digital Age With Marco Ciappelli — On Location at Infosecurity Europe 2026
A rugby World Cup winner walks into a room full of people who defend networks for a living. Maggie Alphonsi joins me to talk about breaking barriers, leading with your strengths, and what changed the day athletes stopped waiting for the back page and started telling their own stories.
📺 Watch | 🎤 Listen | marcociappelli.com
Maggie Alphonsi has spent her life refusing to let other people decide who
Technology Got Safer, But The Smartest Hackers Don't Hack. They Just Ask | An Interview with Lee Clark | An Analog Brain In A Digital Age With Marco Ciappelli — On Location at Infosecurity Europe 2026
PODCAST EPISODE | An Analog Brain In A Digital Age With Marco Ciappelli — On Location at Infosecurity Europe 2026
The most dangerous attacks at Infosecurity Europe 2026 weren't the high-tech ones. Lee Clark of the Retail & Hospitality ISAC sits down with me to explain why the soft target is still a human being — a help desk, a new hire, a phone ringing at dinner — and what stays in our hands as th
Call It What It Is: When Ransomware Becomes Terrorism | An Interview with Cynthia Kaiser | Redefining CyberSecurity With Sean Martin — On Location at InfoSecurity Europe 2026
A ransomware crew can run through your whole company between dinner and dessert. Sean Martin sat down with Cynthia Kaiser — twenty years at the FBI, now leading the Halcyon Ransomware Research Center — on the speed of the threat, the human cost the industry keeps abstracting away, and why a slice of ransomware deserves a harder name than “crime.”
📺 Watch | 🎙️ Listen | seanmartin.com
Put your phone
Cybersecurity Leadership Is a People Problem, Not a Technology Problem | A Redefining CyberSecurity Podcast Conversation with Tera Ladner, Deputy Global Chief Information Security Officer of Aflac
⬥EPISODE NOTES⬥
What does it take to lead a 200-person security organization without coming up through the technical ranks? Tera Ladner, Deputy Global Chief Information Security Officer at Aflac, answers that question by describing a path that runs through information management, e-discovery, and a law degree before it ever reaches the security org chart. The result is a leader who looks at a prog
The Oldest Con, the Newest Tools | An Interview with Sarah Armstrong-Smith At Infosecurity Europe 2026 | An Analog Brain In A Digital Age With Marco Ciappelli
There is a con called the Spanish Prisoner. A letter arrives from a stranger: a wealthy man sits in a foreign jail, and for a small advance to free him, he will reward you many times over. The trick is at least four hundred years old. It is also, give or take a few details, the email sitting in your spam folder this morning.
I keep that in mind whenever someone tells me cybercrime is a technology
The Art of Standing Out When Everything Sounds the Same | A Music Evolves Conversation with Sam Young, DJ and Producer
Show Notes
What happens to creativity when every song, sound, and style is a thumb-tap away? Sam Young has spent more than two decades behind the decks in London, and his answer is blunt: originality is at an all-time low. As a DJ, producer, remixer, and founder of the record label WyldCard, he sits at the exact point where taste, technology, and commerce collide, and he sees a culture increasingl
A Crime Against Time | An Interview with Rik Ferguson | Redefining CyberSecurity With Sean Martin — On Location at InfoSecurity Europe 2026
PODCAST EPISODE | Redefining CyberSecurity With Sean Martin — On Location at InfoSecurity Europe 2026
On Location With Sean Martin And Marco Ciappelli
Adversaries are stealing encrypted data today that they cannot read yet, and storing it until a quantum computer can. Sean Martin sat down with Forescout’s Rik Ferguson to talk about “harvest now, decrypt later,” why Q-Day is closer than the comfor

What Burnout Costs the Cybersecurity People Who Keep Us Safe | An Interview with Bronwyn Boyle | An Analog Brain In A Digital Age With Marco Ciappelli | From Infosecurity Europe 2026
PODCAST EPISODE | An Analog Brain In A Digital Age — On Location at InfoSecurity Europe 2026
On Location With Sean Martin And Marco Ciappelli
Bronwyn Boyle can talk about software vulnerabilities for hours. Talking about her own — the burnout she didn’t recognize until someone named it — turned out to be harder, and more important. We sat down at InfoSecurity Europe to talk about the human cost o

When the Threat Moves Daily and the Law Moves in Years | An Interview with James Morris | Redefining CyberSecurity With Sean Martin — On Location at InfoSecurity Europe 2026
PODCAST EPISODE | Redefining CyberSecurity With Sean Martin — On Location at InfoSecurity Europe 2026
On Location With Sean Martin And Marco Ciappelli
The UK’s threats change by the day. Its laws change over years. Sean Martin sat down with James Morris — former Member of Parliament, now Director of the CSBR — to ask how a government writes cyber policy fast enough to matter, and why “resilience”

Connecting Secure Storage to the Bigger Security Picture | A Brand Highlight at Infosecurity Europe 2026 with Jeanclaude Toma, Chief Executive Officer of Apricorn
At Infosecurity Europe 2026, Jeanclaude Toma, Chief Executive Officer of Apricorn, joins Sean Martin to reframe where secure storage fits in the security conversation. After roughly four decades building hardware-encrypted drives, Apricorn wants the market to treat storage as a security decision rather than a hardware afterthought.
How does a storage device become a security control? Toma points t
Sixty Products, One Engine | A Brand Highlight at Infosecurity Europe 2026 with VimalRaj Sampathkumar, Head of Technical Operations, UK & Ireland of ManageEngine
At Infosecurity Europe 2026 in London, VimalRaj Sampathkumar, Head of Technical Operations for the UK and Ireland at ManageEngine, opens with a sharp observation: the market does not lack tools, it lacks tools that work together. After 16 years with the company, he has watched IT and security teams collect software faster than they can connect it.
ManageEngine, a division of Zoho Corporation, buil
Where Data Sovereignty and Always-On Security Operations Meet | A Brand Spotlight at Infosecurity Europe 2026 with Bill Peterson, Senior Director of Product Marketing of Sumo Logic
At Infosecurity Europe 2026 in London, Bill Peterson, Senior Director of Product Marketing at Sumo Logic, joins us to unpack a tension every regulated security team knows well. When an incident hits, the business has to keep running. At the same time, regulators expect sensitive data to stay in region. For a long time, those two demands have pulled in opposite directions.
Sumo Logic has spent 15 y
Measuring Risk Was Never the Point | A Brand Spotlight at Infosecurity Europe 2026 with Matt Middleton-Leal, Regional Vice President, Northern Europe of Qualys
At Infosecurity Europe 2026, Matt Middleton-Leal, Regional Vice President for Qualys across Northern Europe, joins Sean Martin inside the Risk Operations Center built into the Qualys booth. The premise is blunt: cybersecurity has spent years getting good at measuring risk and almost no time getting good at fixing it. The Risk Operations Center, or ROC, is the Qualys answer to that imbalance.
So wh
When the Boardroom Asks "Are We Okay?" | A Brand Spotlight at Infosecurity Europe 2026 with Ian Schenkel, VP Sales, EMEA & APAC of Intel 471
Something has changed at the board level. Recorded in the media room at Infosecurity Europe 2026 in London, Ian Schenkel, VP Sales, EMEA & APAC of Intel 471, describes directors who no longer take security on faith. After a year of headline breaches from Jaguar Land Rover to Marks and Spencer and the Co-op, leadership wants proof rather than promises.
What does the board actually want to know? A s
Seeing What Your EDR Can't | A Brand Spotlight at Infosecurity Europe 2026 with Matt Ellison, Director of Sales Engineering EMEA & APAC of Corelight
At Infosecurity Europe 2026 in London, Matt Ellison, Director of Sales Engineering EMEA & APAC at Corelight, joins Sean Martin to unpack the visibility gap widening across security operations. The SOC is either drowning in data or missing the data that matters most. Corelight, custodian of the open-source Zeek project, builds a platform that turns raw network traffic into evidence teams can actual
Resilience Is the New Compliance: Why Recovery Is the Real Test of Cyber Readiness | A Brand Spotlight at Infosecurity Europe 2026 with Pete Hannah, VP of Sales, Western Europe of Object First
At Infosecurity Europe in London, Pete Hannah, VP of Sales for Western Europe at Object First, joins Sean Martin to reframe a question many organizations still get wrong. The issue is not only how to keep ransomware out, but how quickly you can recover once it gets in. With Europe's regulatory landscape tightening, that distinction is becoming the difference between disruption and disaster.
What d
The Business of Extortion — Storytelling, Ransomware, and the BBC's Cyber Hack | Geoff White | PODCAST EPISODE | An Analog Brain In A Digital Age — On Location at InfoSecurity Europe 2026 On Location With Sean Martin And Marco Ciappelli
There is a moment in every conversation about cybercrime when the criminal stops being a shadow and becomes a person with a desk, a calendar, and a complaint about Monday. That moment is the one that interests me.
For years I’ve been told cybersecurity is a technical problem. Firewalls, patches, acronyms nobody outside the room understands. And it is, partly. But sit with Geoff White for fifteen m
Proof of Impact | Lens Four by Sean Martin | Read by TAPE9
⬥EPISODE NOTES⬥
Almost nothing got said on the stages at Global Citizen NOW 2026 without a number behind it. $47 million toward a $100 million education fund. 27 organizations funded. 1,500 jobs from a single restoration effort. 18 million lives reached in one campaign. The headline was the money. The tell was quieter — a pilot to verify, record, and monitor every donated dollar with AI and blockc
When Patient Records, Powerlines, and Prompts All Lead to the Same Risk | A Redefining CyberSecurity Podcast Conversation with Gil Bashe, Chair, Global Health and Purpose of FINN Partners
⬥EPISODE NOTES⬥
The healthcare system is, by some measures, the most targeted sector in cybersecurity. Patient records get lifted, hospitals get held for ransom, and the supposed protections often look more like antiquated friction than modern defense. Gil Bashe, Chair of Global Health and Purpose at FINN Partners, joins Sean Martin to explore why the systems meant to protect people's most sensiti
Telling the Stories of Cybercrime | An Interview with Geoff White | An Analog Brain In A Digital Age With Marco Ciappelli
PODCAST EPISODE | An Analog Brain In A Digital Age With Marco Ciappelli
Geoff White goes where organized crime and technology cross, and he comes back with stories. In this one he announces his newest BBC series — the rise and fall of the Conti ransomware gang — and we get into the thing underneath all of it: how you make a crime nobody can see feel real to people who will never see it.
📺 Watch |
After RSAC Conference 2026, Reflecting on Agentic AI, Community, and the Evolution of Cybersecurity | A Brand Highlight at RSAC Conference 2026 with Tony Anscombe, Chief Security Evangelist of ESET
Agentic AI was the theme that pulled away from the pack at RSAC Conference 2026. Tony Anscombe of ESET makes the case that once AI shifts from being directed by humans to operating with its own objectives and logic, the security surface changes with it, and organizations are being forced to rethink what they protect and how.
At the show, ESET announced two products that meet that moment head on. T
Tackling the Trust Crisis: Inside the 2026 HITRUST Trust Report | A Brand Spotlight Conversation with Vincent Bennekers, VP of Quality at HITRUST | Hosted by Sean Martin
Cybersecurity assurance was supposed to give boards, regulators, customers, and partners a clear answer to one question: can the security of the organizations they depend on actually be trusted? In 2026, that answer is harder than ever to come by. Supply chains are sprawling, attackers are pivoting through third parties, and too many assurance reports still rely on questionnaires, self-attestation
The Vendor You Cannot Name | Lens Four by Sean Martin | Read by TAPE9
⬥EPISODE NOTES⬥
The most dangerous sentence in cybersecurity disclosure right now is "no evidence of unauthorized access to our network." It is technically true. It is also operationally hollow. The customer whose data is on a leak site does not care which network it left from. The plaintiff in Bexar County does not care. The regulator about to receive a federal incident report under a 72-hour clo

The Artemis Generation (feat. Dr. Polanski, Lowell Observatory) | Stories From Space Podcast With Matthew S Williams
Host | Matthew S Williams
For more podcast Stories from Space with Matthew S Williams, visit: https://itspmagazine.com/stories-from-space-podcast
______________________Episode Notes
From Apollo to Artemis: What Lowell Observatory Knows About Going Back to the Moon
Fifty years is a long time to forget how to do something. That is, more or less, where NASA stood when Artemis 1 left the pad — and whe
Book: Deep Future — Creating Technology That Matters | An Interview with Pablos Holman | An Analog Brain In A Digital Age With Marco Ciappelli
PODCAST EPISODE | An Analog Brain In A Digital Age With Marco Ciappelli
Pablos Holman has built spaceships, zapped malaria-carrying mosquitoes with a laser, earned thousands of patents, and is now betting his venture capital on the inventors Silicon Valley forgot to fund. His new book, Deep Future: Creating Technology That Matters, is a call to arms against a tech industry that got drunk on softwa
Recommended
این نقطه
TED Business
Dark Night Tales with Brian King
Fantasy Flex
زن بودن

Medicine with Meaning
Yours Truly Johnny Dollar Collection
Take Back Your Health®
CBS Radio Mystery Theater | Old Time Radio
Solved Murders - True Crime Stories
紐約鳥|New York Aperture
The Swerve Podcast: Obscure Topics | Conspiracy Theories
