The InfoSec Control Room
The InfoSec Control Room is a cybersecurity podcast hosted by Taher Amine ELHOUARI, focusing on governance, risk, compliance, resilience, and CISO-level decision-making. It explores the gap between what organizations believe they have in place and what actually works during incidents, audits, regulatory questions, and risk-based decisions. Topics include information security, GRC, CISO leadership, ISO standards, cyber resilience, privacy, incident response, CSIRT operations, security awareness, and regulatory expectations. The core premise is that most organizations have a governance problem that manifests as security. The show targets CISOs, security leaders, GRC professionals, auditors, consultants, and practitioners.
Episodes
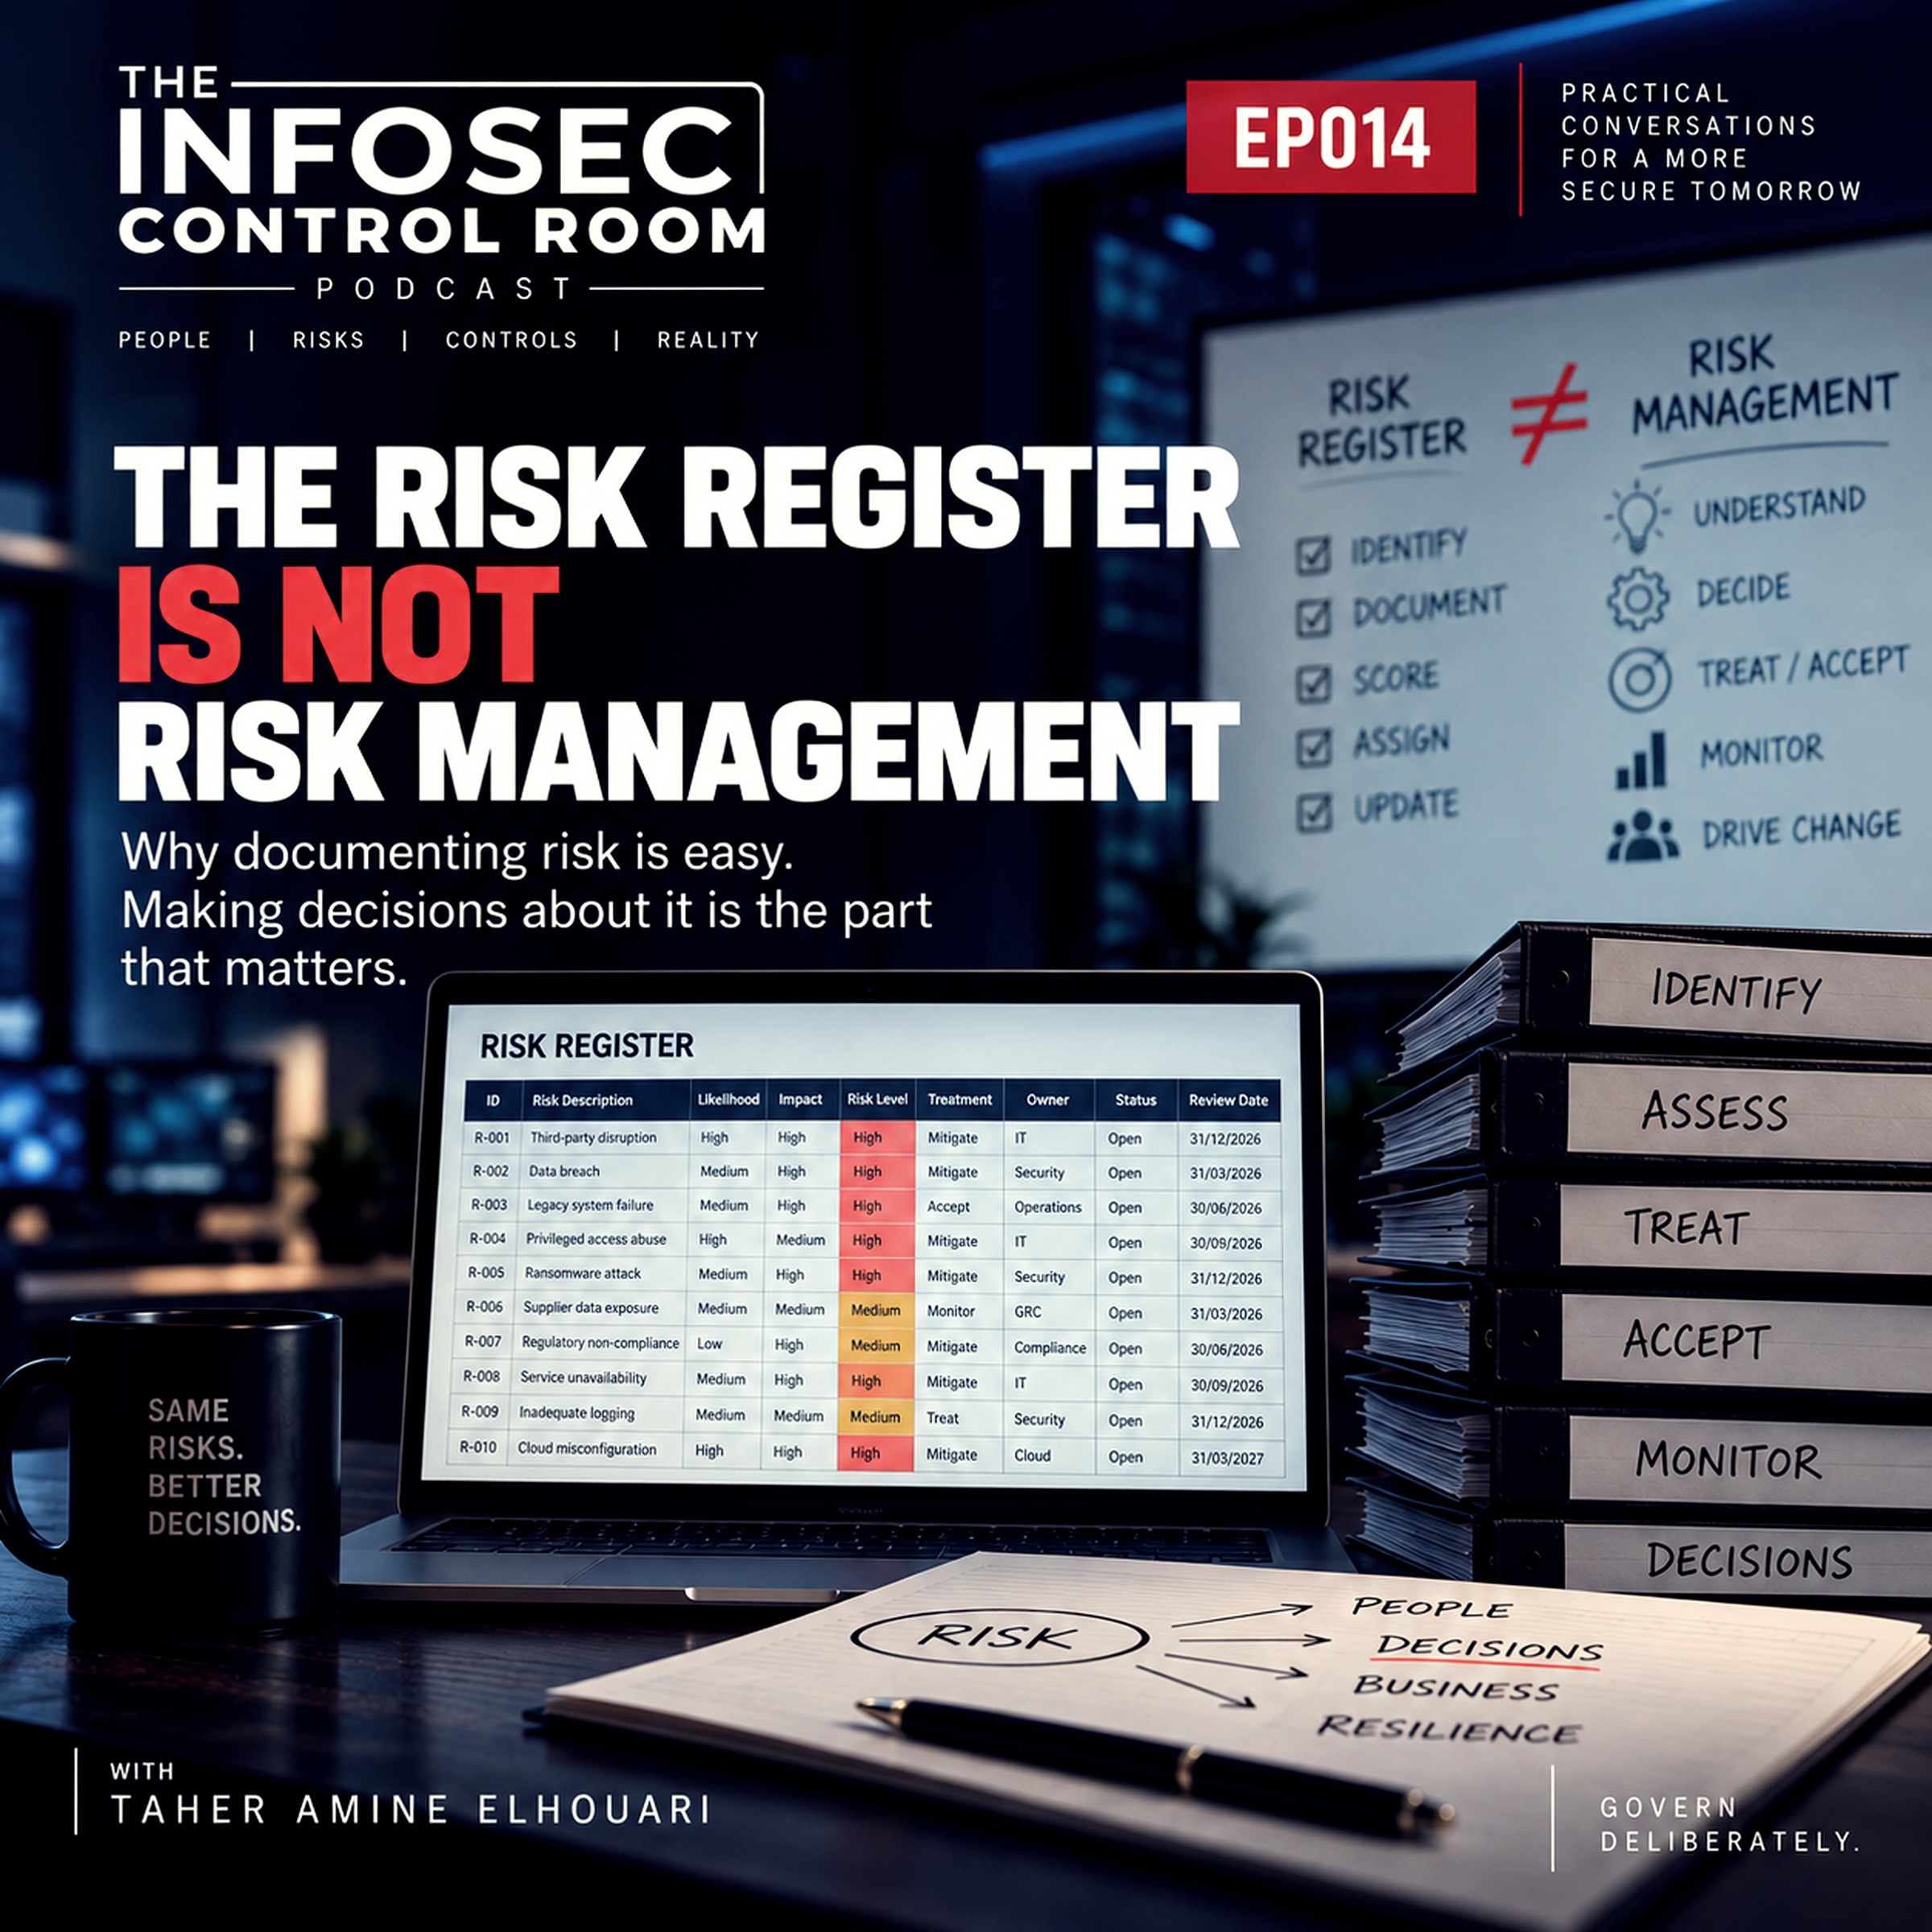
EP014: The Risk Register Is Not Risk Management
In EP014 of The InfoSec Control Room, I challenge one of the most common habits in cybersecurity governance: treating the risk register as if it were risk management itself.A register can be detailed, perfectly formatted, fully scored, assigned, reviewed, and still have very little impact on the organization. The real question is not whether the risk exists in Excel or in a GRC platform. The real
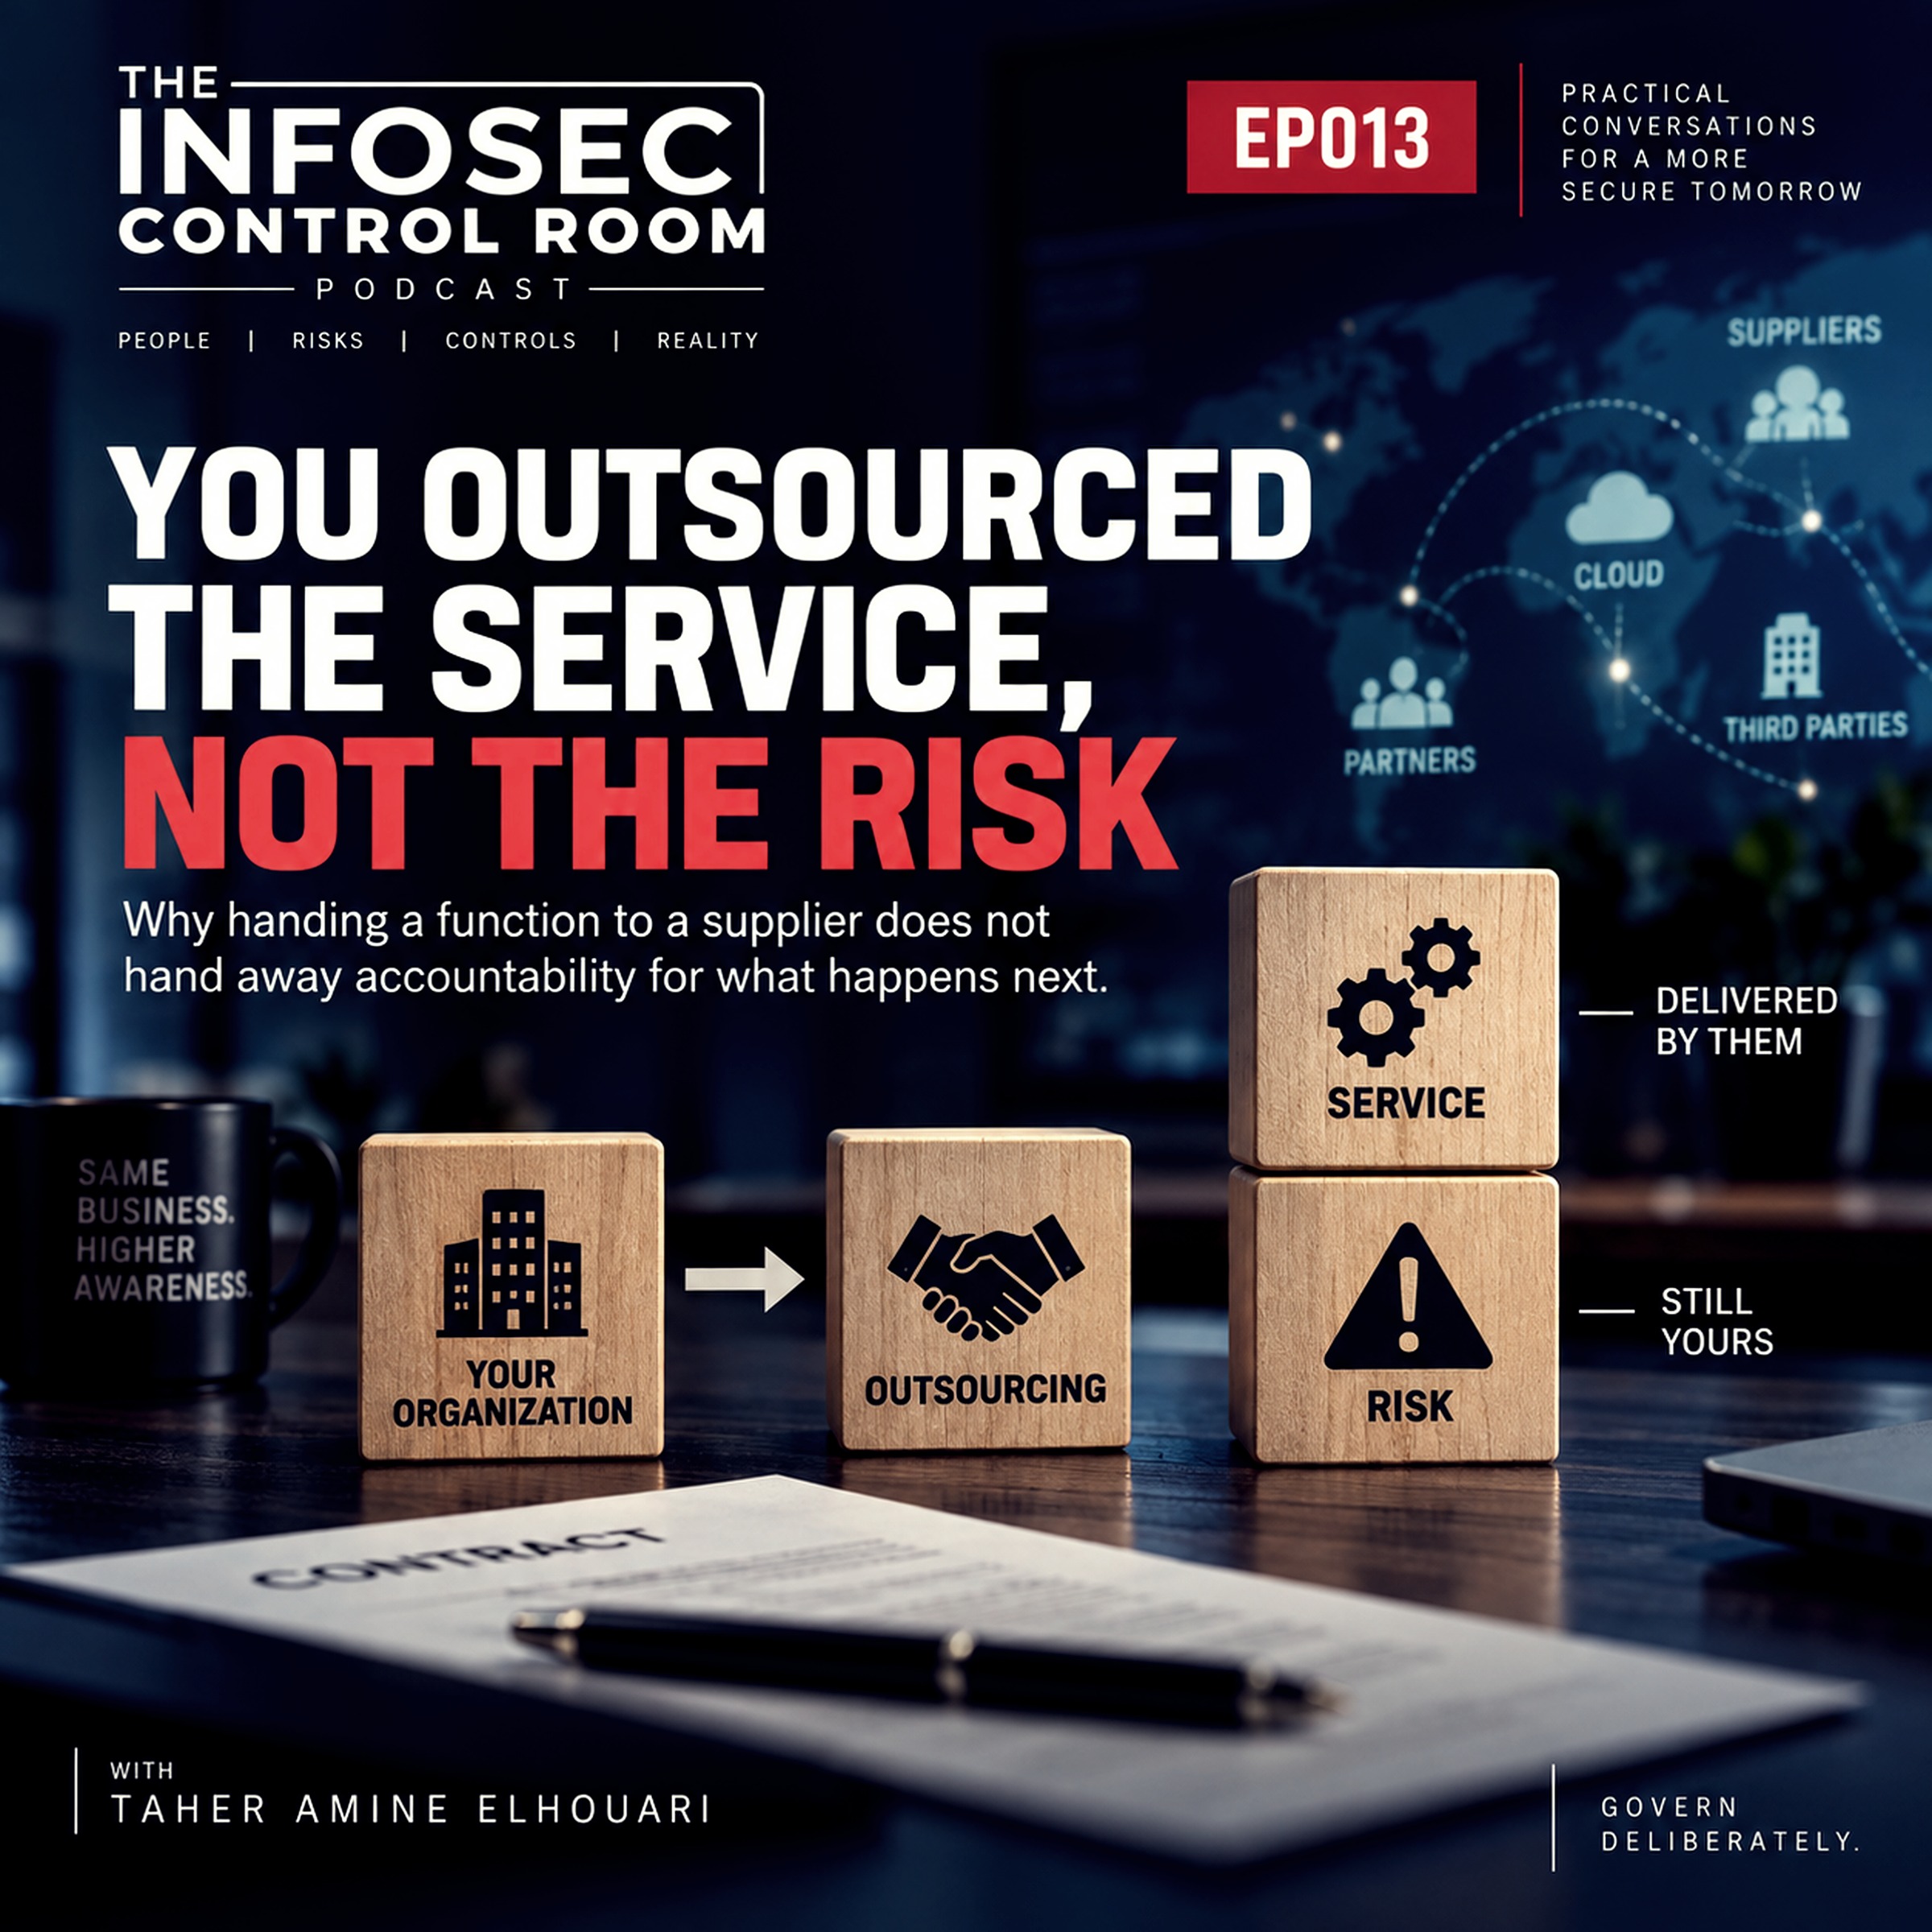
EP013: You Outsourced the Service, Not the Risk
In EP013 of The InfoSec Control Room, I look at one of the most common misconceptions in modern cybersecurity and business operations: the idea that outsourcing a service also outsources the risk.Organizations rely on cloud providers, SaaS platforms, MSSPs, payroll processors, payment providers, telecom operators, external developers, consultants, and many other partners. That is normal. The probl
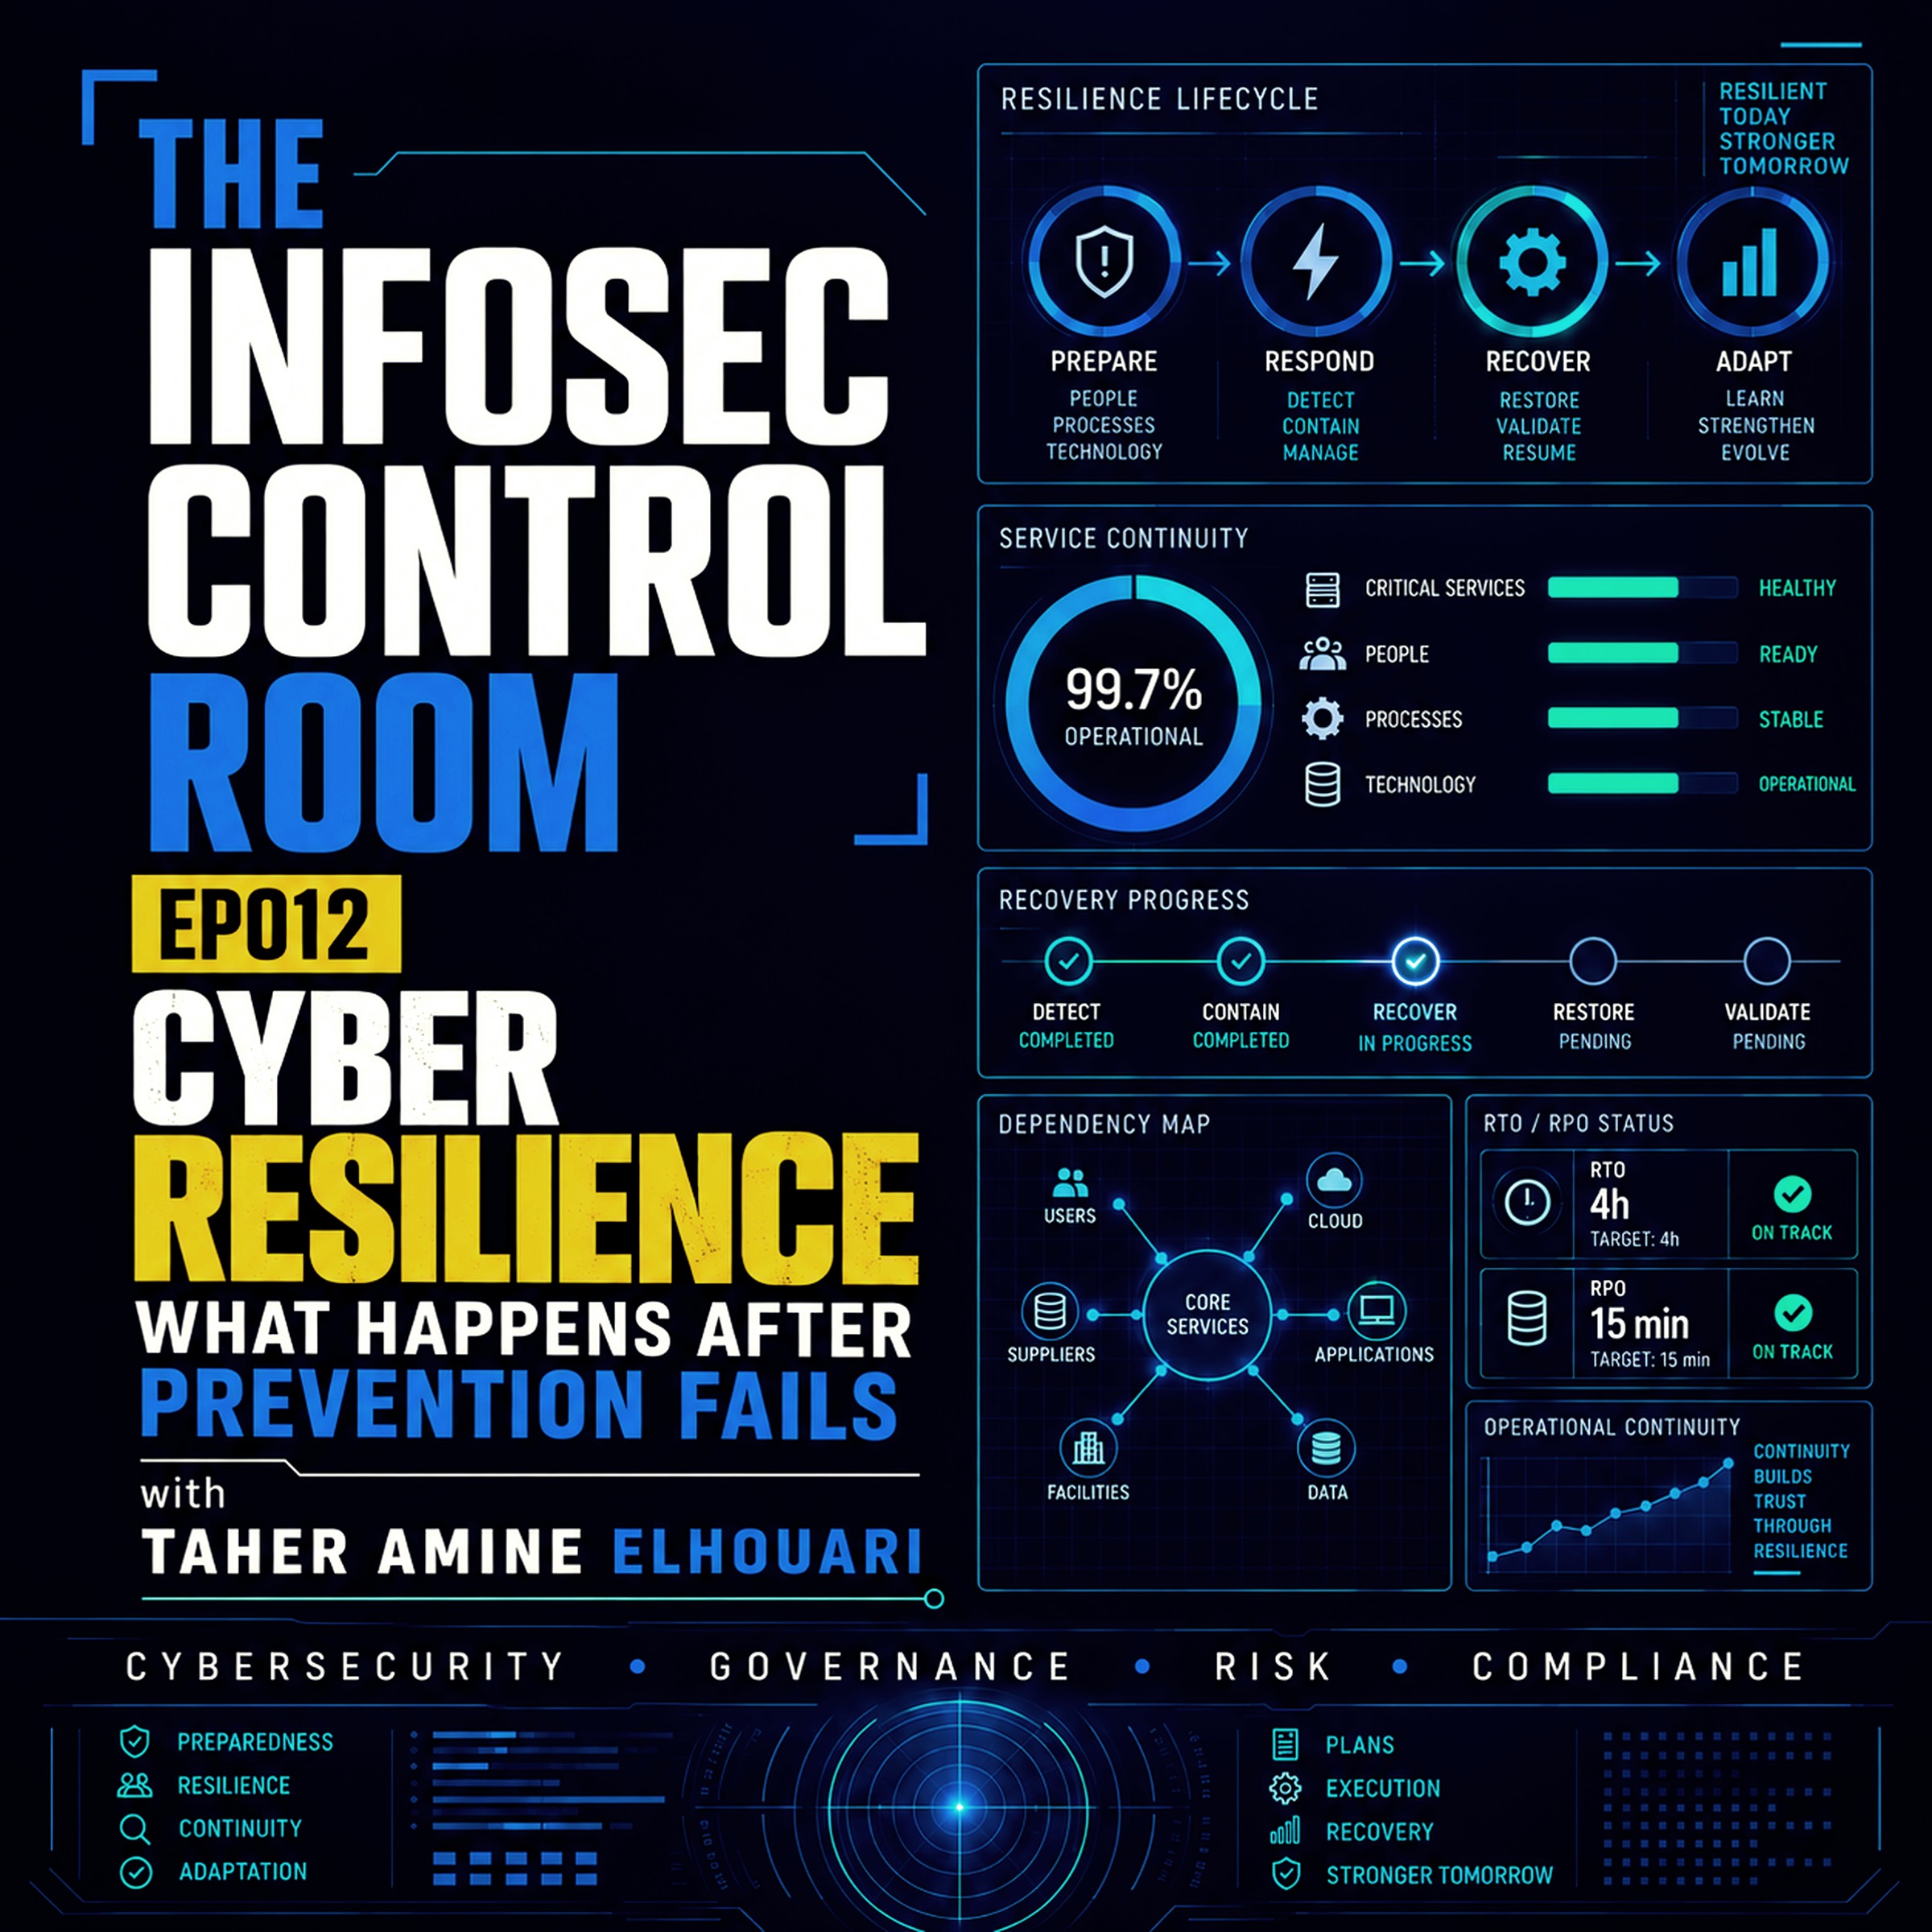
EP012: Cyber Resilience — What Happens After Prevention Fails
In EP012 of The InfoSec Control Room, I explore what happens when prevention is no longer enough.Security programs spend enormous effort trying to stop incidents, outages, compromises, and failures before they happen. That work matters. But no control is perfect, no environment is static, and eventually something will get through, break, fail, or become unavailable.The real question then becomes:
EP011: ISO 27001 Is Not the Certificate on the Wall
In EP011 of The InfoSec Control Room, I look at what happens after an organization earns its ISO/IEC 27001 certificate.Certification can be valuable. It can bring structure, discipline, credibility, and a much clearer way to manage information security. But problems begin when the certificate becomes the objective instead of the result of a functioning management system.This episode explores the d
EP010: The Board Does Not Need Another Cyber Dashboard
In EP010 of The InfoSec Control Room, I look at a problem that appears in almost every cybersecurity program: organizations produce more security data than ever, yet leadership still struggles to understand what actually matters.Boards are shown vulnerabilities, alerts, patch percentages, phishing results, incidents, audit findings, risk scores, trend lines, heat maps, and plenty of red, amber, an
EP009: Your CSIRT Is Not Ready Just Because It Exists
In EP009 of The InfoSec Control Room, I look beyond the simple statement, “We have a CSIRT,” and ask the question that actually matters: what can that team really do when something serious happens?A CSIRT can exist on the organization chart, have assigned staff, procedures, tooling, and even a dedicated mailbox, while still being poorly prepared for a real incident. Readiness comes from much more
EP008: Stop Lying to Yourself About Cyber Maturity
In EP008 of The InfoSec Control Room, Taher Amine ELHOUARI takes on one of cybersecurity’s favorite activities:Measuring maturity.Organizations love maturity scores.3.4 out of 5. Level 4. Managed. Optimized. Green dashboard.Everything looks reassuring.But what does the score actually mean?Can the organization detect an attacker?Can it restore a critical service?Can it revoke privileged access quic
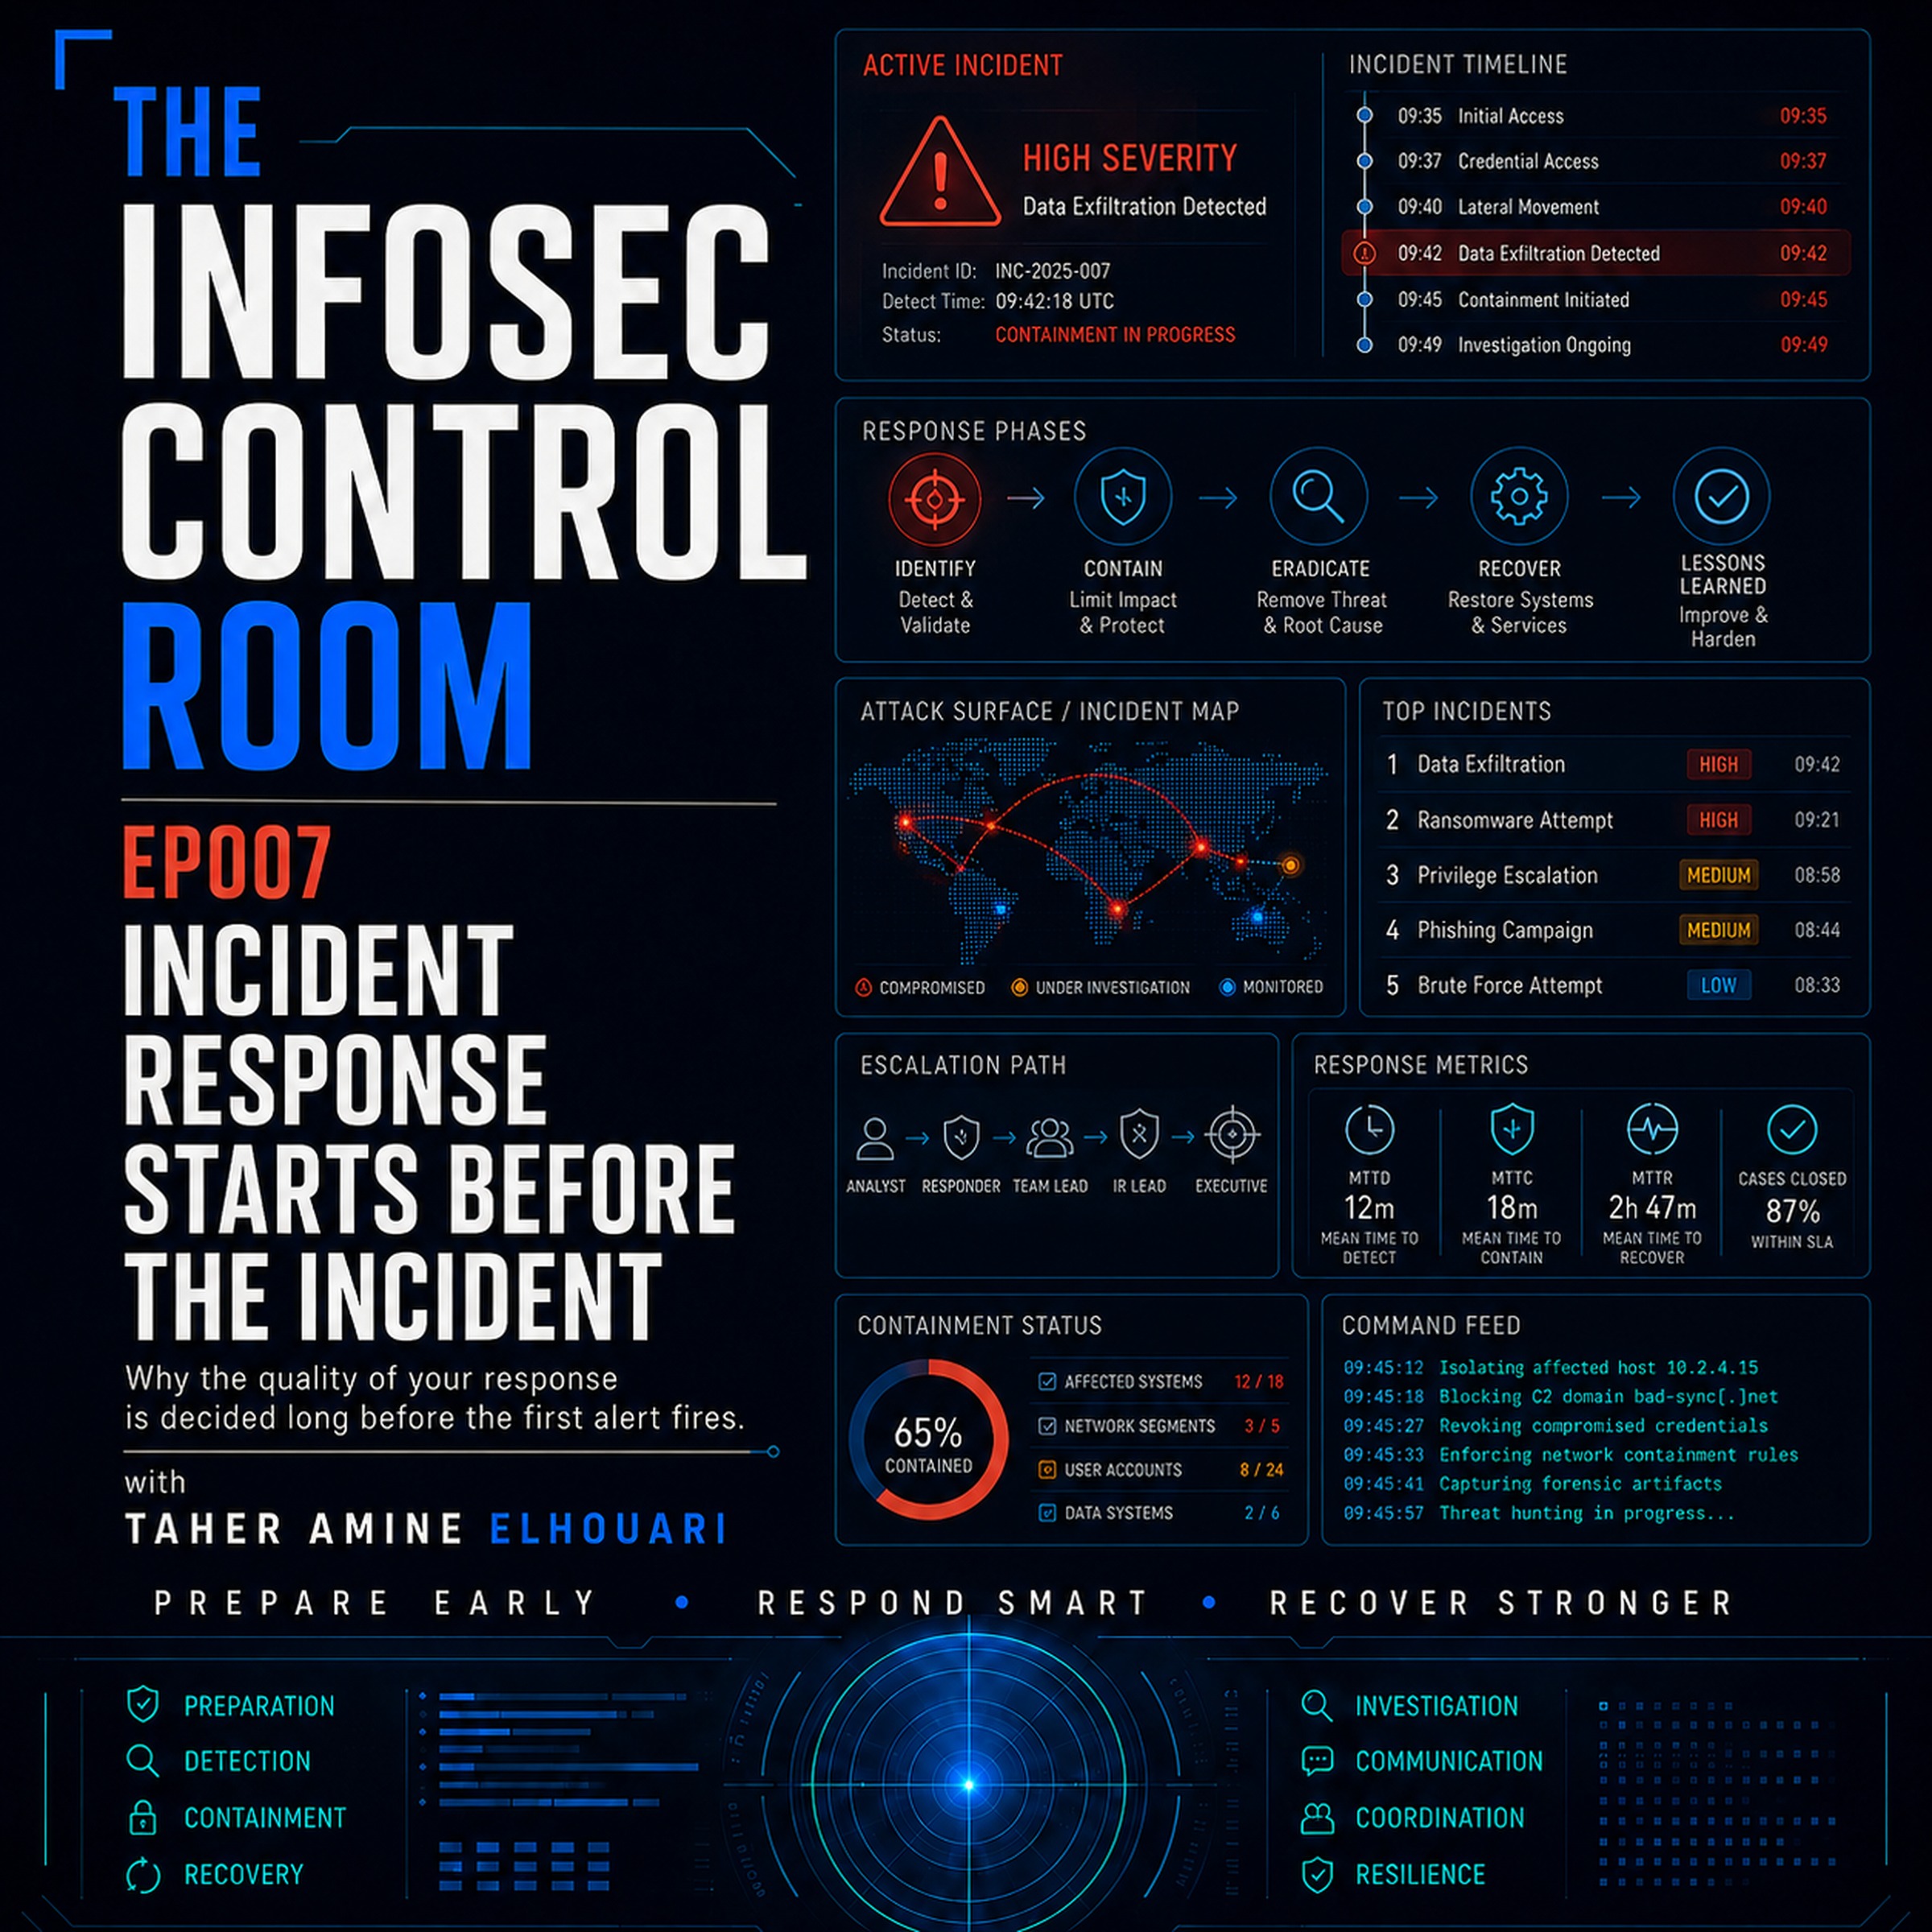
EP007: Incident Response Starts Before the Incident
In EP007 of The InfoSec Control Room, Taher Amine ELHOUARI explores a simple but often misunderstood reality:Incident response does not begin when the incident happens.By the time the first serious alert fires, many of the decisions that will determine the quality of the response have already been made.Who has authority to isolate a critical system?Who can declare a major incident?Who decides whet
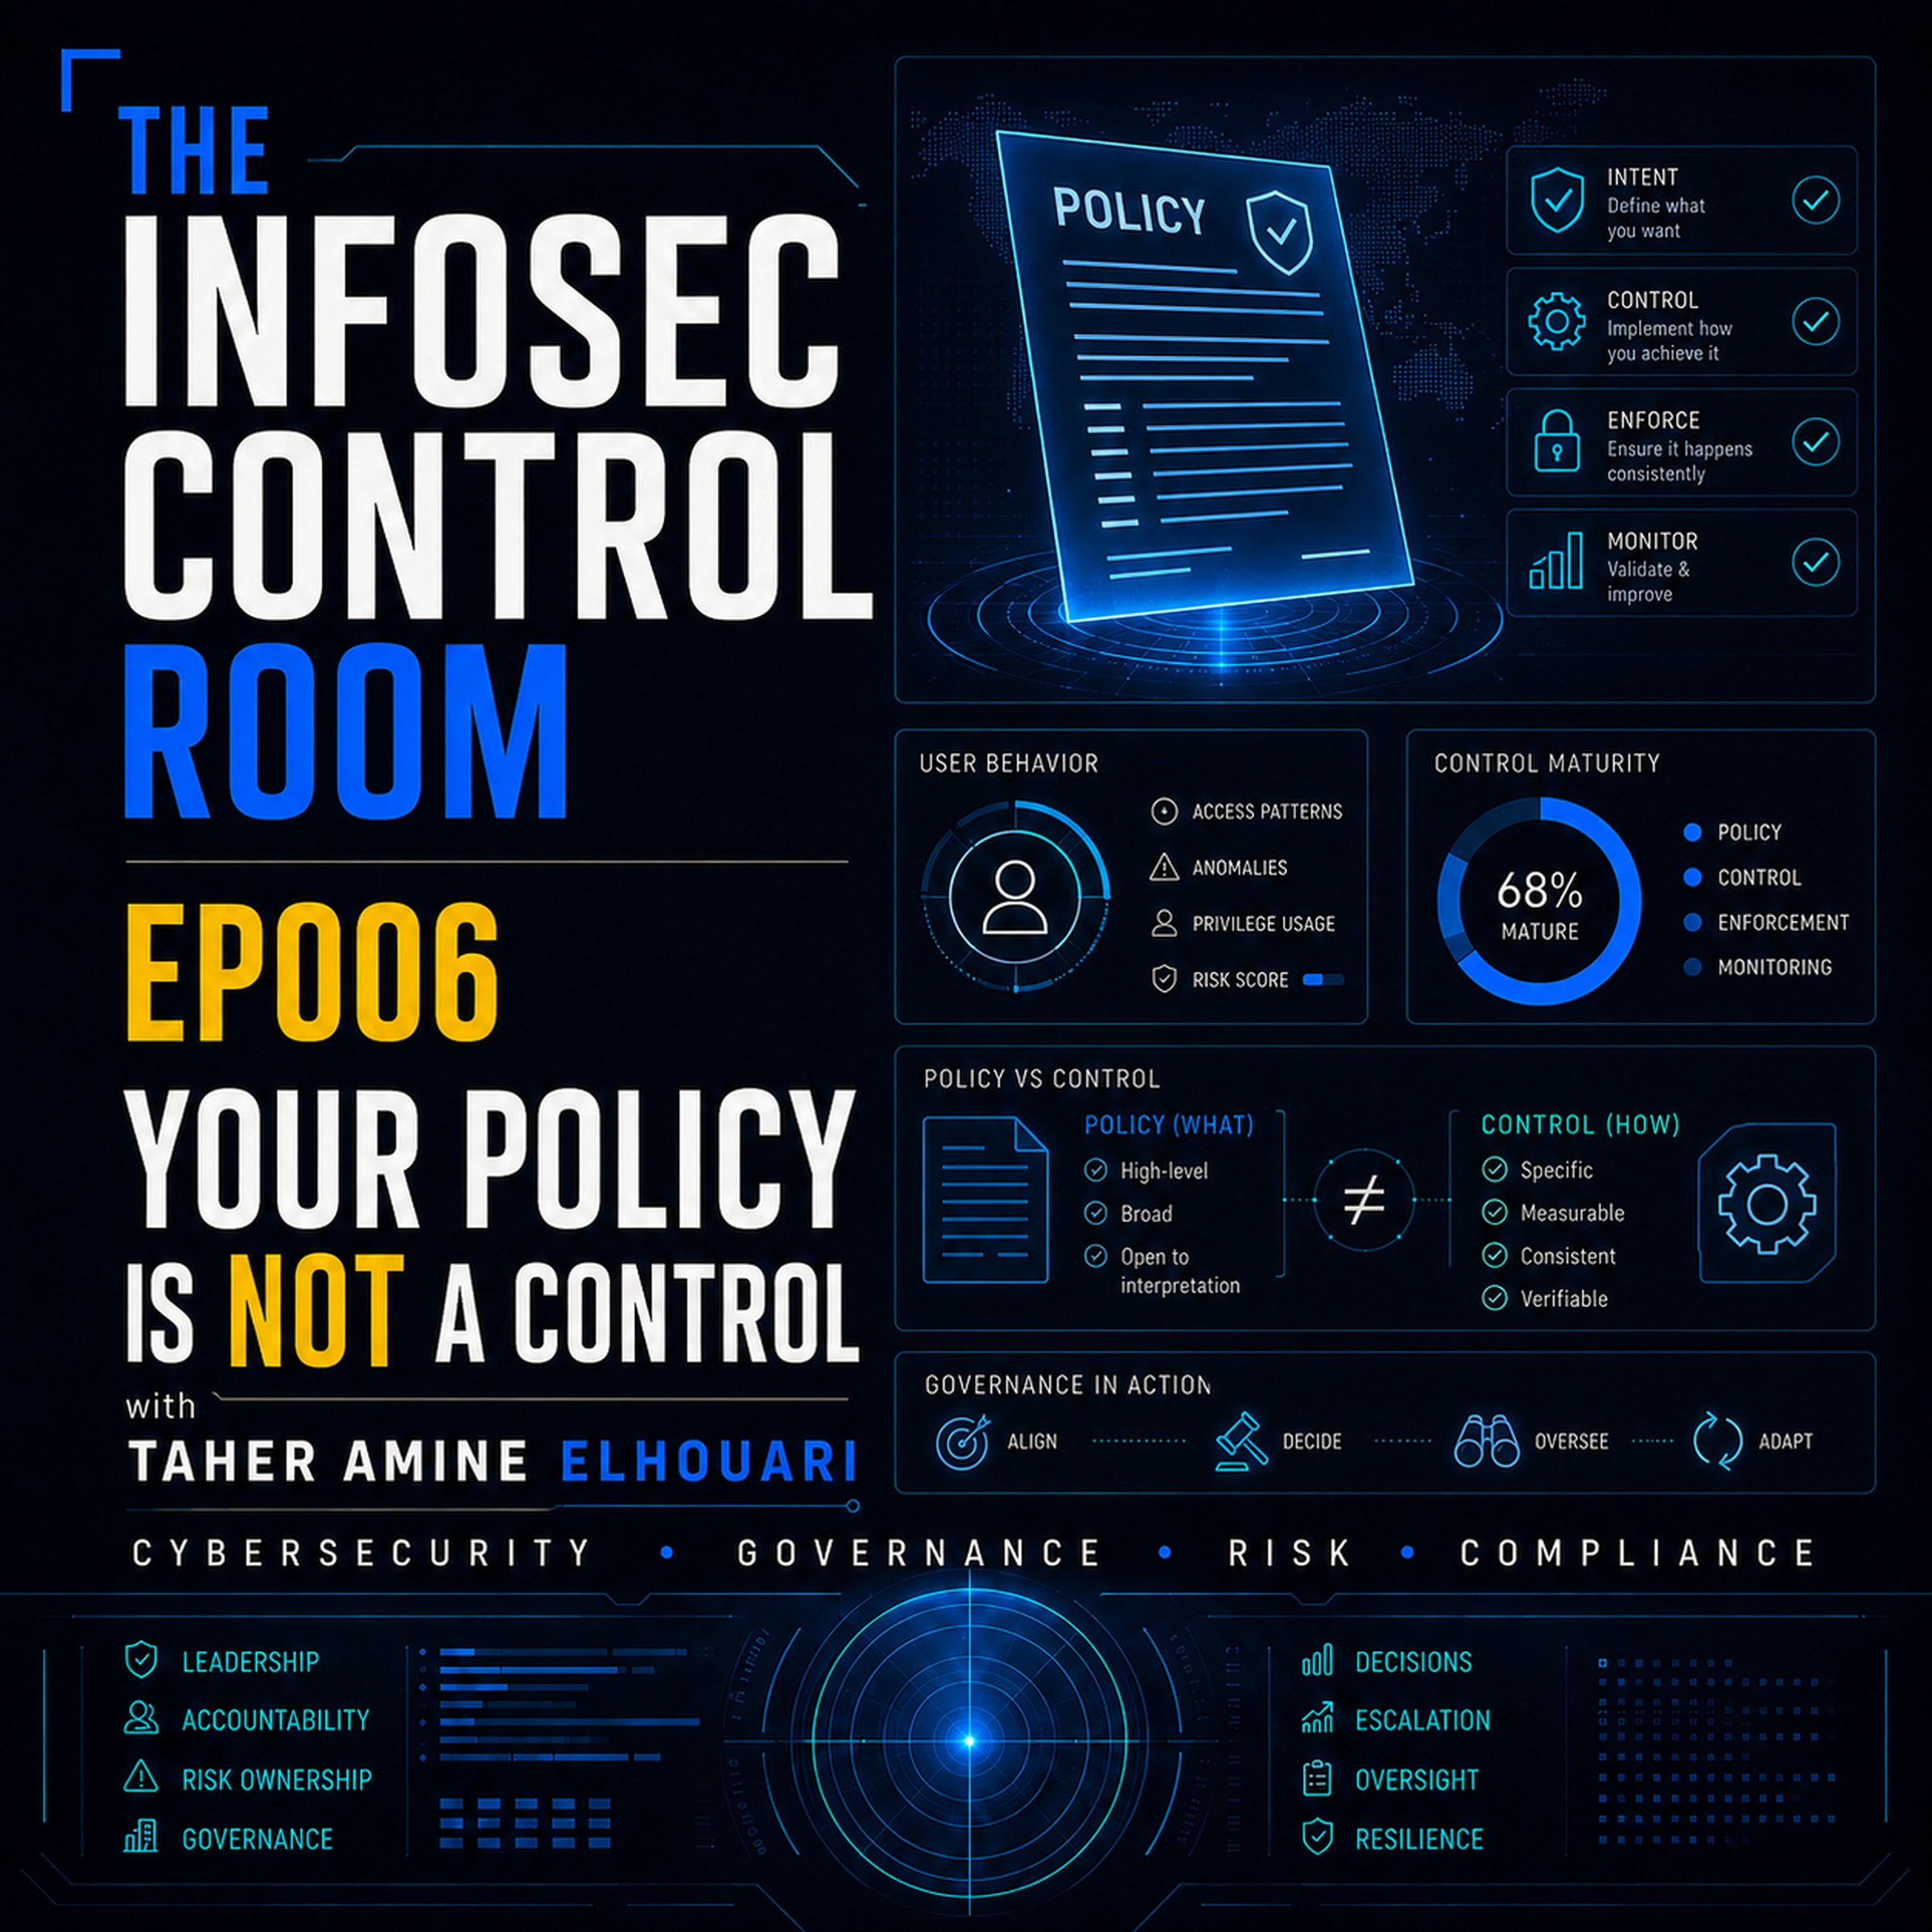
EP006: Your Policy Is Not a Control
In EP006 of The InfoSec Control Room, Taher Amine ELHOUARI takes on one of the most common misconceptions in information security governance:Having a policy does not mean you have a control.An organization can have approved information security policies, access control requirements, data classification rules, acceptable-use standards, incident procedures, and beautifully version-controlled documen
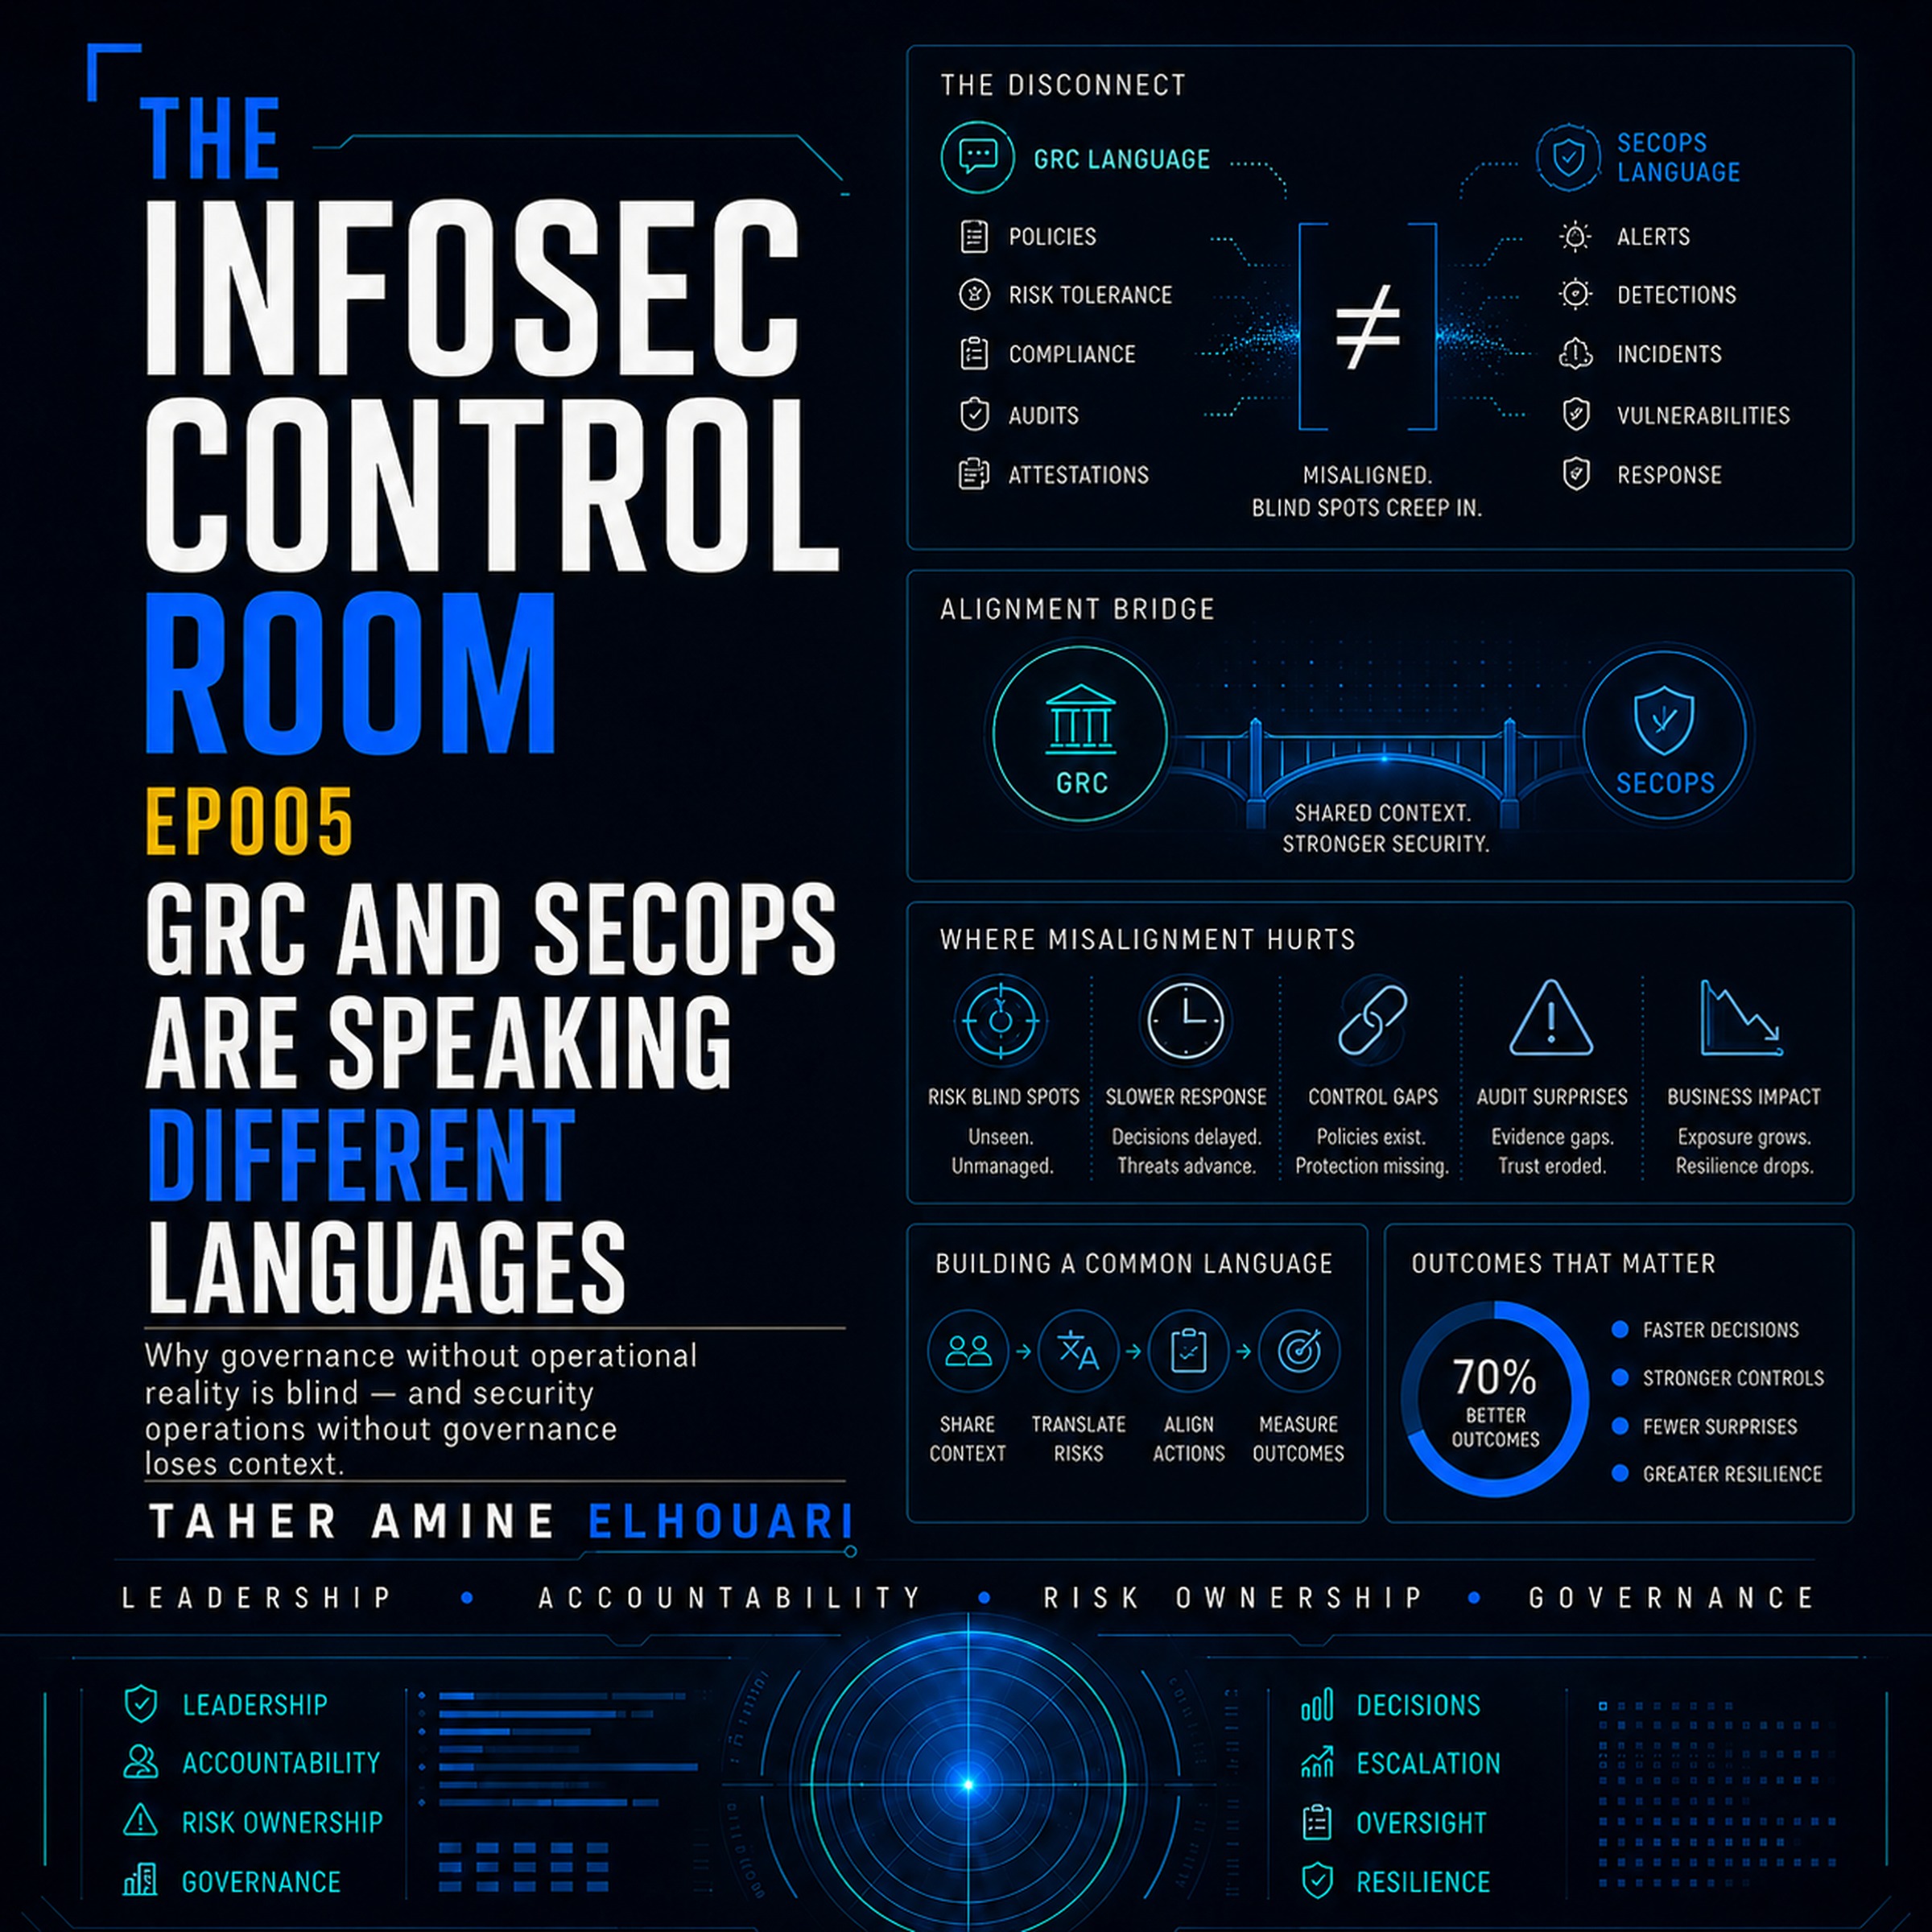
EP005: GRC and SecOps Are Speaking Different Languages
In EP005 of The InfoSec Control Room, Taher Amine ELHOUARI explores one of the most important — and often underestimated — relationships inside a cybersecurity program: the connection between GRC and Security Operations.In many organizations, GRC and SecOps behave like two neighboring countries.GRC speaks in controls, policies, risk registers, audit findings, evidence, compliance obligations, and
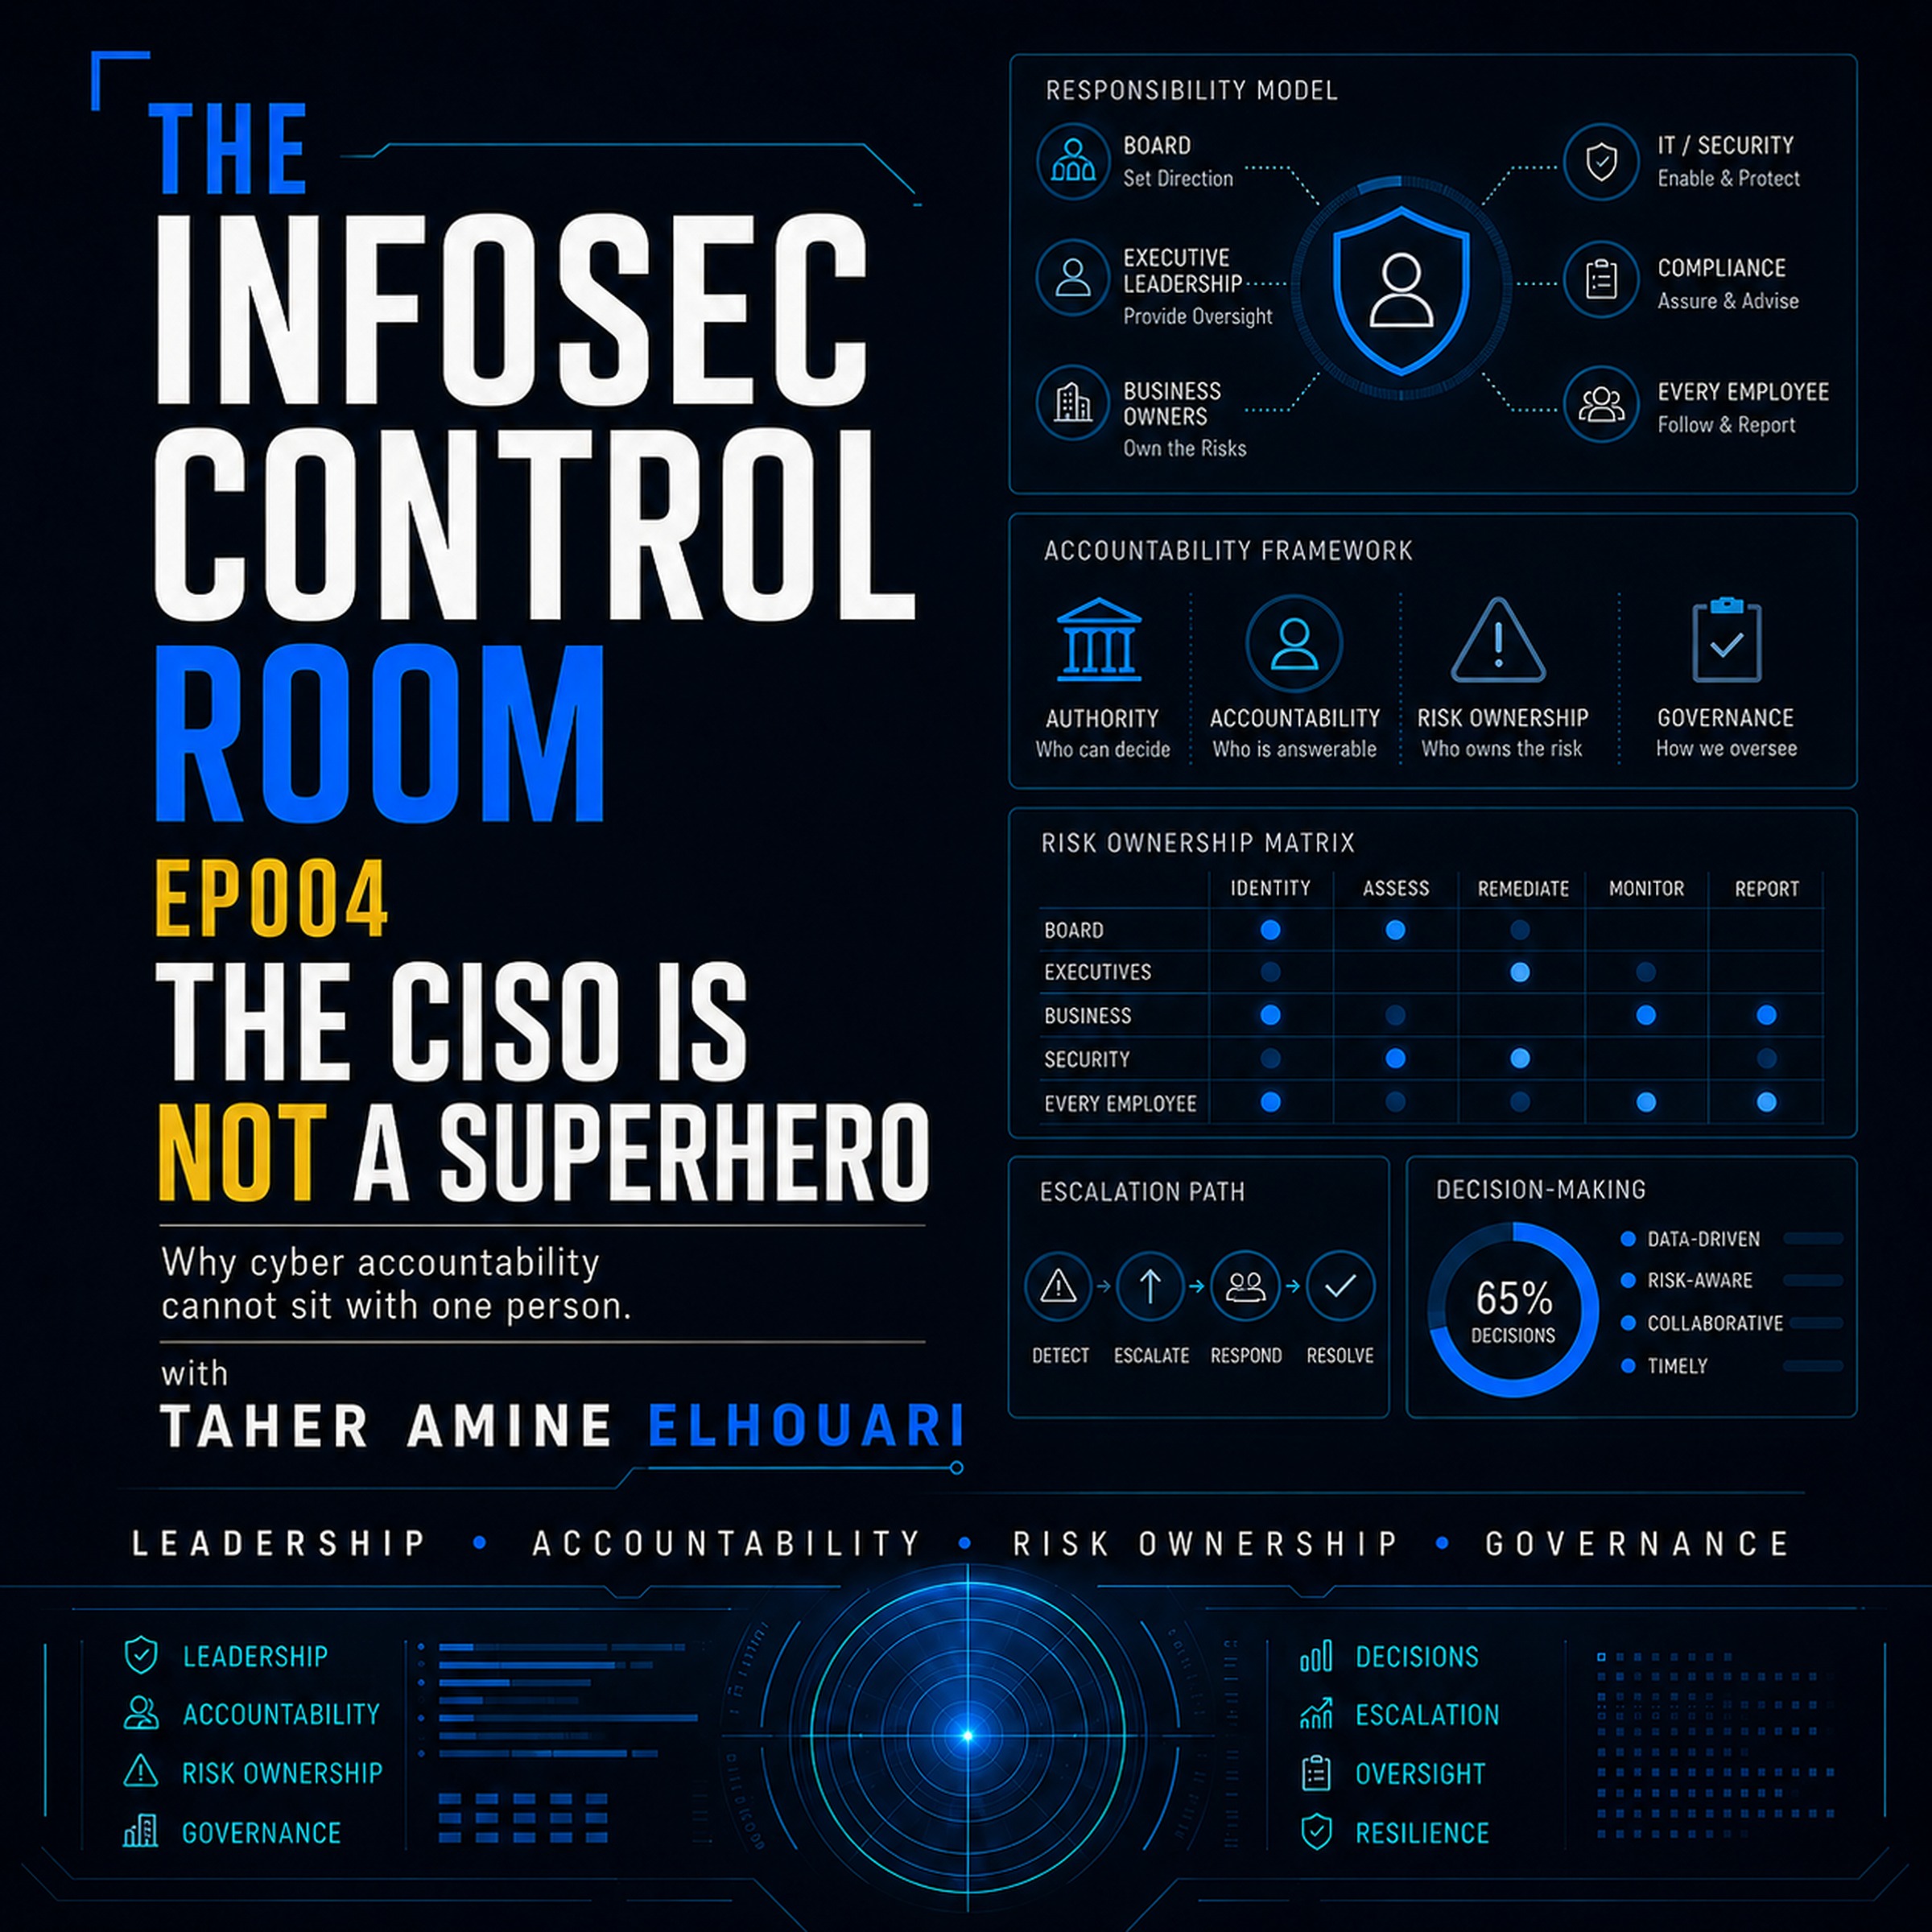
EP004: The CISO Is Not a Superhero
In EP004 of The InfoSec Control Room, Taher Amine ELHOUARI challenges one of the most common and damaging assumptions in cybersecurity governance:“We have a CISO. Cybersecurity is their responsibility.”It sounds reasonable until you start asking who actually creates, owns, accepts, and manages cyber risk across an organization.A business unit launches an application without involving security. Pro
EP003: Compliance Is Not Control
In EP003 of The InfoSec Control Room, Taher Amine ELHOUARI explores the uncomfortable gap between being compliant and actually being in control.An organization can have approved policies, completed audits, risk registers, procedures, evidence, management reviews, and even certifications on the wall; while still struggling to answer very simple questions:Can we actually restore our critical systems
EP002: The Real Reason Security Programs Fail
In this episode of The InfoSec Control Room, Taher Amine ELHOUARI explores one of the core ideas behind the podcast: many security programs do not fail because there is no cybersecurity activity. They fail because that activity is not governed, owned, measured, or improved properly.The episode explains why security failures are often symptoms of deeper structural issues: unclear accountability, we
EP001: Welcome to The InfoSec Control Room
In this first original episode of The InfoSec Control Room, Taher Amine ELHOUARI formally introduces the podcast, the story behind it, and the core philosophy that will guide future episodes.This opening episode explains why The InfoSec Control Room exists, who it is for, and why cybersecurity must be understood beyond tools, incidents, vulnerabilities, frameworks, and technical controls.Taher int
Media Archive: Building Cyber Resilience Beyond Compliance | Full Webinar | Taher Amine ELHOUARI - iExperts
Compliance may demonstrate that security requirements have been addressed. Cyber resilience demonstrates that governance, people, processes, and technology can continue to operate under real pressure.This special webinar edition of The InfoSec Control Room presents the complete audio recording of my latest iExperts session: BUILDING CYBER RESILIENCE BEYOND COMPLIANCE.During this session, I examine
Media Archive: Conformity Assessment Meets Cybersecurity | FIRST & AfricaCERT Symposium 2025
In this Media Archive episode of The InfoSec Control Room, Taher Amine ELHOUARI shares his conference session from the FIRST & AfricaCERT Symposium 2025 in Mauritius: “Conformity Assessment Meets Cybersecurity: Building a Common Language Between Auditors and Analysts.”This session explores one of the most important gaps in cybersecurity assurance: why organizations can appear compliant on pape
Media Archive: The Hidden Face of Cyber Extortion on Algerian National TV
In this Media Archive episode of The InfoSec Control Room, Taher Amine ELHOUARI shares a national television intervention from Taqassi — Season Five, produced by Algerian National Television, focused on cyber extortion and online blackmail. This episode explores one of the most dangerous and rapidly growing crimes in the digital space: how attackers exploit psychology, privacy gaps, digital habits
Media Archive: From Chaos to Control — Building and Maturing CERT/CSIRT Teams
In this Media Archive episode of The InfoSec Control Room, Taher Amine ELHOUARI shares a full masterclass titled “From Chaos to Control: Understanding, Building, and Maturing Your Cyber Response Team.” This session focuses on the fundamentals, structure, and maturity of cyber response teams, including CERTs, CSIRTs, operational readiness, field tactics, and the architecture of cyber resilience.The
Media Archive: Cybersecurity Challenges, Certifications, and Career Lessons
In this Media Archive episode of The InfoSec Control Room, Taher Amine ELHOUARI shares a guest podcast interview originally featured on Lweirday Experience.This conversation explores cybersecurity from multiple angles: fundamentals, career development, certifications, ethical hacking, development security, red/blue/purple teaming, cybersecurity teams, ICS and SCADA security, standards, and the cha
Media Archive: Information Security — A Leading Experience
In this Media Archive episode of The InfoSec Control Room, Taher Amine ELHOUARI shares a long-form interview hosted by Adel BOUROUIS for Algerian Tech Makers.This discussion explores Taher’s journey in information security and cybersecurity, including career development, lessons learned, certifications, challenges, field experience, community contribution, and the mindset required to grow seriousl
Media Archive: Cybersecurity & Data Protection Panel at CTO Forum 2025
In this Media Archive episode of The InfoSec Control Room, Taher Amine ELHOUARI shares his intervention during the Cybersecurity & Data Protection Panel at CTO Forum 2025 in Algiers.This panel focused on key challenges facing organizations in today’s evolving threat landscape, including cybersecurity strategy, risk management, cloud security, data protection, governance, regulatory alignment,
Media Archive: Electronic Flies and Cybersecurity on Algerian National TV
In this Media Archive episode of The InfoSec Control Room, Taher Amine ELHOUARI shares a national television appearance on the topic of electronic flies, cybersecurity, online manipulation, and digital awareness.This discussion focuses on how digital platforms can be misused to influence, manipulate, mislead, or attack individuals and communities, and why cybersecurity awareness must go beyond pas
Media Archive: IT/OT Convergence at North Africa OT Security Forum
In this Media Archive episode of The InfoSec Control Room, Taher Amine ELHOUARI shares an intervention from the North Africa OT Security Forum, originally featured on ExpressFM.This discussion focuses on IT/OT convergence, cybersecurity risks, operational resilience, and the opportunities created when industrial environments, critical systems, and digital technologies become increasingly connected
Media Archive: Cybersecurity and Digital Awareness at Médiatics Radio
In this Media Archive episode of The InfoSec Control Room, Taher Amine ELHOUARI shares a public radio appearance originally recorded with Médiatics, an Algeria-based radio program.This episode focuses on cybersecurity, digital awareness, online risk, and the importance of making information security accessible to a wider audience beyond technical teams.The discussion reflects one of the core missi
Media Archive: Cybersecurity Awareness Session on Radio Médéa
In this Media Archive episode of The InfoSec Control Room, Taher Amine ELHOUARI shares a cybersecurity awareness session originally recorded at Radio Médéa.This episode focuses on public cybersecurity education, online risk, digital safety, and the importance of making security awareness accessible beyond technical teams. It reflects the role of media, experts, and local initiatives in helping peo
Media Archive: CrowdStrike Global Incident Analysis on Algerian National TV
In this Media Archive episode of The InfoSec Control Room, Taher Amine ELHOUARI shares a national television appearance analyzing the CrowdStrike global incident and its wider impact on cybersecurity, operational resilience, digital trust, and organizational dependency on critical technology providers.This episode reflects one of the core missions of The InfoSec Control Room: looking beyond the te
Media Archive: OWASP Algiers on Radio Médéa — Information & Cyber Security
In this Media Archive episode of The InfoSec Control Room, Taher Amine ELHOUARI shares a public radio appearance connected to OWASP Algiers Chapter on Radio Médéa.This episode focuses on information security, cybersecurity awareness, community engagement, and the role of local initiatives in helping students, professionals, developers, and the wider public better understand digital risk.The discus
Media Archive: OWASP Algiers & TechVerse Club on Radio Médéa
In this Media Archive episode of The InfoSec Control Room, Taher Amine ELHOUARI shares a public radio appearance connected to the TID event, OWASP Algiers, and TechVerse Club on Radio Médéa.This episode highlights the community and awareness side of cybersecurity: bringing security knowledge closer to students, young professionals, developers, and the wider public through local initiatives, events
Media Archive: Cybersecurity Awareness Session on Algerian National TV
In this Media Archive episode of The InfoSec Control Room, Taher Amine ELHOUARI shares a cybersecurity awareness session originally featured on Algerian National Television.This episode focuses on making cybersecurity understandable for a wider public audience, connecting technical security concepts with everyday digital behavior, online risk, awareness, and the role of experts in helping society
Media Archive: Cybersecurity Zero to Hero with The Algerian Developer
In this Media Archive episode of The InfoSec Control Room, Taher Amine ELHOUARI shares a cybersecurity live show originally hosted by TAD — The Algerian Developer.This session focuses on the journey from cybersecurity fundamentals to professional growth, helping learners, students, developers, and aspiring security practitioners understand how to approach the field with the right mindset, discipli
Media Archive: Cybersecurity Interview at Eco-Podcast
In this Media Archive episode of The InfoSec Control Room, Taher Amine ELHOUARI shares a public cybersecurity interview originally featured on Eco-Podcast.The discussion explores cybersecurity, information security leadership, digital trust, professional development, and the role of security practitioners in helping organizations and society better understand cyber risk.This episode reflects the b
Media Archive: Cybersecurity and Privacy at JilTech 3rd Edition
In this Media Archive episode of The InfoSec Control Room, Taher Amine ELHOUARI shares a public cybersecurity and privacy intervention delivered during JilTech 3rd Edition in Ghardaia, Algeria.This session reflects the educational and awareness side of cybersecurity: helping audiences understand how information security, privacy, digital behavior, and cyber risk connect in real-world environments.
Media Archive: Cybersecurity Fundamentals Masterclass with GoMyCode
In this Media Archive episode of The InfoSec Control Room, Taher Amine ELHOUARI shares a cybersecurity fundamentals masterclass originally delivered with GoMyCode.This session focuses on making cybersecurity more accessible, practical, and understandable for learners, students, professionals, and anyone interested in entering or strengthening their path in information security.The discussion refle
Media Archive: Cybersecurity Experts Panel at ICT Maghreb 2023
In this Media Archive episode of The InfoSec Control Room, Taher Amine ELHOUARI shares a recorded cybersecurity experts panel intervention from ICT Maghreb 2023.This discussion reflects the public speaking and industry-engagement side of cybersecurity: exchanging perspectives with experts, addressing real-world cyber challenges, and helping a wider audience understand the role of security leadersh
Media Archive: Cybersecurity Awareness on Algerian National Television
In this Media Archive episode of The InfoSec Control Room, Taher Amine ELHOUARI shares a public media appearance as a cybersecurity expert on Algerian National Television.The discussion focuses on cybersecurity awareness, ethical hacking, online risk, digital safety, and the importance of helping the public understand how cyber threats affect individuals, organizations, and society.This episode re
Recommended
English with Olivia | Slow Conversations & Vocabulary
Stand In The Circle
SLOW ENGLISH PODCAST (A1-A2) With Subtitles | Daily Videos | English With Us Podcast
Learn English A2 with Daily News | Simple English Listening Practice

پلی لیست | PlayList
Conspiracy Files with Paige Carter
Bad Friends

Learn 50 English Phrases While You Sleep | Everyday English Phrases & Vocabulary

This Past Weekend w/ Theo Von

Dateline NBC

Back to the 80s Radio
Crime Stories with Nancy Grace
