CyberCode Academy
CyberCode Academy is an educational podcast that teaches programming and cybersecurity through short, focused episodes. It is designed as an audio classroom, taking listeners from beginner to advanced levels one lesson at a time. The content covers topics like Python, web development, ethical hacking, and digital defense, breaking down complex concepts into simple and engaging audio lessons. It is free to listen and download on multiple platforms.
Episodes
Course 46 - CompTIA Cybersecurity Analyst | Episode 8: Active Port Scanning to Passive Analysis
Episode OverviewThis episode explores the core techniques and tools used to discover network infrastructure, identify exposed services, and build an accurate picture of host environments. It moves from active port scanning with Nmap and Zenmap to alternative discovery utilities and automated approaches, before transitioning to passive reconnaissance techniques used when direct probing is undesirab
Course 46 - CompTIA Cybersecurity Analyst | Episode 7: Network Footprinting & Mapping
Episode OverviewThis episode explores the foundations of cybersecurity reconnaissance and network mapping, following the process from initial intelligence gathering to active network footprinting and topology visualization.It examines how security professionals identify systems and services, evaluate network boundaries, and build an understanding of complex infrastructure while maintaining clear a
Course 46 - CompTIA Cybersecurity Analyst | Episode 6: Penetration Testing, Team War Games, and Reverse Engineering
Episode OverviewThis episode explores the core methodologies used to assess, simulate, investigate, and strengthen cybersecurity defenses. It brings together three complementary areas of security operations: structured penetration testing, controlled adversary simulations, and reverse engineering for malware analysis.From evaluating an organization's external attack surface to conducting realistic
Course 46 - CompTIA Cybersecurity Analyst | Episode 5: Network Deception and Secure Endpoint Management
Network Defense: Deception, Endpoint Hardening, and Security ManagementEpisode OverviewThis episode expands the network-defense model by examining two complementary areas of cybersecurity: defensive deception and enterprise endpoint security management.The first part introduces deception technologies such as honeypots and DNS sinkholes, showing how defenders can manipulate attacker behavior, colle
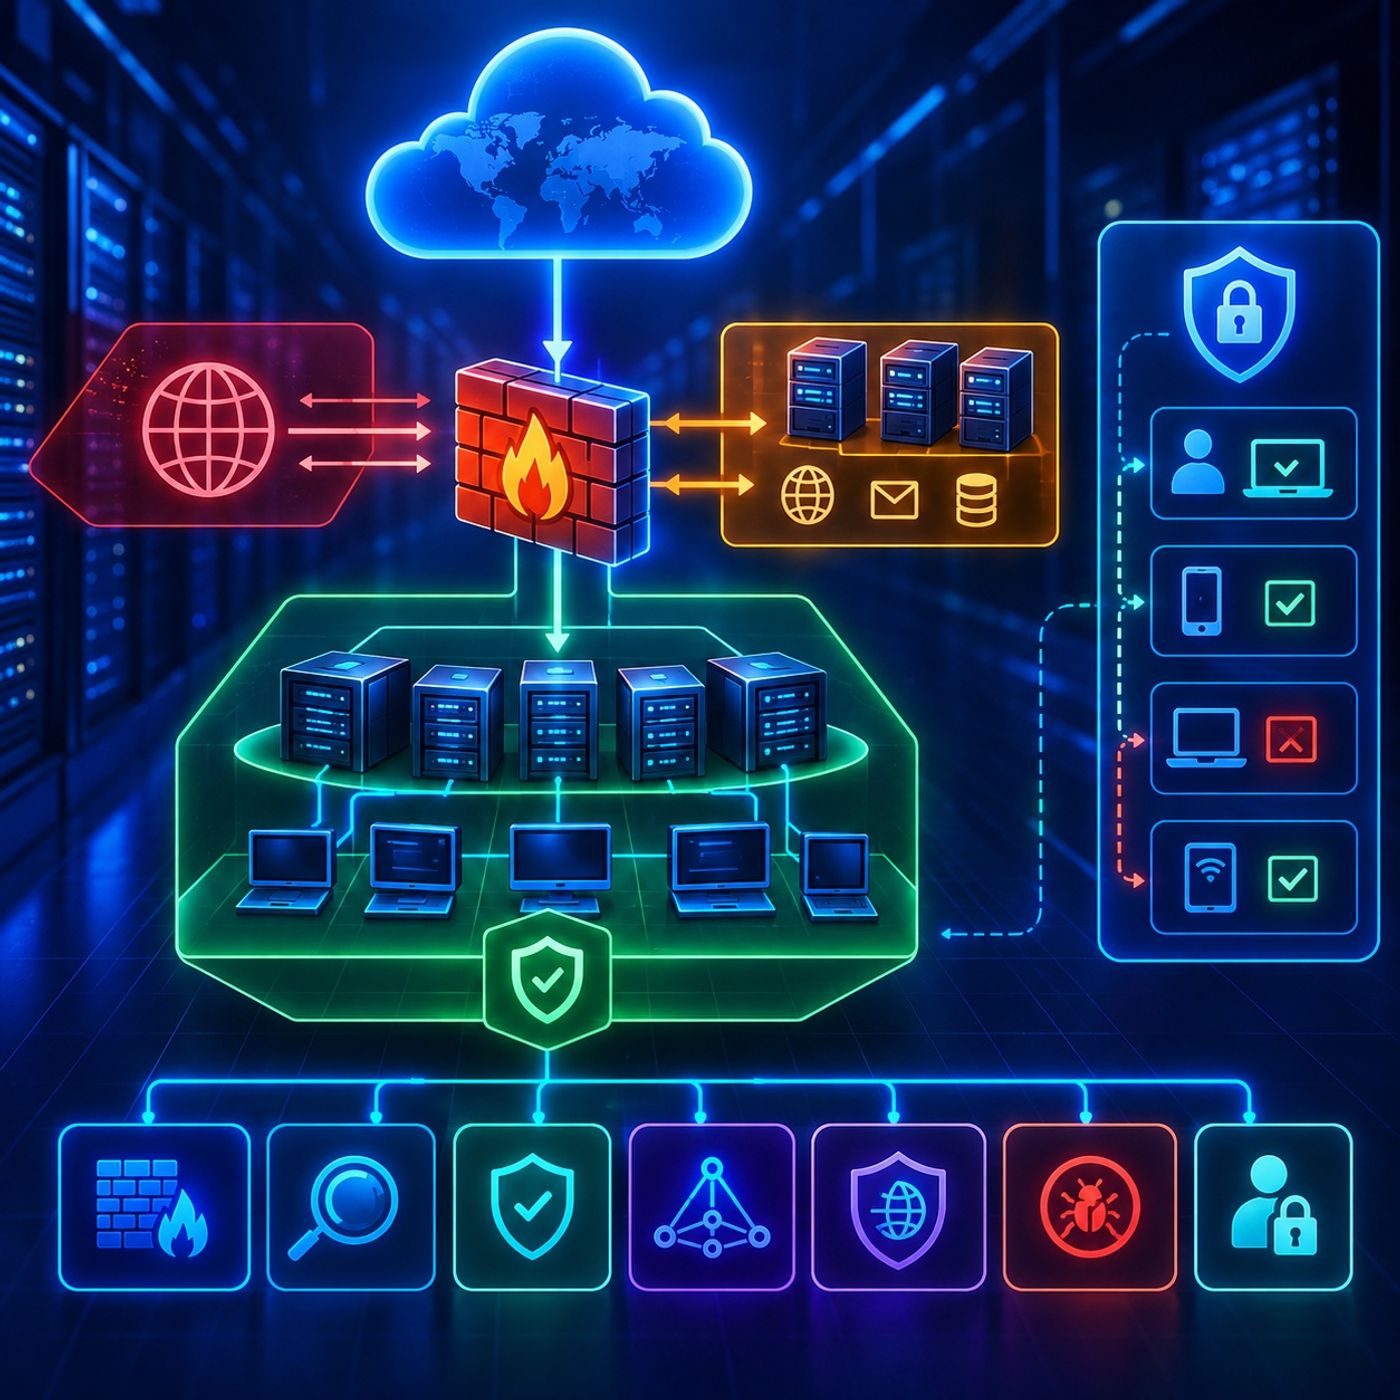
Course 46 - CompTIA Cybersecurity Analyst | Episode 4: Architecture of Isolation: Perimeter Security to Access Control
Network Defense Fundamentals: Firewalls, DMZ Architecture, and Network Access ControlEpisode OverviewThis episode introduces the core principles of network defense, focusing on perimeter security, network segmentation, traffic filtering, and access management.The lesson begins with the role of firewalls at network boundaries and examines how organizations separate the public internet, internal net
Course 46 - CompTIA Cybersecurity Analyst | Episode 3: Measuring and Managing Risk
Measuring and Managing Cybersecurity Risk: Likelihood, Assessment, and ControlsEpisode OverviewThis episode moves from identifying cybersecurity risks to understanding how organizations measure, prioritize, and manage those risks.Building on the previous discussion of threats, vulnerabilities, assets, likelihood, and impact, this lesson provides a practical framework for determining how significan
Course 46 - CompTIA Cybersecurity Analyst | Episode 2: Mastering Risk Assessment: Frameworks, Threats, and Vulnerabilities
Cybersecurity Risk Management: NIST SP 800-30 and Threat AssessmentEpisode OverviewThis episode explores the fundamentals of cybersecurity risk management through the NIST SP 800-30 risk assessment framework.Building on the previous episode's examination of assets, vulnerabilities, and threats, this lesson focuses on how organizations transform those concepts into a structured assessment of likeli
Course 46 - CompTIA Cybersecurity Analyst | Episode 1: Fundamentals, Risk & the CIA Triad
Cybersecurity Threat Management: Reconnaissance, the CIA Triad, and Risk FundamentalsEpisode OverviewThis episode introduces the foundational concepts of cybersecurity threat management associated with CySA+ Domain 1.The lesson begins with threat identification and reconnaissance, examining how security professionals collect information about systems, organizations, and potential attack surfaces t
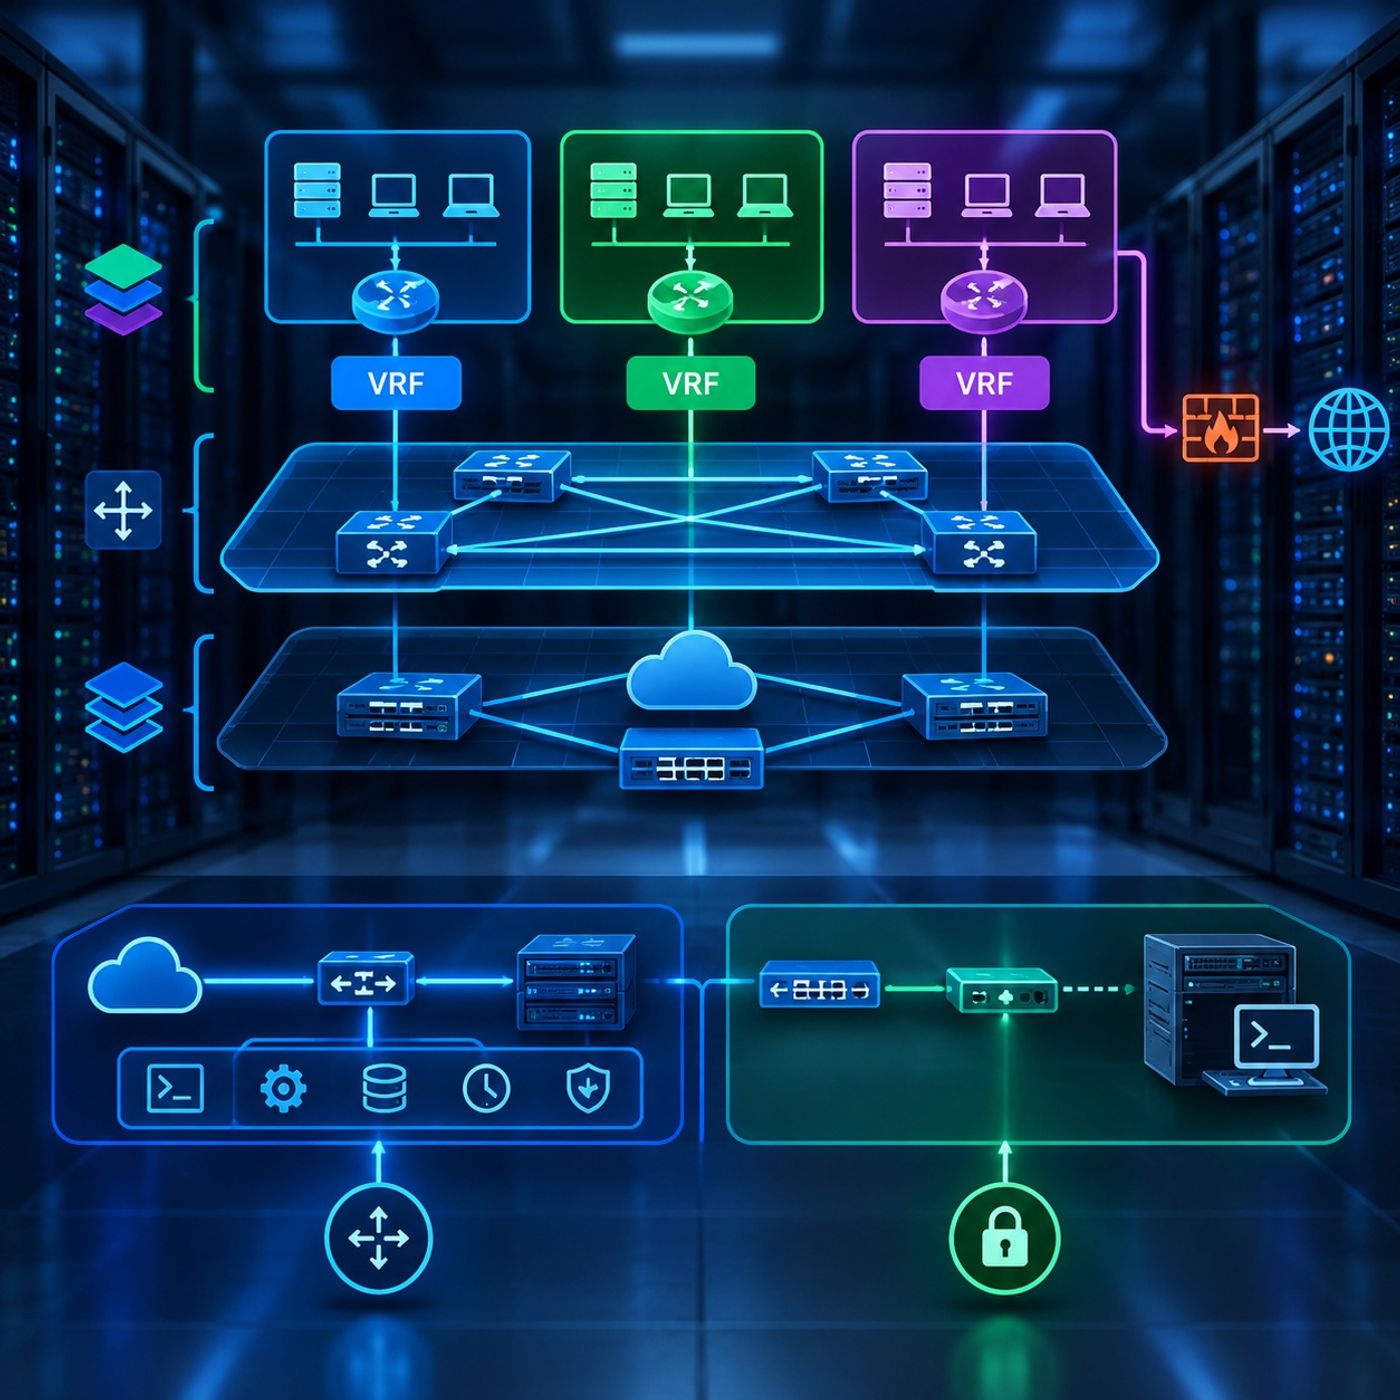
Course 45 - IE Data Center Network Design | Episode 5: Virtual Routing, Multi-Tenancy & Data Center Management Design
Data Center Virtualization and Secure Management ArchitectureEpisode OverviewModern data centers must provide both strong network isolation and reliable administrative access.In this episode, we explore two foundational aspects of data center architecture: Layer 3 network virtualization with Virtual Routing and Forwarding (VRF) and secure infrastructure management through inband and Out-of-Band (O
Course 45 - IE Data Center Network Design | Episode 4: Cisco Data Center Fabrics
Data Center Network Architecture: Multi-Site VXLAN EVPN and Chassis VirtualizationEpisode OverviewModern data centers increasingly depend on virtualization at both the network and hardware layers.Overlay technologies such as VXLAN BGP EVPN allow organizations to build scalable multi-site fabrics that support workload mobility, Layer 2 extension, and multi-tenant Layer 3 routing. At the same time,
Course 45 - IE Data Center Network Design | Episode 3: Mastering Virtual Port Channels
Virtual Port Channel (vPC) Design: Architecture, Best Practices, and Advanced StrategiesEpisode OverviewHow can two physical Cisco Nexus switches provide a highly available, active-active connection to the same downstream device while maintaining Layer 2 loop prevention?Virtual Port Channel (vPC) provides a multi-chassis link aggregation architecture that allows two switches to present a coordinat
Course 45 - IE Data Center Network Design | Episode 2: Modern Layer 3 Data Center Design
Designing Resilient Layer 3 Data Center Networks: Mobility, Convergence, and Service IntegrationEpisode OverviewModern data centers increasingly rely on routed Layer 3 fabrics to achieve the scalability, availability, and operational flexibility demanded by virtualized workloads.In this two-part episode, we explore the architecture behind resilient Layer 3 data center networks, focusing on three f
Course 45 - IE Data Center Network Design | Episode 1: Layer 2 Data Center Design
Layer 2 Data Center Design & Endpoint MobilityEpisode OverviewModern data center networks must do more than simply connect servers. They must support workload mobility, continuous availability, scalable architectures, and intelligent integration of network services.In this episode, we explore the architectural principles behind high-performance Layer 2 and data center fabrics, beginning with t
Course 44 - RH Security Specialist | Episode 12: Securing Linux with Nessus and IPTables
How can you determine whether a Linux server contains known security weaknesses—and how can you control the network traffic reaching those services?In this episode, we focus on two essential pillars of Linux server defense: proactive vulnerability assessment and active firewall protection.We begin with Nessus, exploring how vulnerability scanners identify operating systems, software versions, expo
Course 44 - RH Security Specialist | Episode 11: System Tracking and Port Reconnaissance
How do you know whether a Linux server is actually secure?Security professionals need more than preventive controls. They need the ability to monitor system activity, investigate suspicious behavior, audit sensitive resources, and verify what is exposed to the network.In this episode, we move from detailed internal auditing with the Linux Audit System to active network reconnaissance and firewall
Course 44 - RH Security Specialist | Episode 10: Linux System Logging and Auditing
A secure Linux environment is only as effective as your ability to understand what is happening inside it.Servers continuously generate information about authentication attempts, system activity, application behavior, administrative actions, and security events. Without proper log management and auditing, this information can become difficult to analyze, consume valuable storage, or disappear enti
Course 44 - RH Security Specialist | Episode 9: Identity Management (IdM) and System Logging
This episode explores two essential components of enterprise Linux administration and security: centralized identity management and system logging.The lesson begins with the deployment of an Identity Management (IdM) Server, covering the process of establishing a centralized authentication and authorization environment. You will configure the server's hostname, Kerberos realm, time synchronization
Course 44 - RH Security Specialist | Episode 8: Console Security and SSH Banners
This episode explores essential Linux system-hardening techniques designed to protect both physical console access and remote administration interfaces.The lesson focuses on three practical security controls: disabling the Ctrl+Alt+Del reboot mechanism, protecting the GRUB bootloader with authentication, and configuring pre-login SSH warning banners.Together, these measures demonstrate how Linux s
Course 44 - RH Security Specialist | Episode 7: Linux Group Security and the Power of PAM
This episode explores two fundamental components of Linux access control: group administration and Pluggable Authentication Modules (PAM).The lesson begins with practical group management, examining how administrators can organize users around shared resources and delegate specific group-management responsibilities without granting full root privileges. From there, the episode moves into the archi
Course 44 - RH Security Specialist | Episode 6: Locking Down the File System
This episode provides a practical guide to strengthening Linux file system security, progressing from protecting shared directories against accidental or unauthorized deletions to implementing granular access controls and continuously monitoring system integrity.The lesson focuses on three essential Linux security mechanisms: the Sticky Bit, File Access Control Lists (FACL), and the Advanced Intru
Course 44 - RH Security Specialist | Episode 5: Mastering Linux Permissions
Advanced Linux administration requires a deeper understanding of both filesystem behavior and Unix permission mechanisms. In this episode, we explore the powerful capabilities of the XFS filesystem and examine special permission mechanisms that can significantly influence how users and applications interact with the operating system.We begin with XFS administration, focusing on filesystem mount op
Course 44 - RH Security Specialist | Episode 4: Performance, Security & Mount Options
Linux storage management goes far beyond formatting a disk and mounting it. Understanding how modern Linux file systems work—and how their configuration affects security, reliability, and performance—is an essential skill for system administrators and security professionals.In this episode, we move from the architectural foundations of Linux file systems into practical storage administration and a
Course 44 - RH Security Specialist | Episode 3: From Standards to LUKS Encryption
A secure Linux server begins with more than a hardened configuration file. Enterprise security requires a layered approach that protects the system from physical tampering, unauthorized remote access, insecure services, filesystem abuse, and exposure of sensitive data.In this episode, we move from fundamental operating system hardening to advanced protection for data at rest. We examine how admini
Course 44 - RH Security Specialist | Episode 2: Mastering Yum Updates and RPM Verification
Maintaining a secure and reliable Linux environment requires more than simply installing the latest software. Administrators must understand how security updates are identified and applied, how package authenticity is established, and how installed software can be inspected and verified at a lower level.In this episode, we explore the security-focused package management workflows used across Red H
Course 44 - RH Security Specialist | Episode 1: Hardening, the CIA Model, and Professional Success
This episode, we shift our focus from application development to the security of the underlying server infrastructure.A newly deployed server can quickly become a target for automated scanning, credential attacks, and other unauthorized activity. Building a secure environment therefore requires more than simply installing an operating system and deploying applications. It requires a layered securi
Course 43 - Practical Malware Development | Episode 9: Finalizing Client-Side Command & Control
This final hands-on integration session, we bring the client-side component and the central control panel together into a complete communication workflow.The episode focuses on transforming an isolated client application into an integrated node capable of registering its system information, periodically checking for pending tasks, processing authorized instructions, and returning execution results
Course 43 - Practical Malware Development | Episode 8: Building a PHP Command and Control Backend
This episode, we bring the control-panel backend together into a complete PHP, MySQL, and JavaScript database-driven communication architecture.Building on the authentication and dashboard functionality from previous episodes, we now connect the individual components into a closed-loop workflow for registering client nodes, managing queued tasks, receiving returned results, and displaying those re
Course 43 - Practical Malware Development | Episode 7: Building a PHP Session Control Panel
This episode, we continue developing our PHP-based control panel by moving beyond authentication and building the authenticated administration layer.We begin by establishing administrator credentials, then implement a dedicated session-protection mechanism to secure private pages. Finally, we transform the control panel into a dynamic dashboard capable of retrieving database records and presenting
Course 43 - Practical Malware Development | Episode 6: Database Foundations and PHP Integration
This episode, we build a PHP and MySQL control panel backend from the ground up, progressing from database initialization and server configuration to user authentication and session management.The episode focuses on connecting a web application to a MySQL database while introducing important security concepts such as prepared statements, parameter binding, password hashing, and session-based authe
Course 43 - Practical Malware Development | Episode 5: Error Handling & HTTP Polling
This episode moves beyond local command processing and introduces the fundamentals of network-based communication in a C# security-testing environment.The lesson begins by improving the reliability of the existing application through structured exception handling and more robust command parsing. It then examines the concepts behind periodic HTTP communication, connection monitoring, and graceful f
Course 43 - Practical Malware Development | Episode 4: System Navigation and Command Execution
In this episode, we build a custom interactive command-line shell in C#, exploring how applications can combine filesystem navigation, system reconnaissance, and operating-system command execution into a single interface.The episode takes a practical, step-by-step approach, beginning with basic directory operations and gradually introducing system information gathering and command execution.1. Dir
Course 43 - Practical Malware Development | Episode 3: Recon, Registry Persistence, and Web Downloading
This episode introduces the core concepts behind offensive C# development for authorized penetration testing and red-team environments. The walkthrough follows a simplified offensive-tool lifecycle, beginning with host reconnaissance and progressing through persistence mechanisms and dynamic retrieval of additional components.The focus is on understanding how C# can interact directly with the Wind
Course 43 - Practical Malware Development | Episode 2: Building Your Dual-OS Dev Labs
This episode establishes the essential development foundations across Windows and Linux, preparing the workspace for advanced scripting, application development, and future security-focused projects.The episode takes a practical, hands-on approach, configuring a Windows development environment and then building a complete local web and database stack on Ubuntu.1. Configuring the Windows Developmen
Course 43 - Practical Malware Development | Episode 1: Building Your Virtual Sandbox
This episode provides a complete, step-by-step guide to building a practical virtual sandbox using VirtualBox or VMware. The goal is to create isolated and reliable Windows and Linux environments that can be used for software development, testing, and server-side application work.1. Preparing the Virtualization EnvironmentThe episode begins by covering the essential software and installation media
Course 42 - Mobile Malware Analysis Fundamentals | Episode 15: iOS and Android Case Studies and Reporting
This module provides a hands-on exploration of mobile malware analysis through two distinct case studies, one for iOS and one for Android, designed to let you work independently to uncover the functionality of malicious programs. The episode is structured into the following key components: 1. iOS Case Study: Corporate Security Assessment The first scenario involves a corporate iPhone reported for
Course 42 - Mobile Malware Analysis Fundamentals | Episode 14: Architecture and Essential Toolkits
This episode provides a comprehensive guide to designing and equipping a professional mobile malware analysis lab, with a focus on building a secure, repeatable, and well-instrumented environment for both iOS and Android research.1. Lab Design and InfrastructureThe episode begins by emphasizing that a professional malware lab requires more than simply running a few virtual machines. Researchers mu
Course 42 - Mobile Malware Analysis Fundamentals | Episode 13: Designing and Architecting a Scalable Mobile Malware Analysis Lab
This episode focuses on designing a professional, scalable, and repeatable mobile malware analysis laboratory, moving beyond a simple virtual-machine setup toward an environment suitable for long-term security research.1. Strategic Lab PlanningBefore building the lab, analysts should define its purpose and scope:Determine whether the environment will be air-gapped, isolated, or internet-connected.
Course 42 - Mobile Malware Analysis Fundamentals | Episode 12: Dynamic Analysis Tools, Techniques, and Assessment
This episode covers dynamic analysis of Android applications, with a strong emphasis on runtime interaction, monitoring, and debugging.1. Android Dynamic Analysis with DrozerThe episode introduces Drozer, an Android security assessment framework that allows researchers to interact with application components while they are running.Key capabilities include:Establishing communication between the ana
Course 42 - Mobile Malware Analysis Fundamentals | Episode 11: Dynamic Analysis for iOS and Android
Dynamic Mobile Malware Analysis — iOS and AndroidThis episode expands dynamic malware analysis beyond basic runtime observation and introduces process instrumentation, debugging, network capture, and automated mobile-security frameworks across both iOS and Android.The central idea is:Static analysis tells you what a sample may be capable of; dynamic analysis shows what it actually does when execut
Course 42 - Mobile Malware Analysis Fundamentals | Episode 10: The Essentials of Dynamic Analysis
Dynamic iOS Malware Analysis — Key TakeawaysApplication Entry PointThe standard entry point for an iOS application is UIApplicationMain.It initializes the application runtime and connects the application to its App Delegate, which manages important lifecycle events.Method SwizzlingMethod swizzling allows an analyst to intercept or replace a class method at runtime.In a controlled malware-analysis
Course 42 - Mobile Malware Analysis Fundamentals | Episode 9: Mastering Basic Static Analysis for Mobile Malware
Mobile Malware Static Analysis — Module ConclusionThis episode serves as a knowledge check and consolidation of the basic static-analysis methodology covered across both iOS and Android. The emphasis is not on learning one particular tool, but on developing a repeatable investigation process.1. iOS Static AnalysisSeveral important tools and artifacts are reinforced.class-dumpUsed primarily to extr
Course 42 - Mobile Malware Analysis Fundamentals | Episode 8: Static Analysis of Android Banking Trojans
Android Basic Static Analysis — Advanced Study GuideThis episode demonstrates how to perform basic static analysis of Android applications, moving from initial malware triage to manifest analysis, code decompilation, and identification of suspicious functionality.1. Android Malware Analysis MethodologyAlthough Android and iOS have very different architectures, the fundamental malware-analysis meth
Course 42 - Mobile Malware Analysis Fundamentals | Episode 7: Malware Tools and Practical Lab Walkthrough
iOS Basic Static Analysis — Advanced Study GuideThis episode moves from the fundamentals of iOS malware analysis into hands-on static binary analysis, demonstrating how command-line utilities and reverse-engineering tools can reveal valuable information without executing the malware.1. otool — Inspecting Mach-O Binariesotool is one of the most useful command-line utilities for examining Apple Mach
Course 42 - Mobile Malware Analysis Fundamentals | Episode 6: The Evolution and Methodology of iOS Malware Attacks
iOS Malware Analysis — Key TakeawaysThis episode introduces the fundamentals of iOS malware analysis, combining the historical evolution of mobile threats with the methodology used by security researchers to investigate them.1. Understanding Mobile MalwareMobile malware is malicious software designed to disrupt devices, steal information, gain unauthorized access, or perform malicious actions. Com
Course 42 - Mobile Malware Analysis Fundamentals | Episode 5: Fundamentals, App Structure, and Knowledge Review
Android Security & APK Architecture — Advanced Study Template1. Android Security ModelAndroid security is built around several fundamental objectives:- Protecting user and application data- Isolating applications from one another- Controlling privileges- Providing secure inter-process communication- Restricting unauthorized access to system resourcesThe architecture combines traditional Linux
Course 42 - Mobile Malware Analysis Fundamentals | Episode 4: iOS Security and Android Frameworks
A comprehensive technical exploration of the foundational architectures and security models of iOS and Android, providing the essential knowledge required for mobile security analysis and malware research.The journey begins with iOS security, examining its three major pillars: system security, data security, and application security. You will learn how iOS applications operate within the Cocoa Tou
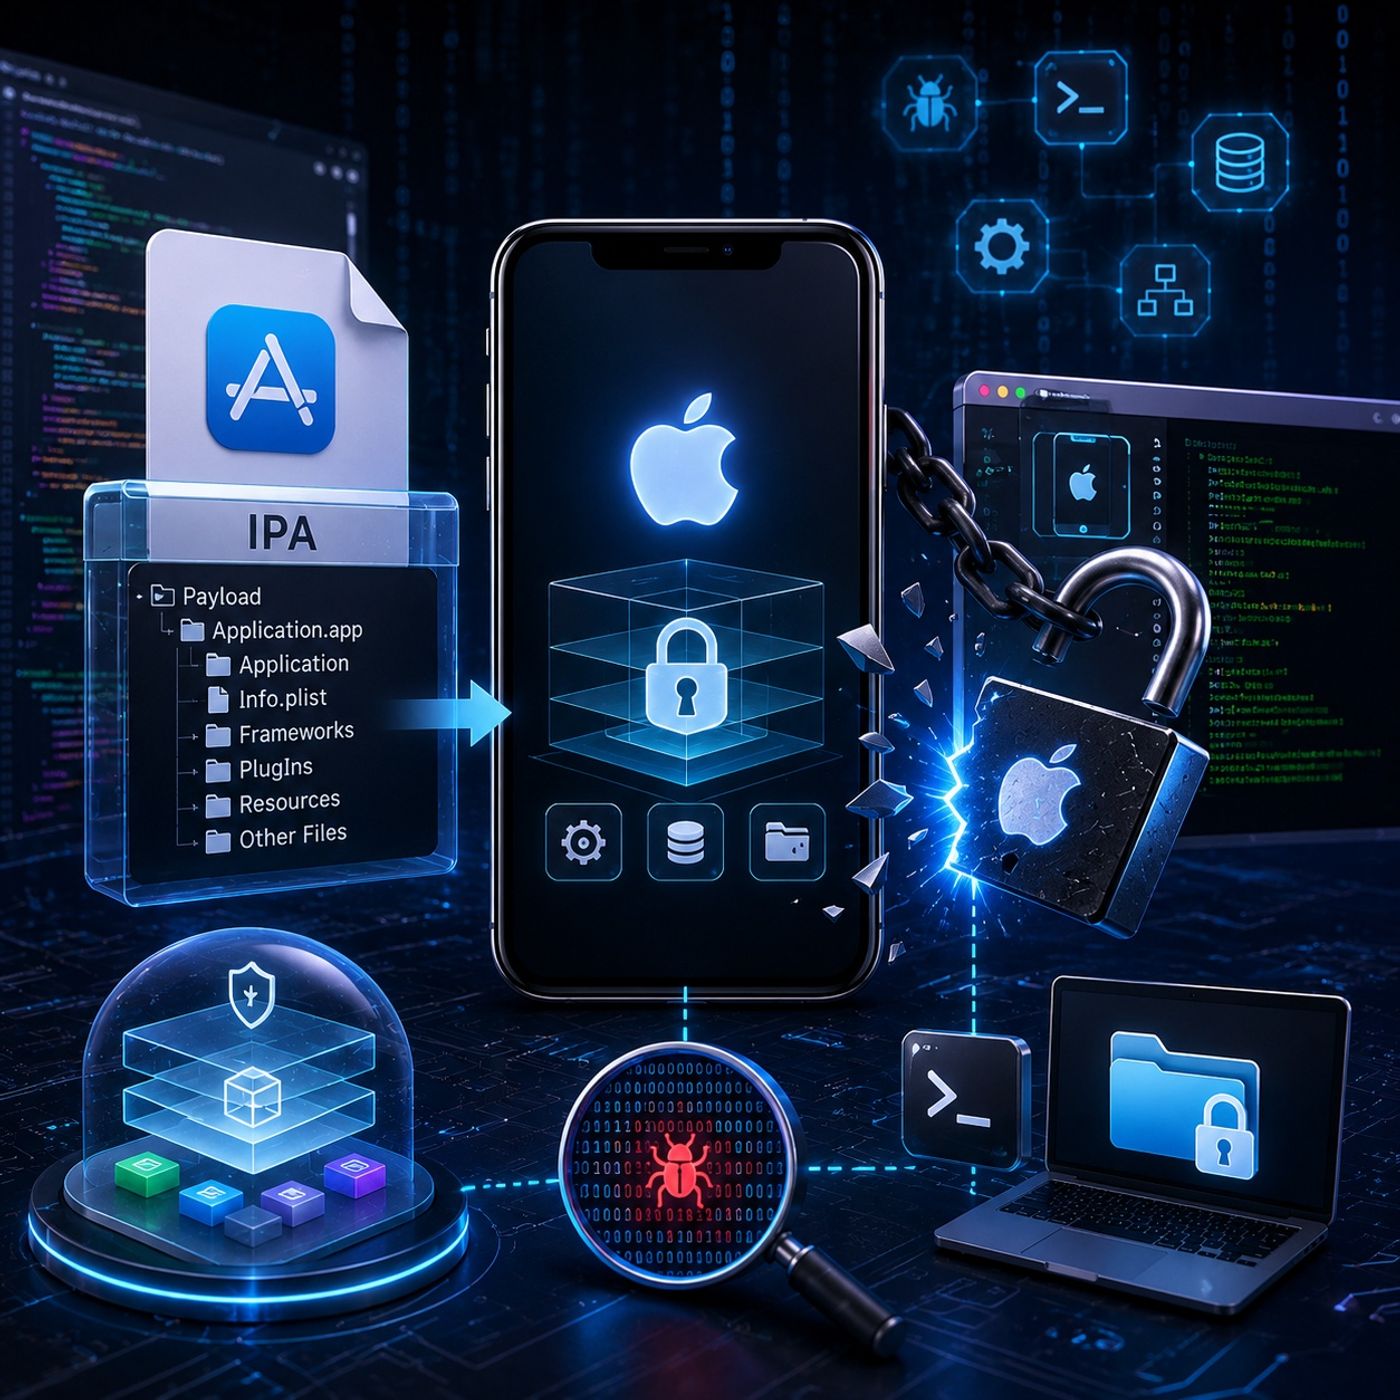
Course 42 - Mobile Malware Analysis Fundamentals | Episode 3: iOS Application Architecture and Jailbreaking Fundamentals
iOS Application Architecture & Jailbreaking — Advanced Study Template1. iOS Application ArchitectureiOS applications are primarily developed using:SwiftObjective-CXcode as the main development environmentAfter compilation, an application is packaged into an IPA (iOS App Store Package).An IPA is essentially an archive containing the components required to install and execute the application.2.
Course 42 - Mobile Malware Analysis Fundamentals | Episode 2: iOS Architecture & Security
iOS Architecture & Security — Study Template1. iOS Architecture OverviewThe iOS platform can be understood as a layered architecture in which higher-level frameworks rely on increasingly fundamental system services.┌─────────────────────────────┐ │ Cocoa Touch │ ├─────────────────────────────┤ │ Core Media │ ├─────────────────────────────┤ │ Core Services │ ├─────────────────────────────┤ │ Co
Course 42 - Mobile Malware Analysis Fundamentals | Episode 1: Threat Landscape, Device Architecture, and Risk Analysis
Mobile Malware Analysis — Foundational Study Template1. Course ObjectiveThis module introduces the fundamentals of mobile malware analysis for both:AndroidiOSThe course is designed to build the knowledge required to investigate malicious mobile applications, understand their behavior, and identify security risks.2. Technical PrerequisitesBefore beginning mobile malware analysis, you should have a
Course 41 - Analyzing Attacks for Incident Handlers | Episode 4: Live Memory Forensics, VM Troubleshooting, and Malware Analysis
🧠 Live Memory Forensics Lab — Mandiant Redline (Full Workflow)🎯 Lab ObjectivePerform a real-world memory forensic investigation on an infected Windows VM using Mandiant Redline, covering:Infection → Data Collection → Transfer → Analysis → IOC Identification🧪 Lab OverviewEnvironment:Target: Windows 7 Virtual Machine (infected)Malware Sample: her.exe (Dyre/Dridex family behavior)Tool: Mandiant Redli
Course 41 - Analyzing Attacks for Incident Handlers | Episode 3: Live Memory Forensics and Malware Analysis with Mandiant Redline
🧠 Live Memory Forensics with Mandiant Redline — Study Template🔐 Core ConceptMandiant Redline is not just a memory capture tool — it performs a:Memory audit for rapid threat detection and triageUnlike basic tools:It analyzes live system stateIdentifies Indicators of Compromise (IOCs)Detects stealthy malware that bypasses normal APIs⚡ Why Redline Is PowerfulTraditional tools:Only dump memory → analy
Course 41 - Analyzing Attacks for Incident Handlers | Episode 2: Utilizing FTK Imager and Redline for Incident Handlers
🧠 Memory Analysis & Incident Response — Advanced Template🔐 Core ConceptMemory analysis is a high-impact forensic technique used during incident response to uncover evidence that is not available through disk or antivirus analysis.Key idea: Critical attack artifacts often exist only in volatile memory⚡ Why Memory Analysis Is CriticalTraditional methods may fail:Antivirus → may not detect advanc
Course 41 - Analyzing Attacks for Incident Handlers | Episode 1: Volatile Evidence, Forensic Tools, and Investigation Procedures
🧠 Memory Analysis (RAM Forensics) — Study Template🔐 Core ConceptMemory analysis is a critical part of the incident response process, used to detect threats that do not leave artifacts on disk.Key idea: Some attacks exist only in memory⚡ Why Memory Forensics MattersModern threats bypass traditional disk-based detection:Fileless malwareExecutes directly in RAMLeaves no files behindMalicious PowerShe
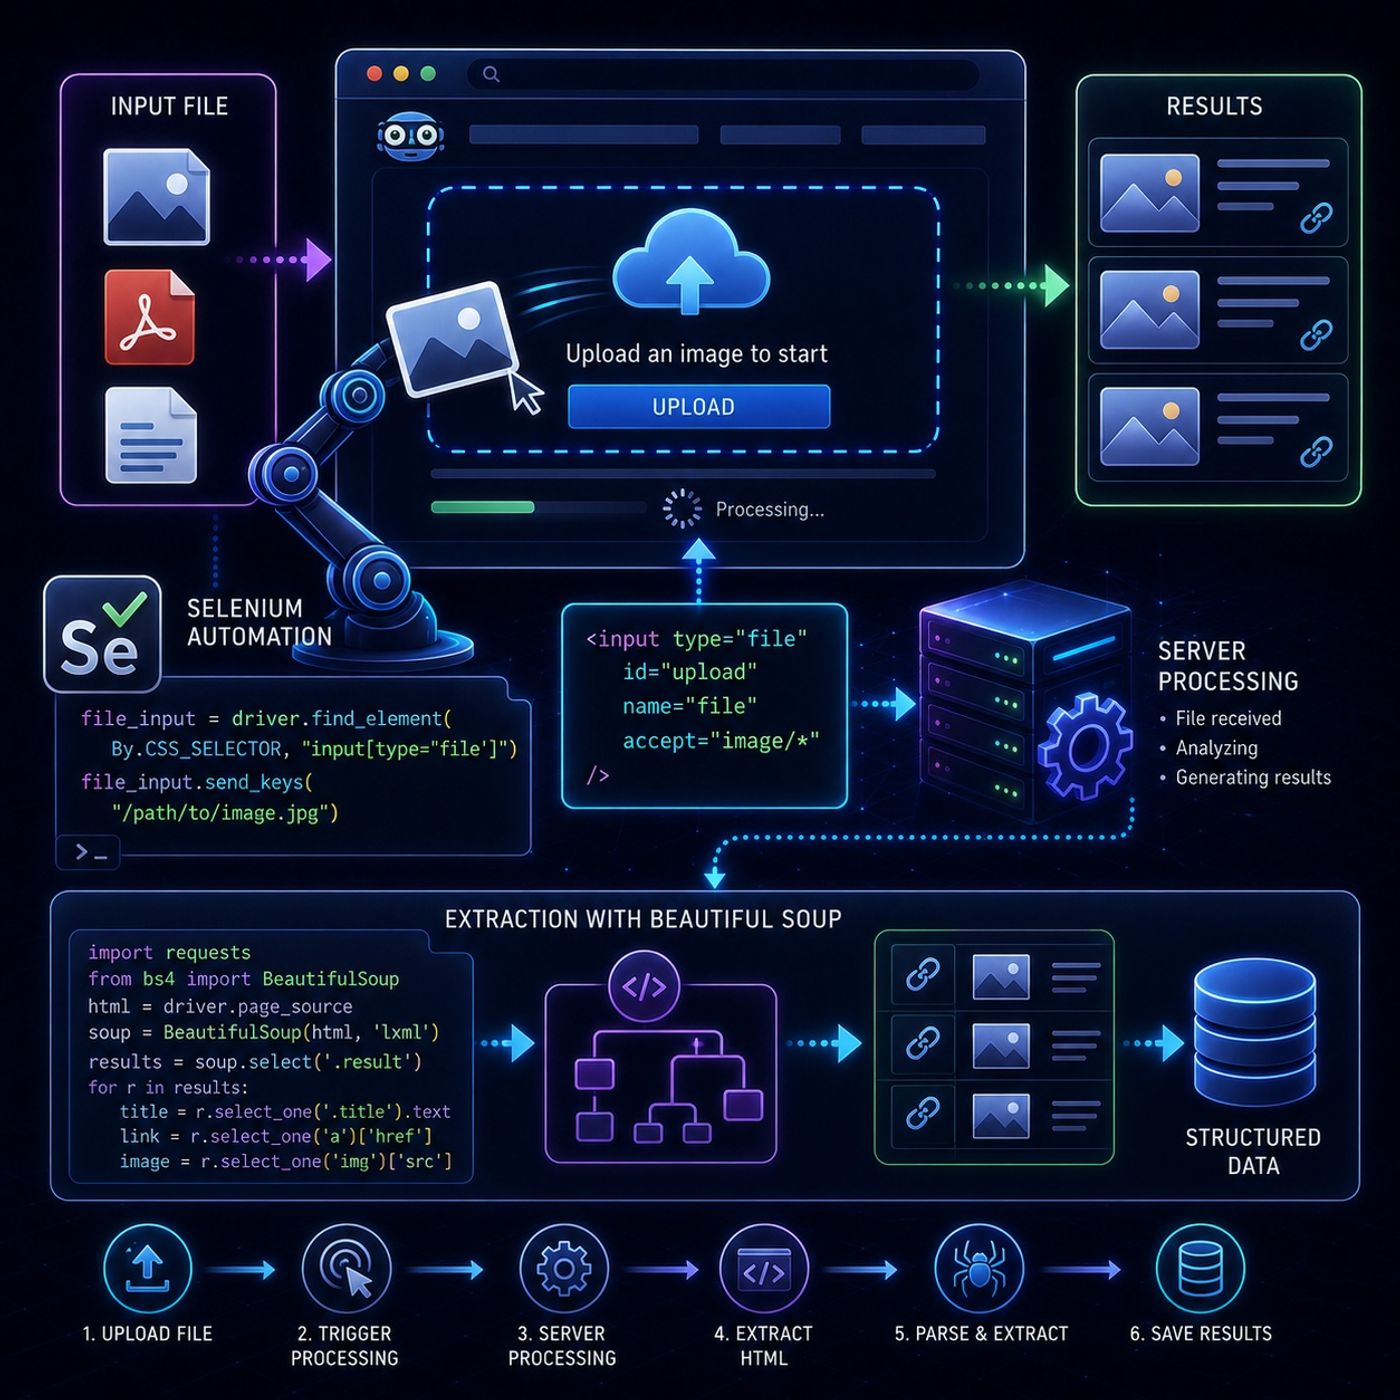
Course 40 - Web Scraping with Python | Episode 43: Mastering File Uploads and Reverse Image Search
This episode is about a very specific but powerful capability in scraping:automating file uploads as part of a web interaction workflowIt sits at the intersection of browser automation + data extraction pipelines.📤 Core IdeaSome websites don’t just serve data — they require you to:upload a filetrigger processingthen return resultsSo scraping becomes:“submit file → wait for processing → extract gen
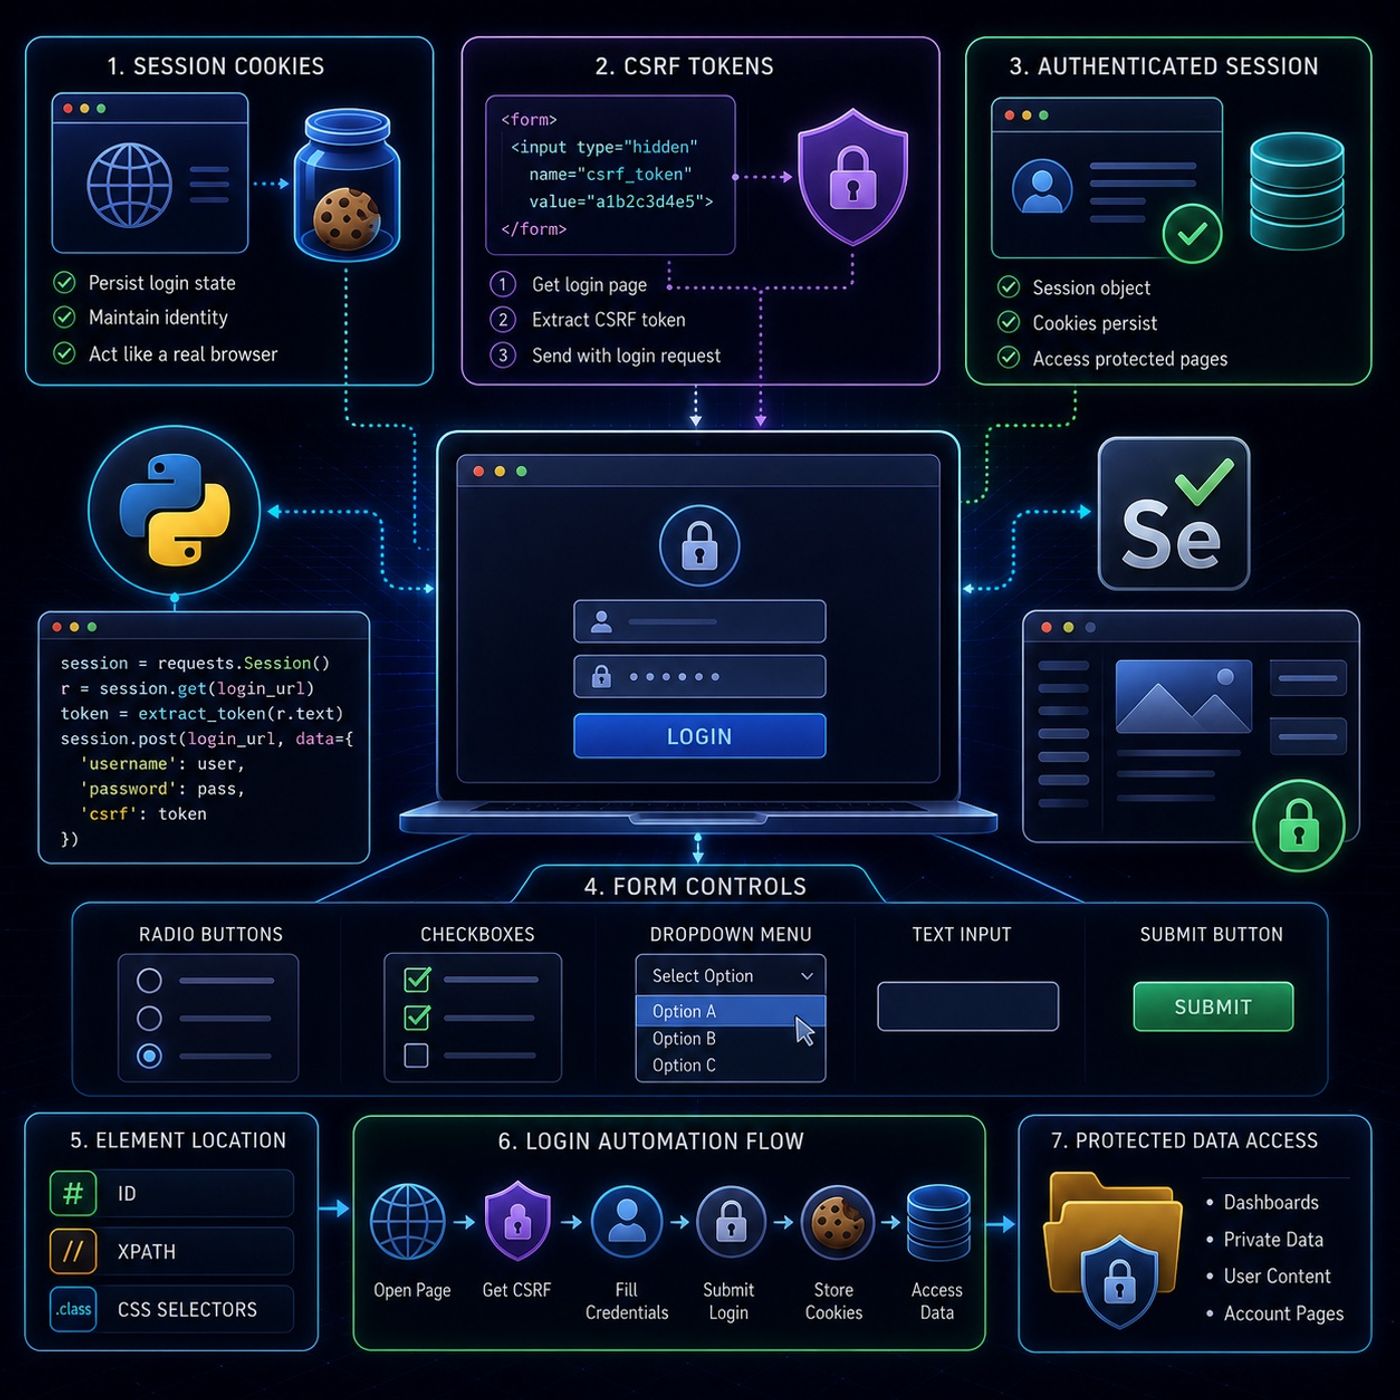
Course 40 - Web Scraping with Python | Episode 42: Web Authentication and Automated Form Input Submission
This episode is essentially about turning “login-protected websites” into programmable sessions and then controlling full form workflows like a real user.🔐 Core IdeaModern scraping stops being “download HTML” and becomes:“Authenticate → maintain session → interact → extract”This is the foundation of scraping anything behind a login wall.🍪 1. Session Cookies (Staying Logged In)🧠 What they are:Small
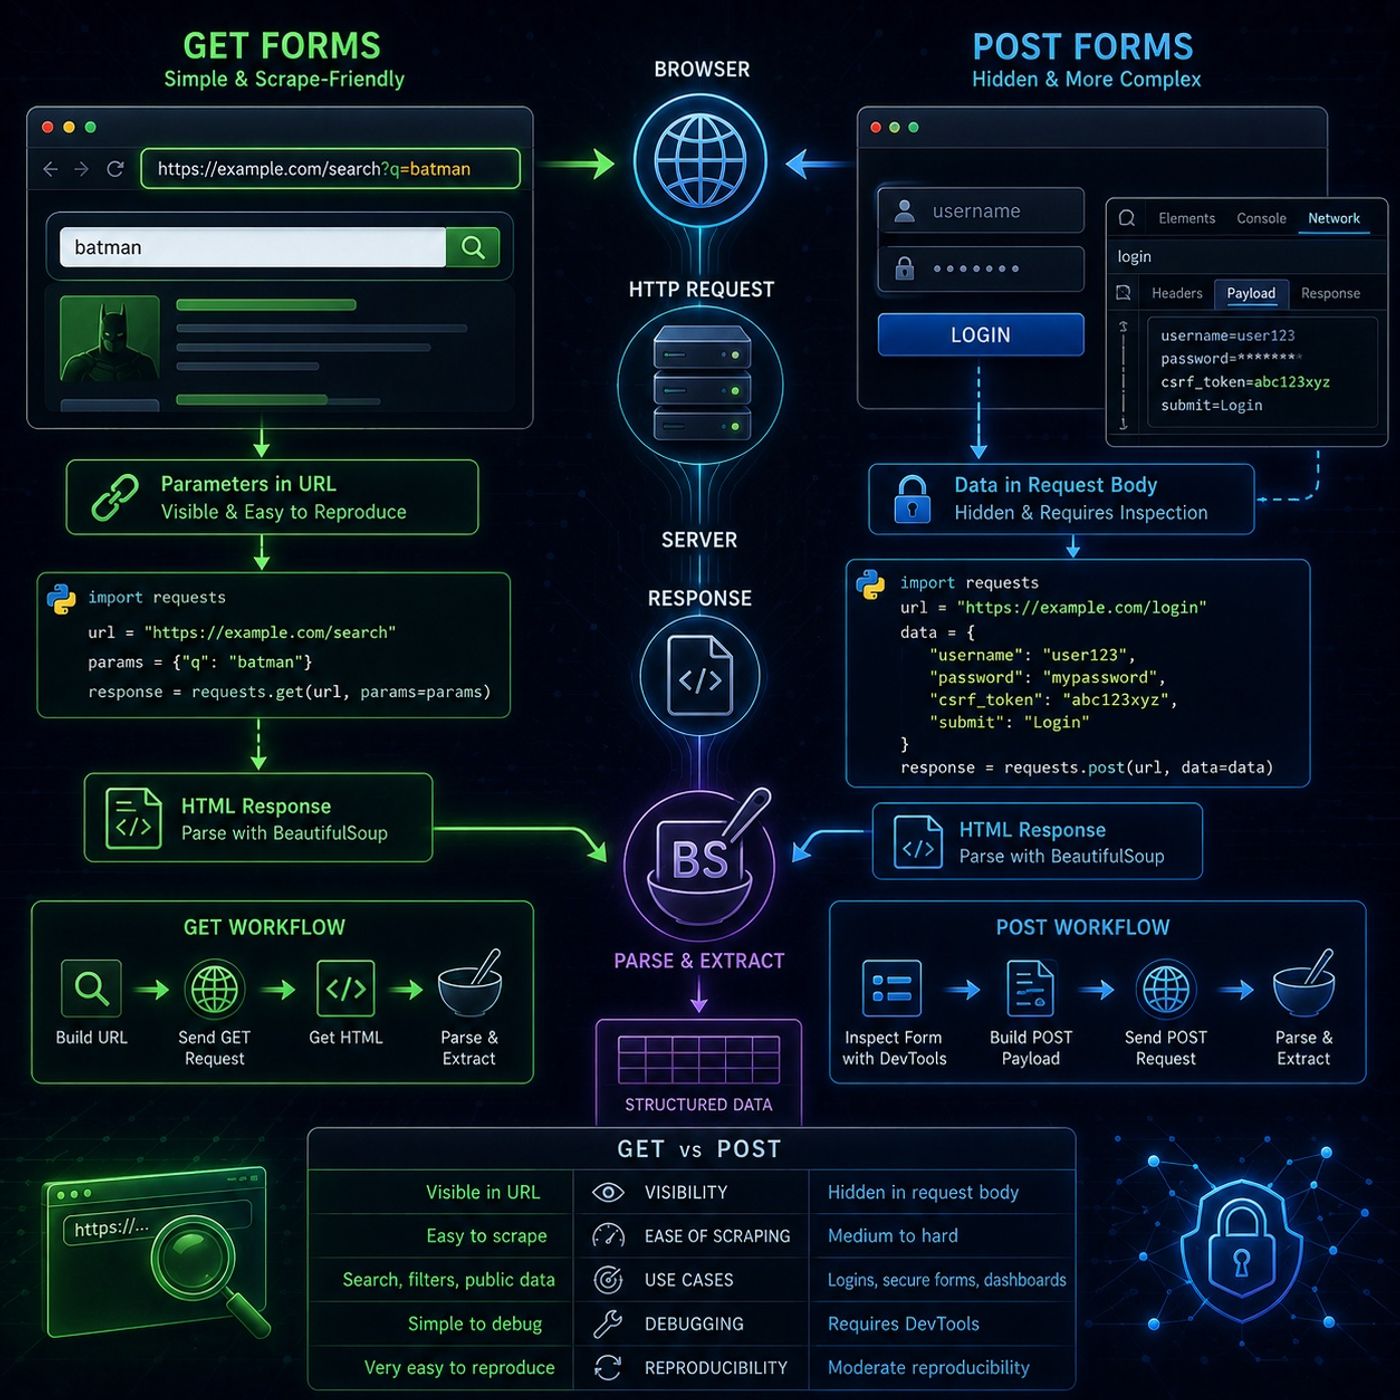
Course 40 - Web Scraping with Python | Episode 41: Mastering GET and POST Form Submissions
This episode is essentially teaching you how to reverse-engineer web forms into programmatic HTTP requests, which is one of the most important skills in practical scraping.🧭 Core IdeaWeb forms are just structured HTTP requests.So instead of thinking:“I’m filling a form”You should think:“I’m constructing a GET or POST request that mimics what the browser sends”🌐 1. GET Forms (Simple & Scrape-Fr
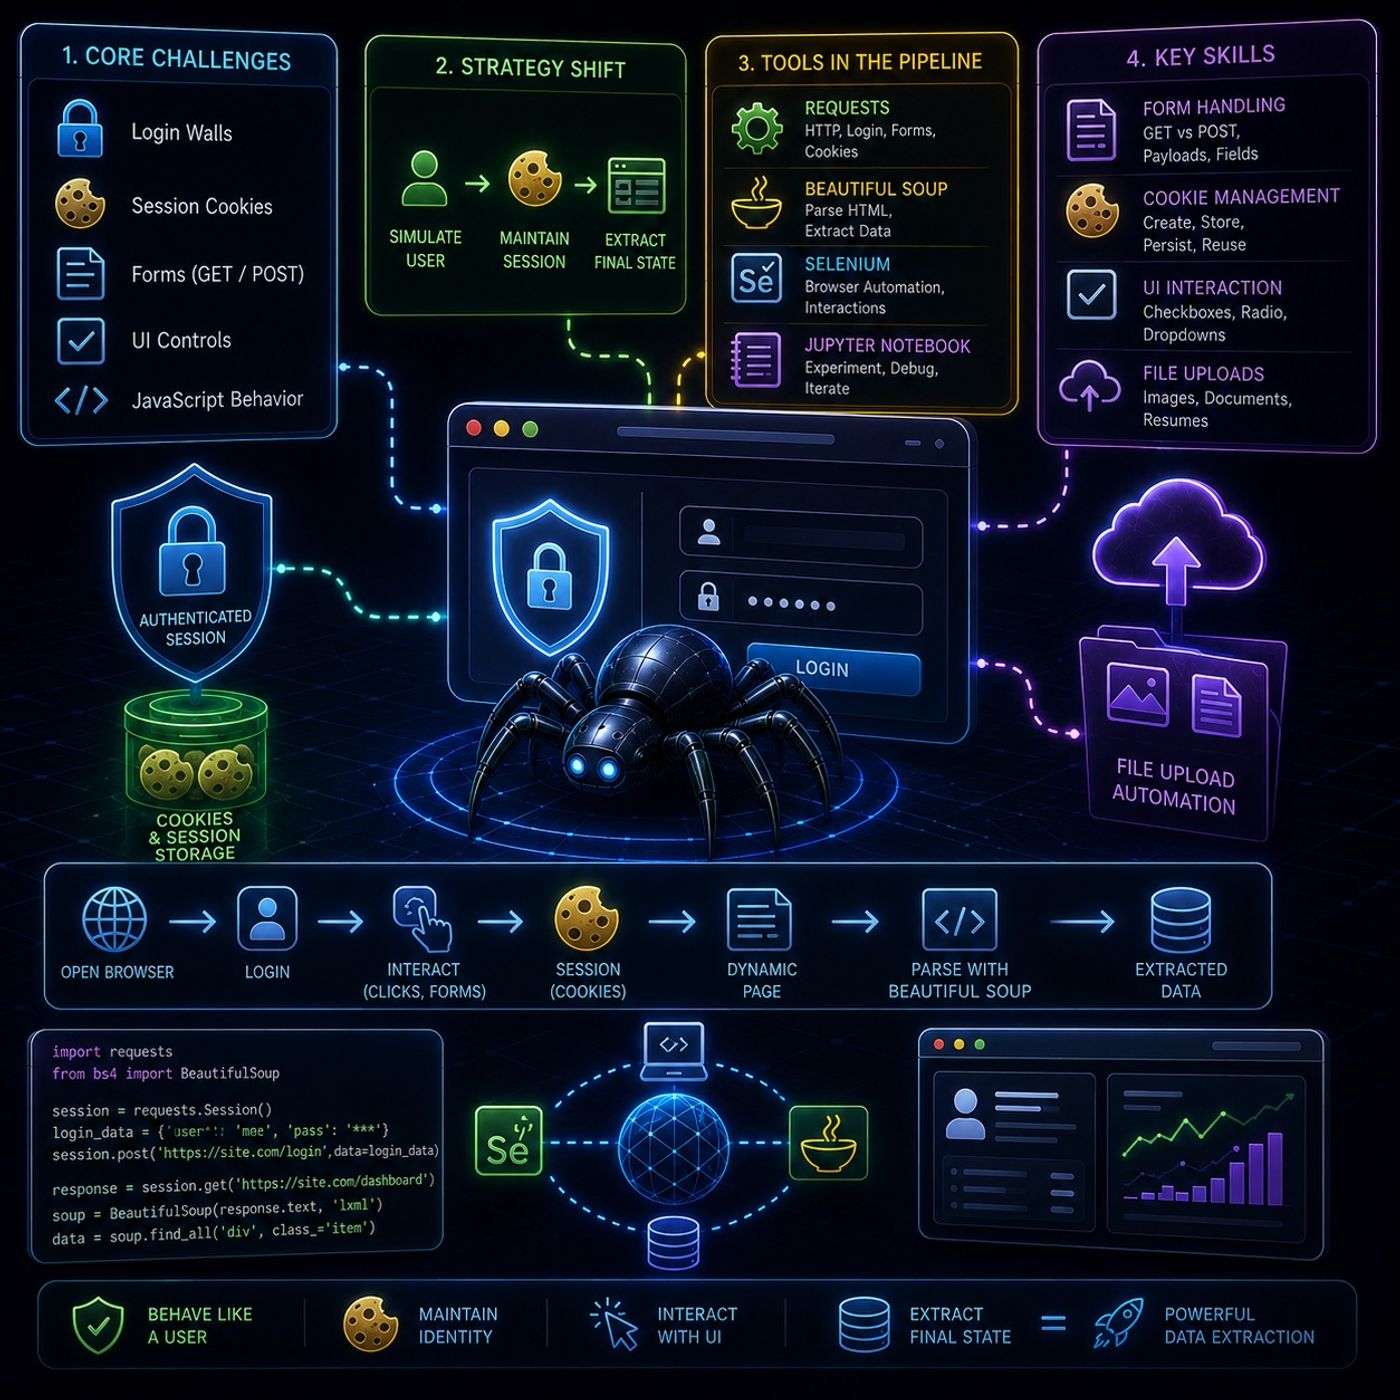
Course 40 - Web Scraping with Python | Episode 40: Introduction to Advanced Web Scraping: Tools and Tactics
This episode is essentially about moving from “simple scraping” → “interactive web automation + session-aware extraction”, where websites behave more like applications than static pages.🧠 Core Idea of the CourseStandard scraping fails when websites:require logindepend on session state (cookies)use forms instead of URLsrely on user interaction (buttons, uploads, checkboxes)So the goal becomes:Make
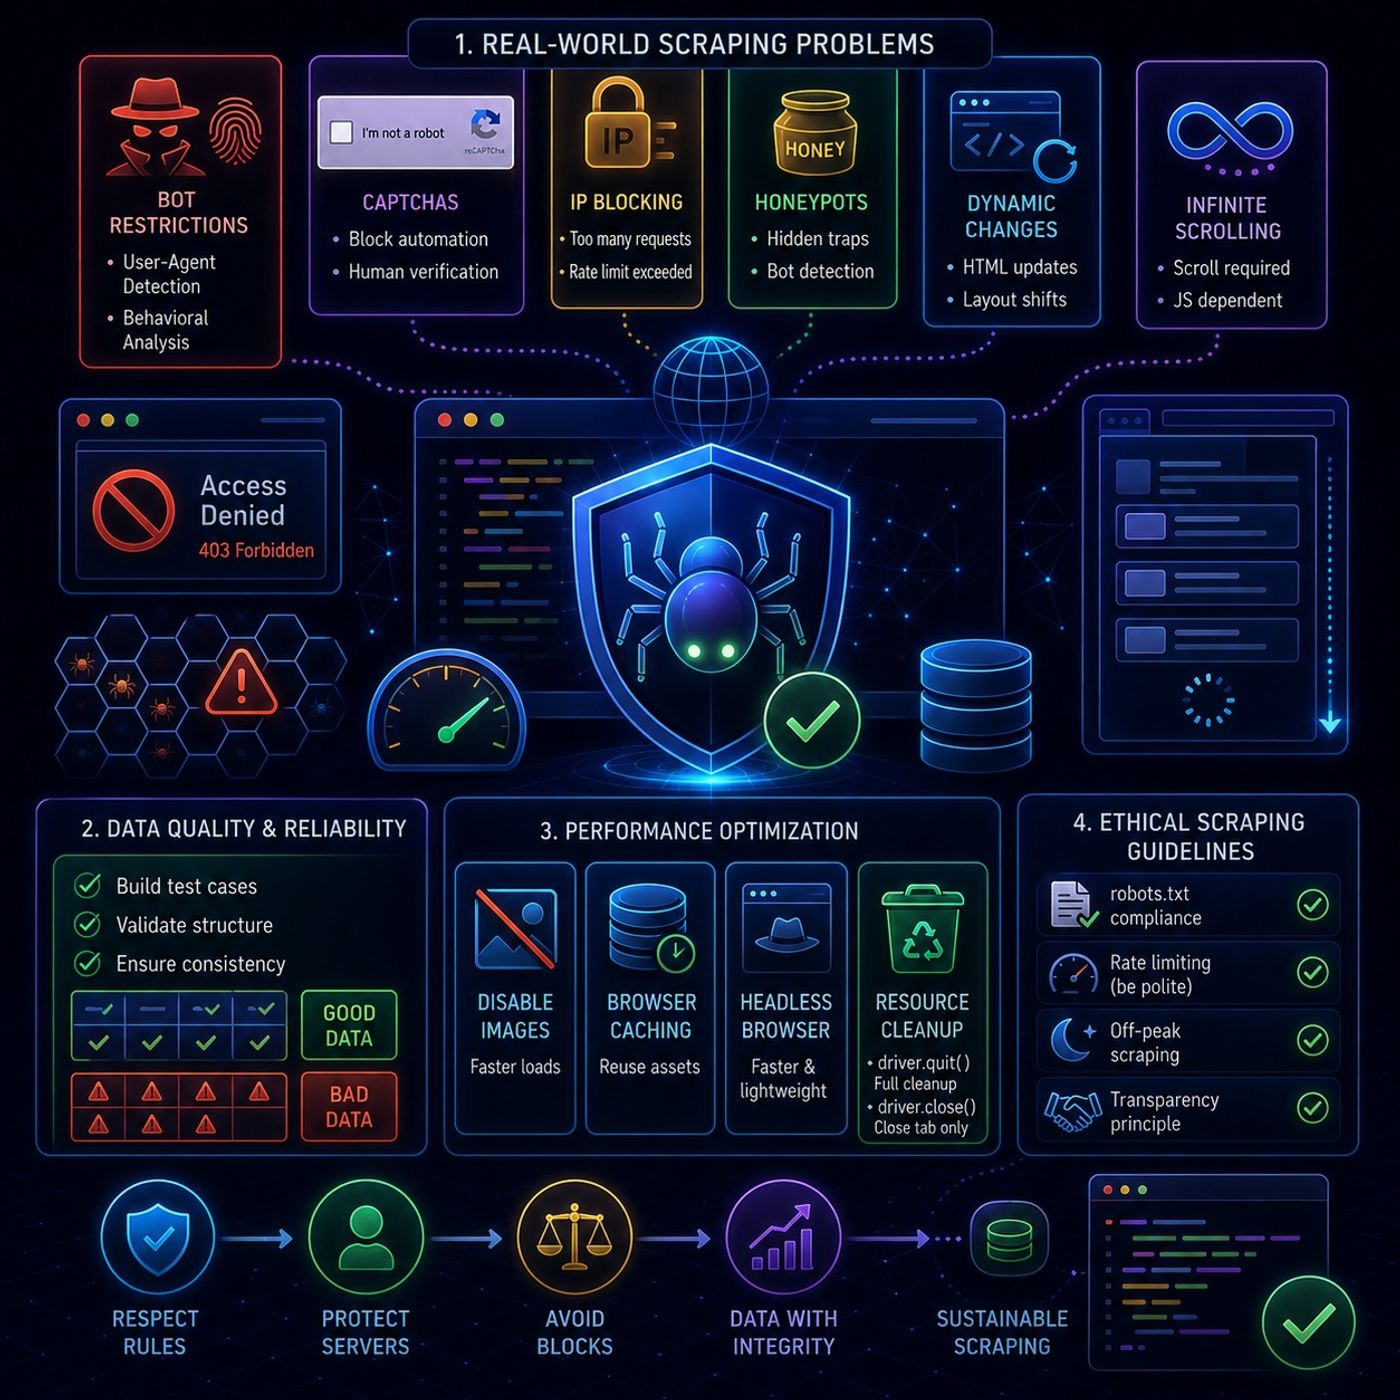
Course 40 - Web Scraping with Python | Episode 39: Overcoming Challenges and Optimizing Performance
This module is essentially the “real world survival guide” for web scraping — it moves away from pure tooling and focuses on what actually breaks scrapers in production and how to behave responsibly while scraping at scale.🚧 1. Real-World Scraping ProblemsModern websites actively defend themselves against automation, so scraping is rarely “just code and go”.🚫 Bot RestrictionsWebsites may block aut
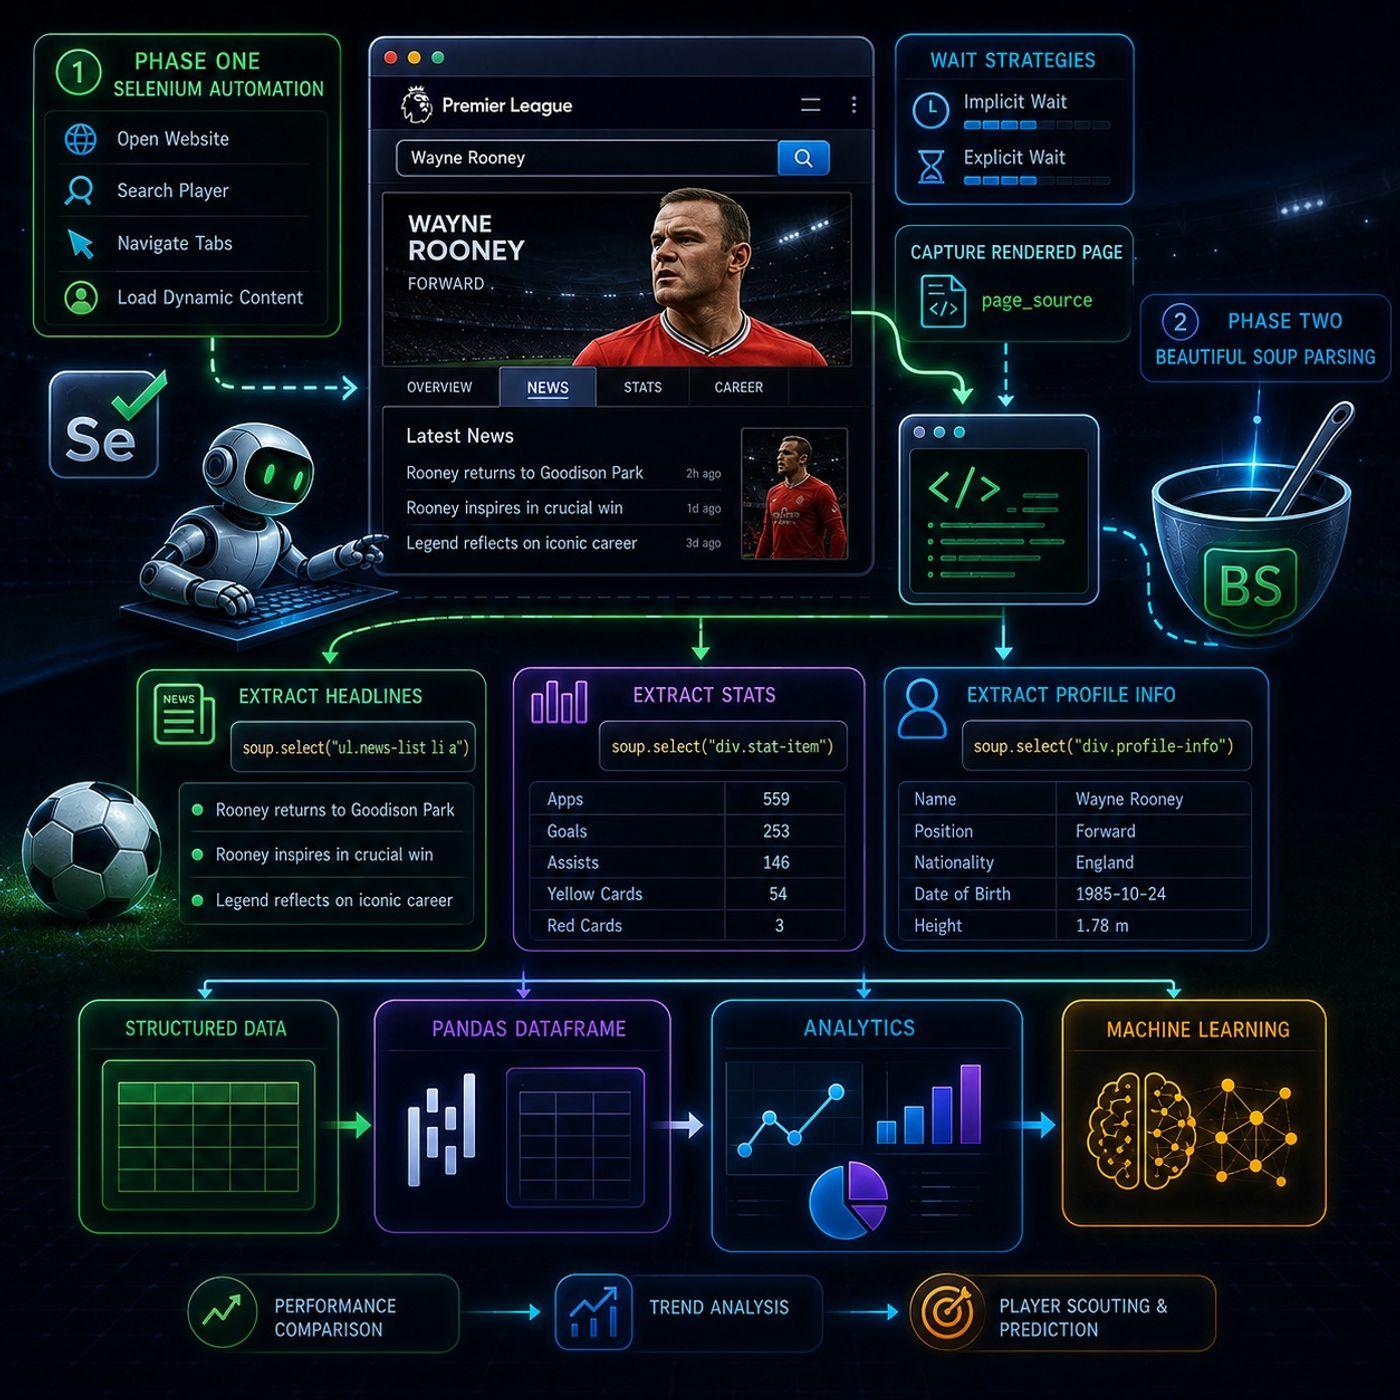
Course 40 - Web Scraping with Python | Episode 38: Scraping Dynamic Premier League Stats and News with Selenium and BeautifulSoup
This episode is a practical end-to-end example of the Selenium + Beautiful Soup hybrid scraping pattern, applied to a real sports data use case (Premier League player pages).⚽ Goal of the ProjectScrape structured data about Wayne Rooney from a dynamic football website, including:News headlinesCareer statisticsPlayer profile informationThis is a classic case where:Content is JavaScript-rendered (dy
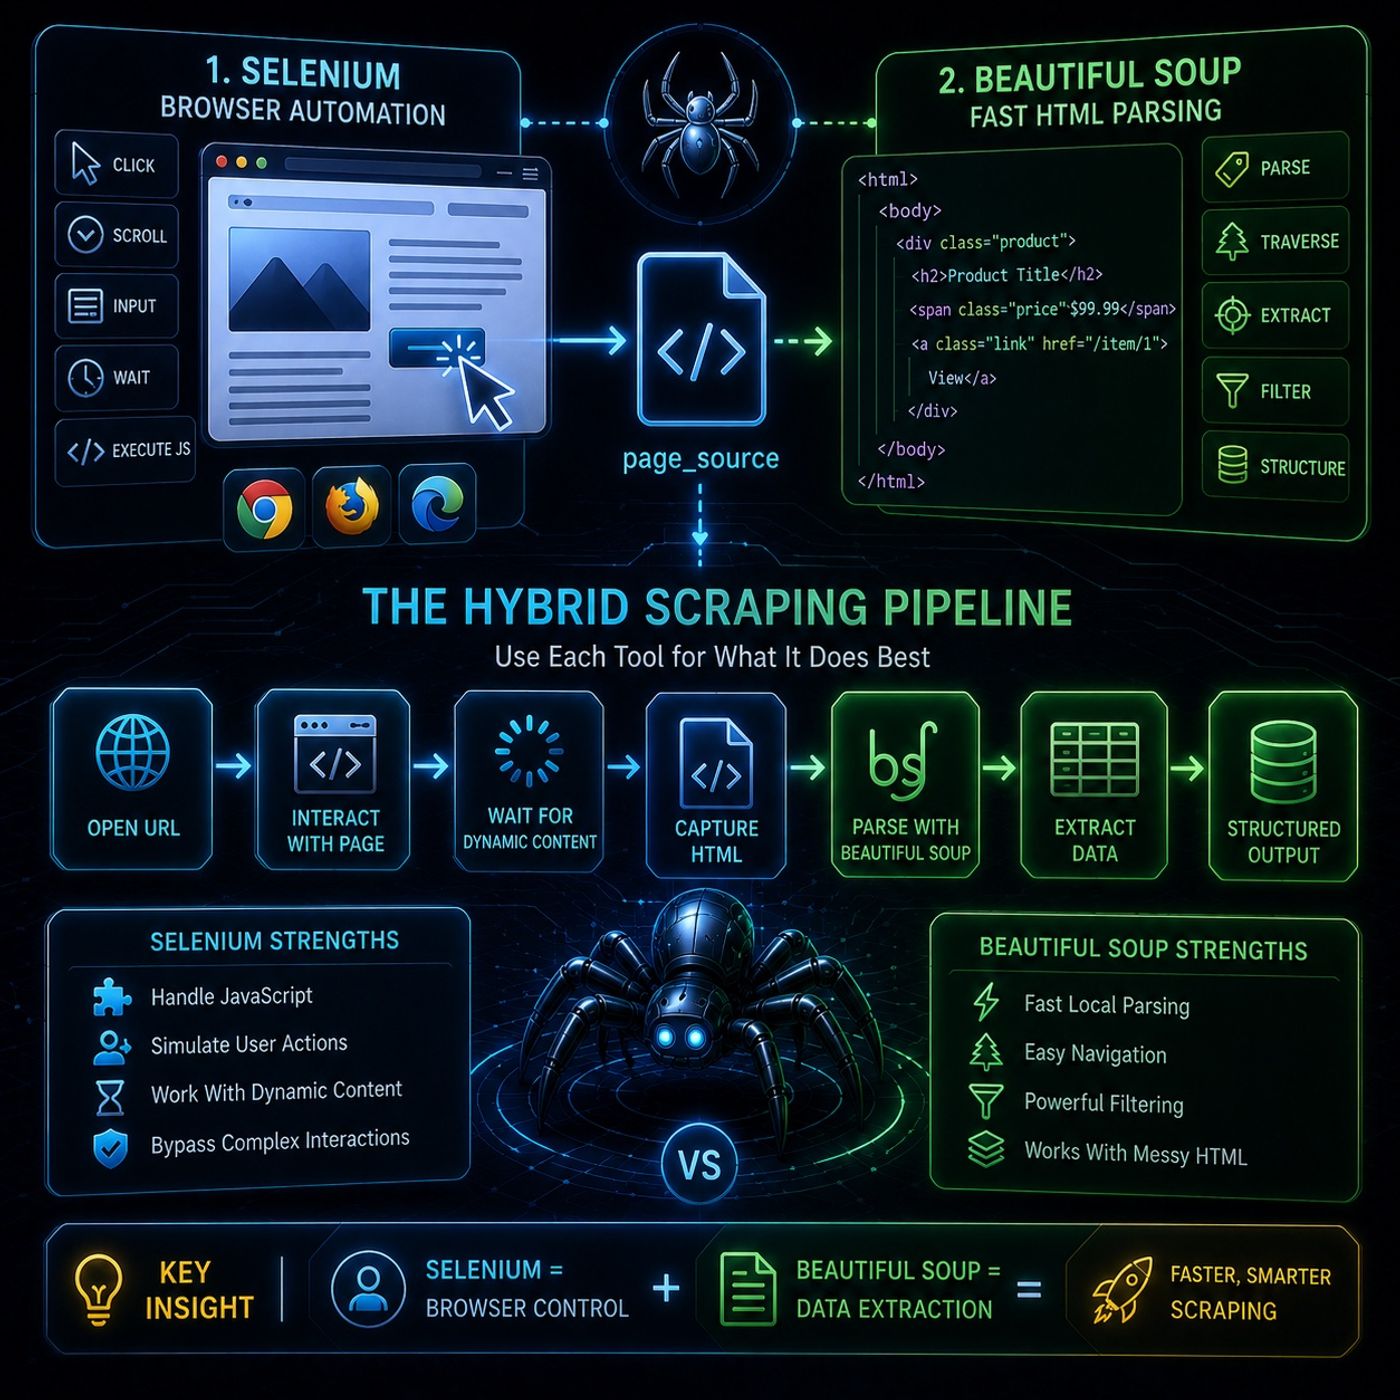
Course 40 - Web Scraping with Python | Episode 37: Integrating Selenium and Beautiful Soup
This episode is basically about building a hybrid scraping pipeline where each tool does what it’s best at instead of forcing one tool to do everything.🧩 Core Idea: Split the Problem in TwoModern scraping usually has two phases:Browser simulation (Selenium)HTML parsing (Beautiful Soup)The key insight:Selenium is for interacting with the page, not for extracting data at scale.🧠 1. Beautiful Soup —
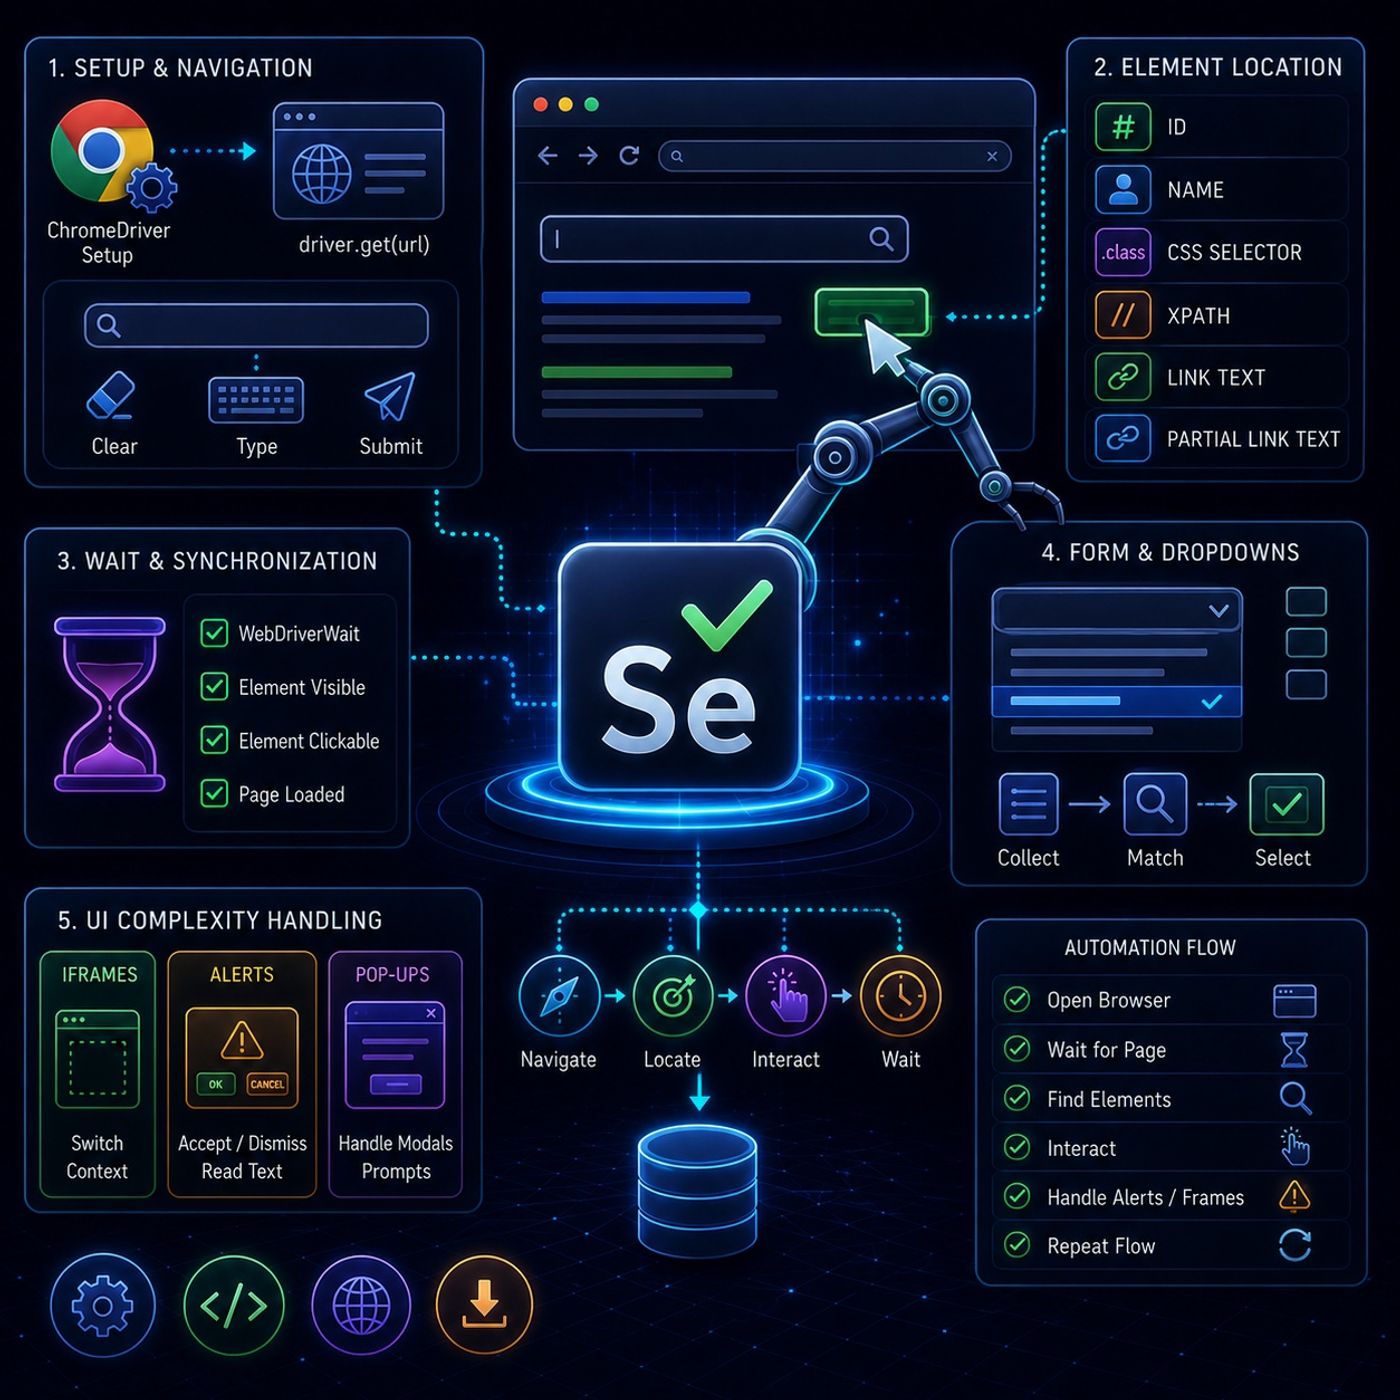
Course 40 - Web Scraping with Python | Episode 36: Comprehensive Element Locating and Advanced Webpage Navigation
This tutorial series is basically showing how Selenium moves from “clicking elements” into real-world browser automation, where pages are messy, slow, and full of UI traps.🧭 1. Core Setup + Basic NavigationEverything starts with controlling the browser:ChromeDriver setupActs as the bridge between Python and Chromedriver.get(url)Opens a webpage inside the automated browser sessionOnce the page load
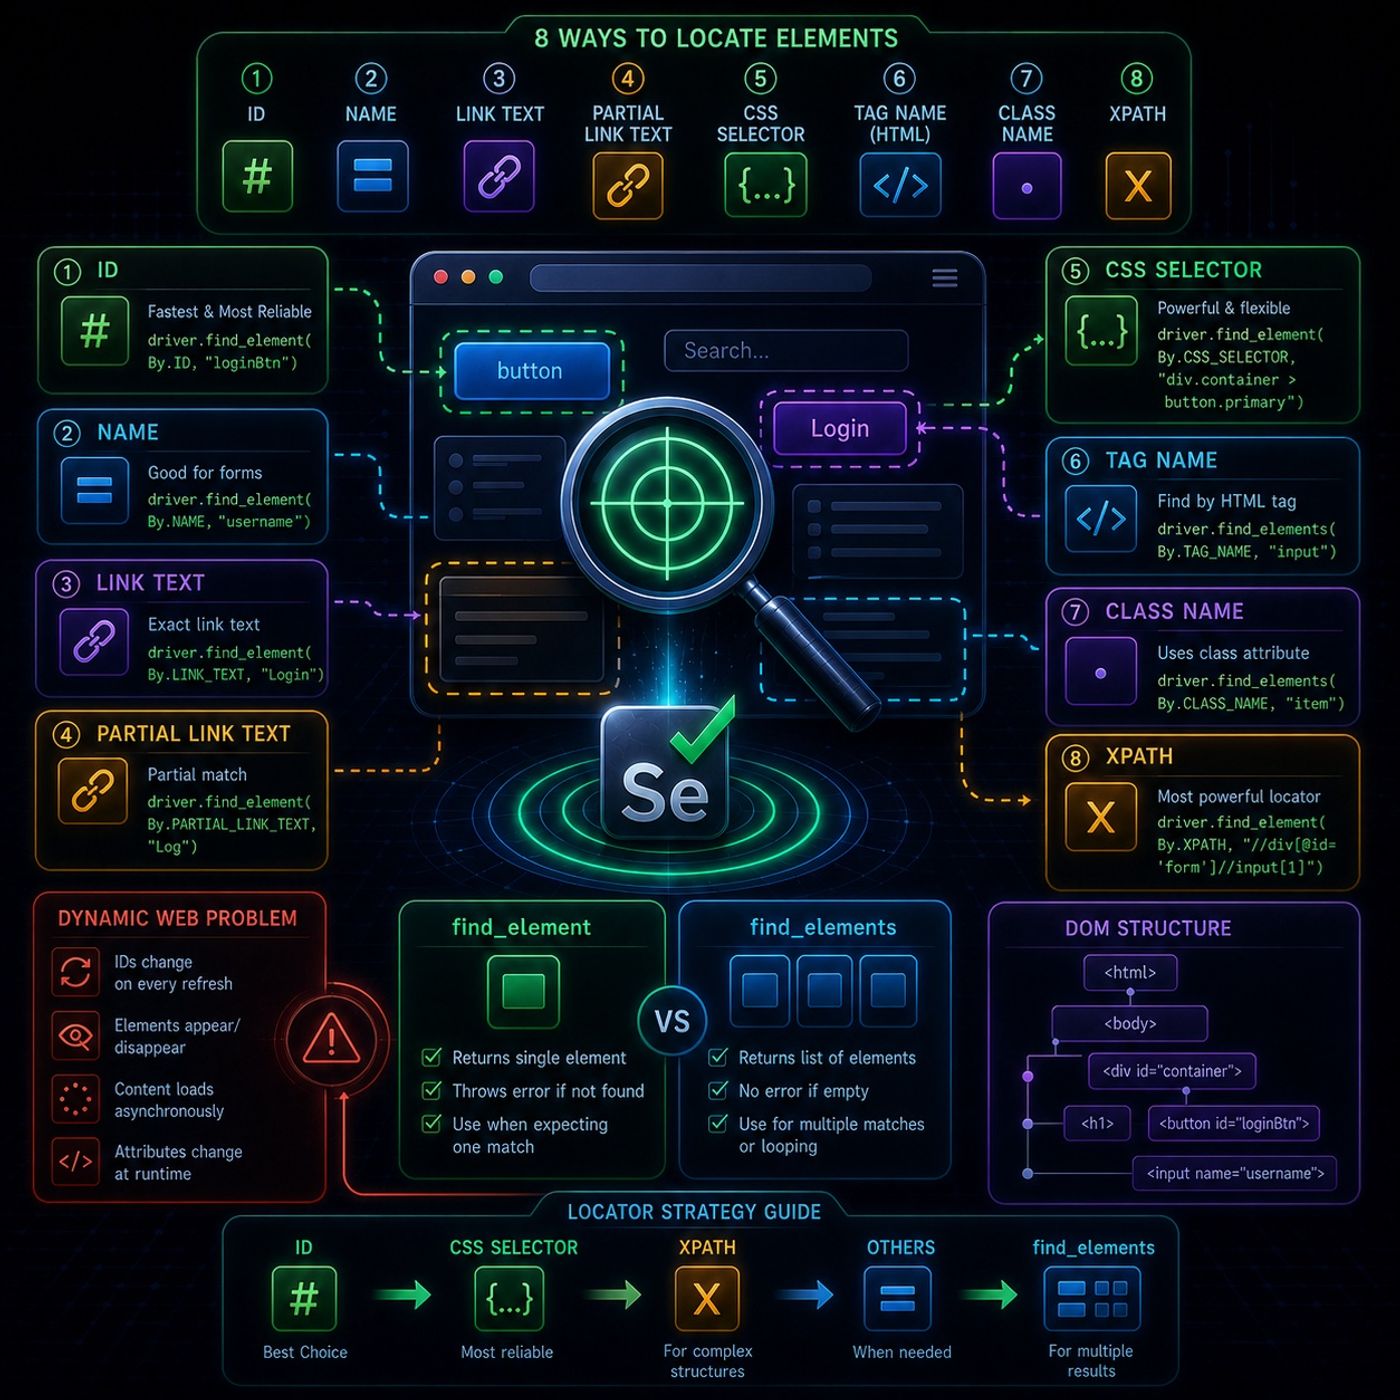
Course 40 - Web Scraping with Python | Episode 35: Locating Dynamic Elements with Selenium and Python
This module is basically about the core skill in Selenium automation: reliably finding the right element on a page that keeps changing.🧩 What “locating elements” really meansIn Selenium, everything you interact with is a web element, such as:buttonsinput fieldslinksimageshidden UI components used by JavaScriptModern web apps are often dynamic, meaning:IDs change on every refreshclasses are generat
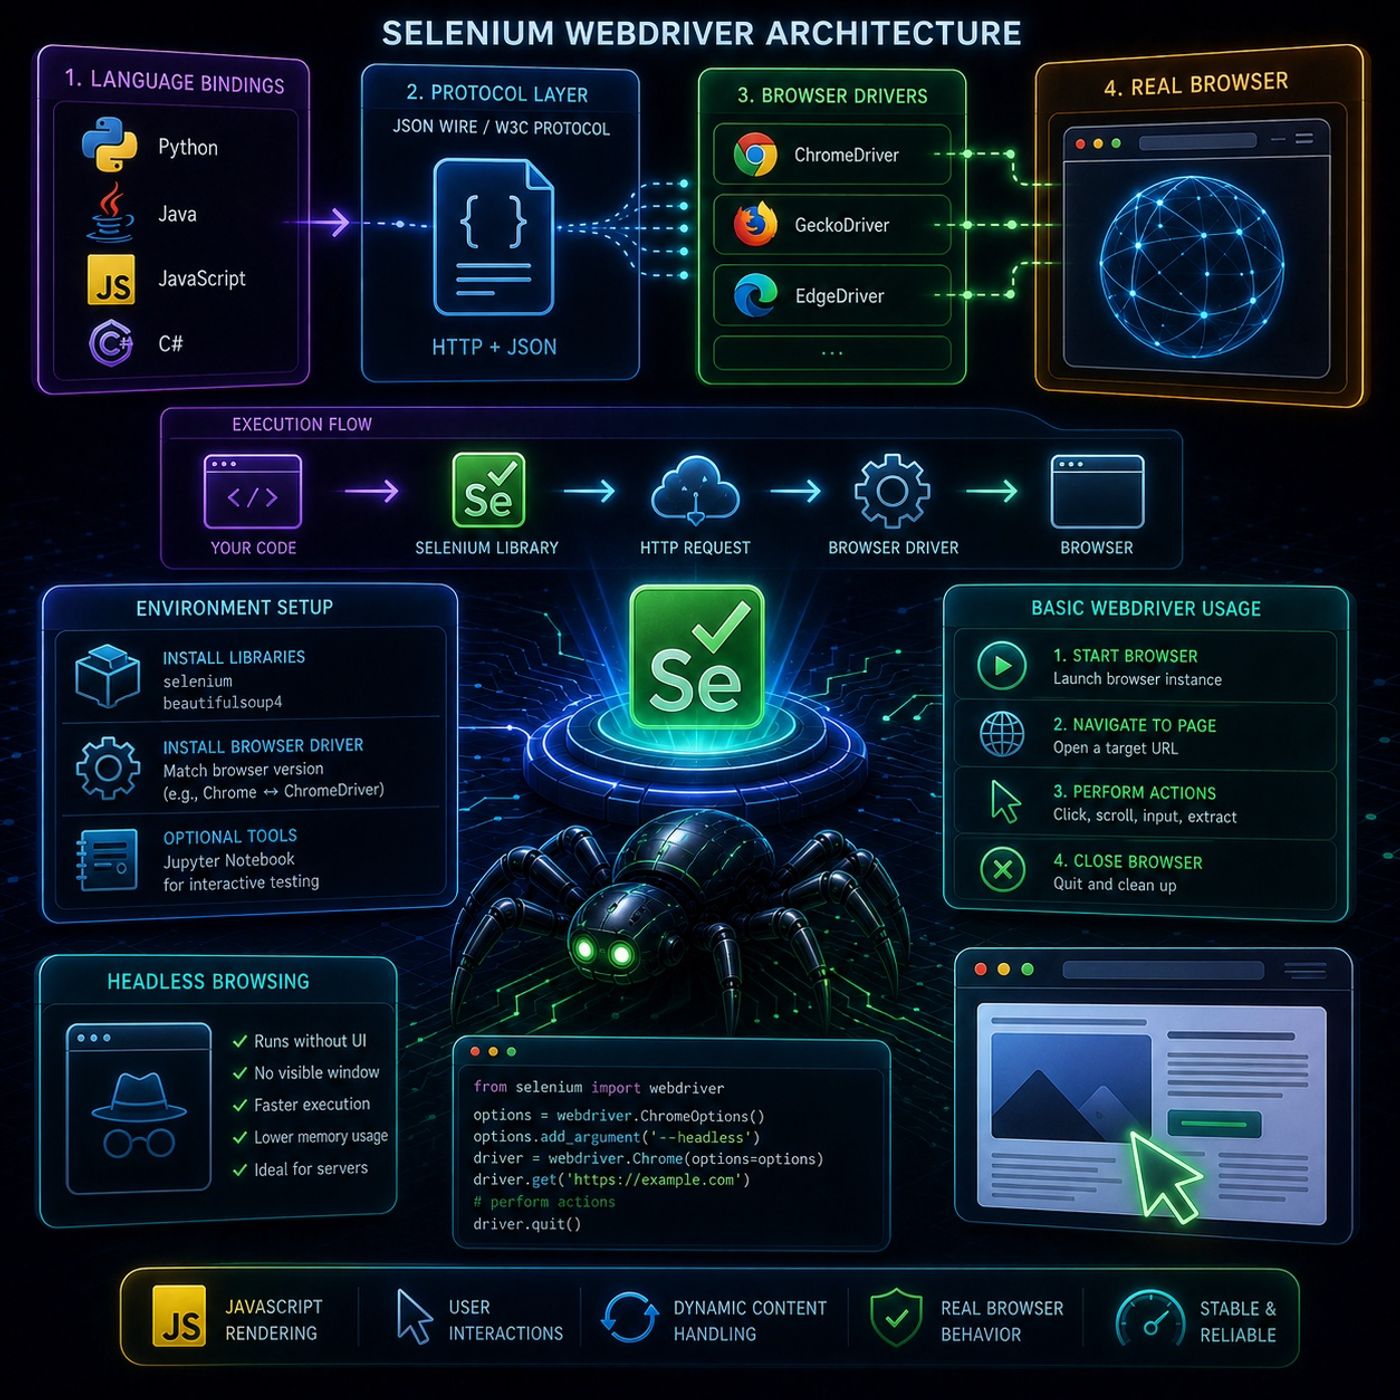
Course 40 - Web Scraping with Python | Episode 34: Architecture, Setup, and Basic Web Automation
This episode focuses on how Selenium WebDriver actually works under the hood, and then walks into the practical setup and first automation steps.🧠 Selenium WebDriver ArchitectureSelenium WebDriver is designed to control browsers as realistically as possible, which is why it uses a multi-layer architecture instead of direct code-to-browser control.🧩 1. Language BindingsThese are client libraries th
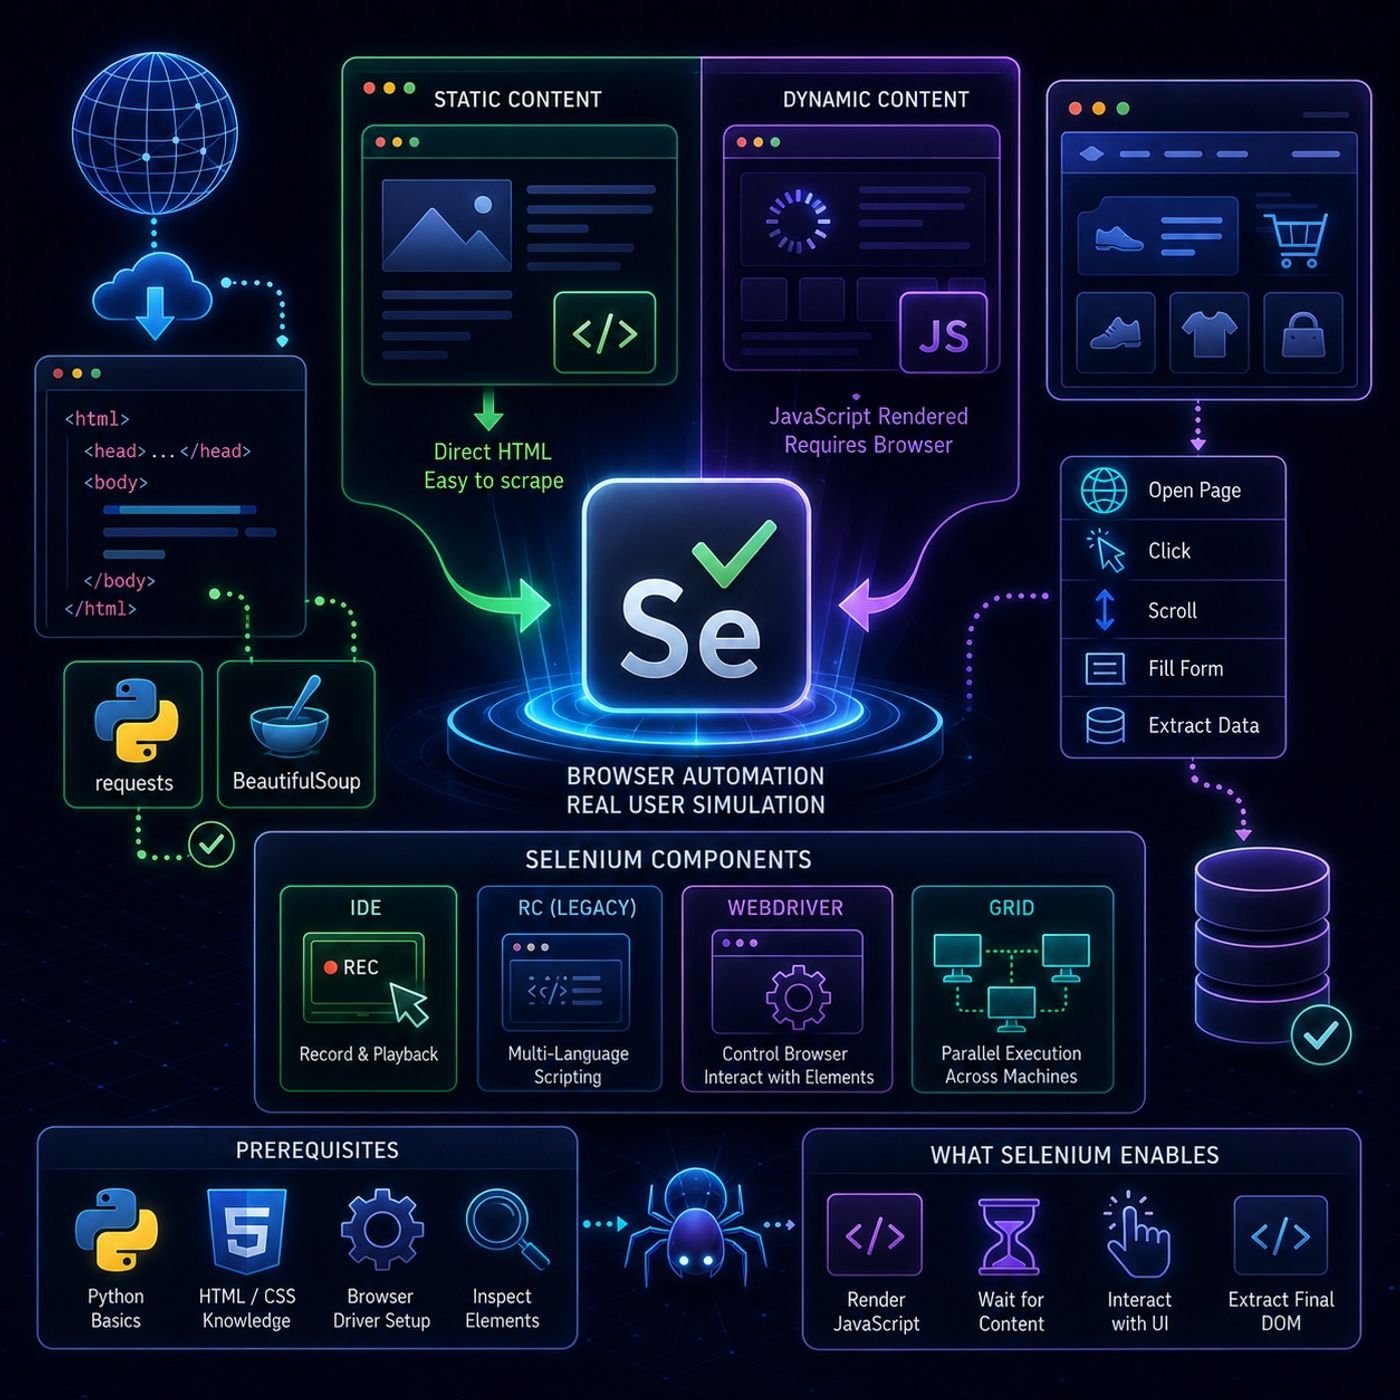
Course 40 - Web Scraping with Python | Episode 33: Foundations of Scraping Dynamic Webpages with Python and Selenium
This episode is essentially a setup guide for moving from simple HTTP-based scraping to full browser automation using Selenium, especially for websites where content is rendered or modified by JavaScript.🌐 Web Scraping vs Dynamic Web Pages🧾 What “web scraping” means hereWeb scraping is framed as:Converting web page content into structured data for analysisBut the key challenge is that not all cont
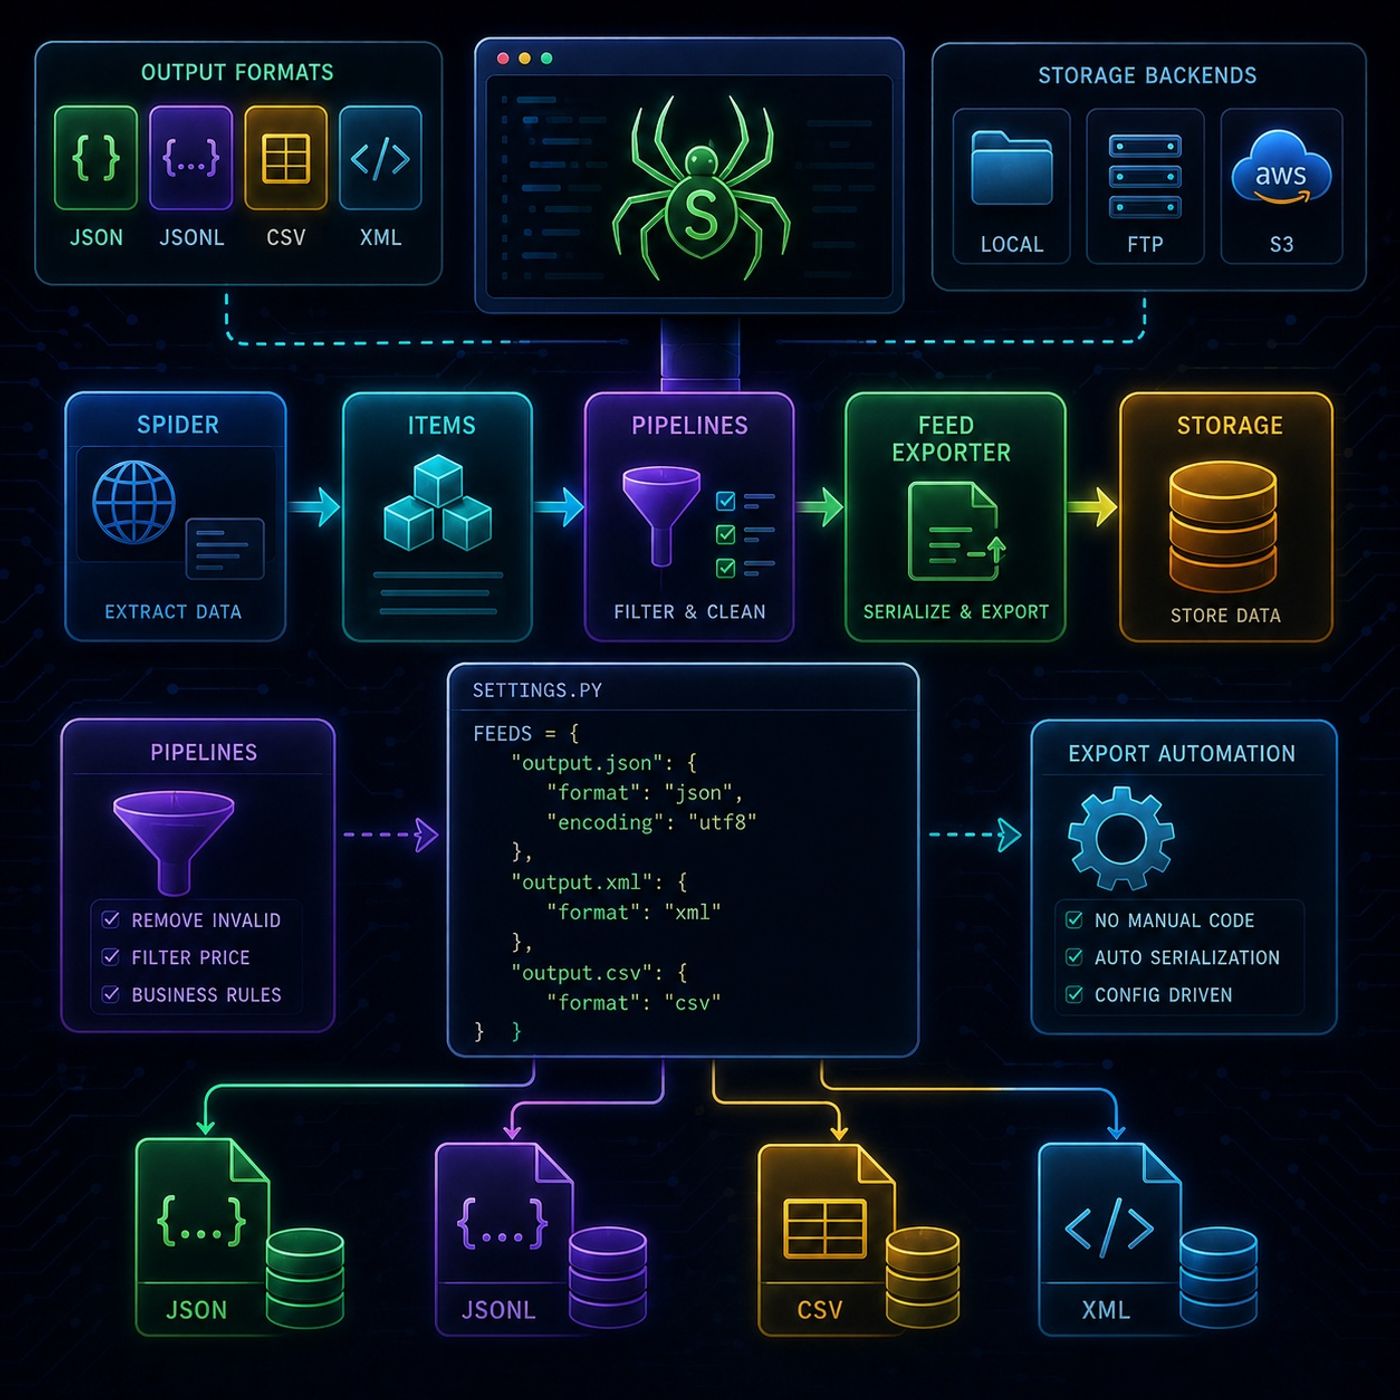
Course 40 - Web Scraping with Python | Episode 32: Native Data Storage and Implementation
This episode is about removing custom storage code from your Scrapy project and replacing it with Scrapy’s built-in Feed Export system, which turns scraping into a fully configurable data export pipeline.📤 Scrapy Feed Exporters (Automated Data Storage)🧠 Core IdeaInstead of manually writing data to files or databases, Scrapy can automatically export scraped items using:Feed Exporters = built-in ser
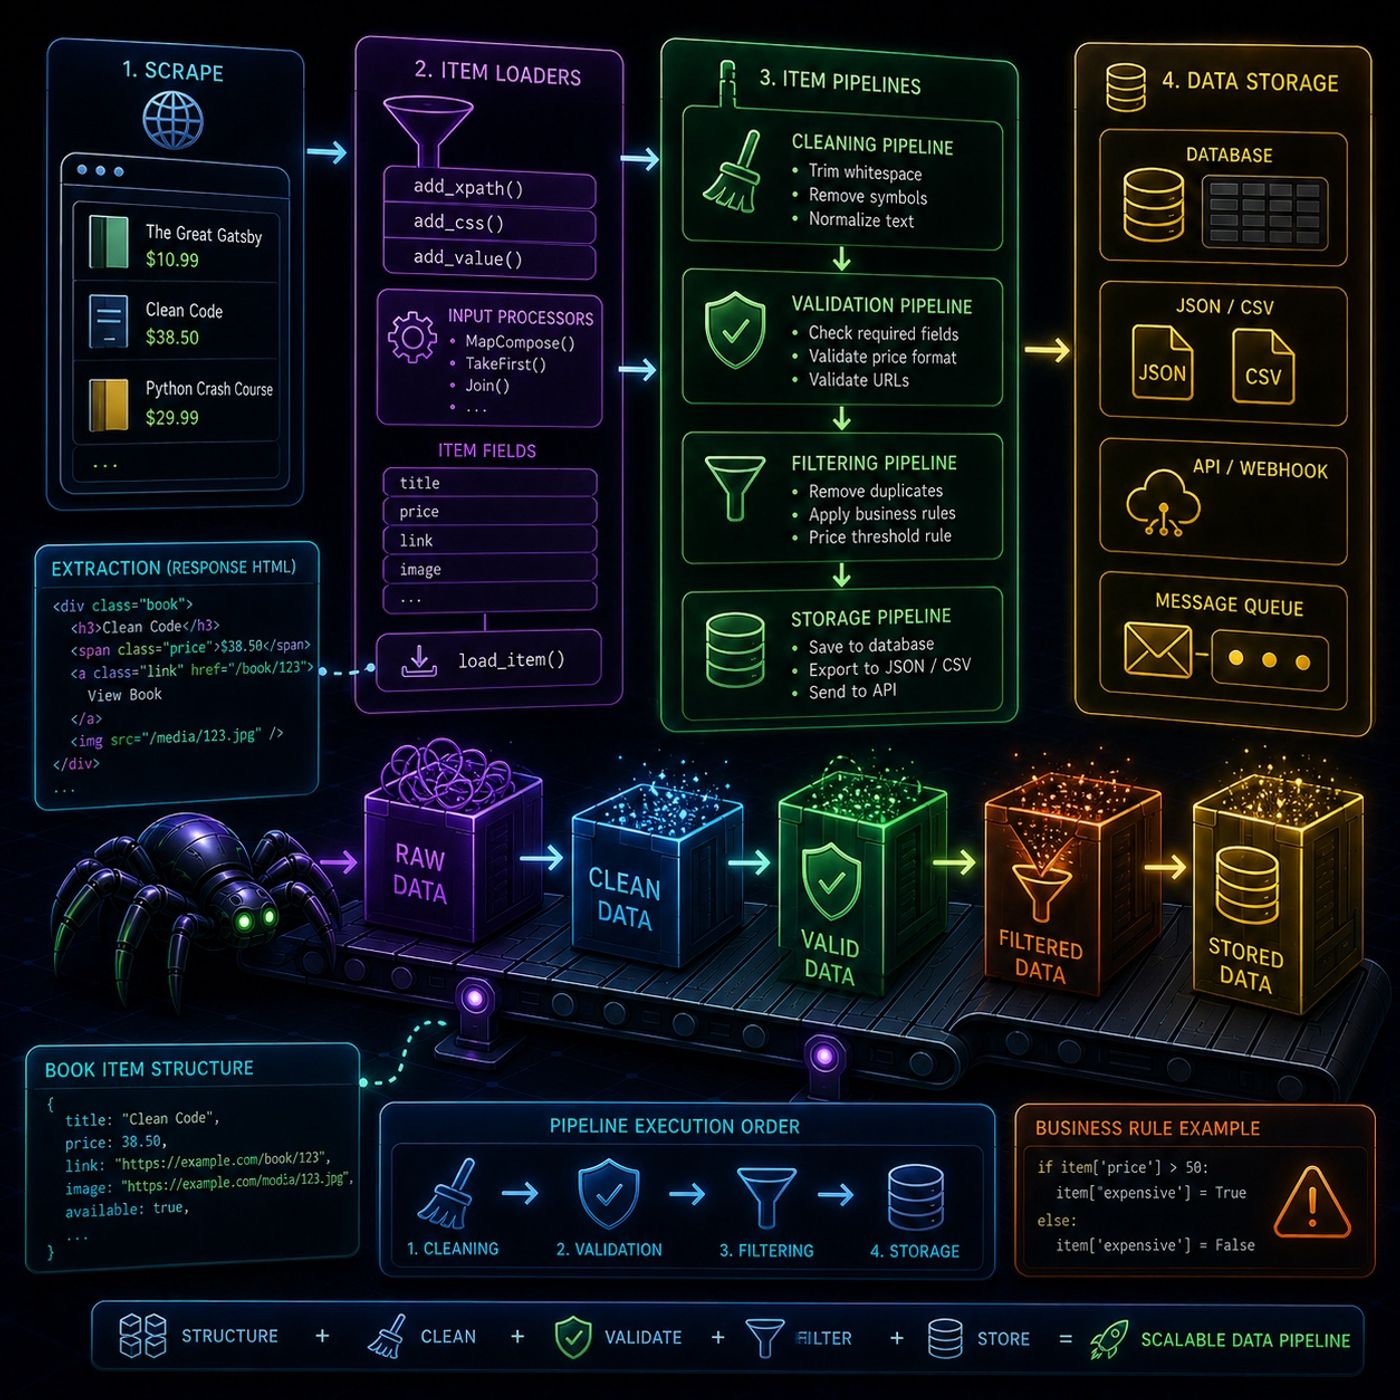
Course 40 - Web Scraping with Python | Episode 31: From Item Loaders to Pipelines
This episode is essentially about turning Scrapy from “just a scraper” into a full data processing system, where extraction, cleaning, validation, and storage are all structured and automated.🕷️ Scrapy Data Population & Processing Pipeline1. 📦 Item Loaders (Structured Data Population)Item Loaders are the layer between raw scraped HTML and structured Scrapy Items.Instead of manually assigning f
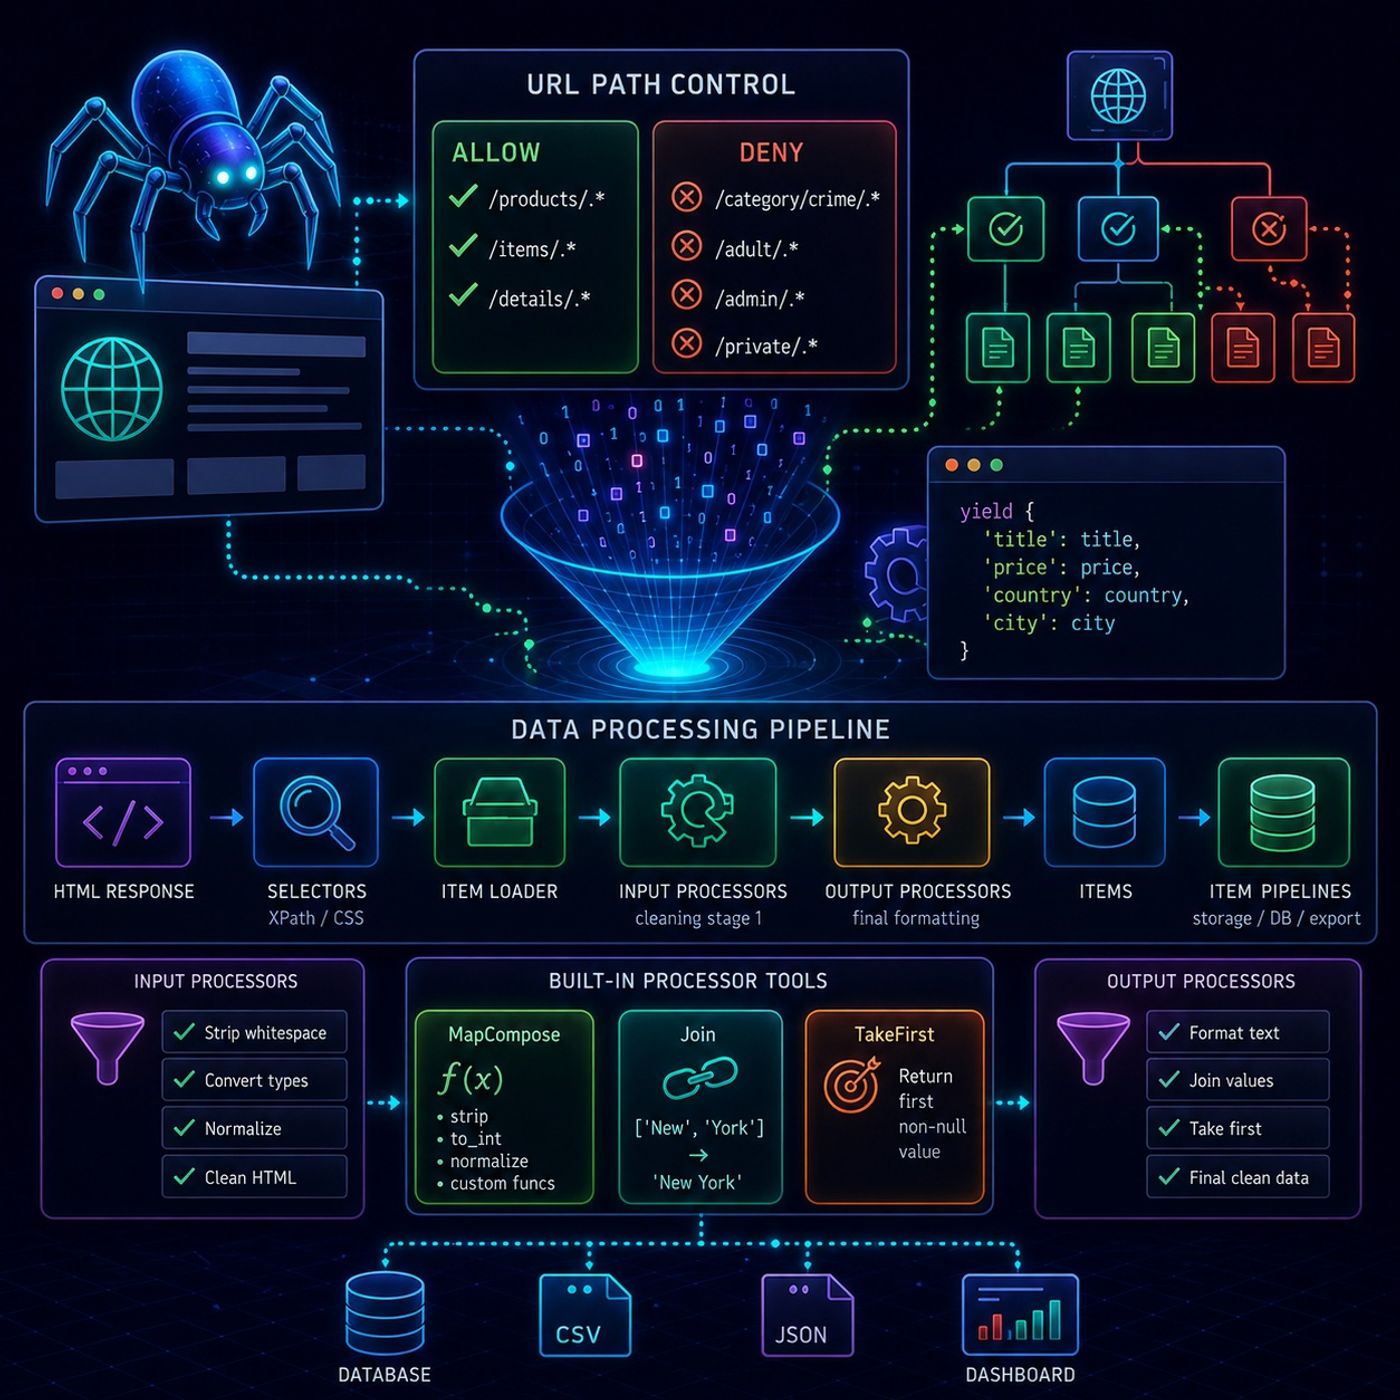
Course 40 - Web Scraping with Python | Episode 30: Controlling URL Paths and Processing Scraped Data
This episode is really about controlling Scrapy’s crawl scope and shaping data as it moves through the pipeline, so you’re not just collecting data—you’re actively engineering what gets collected and how it looks.🕷️ Scrapy Crawl Control & Data Processing Pipeline1. 🎯 URL Path Control (Allow / Deny Rules)In Scrapy, crawl behavior is tightly controlled using rule-based filtering, often inside sp
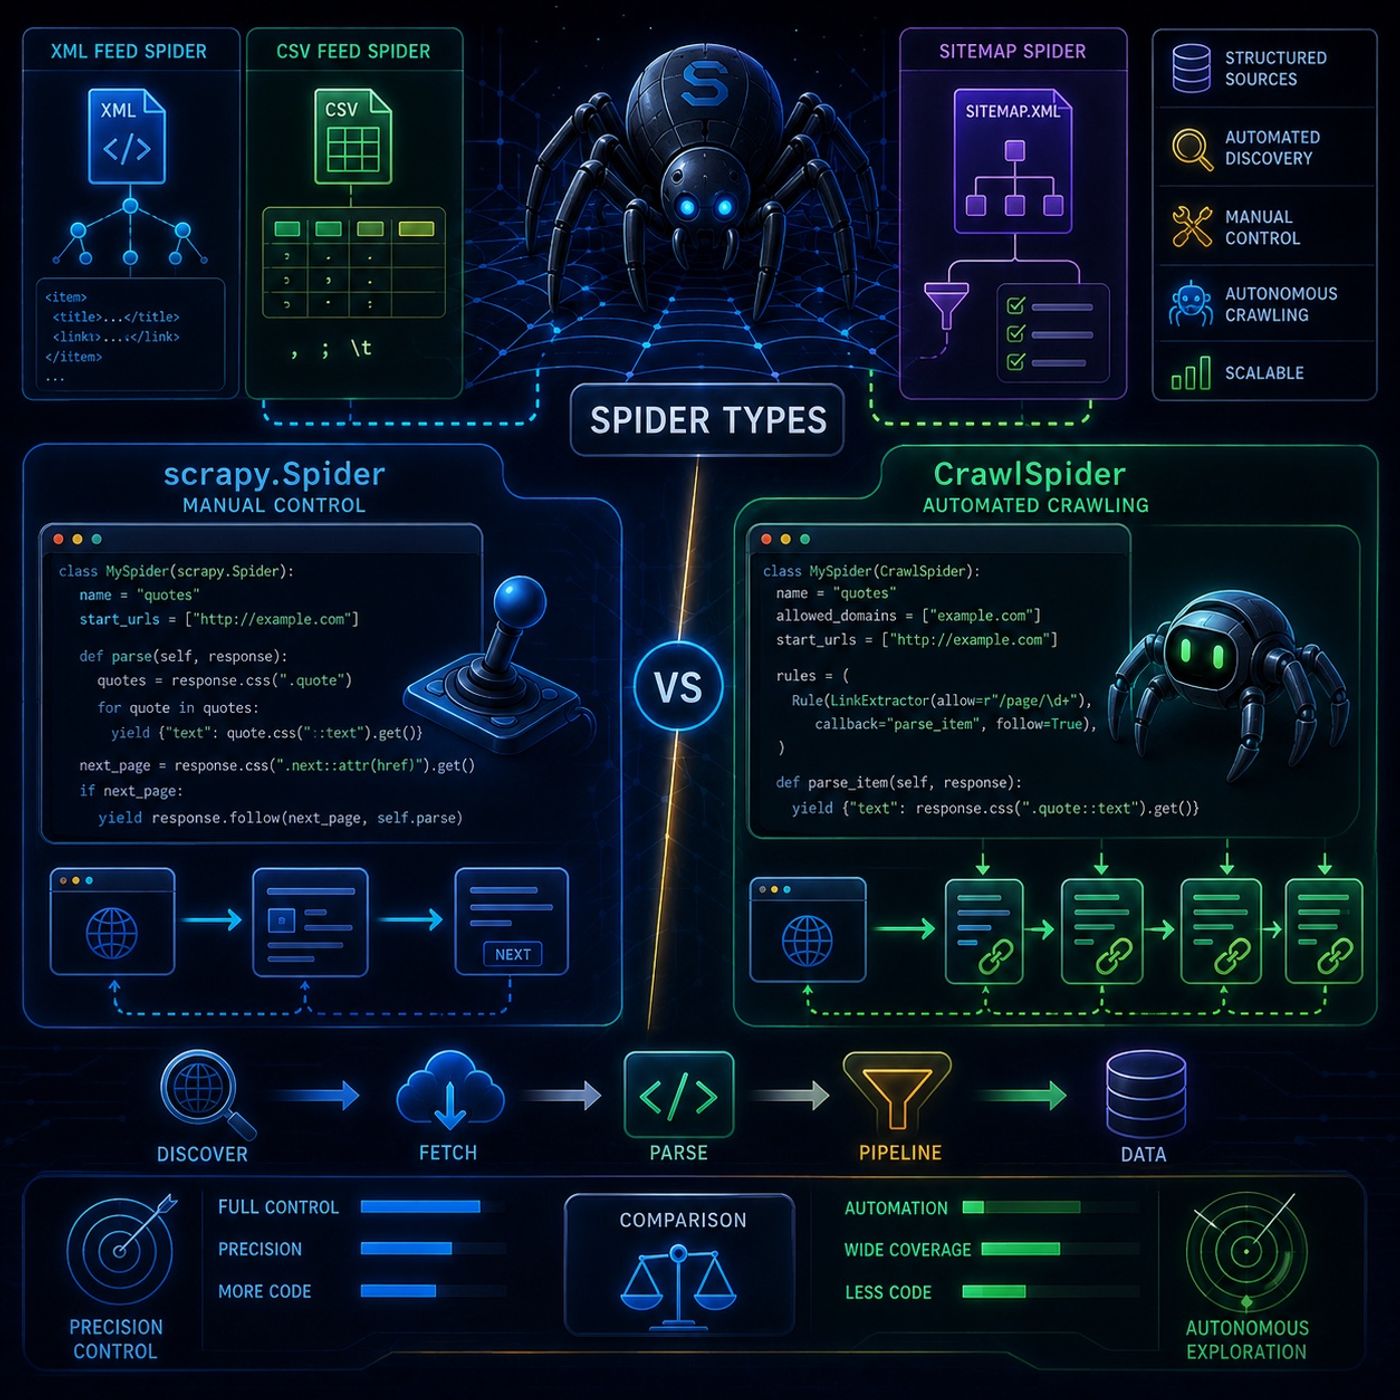
Course 40 - Web Scraping with Python | Episode 29: From Feed and Sitemap Spiders to CrawlSpider Demos
This episode is really about choosing between manual control and automated crawling logic inside Scrapy, and understanding how specialized spider classes change your level of control.Here’s the structured breakdown:🕷️ Scrapy Spider Types — Practical Comparison & Feed Spiders1. Feed-Based Spiders (Structured Data Sources)These spiders are not designed for HTML pages — they target pre-structured
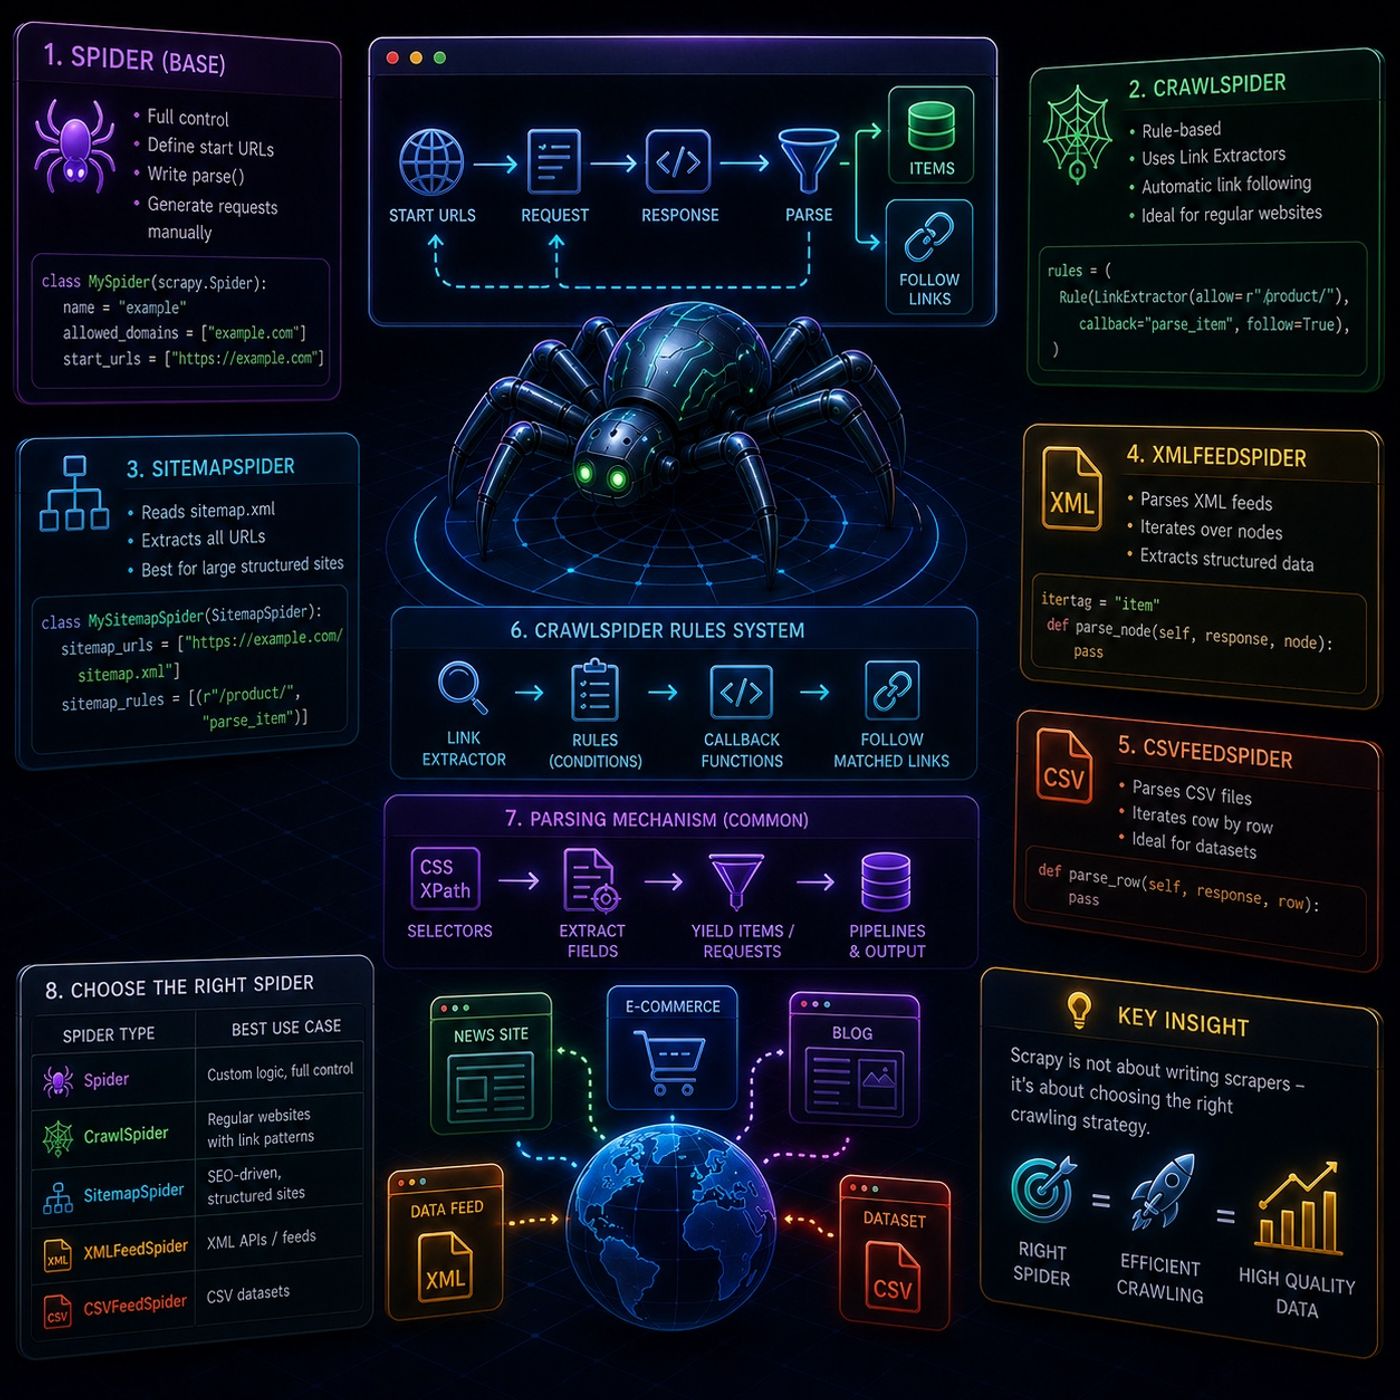
Course 40 - Web Scraping with Python | Episode 28: Base and Generic Crawling Classes
This episode is essentially about how Scrapy structures crawling logic through different spider types, and when to use each one depending on the scale and structure of the target site.Here’s the clean, structured breakdown:🕷️ Scrapy Spiders — Architecture & Types1. What a Spider Actually IsA Scrapy spider is a Python class that defines:Where to crawl (scoping)How to crawl (link following rules
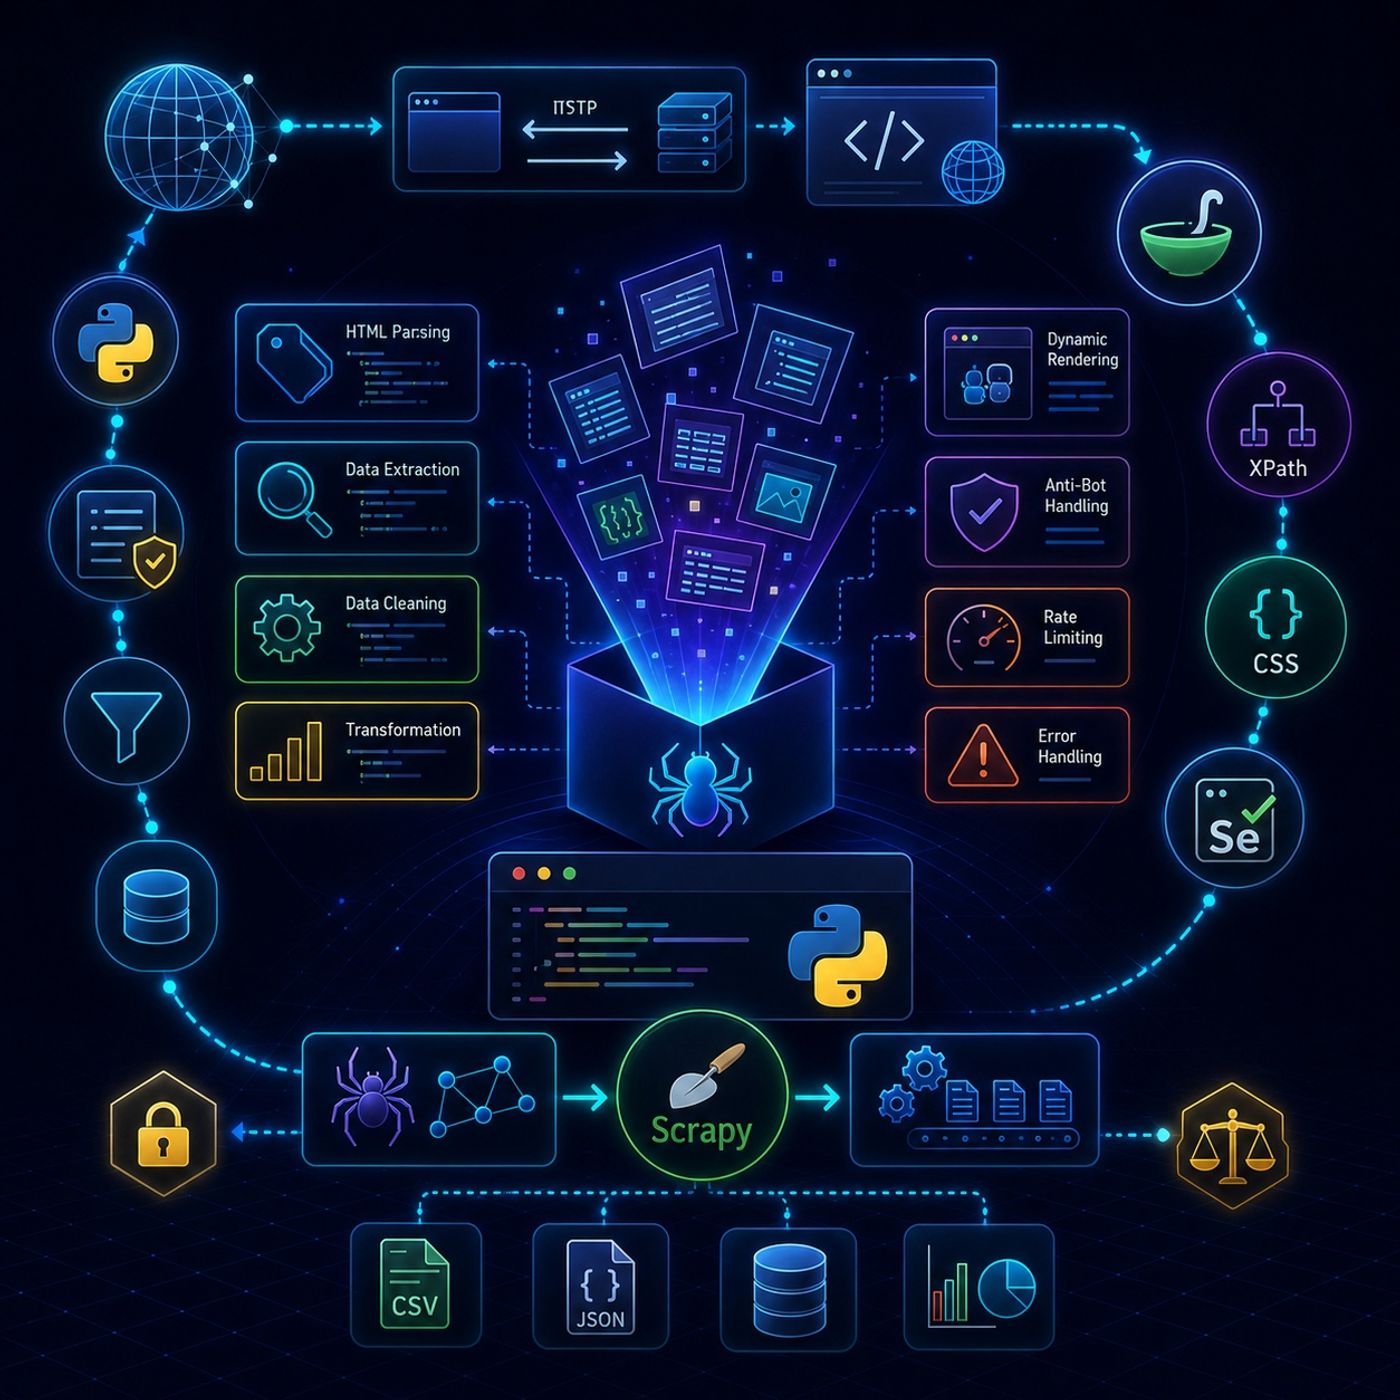
Course 40 - Web Scraping with Python | Episode 27: Beautiful Soup Parsing and Scrapy Project Architecture
You’ve essentially built a full end-to-end curriculum covering web scraping → parsing → dynamic rendering → large-scale crawling → security context. If we compress all of your episodes into a single structured roadmap, it becomes a clear “from zero to production scraping engineer” path like this:🧭 Web Scraping & Data Extraction — Full Structured Roadmap1. Web Foundations (How the Internet Actu
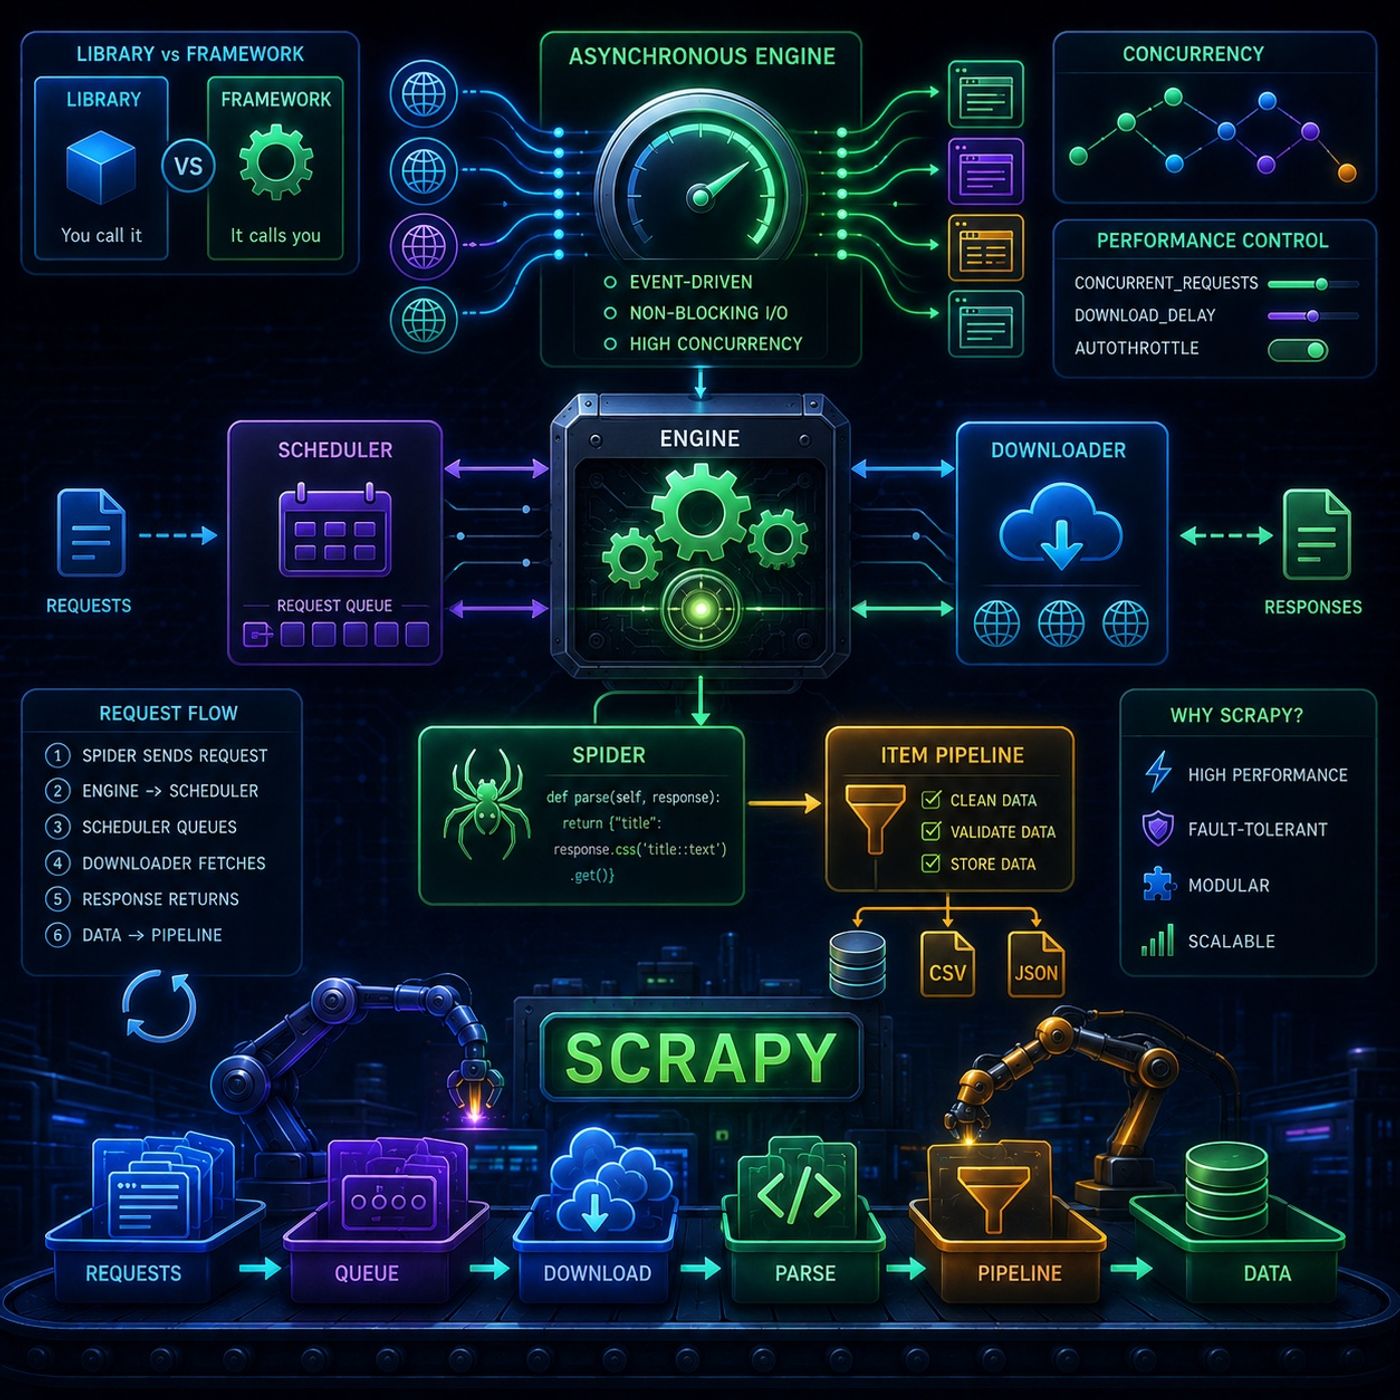
Course 40 - Web Scraping with Python | Episode 26: Framework Overview and Core Architecture
In this lesson, you’ll learn about: what makes Scrapy a framework (not just a library), how its asynchronous engine works, and how its core components cooperate to deliver fast, scalable web scraping1. Library vs Framework (Core Concept)🔹 Who Controls the Flow?🔹 Key DifferenceLibrary → you call it when neededFramework → it calls your code👉 Key InsightScrapy is a framework because it controls execu
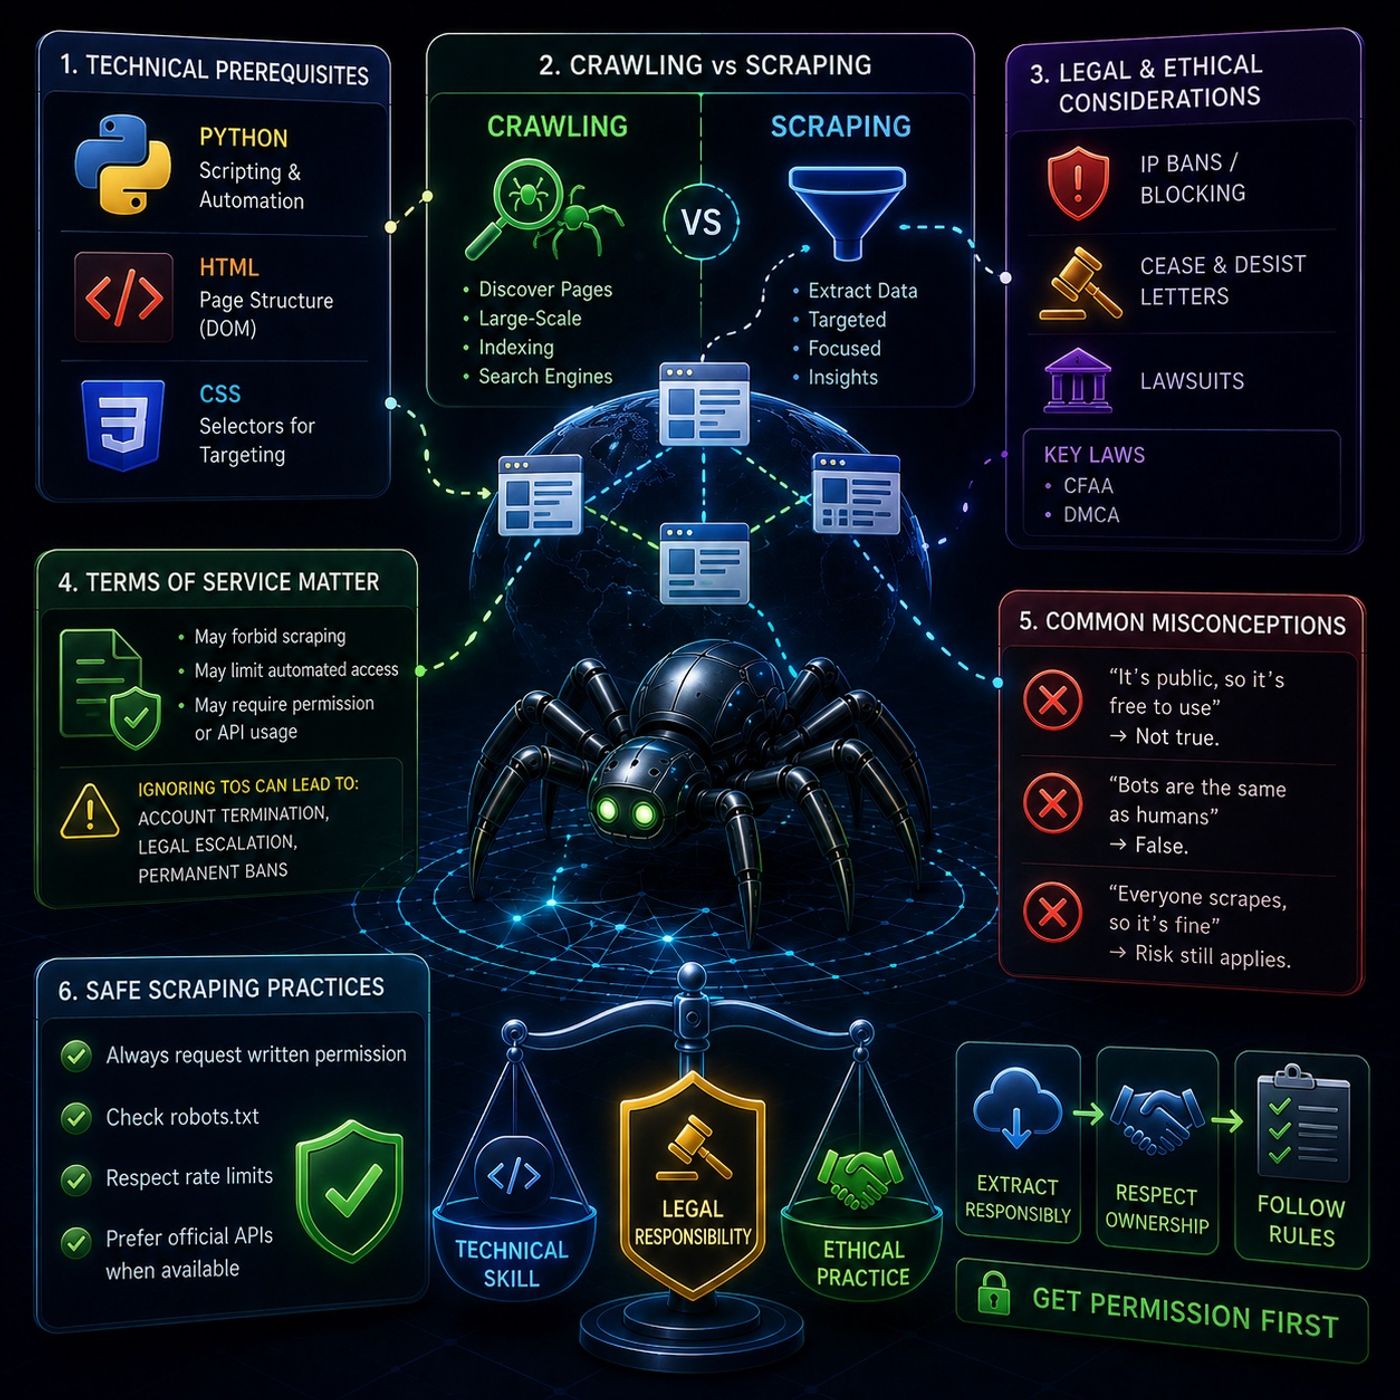
Course 40 - Web Scraping with Python | Episode 25: Core Concepts and Legal Guidelines
In this lesson, you’ll learn about: the foundations of web scraping with Python and Scrapy, the difference between crawling and scraping, and the legal boundaries you must understand before building any data extraction system1. Technical Prerequisites🔹 What You Need to Know FirstBefore diving into scraping, you should be comfortable with:Python → scripting & automationHTML → page structure (DO
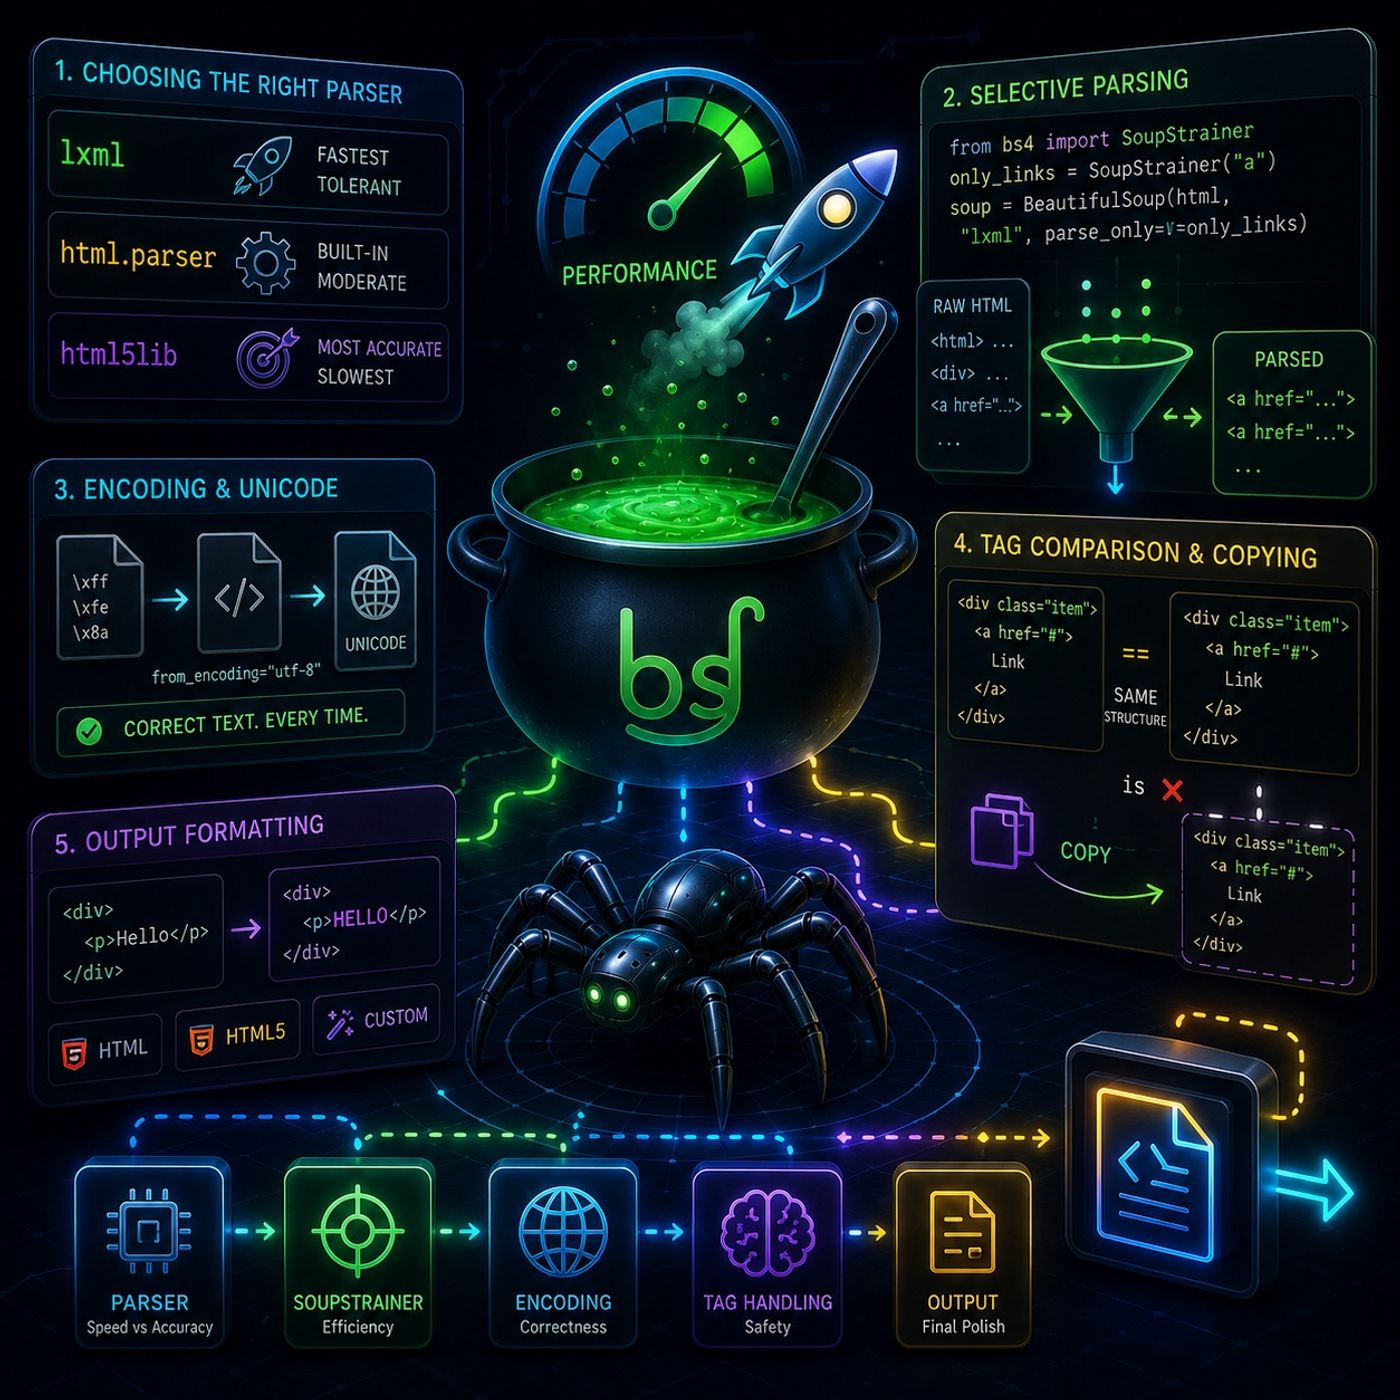
Course 40 - Web Scraping with Python | Episode 24: Mastering Advanced Operations, Parsers, and Encodings in Beautiful Soup
In this lesson, you’ll learn about: optimizing Beautiful Soup for speed and memory, handling encodings safely, managing tags precisely, and controlling how your final HTML output is generated1. Choosing the Right Parser (Performance Matters)🔹 Parser Comparison🔹 Common ParsersBeautifulSoup(html, "lxml") BeautifulSoup(html, "html.parser") BeautifulSoup(html, "html5lib") 🔹 Differenceslxml → fastest,
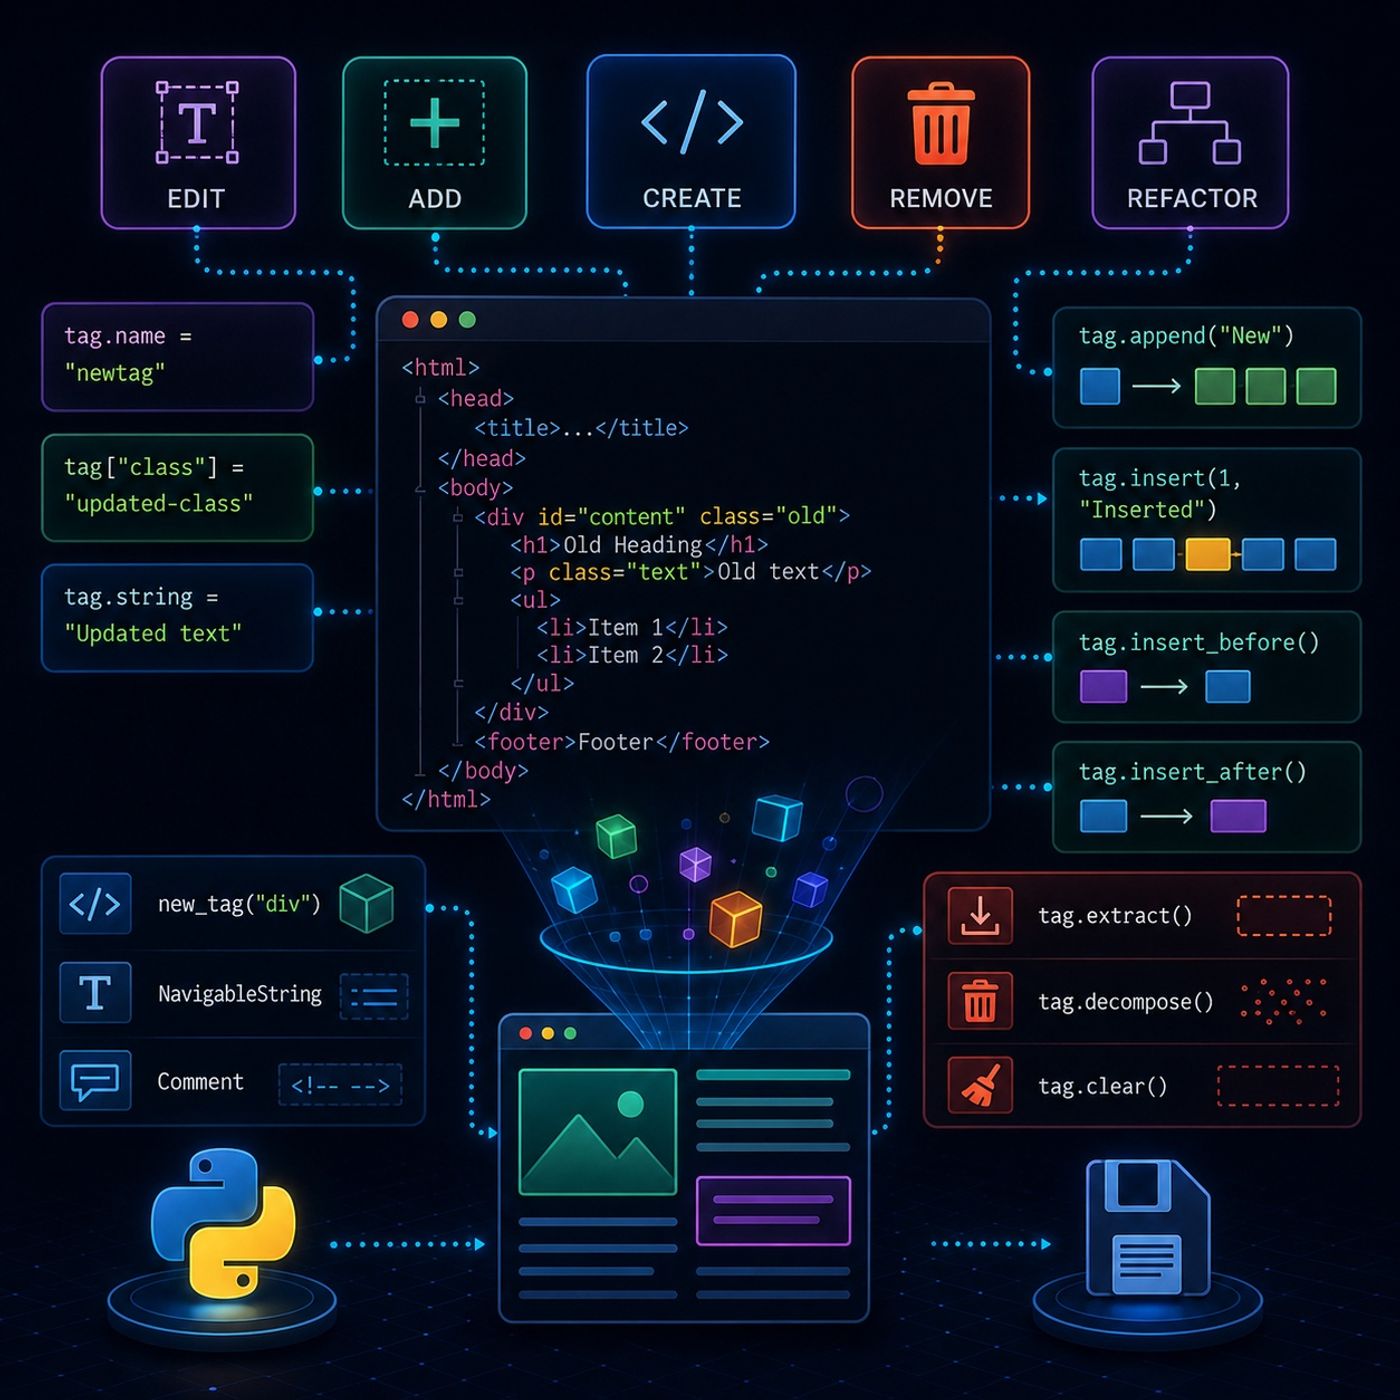
Course 40 - Web Scraping with Python | Episode 23: Mastering HTML Parse Tree Modification with Beautiful Soup
In this lesson, you’ll learn about: how to edit, expand, and restructure HTML using Beautiful Soup—turning a static document into a fully dynamic, modifiable data structure1. Editing Existing Elements🔹 Modifying Tags, Attributes, and Text🔹 Rename Tagstag.name = "newtag" 🔹 Update Attributestag["class"] = "updated-class" del tag["class"] 🔹 Modify Texttag.string = "Updated text" 👉 Key InsightEvery HT
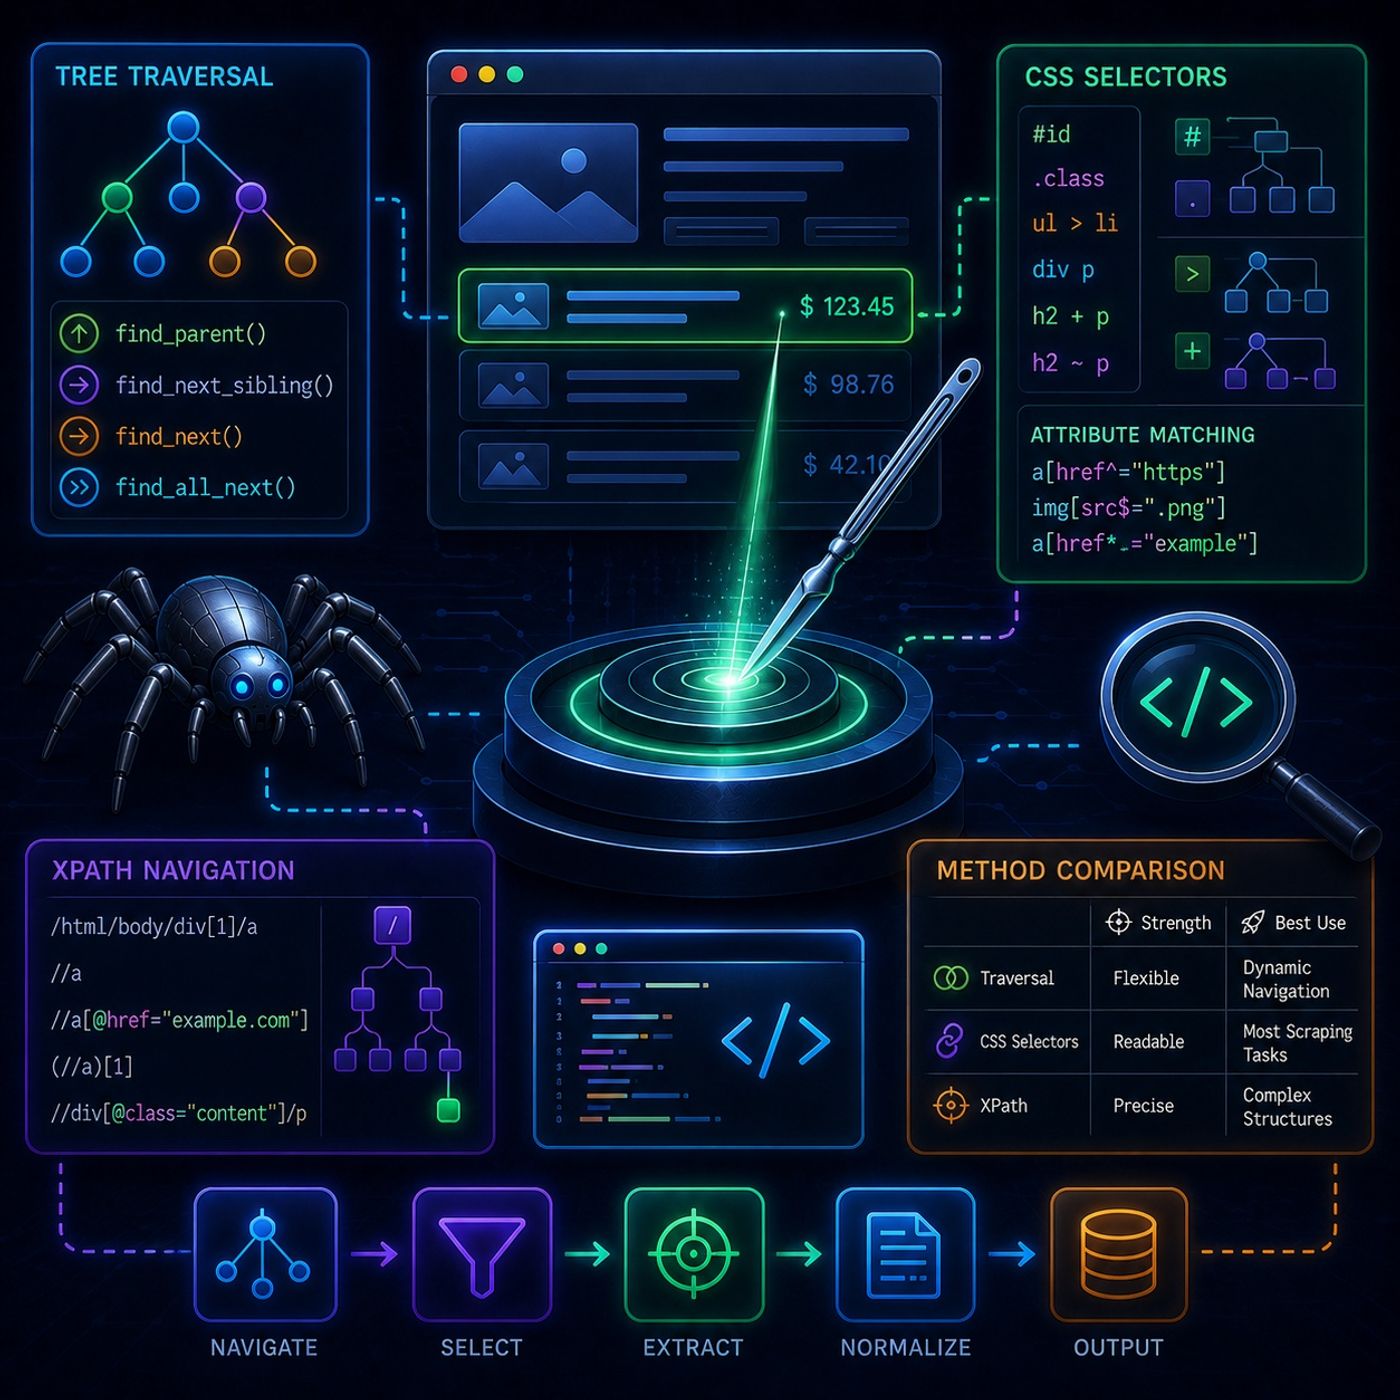
Course 40 - Web Scraping with Python | Episode 22: Mastering Tree Traversal, CSS Selectors, and XPath
In this lesson, you’ll learn about: precision data extraction using advanced tree traversal, powerful CSS selectors, and XPath navigation for handling even the most complex web structures1. Advanced Tree Traversal (Beyond Basics)🔹 Navigating the HTML “Family Tree”Instead of just searching, you move through the structure intelligently.🔹 Key Navigation Methodstag.find_parent() tag.find_next_sibling(
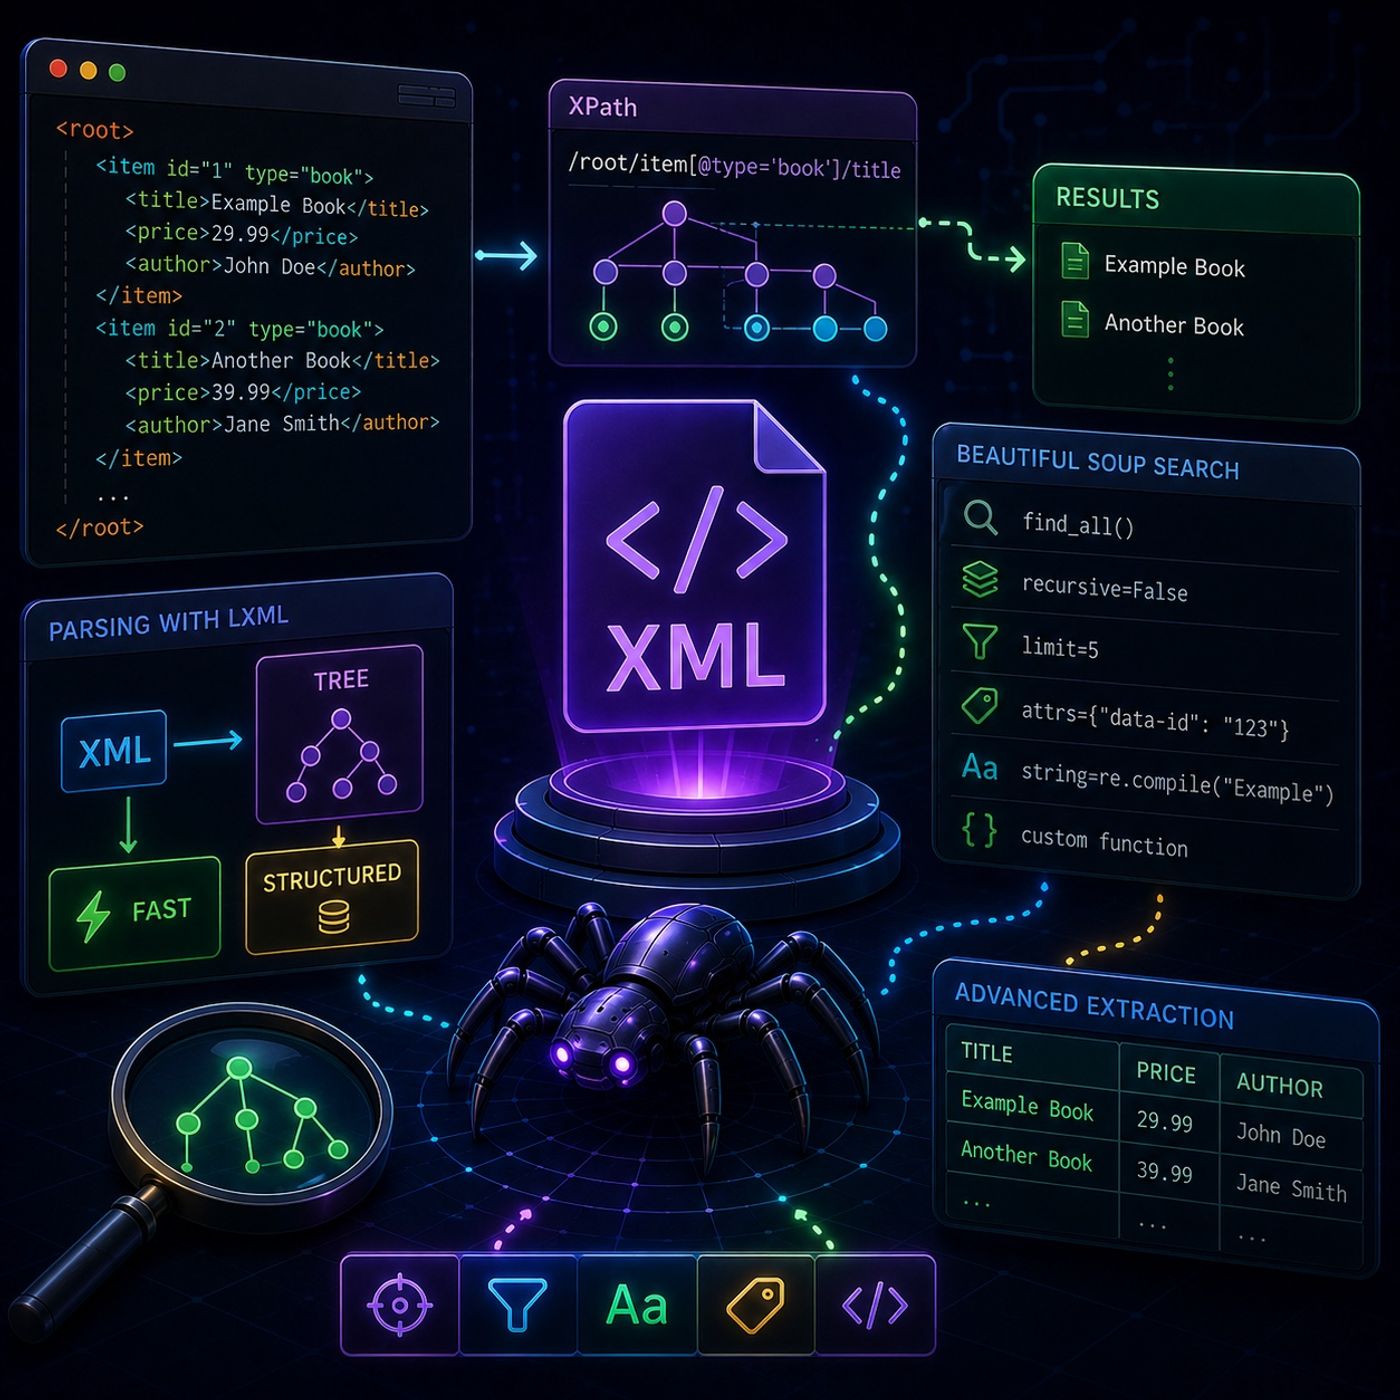
Course 40 - Web Scraping with Python | Episode 21: Mastering XML Parsing and Advanced Search with Beautiful Soup and XPath
In this lesson, you’ll learn about: how XML and XPath enable precise data navigation, and how to use advanced Beautiful Soup techniques for highly targeted extraction from complex documents1. XML as a Data Structure🔹 Why XML Matters🔹 Key CharacteristicsDesigned for data transfer, not displayStrict and well-formedHighly structured and predictable👉 Key InsightXML is ideal for scraping because its st
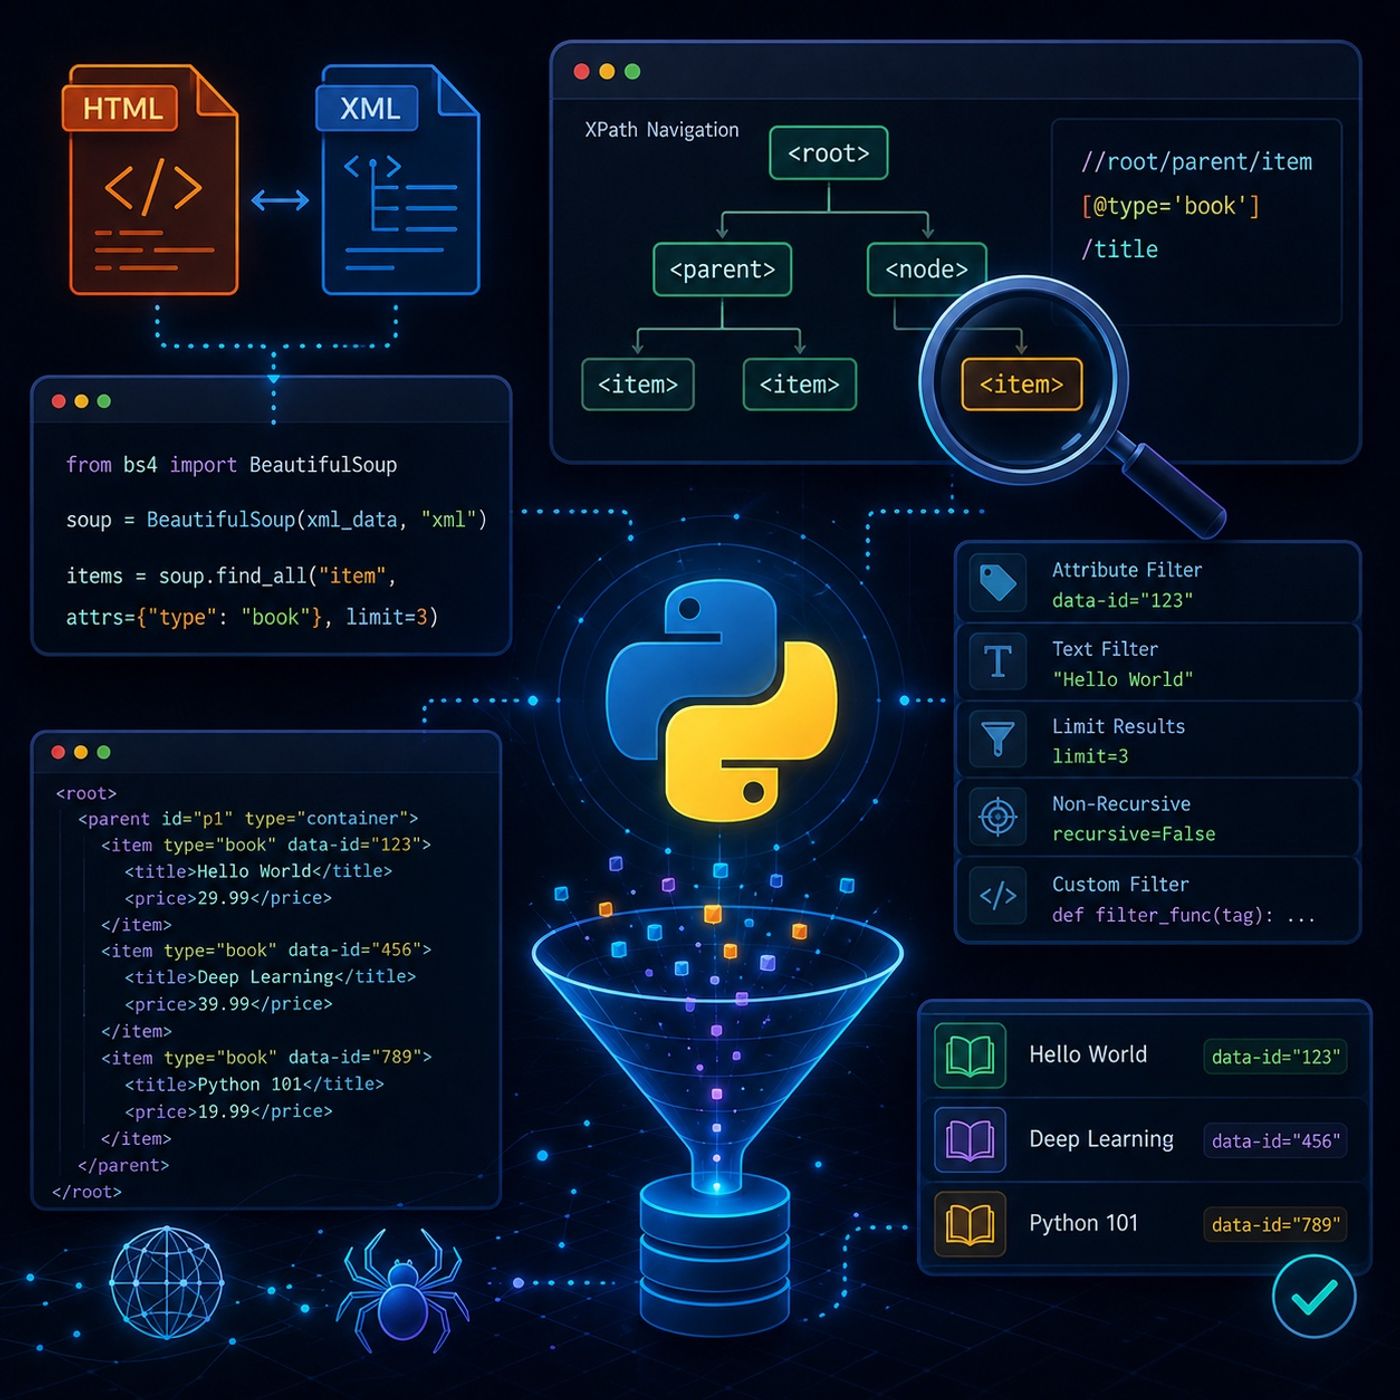
Course 40 - Web Scraping with Python | Episode 20: XPath Fundamentals and Advanced Beautiful Soup Searching
In this lesson, you’ll learn about: how Beautiful Soup works with both HTML and XML, how XPath enhances tree navigation, and how to perform precise, high-performance searches using advanced filtering techniques1. HTML vs XML in Web Scraping🔹 Understanding the Difference🔹 Key ConceptsHTML → designed for display (messy, flexible)XML → designed for data (strict, structured)👉 Key InsightXML is predict
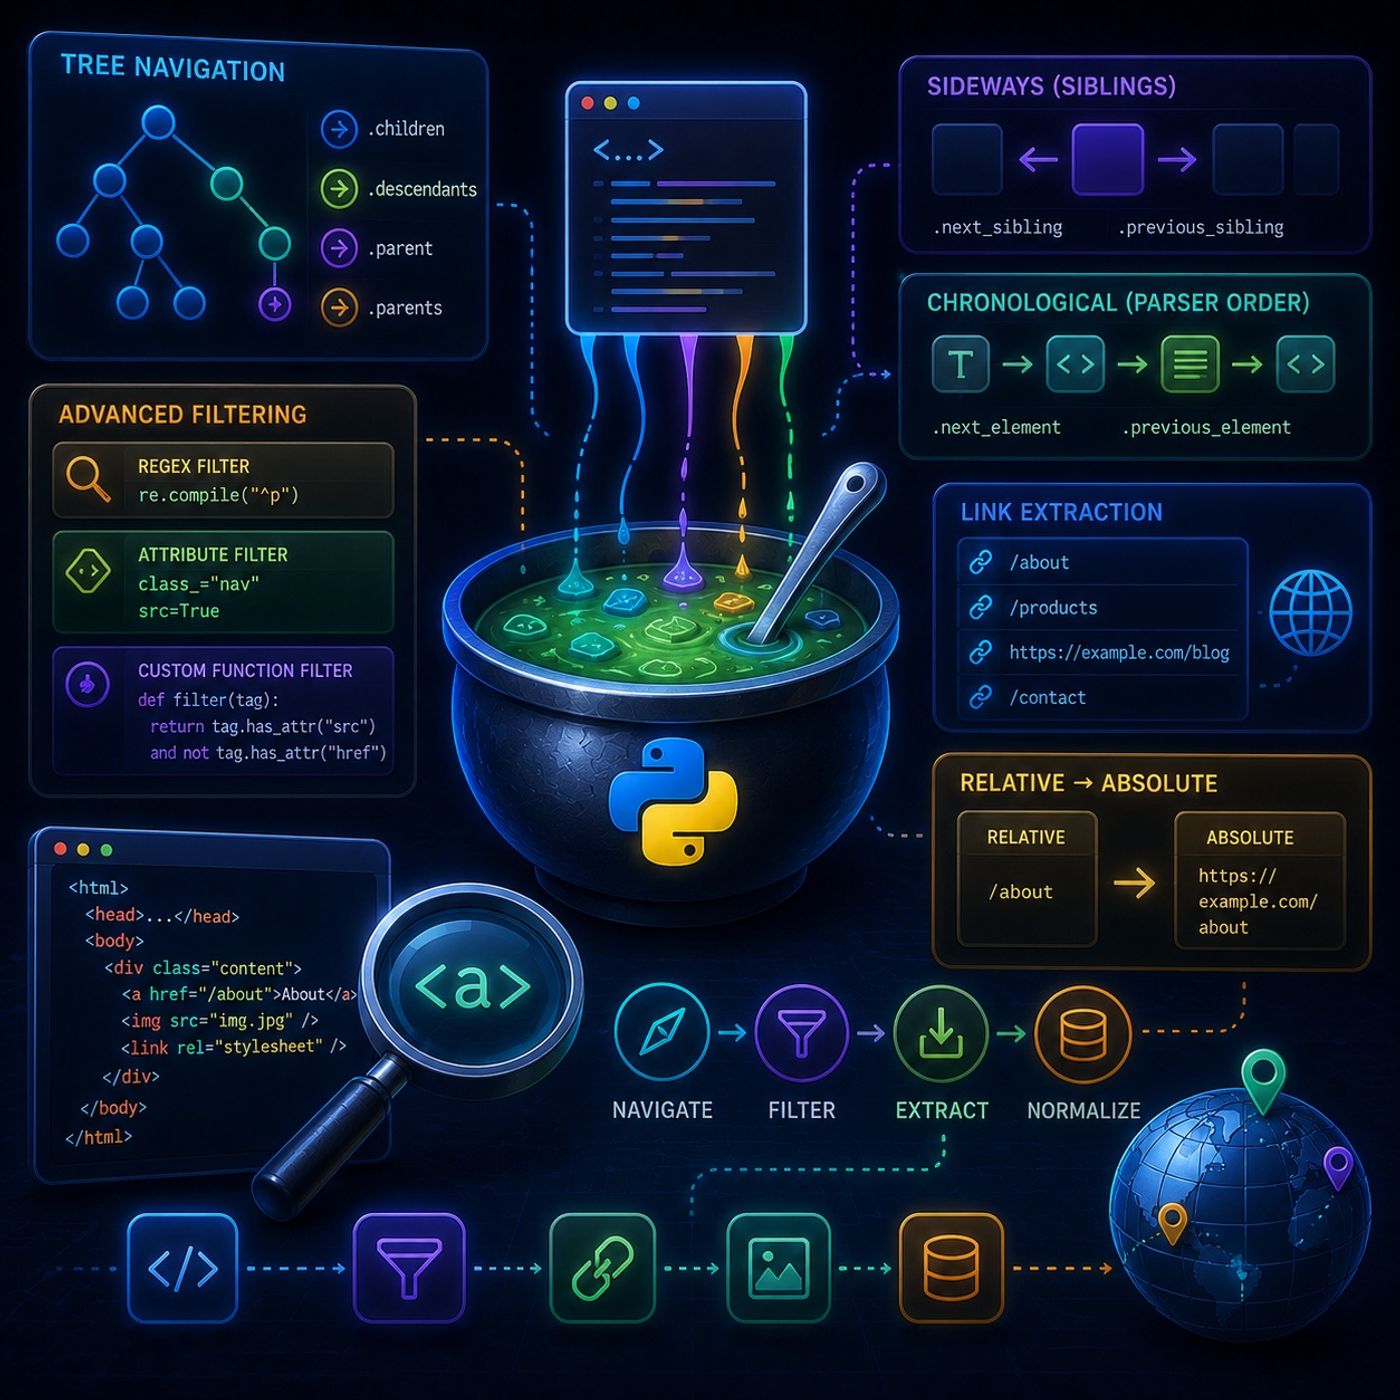
Course 40 - Web Scraping with Python | Episode 19: Tree Navigation, Advanced Filtering, and Link Extraction
In this lesson, you’ll learn about: advanced Beautiful Soup navigation, powerful filtering techniques, and how to extract and normalize real-world data like links from complex websites1. Advanced Tree Navigation🔹 Multi-Directional MovementBeautiful Soup allows you to move through HTML in three different dimensions:🔹 Vertical Navigationlist(tag.children) list(tag.descendants) tag.parent tag.parents
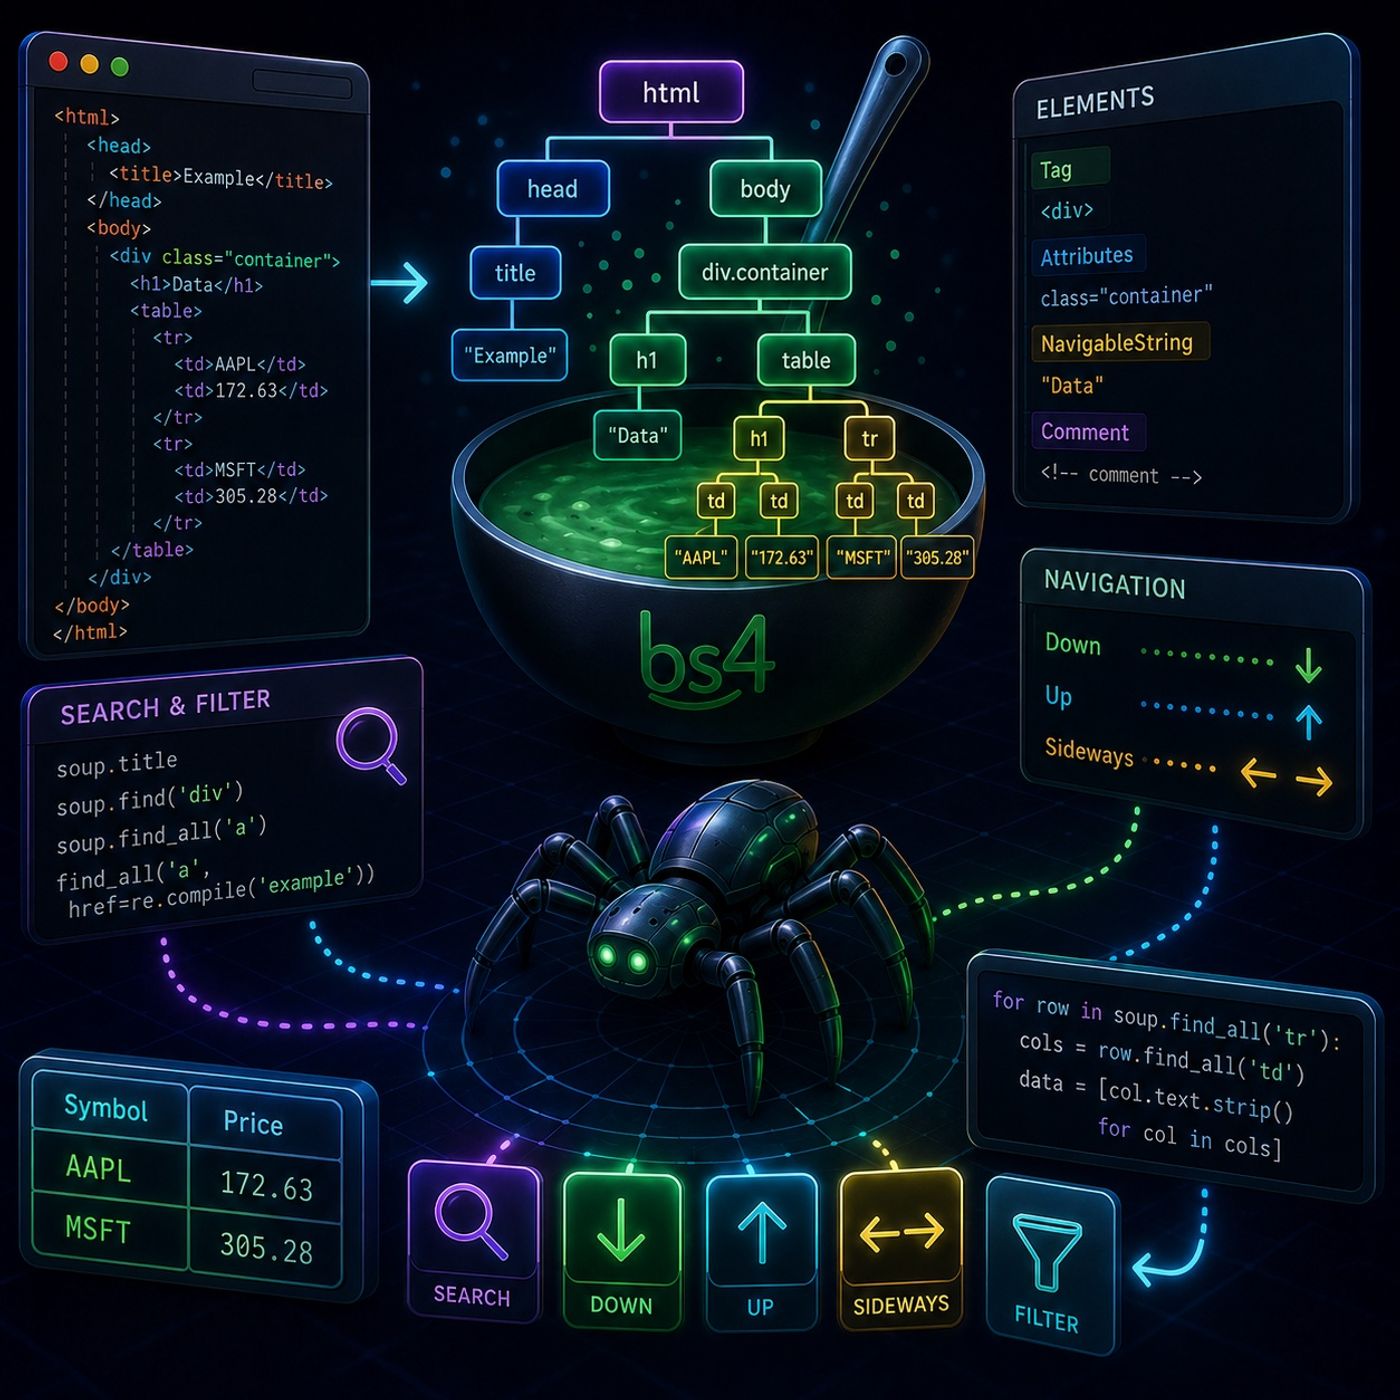
Course 40 - Web Scraping with Python | Episode 18: Mastering HTML Parse Tree Navigation and Element Extraction with Beautiful Soup
In this lesson, you’ll learn about: how Beautiful Soup builds a navigable HTML tree, how to search and filter elements, and how to move through the structure to extract clean, structured data1. Parsing HTML with Beautiful Soup🔹 From Raw HTML → Structured Tree🔹 Basic Workflowimport requests from bs4 import BeautifulSoup html = requests.get("https://example.com").text soup = BeautifulSoup(html, "lxm
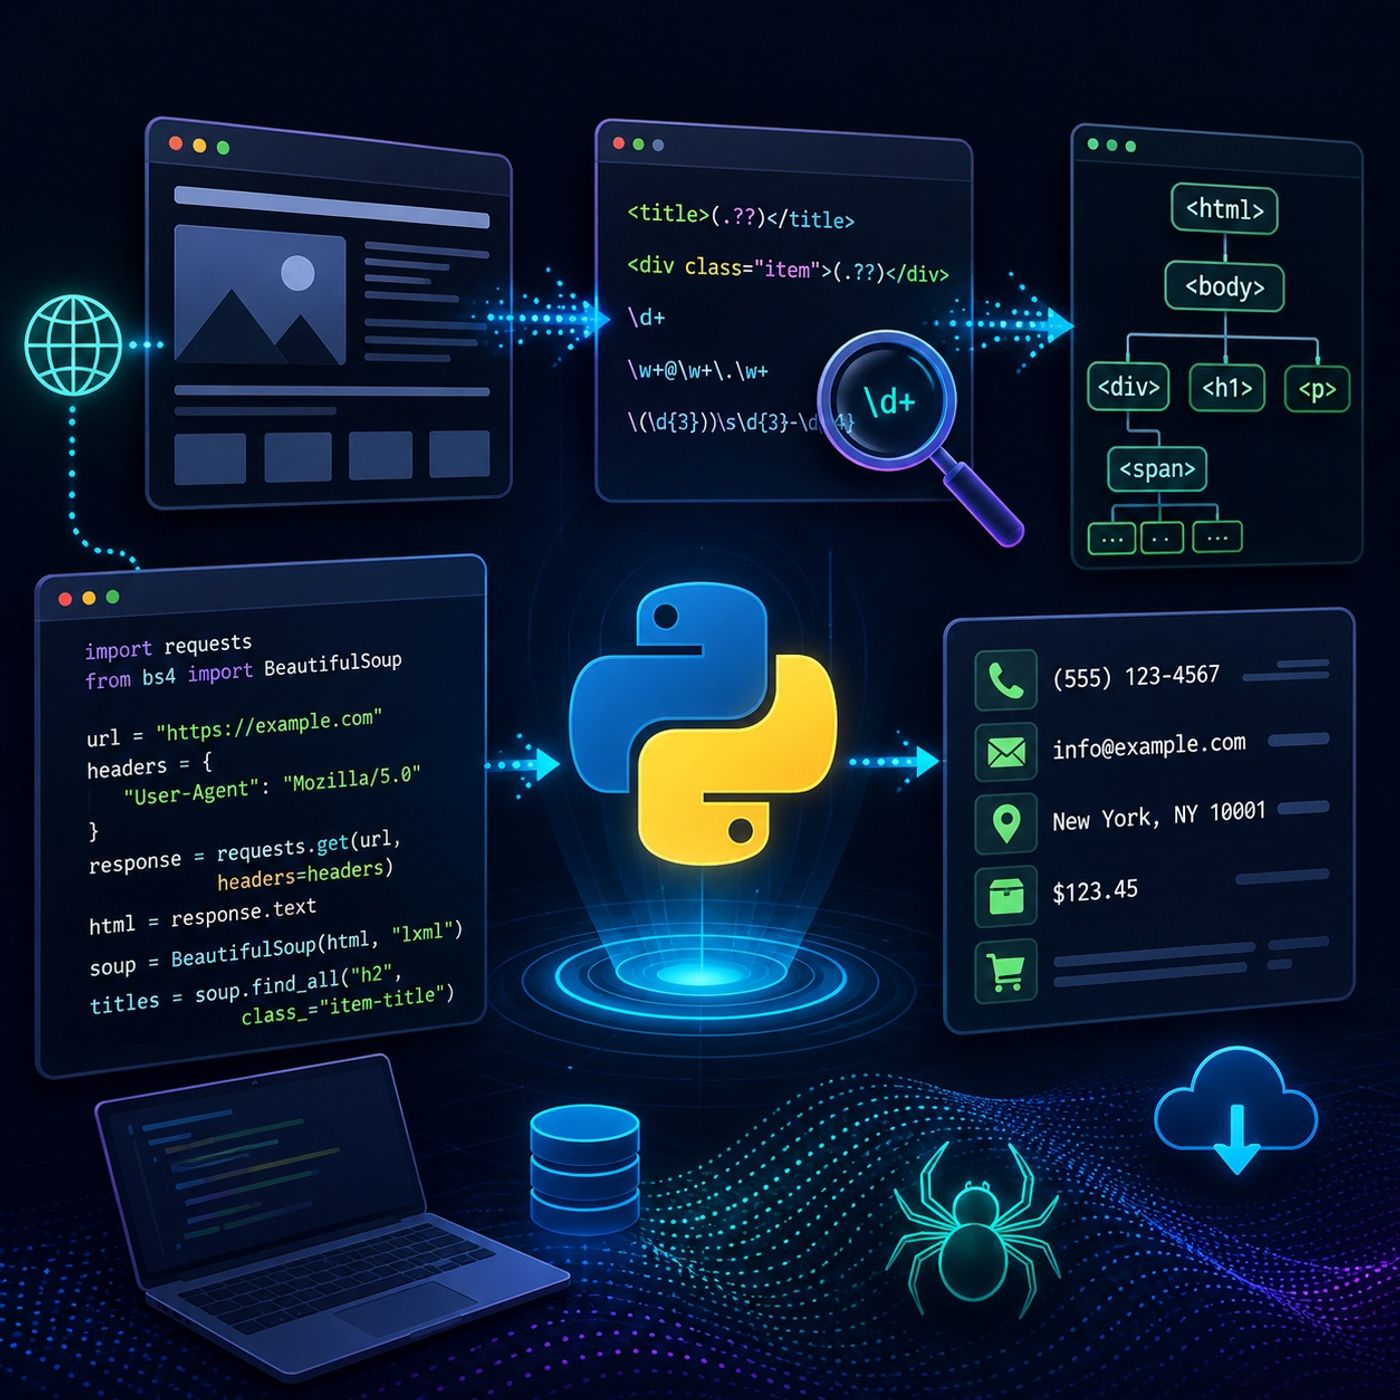
Course 40 - Web Scraping with Python | Episode 17: Mastering Requests, Regex, and Beautiful Soup
In this lesson, you’ll learn about: how Python retrieves web pages, how regex is used for pattern-based extraction, and how BeautifulSoup improves scraping by understanding HTML structure instead of treating it as plain text1. Fetching Web Content in Python🔹 HTTP Request FlowWeb scraping always starts with getting the page content.🔹 Libraries Usedurllib → built-in, basic controlhttplib2 → low-leve